Why People Still Tinker With The Apple TV 3 And What Actually Changes
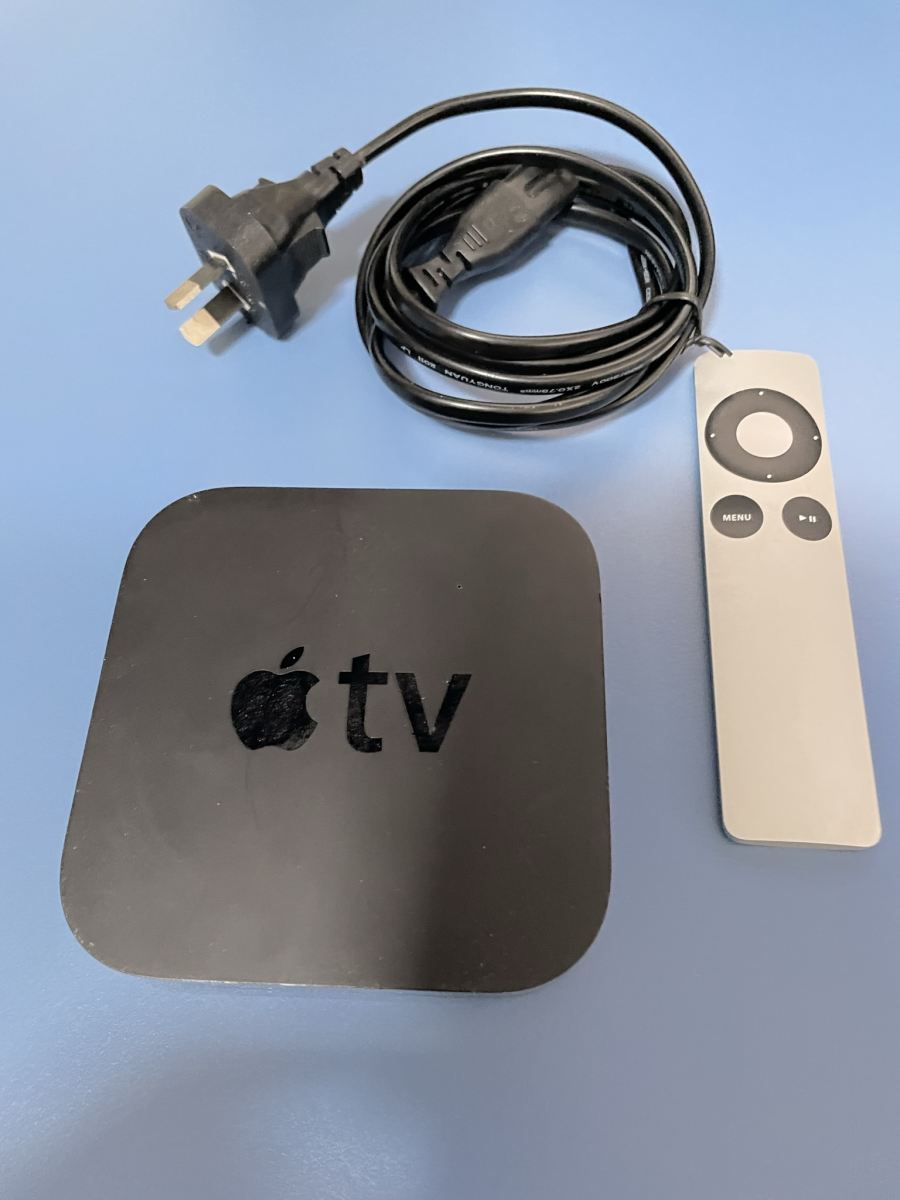
The Apple TV 3rd Gen is ancient hardware by now. It runs iOS 6 at most, has a dual-core ARM processor, and 256MB of RAM. That is not a lot of anything. But because of that age, it is also completely unpatched against older exploits. The device sits there waiting for people who still want it to do things Apple no longer supports. Jailbreaking it unlocks a layer of the system that the factory firmware keeps hidden. The most common thing people end up doing with it is running Sileo or Cydia on the box, installing a package like iFile, and then going from there. The phrase sounds like clickbait, but the idea behind it is straightforward. Apple ships the ATV3 with a sandboxed environment. You get what they give you. Jailbreaking removes that sandbox boundary. Once you have root access, you can install tweaks, modify system files, and run unsigned code. The hidden features are not some secret menu Apple buried in the source code. They are things like SSH access, custom launch agents, file system manipulation, and the ability to run alternative front ends or media servers directly on the device instead of streaming content from elsewhere. I have done this on about a dozen ATV3 units over the years. The usual process goes through a tool called AtvGif. You connect the Apple TV to your computer with a USB cable. The USB port on the ATV3 is actually a debug port, not a charging-only port like on later models. You use a micro-USB to USB-A cable, and you plug into the port labeled service. That port talks to the baseband processor, which is where the exploit lives. The exploit itself is a buffer overflow in the way the device handles certain malformed GIF files during the settings screen animation. It sounds ridiculous. It works.
Here is the practical part of the process. You download the latest AtvGif release from the official repository, extract it, and run the executable. You hold Menu and Volume Down together on the remote while plugging the USB cable in. The ATV3 boots into DFU mode, which puts it in a state where the normal operating system is not running and the exploit chain can inject code. The tool detects the device, chains the exploit, and drops you into a root shell. From there, you push a custom bootloader and recovery partition that lets you boot into a jailbroken environment instead of the stock iOS firmware. The whole thing takes roughly 5 to 10 minutes if your cable is decent and the tool finds the device on the first attempt. The actual hidden feature unlock depends on what you install after the root shell. If you flash a custom kernel patch and install an app store replacement like iREStorer or use the package manager, you gain access to tweaks that enable AirPlay from any app, not just the ones Apple approved. You can run XBMC or Kodi directly on the device as a standalone media player. You can install packages that change the UI theme, add a desktop environment, or enable background downloads. You can also enable SSH and log in remotely to move files around without needing the physical device every time. One thing most guides leave out is the bootloader situation. The ATV3 uses a custom version of xnu with a locked boot chain. The AtvGif exploit only gets you temporary root. To make the jailbreak persistent across reboots, you need to replace the boot rom partition or use a hardware mod. I ran into this on a unit where the exploit worked fine, I installed all the tweaks, and the device kept falling back to the stock OS on every reboot. The issue was that the NAND flash on that particular unit had wear leveling that caused the exploit payload to land in a bad block. I solved it by using the hardware flash tool to read the NAND, finding the correct offset for the exploit injection, and writing it manually. That is not something you should try if you do not have a CH341A programmer and a SOIC clip. Most people just end up using a hardware mod like the JTAG connector mod to bypass the software lock entirely.
Another counter-intuitive detail is that more RAM does not help here. The ATV3 is already resource-constrained. Installing too many tweaks will cause the device to segfault on boot. I once pushed twelve packages onto a unit and it would not get past the Apple logo. The fix was to disable all but three packages, keep iFile, enable SSH, and install one UI tweak at a time while watching the logs over the serial console. The serial console is accessible if you open the case and find the UART pins near the NAND flash chip. Three pins: ground, TX, RX. You connect a USB-to-TTL adapter at 115200 baud and watch the boot output in real time. That is how you know when a package is crashing the system before it even finishes installing. There are real limitations to this. The ATV3 cannot run modern streaming apps even after jailbreaking. Netflix and Disney Plus check for a valid secure boot chain and drop out if they detect any modification. You will not be able to watch 4K content on this device regardless of what you install. The hardware simply does not support it. The HDMI output is 1080p max, and even that requires the right cable and display setup. The USB port is USB 2.0, so external storage transfers are slow. And the Wi-Fi chipset is dated. If you are doing heavy network streaming, a wired Ethernet connection through an USB-to-Ethernet adapter is significantly more stable than the built-in wireless. Security is another factor worth mentioning plainly. A jailbroken ATV3 is not a secure device. Root access means anyone with network access to the box can log in and modify files. I recommend changing the default root password immediately after the jailbreak, disabling any services you do not need, and putting the device on a separate VLAN if your router supports that. The ATV3 does not support WPA3. It runs an old version of OpenSSL. If you expose it to the internet, you are asking for trouble.
Get the Full Details
The toolchain and all the packages mentioned here are available through the usual jailbreak communities. Search for AtvGif releases, the custom kernel patches for ATV3, and the package repositories that support the armv7 architecture. The main repo URL has changed a few times over the years as hosting situations shift, so check the latest post on the relevant forum thread rather than trusting an old bookmark. The community maintains mirrors. If your goal is simply to play media files from a NAS or USB drive, you might not need a full jailbreak. There are older versions of XBMC that run on the stock firmware through sideloading. It is less convenient but does not void anything or expose the device to root-level risks. If you want the full modified experience though, the jailbreak route is the only path. The ATV3 is old enough that the exploits are well documented and the tools are mature. It is not exciting technology anymore, but it still works if you know where to look and what to expect.