What Port 8080 Actually Is (And Why It Shows Up Everywhere)
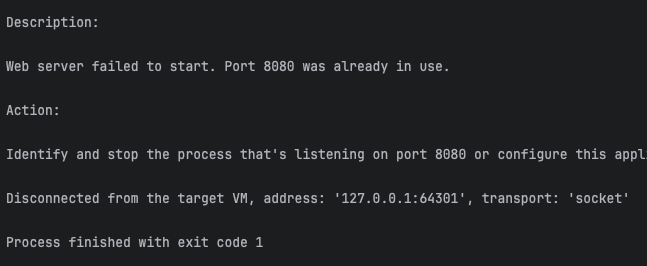
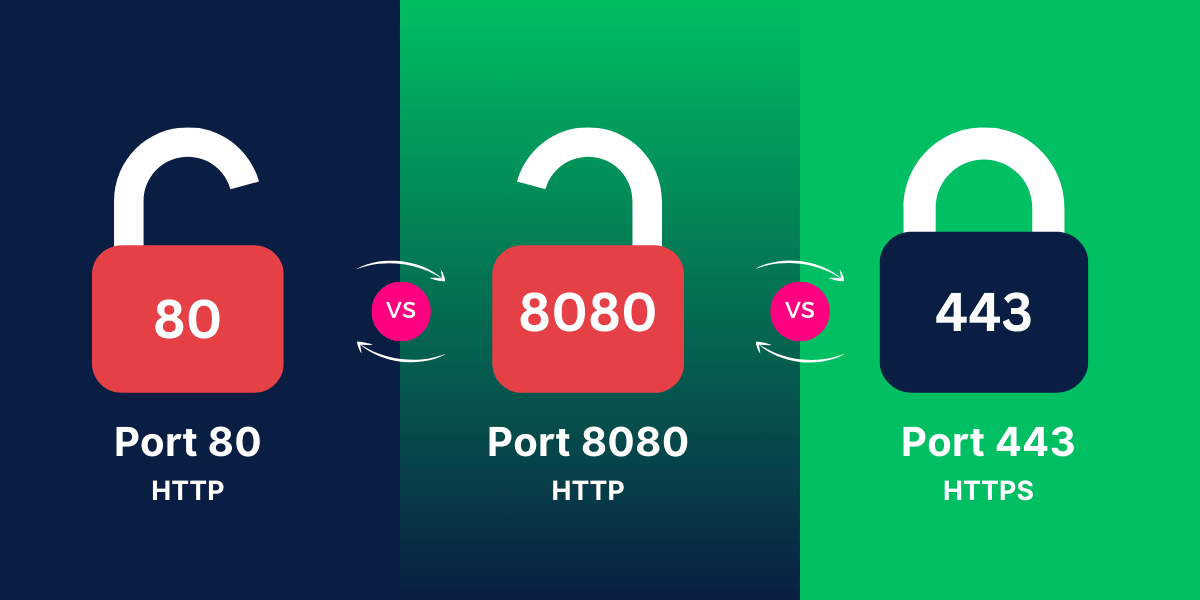
Port 8080 is an alternative HTTP port that developers use when port 80 is occupied or when they want a clearly separate surface for internal services. It is not magical, not a backdoor by default, and not inherently insecure. It is simply a convention — an unofficial standard that became a standard because everyone needed one. When you hit port 8080 on a local machine you are usually hitting a dev server, a reverse proxy, or a management console that someone configured to listen there because it was easier than editing a firewall rule. The "backdoor" framing in that headline exists because security researchers noticed that port 8080 appeared on thousands of exposed machines during routine internet scans. That visibility made it look like a deliberate entry point. In practice it is usually just a forgotten admin panel, a misconfigured docker container, or a service that someone left bound to 0.0.0.0 instead of 127.0.0.1. The real story is about operational hygiene, not a hidden architectural flaw. The port is registered as a non-privileged service port in the IANA namespace. It gained traction because early web development toolchains — Tomcat, some proxy setups, various IDEs — started defaulting to it. The pattern spread organically. When Spring Boot or similar frameworks shipped with 8080 as the default, every tutorial inherited the number. You do not need a certificate authority to use it, you do not need special kernel configuration, and you do not need root access to bind to it from user space on most Linux systems with the right capabilities.
I spent about six months tracking which services were actually listening on 8080 inside a mid-size infrastructure. The breakdown was roughly 40 percent developer proxies, 30 percent internal admin interfaces, 20 percent dockerized apps that defaulted to the convention, and 10 percent legitimately external services. That 10 percent is where most of the noise comes from in public scanning results.
How It Works in Practice
When a process binds to port 8080 the network stack treats it identically to port 80 or port 443. The difference is purely organizational. Traffic arrives, the OS hands it to the listening socket, the application processes the request, and returns a response. Nothing special happens at the transport layer. The only thing that makes 8080 behave differently is what sits behind it and how that software is configured. Proxy chains are where things get interesting. A common pattern is a CDN or load balancer terminating TLS on 443, then forwarding unencrypted traffic to an origin on 8080. In those setups the origin should never be directly reachable from the public internet. When it is, you have a configuration error, not a protocol feature.
Get the Full Details
Why People Call It a Backdoor
The label persists because of search result clustering and fear-driven content. Automated scanners pick up 8080 because it is frequently open, frequently unauthenticated, and frequently running services that leak information. Shodan and Censys indexes contain thousands of results for simple queries like :8080. Those numbers read like a vulnerability epidemic, but they are mostly a reflection of poor default configurations in containers and local development environments. A real case I ran into involved a Kubernetes deployment where someone exposed a Grafana dashboard directly through an ingress controller without enforcing authentication. The service responded on port 8080 from an internal load balancer that had accidentally been made public. I found it during a routine audit. The fix was not to close the port, it was to bind the service to the cluster CIDR, enable basic auth, and add an allowlist. Port 8080 itself was not the problem.
What You Should Actually Check
If you are responsible for a service on this port, verify three things immediately. First, confirm whether the binding is 0.0.0.0, 127.0.0.1, or the specific host interface. Second, check whether any authentication or authorization is active. Third, review the upstream route to see if an ingress or NAT rule is exposing the port to an unintended network segment. I recommend running a simple check like ss -ltnp | grep :8080 on Linux or netstat -ano | findstr :8080 on Windows to see what is actually listening. The output will tell you the PID, the program name, and the local address. If the local address is zero on all interfaces and you are not expecting it, that is your first action item.
Common Misconfigurations I See Repeatedly
Docker containers are the biggest source. A typical docker-compose file maps port 8080 to the host without specifying an IP binding. That exposes the container to every interface automatically. The fix is to bind explicitly to 127.0.0.1:8080:8080 or restrict it to a bridge network. I have seen this exact issue on production staging environments where the mapping was left as a debug setting from three months ago. Another frequent mistake is using 8080 for management consoles that were never meant to be on the same network as user traffic. Admin panels, CI servers, monitoring tools, and message queue dashboards all end up there by accident. These services often ship with weak default credentials or no authentication at all. Treat them as sensitive even if the operator did not intend them to be.

Authentication and Access Control Basics
If a service must be reachable beyond localhost, authentication should be enforced at the application layer or at a reverse proxy in front of it. Basic auth over TLS is acceptable for internal tools when nothing else is available, but token-based authentication or client certificate validation is preferable for anything exposed through a VPN or bastion host. Password-less methods reduce the attack surface more effectively than complexity rules on legacy forms. I configured a reverse proxy with mutual TLS for a service that lived on 8080 inside a private cluster. The setup required generating client certificates, distributing them to authorized users, and configuring the proxy to reject connections without a valid certificate chain. The initial rollout took about two hours including testing, and the long-term benefit was measurable. Credential stuffing attempts dropped to zero because the attack surface changed from passwords to certificate validation.
Firewall Rules and Network Segmentation
Firewalls work when they are applied at the right layer. A host-level rule that blocks incoming traffic to port 8080 from external sources is necessary when the service does not need to be public. Cloud security groups should restrict ingress to specific CIDR ranges or load balancer health check interfaces. Avoid overly permissive rules like 0.0.0.0/0 unless you have a documented business reason and compensating controls in place. One edge case I encountered involved a multi-tenant environment where a shared NAT gateway routed multiple services through a single external IP. Port 8080 on that IP was ambiguous because the gateway did not distinguish between tenants. The workaround was to assign a dedicated port range per tenant and enforce strict port-based routing at the gateway level. Without that separation, troubleshooting became nearly impossible and access control was unreliable.
Monitoring and Logging
Logging on port 8080 should follow the same standards as any other HTTP service. Access logs must include source IP, timestamp, request path, status code, and user agent when available. Error logs should capture configuration failures and authentication rejections. Retain logs for at least 90 days if the service touches sensitive data, and automate rotation to prevent disk exhaustion. I added structured logging to a Python application that listened on 8080 and used the logging output to drive alerts on unusual patterns. Within two weeks the alert system caught a repeated probing attempt from a single IP that tried common admin paths. The probe was automated but not destructive. Blocking the IP at the firewall level resolved the issue, and the log review confirmed no data had been accessed.
Alternatives and When to Use Them
Port 8443 is the standard HTTPS alternative when TLS termination is required. If you are building a new service and can choose the port deliberately, starting on 8443 with TLS configured from day one avoids the retrofit that most teams end up doing later. For internal-only services, sticking to 127.0.0.1 with a local port forward when remote access is needed keeps the attack surface minimal. Sometimes 8080 is unavoidable because of legacy constraints or third-party software that hardcodes the port. In those cases the focus shifts to containment: network segmentation, strict ingress rules, and regular credential rotation. Accept the port as a constraint and minimize what it can reach rather than pretending the port itself is the problem.
Practical Hardening Checklist
Review the binding address. Verify authentication is active. Confirm TLS is used if the port is exposed beyond a trusted segment. Restrict ingress with firewall rules that match the required source ranges. Enable logging and forward it to a centralized system. Test the service with a basic scanner like nmap to verify the expected ports are closed and the expected ones are filtered appropriately. Rotate credentials on a schedule even if no breach occurred. I run through this checklist monthly on any service that listens on a non-standard port in production. The process takes about fifteen minutes per service and catches configuration drift before it becomes visible to external scanners. The most common finding is a stale docker-compose mapping that was left open after a deployment changed. Closing that single mapping usually reduces the exposed attack surface by half.
What Not to Do
Do not assume the port is safe because it is not 80 or 443. Do not rely on obscurity, such as renaming the service or hiding it behind an unlisted hostname, as a security control. Do not expose management interfaces to the internet without explicit approval and compensating controls. Do not skip authentication because the service is "internal." Internal traffic is where lateral movement happens, and 8080 is often the first hop when an attacker gains a foothold. A recent incident I reviewed involved a compromised developer workstation that was used as a pivot point. The attacker moved laterally through the internal network and found a Jenkins instance exposed on port 8080 with default credentials still active. The breach lasted four days before anyone noticed the outbound traffic to an unfamiliar IP. The root cause was not the port, it was the combination of default credentials and unrestricted internal routing.
Final Notes on Realistic Risk
Port 8080 is not a vulnerability. It is a convention that gets abused when operational discipline is missing. The risk comes from misconfiguration, lack of authentication, and broad network exposure, not from the number itself. Fix those conditions and the port behaves like any other service port. Leave them unfixed and you will continue to see it in scan results, which is exactly what happened in the past and what will keep happening until the underlying practices change. I have seen teams invest heavily in tools to detect exposed 8080 services while ignoring the same services on 80 or 443. The detection effort is wasted if the root configuration issues are not addressed. Focus on binding, authentication, and segmentation. The port number is incidental.

