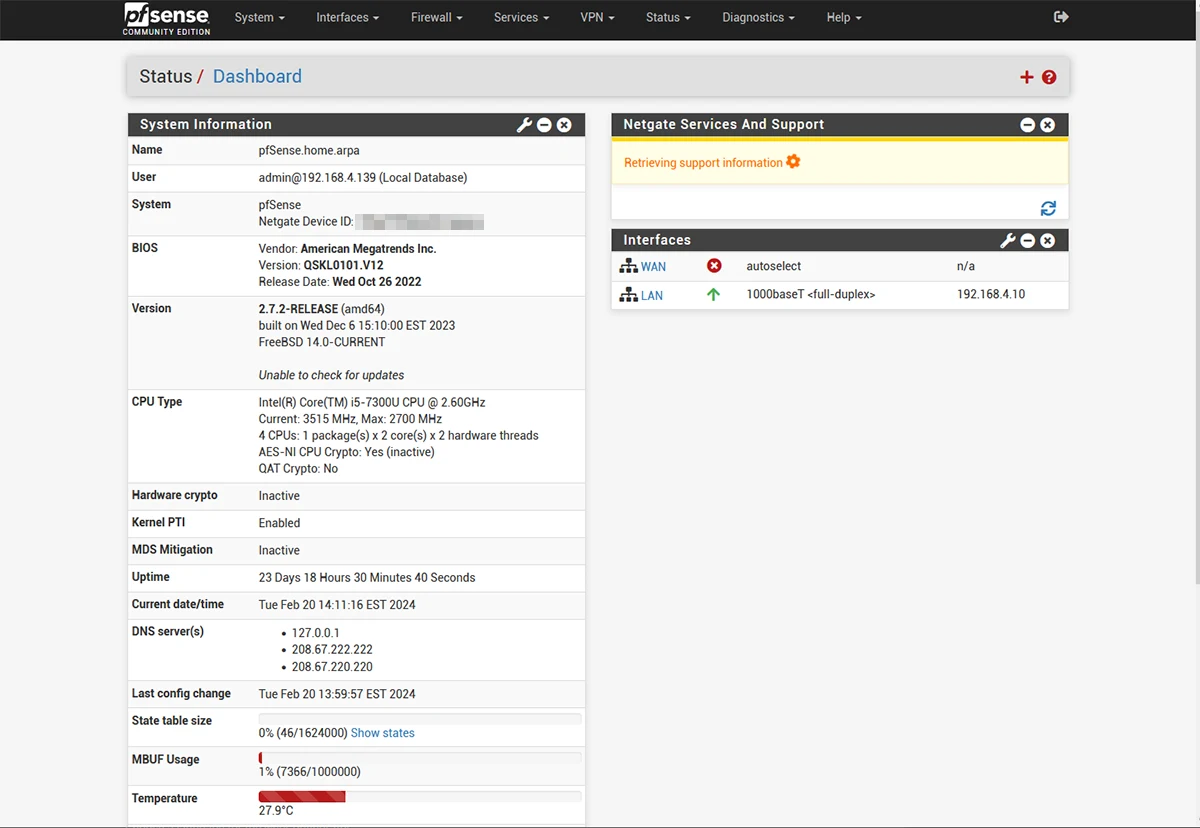
Installing pfSense on Real Hardware vs. Cheap Mini PCs
I've deployed pfSense on dedicated hardware and on repurposed mini PCs. The difference matters more than most guides admit. A used Dell Optiplex with dual NICs and an i5 will handle a home network without breaking a sweat. Those cheap Chinese mini PCs with Celeron N4020 chips? They choke on IPS packages and multi-WAN setups. I learned this the hard way when I put one behind my home office and watched it max out CPU at 100 Mbps of throughput while running Suricata IDS. Moved it to a used ThinkCentre M720q with an i5-8500T and the same workload ran at 650 Mbps with CPU sitting at 15 percent. Installation itself is straightforward enough that anyone who can flash a USB drive can do it. Download the latest release from pfsense.org, write it to a USB stick using Etcher or Rufus, and boot from it. The installer will ask you to partition the disk. It recommends using the entire drive and wiping existing data. Unless you're doing something unusual like keeping a second OS on the same machine, just let it do that. One of the things people mess up is skipping the serial console configuration during install. If you're running this headless in a rack, you need a console connection. I configure mine with COM1 at 115200 baud and wire a null modem cable to an old USB-to-serial adapter so I can access the shell when the web GUI won't load after a bad config backup restore.
Unlocking Security And Control The Ultimate Guide To Pfsense Free
The free version of pfSense gives you the full firewall, VPN, captive portal, and packet capture capabilities. What you don't get is the commercial support contract and some of the enterprise dashboard analytics in pfSense Plus. For most home and small business users, the free version is all you need. The confusion usually comes from people not understanding that the Community Edition and Plus share the same codebase. The only real differences are support channels and a few dashboard widgets. When I first set up a client's pfSense, I configured their LAN as 192.168.1.1/24 with DNS forwarding to Google's 8.8.8.8. That worked fine until they asked me to add a guest wireless network. The default bridge settings and IP allocation created a NAT conflict because the guest VLAN also tried to use 192.168.1.0/24. I had to renumber the main LAN to 10.0.0.1/24 and reconfigure all the DHCP scopes. This is something the installer doesn't warn you about. If you're starting from scratch, just use RFC1918 ranges that you won't later need to change. 10.10.0.1/16 for the internal network avoids this kind of collision entirely.
Configuring NAT and Firewall Rules the Right Way
Most people get firewall rules wrong by making them too permissive. The default pfSense template creates rules that allow LAN to WAN with no restrictions. That's fine for a basic setup but insufficient for anything that needs actual security. I always start by creating an explicit deny-all rule at the top of every interface rule set. Then I add allow rules from the bottom up based on what services actually need to be exposed. NAT is where things get more confusing. pfSense uses "NAT Reflection" to let internal clients access their own servers by the public IP address. This feature breaks half the time people enable it because of asymmetric routing or misconfigured port forwards. I disable reflection by default and tell people to use internal DNS instead. You can set up pfSense's built-in DNS resolver to serve internal hostnames that resolve to private IPs. This is cleaner than reflection and doesn't create hairpin NAT issues. Here's a specific problem I ran into last year that took me three hours to diagnose. A client had a web server on their DMZ that they could reach from the internet but not from the LAN. The NAT rule was correct. The firewall rule on the DMZ interface allowed inbound traffic. The issue was that the server's default gateway was set to the pfSense LAN IP but the return traffic was being routed out the wrong interface due to a secondary IP on the WAN interface. I found it by running tcpdump on the DMZ interface and watching the SYN-ACK packets never appear. The fix was adding a static route on the web server pointing 10.10.0.0/16 through the DMZ gateway instead of the default route.
Get the Full Details

VPNs That Actually Work
The OpenVPN and WireGuard implementations in pfSense are solid. I use WireGuard now because it's faster and the configuration is simpler. OpenVPN still has its place when you need split tunneling with complex routing tables or when connecting to legacy clients. Setting up a site-to-site VPN between two pfSense boxes is basically just copying the wizard through, but the wizard hides some details that matter for reliability. The keepalive interval and renegotiation settings in the Advanced tab of each peer configuration are usually left at defaults that cause connections to drop during ISP outages. I set the persistent keepalive to 25 seconds on both ends and increase the renegotiation window to 3600 seconds. This prevents the tunnel from dropping when one side's NAT table entry times out. I also configure the MTU to 1380 instead of the default 1500 because many home internet connections use PPPoE which adds overhead. Without adjusting MTU, you'll get fragmentation and slow transfers that make no sense until you check the packet sizes.
Packages and What to Actually Install
The package manager is one of pfSense's strongest features. Snort or Suricata for intrusion detection, Squid for proxying, and Unbound for local DNS resolution are the core packages I recommend. People tend to overload their install with too many packages and then wonder why updates take twenty minutes or why the system feels sluggish. I cap it at three packages per deployment unless there's a specific reason for more. Suricata is better than Snort for most use cases now. It supports multi-threading out of the box and the inline IPS mode works reliably if you configure it correctly. The trick is setting the performance profile to "medium" and enabling the prelude logger only if you need centralized alerting. By default, Suricata on pfSense writes logs to /var/log/suricata and those logs grow fast. I set up log rotation with a cron job that compresses files older than seven days and deletes anything older than thirty. Without this, a busy network fills the disk in two weeks.
Backups and Recovery
pfSense makes backing up your config easy. The system provides an export function that saves everything to an XML file. I configure it to automatically back up to an FTP server every day at 3 AM using a simple cron script that calls the config export API endpoint. I also keep a local copy on a USB drive plugged into the appliance. The USB auto-mount feature can save you when the config gets corrupted and you need to restore from a known good state without network access. There is one thing that confuses people about recovery. If you accidentally delete the admin account or lock yourself out of the web GUI, the password reset procedure requires physical access to the console. You boot into single-user mode and run the config file editor. I once spent an hour trying to figure out why I couldn't log in before realizing I had changed the default admin password during a demo and then lost the credentials. The reset process is documented but easy to miss if you're panicked. The console cable I mentioned earlier becomes essential here.

When pfSense Is the Wrong Choice
I want to be blunt about where this tool falls short. If you need more than 1 Gbps of filtered throughput, pfSense on commodity hardware won't cut it. The software firewall introduces too much latency at higher speeds. In those cases, I recommend looking at OPNsense on multi-core enterprise hardware or moving to a hardware appliance from vendors like WatchGuard or Fortinet. If you're managing a fleet of fifty locations and need centralized cloud management, pfSense's built-in remote management capabilities are inadequate compared to solutions like Untangle or Sophos XG. Another scenario where pfSense struggles is high connection density. A typical home setup might have fifty devices. A coffee shop or small office can easily have five hundred concurrent connections from phones, tablets, and laptops. pfSense's state table handles this fine, but the logging and monitoring become unwieldy. You'll spend more time managing alerts than actually securing the network. For those environments, I point people toward commercial solutions that include tenant isolation and usage reporting out of the box. The download link is on the official website at pfsense.org/download. Always verify the checksum before flashing anything. I've seen people download from third-party mirrors and end up with modified ISOs that defeat the purpose of running a secure gateway in the first place. The community forums at forum.pfsense.org are active but the documentation is scattered across multiple pages. I keep a personal reference sheet with the command-line equivalents of the most common web GUI actions because there are times when the shell is faster than clicking through ten menus to change a single setting.


