IPsec Configuration Is Painful But Necessary
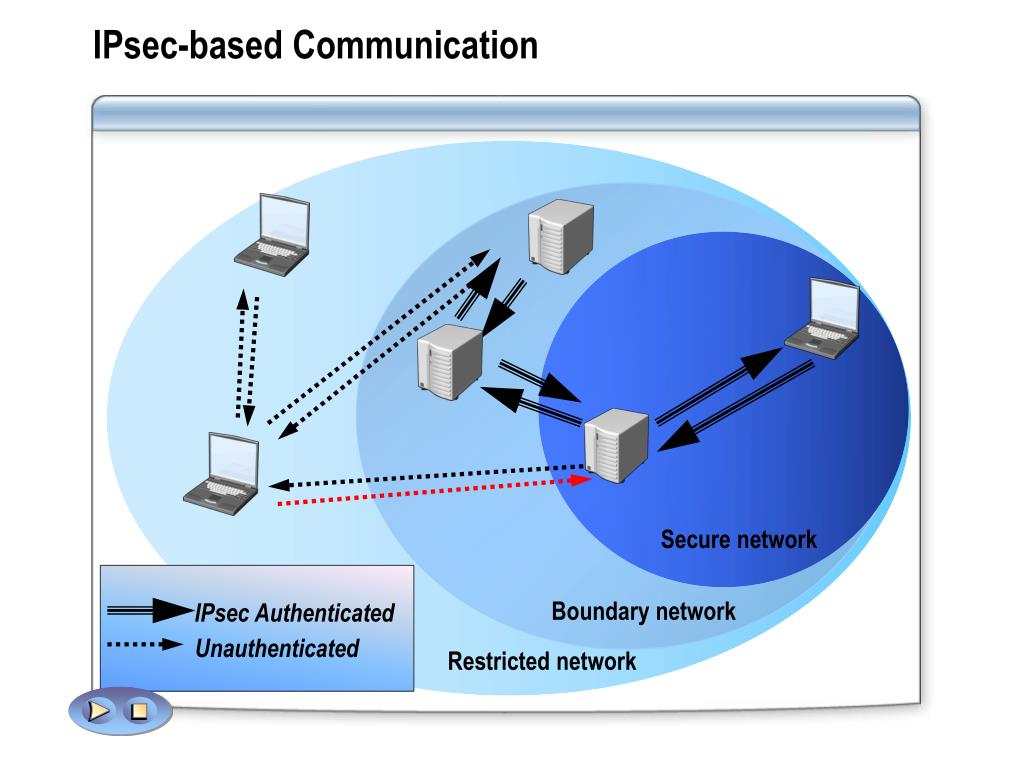
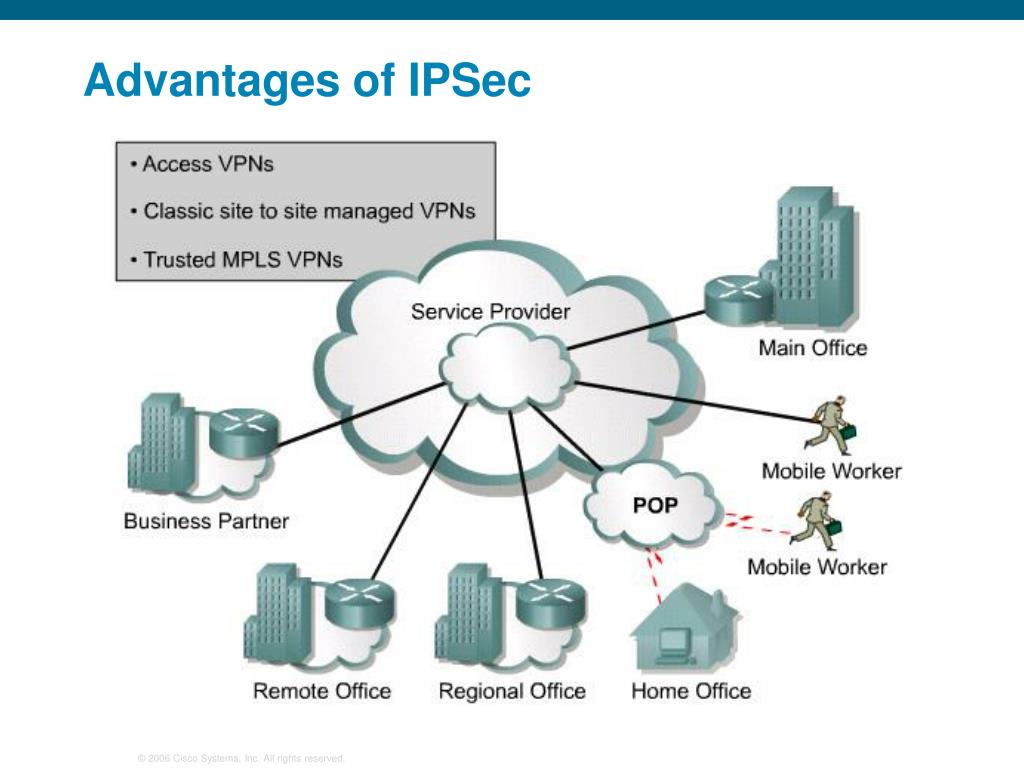
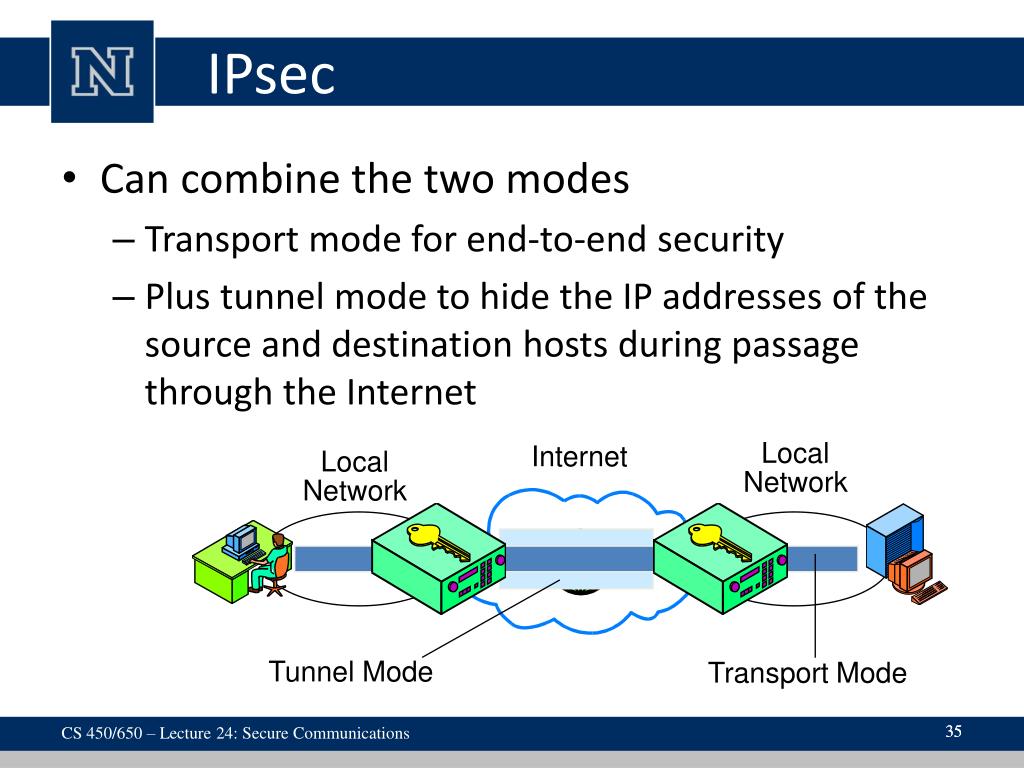
I spent last Tuesday debugging an IKE Phase 1 negotiation failure between a Cisco ISR and a Palo Alto firewall for forty-five minutes before finding out the pre-shared key had an invisible character copy-pasted from a PDF. That is the world of IPsec. It works beautifully when it works. When it does not, the logs are deliberately vague and you end up chasing ghosts. Internet Protocol Security (IPsec) is a suite of protocols that encrypts and authenticates IP traffic at the network layer. It operates in two modes: transport mode, which protects just the payload, and tunnel mode, which wraps the entire original packet inside a new IP header. Most people need tunnel mode because that is how site-to-site VPNs actually function. The protocol handles this through two main sub-protocols. AH (Authentication Header) provides integrity and authentication but no encryption. ESP (Encapsulating Security Payload) does both. You will almost always use ESP. AH is basically dead at this point and some implementations do not even ship it.
Unlocking Secure Network Communication The Power Of Ipsec
The foundation here is the Internet Key Exchange protocol, or IKE. There are two versions and they matter. IKEv1 is the older clunky thing that split into Main Mode and Aggressive Mode. IKEv2 is the modern version and it bundles negotiations more efficiently. A typical Phase 1 establishes an ISAKMP SA using either Pre-Shared Key or Certificate authentication. Phase 2 uses that secure tunnel to negotiate the actual IPsec SA that carries your data. Do not skip understanding that separation because troubleshooting becomes nearly impossible otherwise. Here is something most beginners miss. The transform sets and proposal priorities are where things break in practice. You can have matching pre-shared keys, correct subnets, and proper interfaces enabled, and it still will not work because one side prefers AES-GCM and the other only supports AES-CBC. The negotiation fails silently and you get zero SA established. Always verify the full transform set on both ends, not just the encryption algorithm. Diffie-Hellman groups matter too. DH Group 14 is 2048-bit and is the current baseline. Anything below that is considered weak now. I recommend setting DH 14 as the minimum on every device you touch. I had a deployment last year where a customer's branch office IPsec tunnel kept dropping every forty-seven minutes. The tunnel came back up after sixty seconds, dropped again, and repeated. We checked the configuration three times. Everything looked correct. The issue turned out to be the DPD (Dead Peer Detection) timing mismatched with the idle timeout on an intermediate firewall that was not even in the VPN design. The firewall was silently killing the IKE SA while IPsec itself was still negotiating fine. The workaround was adjusting the DPD interval and adding a specific pass rule for UDP port 500 and 4500 before that firewall. It sounds trivial but the symptom was completely misleading. The local IPsec process showed healthy rekey cycles while the remote end looked disconnected.
Let me walk through a basic site-to-site setup because the theory means nothing without seeing the pieces move.
Get the Full Details

Setting Up a Basic Site-to-Site IPsec Tunnel
You need to define three things upfront before you touch any command line. Your local subnet, the remote subnet, and the shared key. That is it. Everything else is implementation detail. Let me show you what this looks like on a typical Linux machine using strongSwan since it is free and widely available. First install the package. sudo apt install strongswan libcharon-extra-plugins
The configuration lives in /etc/ipsec.conf. A minimal working entry for a site-to-site tunnel looks like this: config setup Then add the pre-shared key to /etc/ipsec.secrets:
charondebug="ike 2, knl 2, cfg 2, net 2, esp 2, dmn 2, mgr 2"
conn remote-site
left=203.0.113.10
leftsubnet=10.0.0.0/24
right=198.51.100.5
rightsubnet=172.16.0.0/24
ike=aes256-sha256-modp2048!
esp=aes256-sha256!
keyexchange=ikev2
auto=start
authby=secret
rightauth=psk
leftauth=psk
203.0.113.10 198.51.100.5: PSK "your-actual-long-key-here" Restart the service and check status: sudo systemctl restart strongswan
sudo ipsec status
You should see both the IKE SA and the IPsec SA in ACTIVE state. If you see INIT or connecting, something is wrong with the proposal negotiation or the firewall is blocking the traffic. Check the logs with journalctl -u strongswan and look specifically at the Phase 1 messages. Those tell you exactly where the handshake failed. The same concept applies to Windows, Cisco IOS, Palo Alto, Fortinet, AWS VPN, and Azure VPN Gateway. The syntax differs but the three requirements stay identical. Local subnet. Remote subnet. Shared credential. If you can nail those down the rest is just reading the documentation for your specific device. There are real limitations you should know about before you commit to IPsec as your solution. Performance is the biggest one. Every packet gets encrypted and decrypted on the device hosting the IPsec endpoint. On a low-power router or an old firewall that means the tunnel throughput will be a fraction of what the link can actually deliver. AES-NI hardware acceleration on modern CPUs helps significantly but if you are running this on budget hardware or in a virtualized environment without proper CPU passthrough you will hit a wall fast. A typical unaccelerated implementation on a basic x86 box handles maybe two to three hundred megabits per second of encrypted throughput before the CPU becomes the bottleneck. Your actual usable throughput may be lower depending on packet size and the encryption suite chosen.
Another issue nobody talks about enough. IPsec does not play well with NAT on the path. NAT-T (NAT Traversal) exists as a workaround by encapsulating IPsec traffic inside UDP port 4500 but it adds overhead and not every intermediate device handles it correctly. I have seen networks where the tunnel worked perfectly in a lab and failed in production because a carrier's CGNAT device was mangling the ESP protocol packets. ESP is protocol 50 and there is no port number to track. Middleboxes that do stateful inspection of ports simply drop ESP traffic because they do not know what to do with it. If you are crossing carrier networks or any environment with unknown intermediate devices, test IPsec there first before deploying it for production traffic. WireGuard handles NAT traversal far more reliably and I would recommend evaluating it as an alternative if that is your scenario. Maintenance is the other hidden cost. Keys expire. Certificates expire. SA counters fill up. You need to actually monitor this stuff rather than configuring it once and forgetting about it. Set up logging for SA rekey events and alert when the interval deviates from the expected pattern. A sudden jump in rekey frequency usually means someone changed the proposal on one end without changing it on the other, or there is a device in the path renegotiating the MTU and fragmenting packets in ways that break the ESP overhead calculation. The practical reality of IPsec is that it is solid infrastructure when it works and it is a debugging nightmare when it does not. The protocol itself is well-designed. The operational complexity is high. Invest time in proper proposal matching, document your subnet lists and key rotation schedule, and never assume a green status light means the tunnel is carrying your actual traffic the way you expect. Run a continuous ping through the tunnel and verify the latency profile. That single test will catch more problems than any log entry in this system.