Setting Up IPsec VPN Between Your On-Prem Network and Databricks
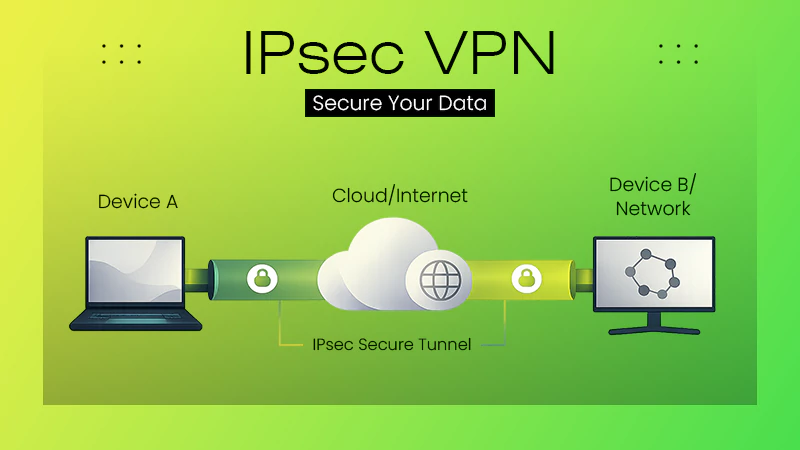
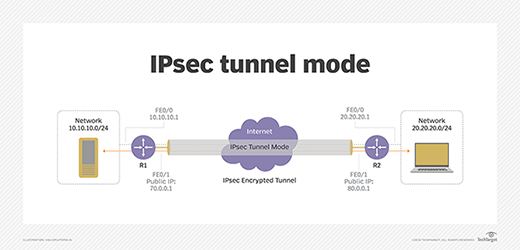
Data transfer between your corporate infrastructure and Databricks used to mean either exposing endpoints publicly or managing a maze of cloud connectors. IPsec VPN changes that. It gives you a tunneled, encrypted path that keeps your data pipeline isolated from the public internet. I spent about three weeks untangling a production migration last year where the original architect had configured the VPN but never tested what happened when the MTU wasn't aligned. Traffic looked like it was flowing fine. Nothing moved. That was the kind of problem that doesn't show up in any tutorial. Here's what you actually need to do. You'll set up a VPN tunnel from your on-premises network into your Databricks workspace using a site-to-site IPsec configuration. Databricks supports this through their Private Link service combined with your own VPN gateway. The general flow is straightforward: create a Databricks workspace in a VNet with private endpoint connectivity, configure your VPN gateway on the on-prem side, establish the IPsec tunnel, then validate that traffic from your data sources flows through the tunnel and reaches Databricks without hitting public endpoints. The critical piece most people miss is the routing table configuration. You need routes on both sides pointing the relevant subnets toward the tunnel. Without proper route propagation, your tunnel is just an expensive pipe that doesn't actually carry anything. I've seen this cause intermittent failures where some queries would work and others would fail depending on which egress point they hit.
For Databricks specifically, you'll want to use their VNet injection feature. This puts your workspace directly into your chosen Azure Virtual Network. Once it's injected, you can apply the same NSG (network security group) rules and routing tables you'd use for any other resource in that VNet. The IPsec tunnel terminates on a VPN gateway that's also in that VNet or peered to it. Traffic from your on-prem sources comes through the tunnel, hits the Databricks private endpoint, and reaches your clusters and jobs. There are two common pitfalls with the Databricks side. First, the workspace needs to be configured for private link before you try to route traffic through it. If you spin up a standard workspace and then attempt to switch to private link mode, you're looking at significant downtime and reconfiguration. Second, make sure your cluster subnets are properly separated from the management plane. Databricks handles control plane traffic through Azure-managed endpoints. You don't want your IPsec tunnel intercepting or blocking those connections. Keep the data plane and control plane paths distinct in your routing design. I ran into a specific issue where our Databricks clusters couldn't reach external artifact repositories because the VPN gateway was applying a default deny route to all outbound traffic. The workaround was adding explicit allow routes for the Azure storage and container registry endpoints that our notebooks needed to pull dependencies from. This took about forty-five minutes to diagnose once I realized the clusters were failing on the import step, not the data ingestion step. The error logs didn't immediately point to networking. They pointed to pip failures, which pointed to DNS resolution, which pointed back to the routing table.
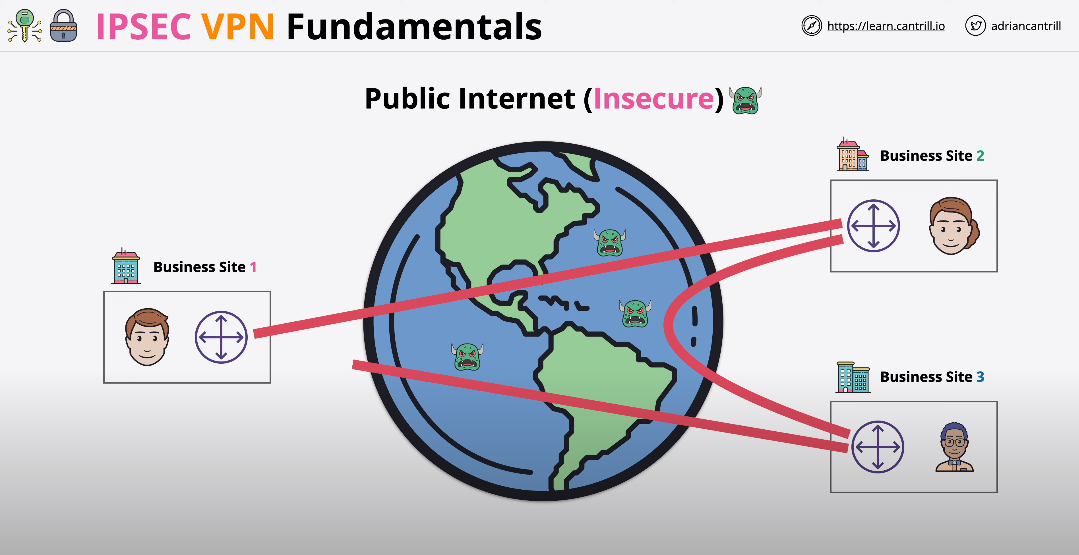
The real value here isn't just encryption in transit. It's network isolation. With IPsec VPN and Databricks private link together, your data never traverses the public internet. That matters for compliance frameworks like SOC 2, HIPAA, and GDPR. It also means you can run analytics on sensitive datasets without creating exposure vectors. Our organization saw our attack surface shrink significantly after this change because we eliminated the public endpoint entry points that third-party data connectors had been using. Performance expectations matter too. IPsec tunnels add overhead from encryption and encapsulation. You're looking at roughly 10 to 15 percent latency increase compared to direct VNet-to-VNet communication. For most analytical workloads this is negligible. Batch ETL jobs that move gigabytes of data might see transfer times increase by a few minutes, but the security gain is usually worth it. If you're running real-time query workloads and latency is critical, you might want to evaluate whether a dedicated ExpressRoute connection would serve you better, though that comes at a substantially higher cost. Monitoring this setup requires attention to a few specific metrics. Check your VPN gateway's tunnel bytes in and out regularly. If you see traffic flowing in one direction but not the other, you've got an asymmetric routing problem. Also monitor the IPsec phase 1 and phase 2 negotiation status. Databricks doesn't expose detailed tunnel diagnostics directly, so you'll rely on the Azure VPN gateway metrics and your on-prem firewall logs to cross-reference what's happening.
Get the Full Details

There are limitations worth stating plainly. IPsec VPN to Databricks isn't a silver bullet. Your on-prem VPN gateway becomes a single point of failure if you don't configure High Availability with dual gateways or active-active tunneling. There's also the operational overhead of key rotation and certificate management. IPsec uses pre-shared keys or certificates for authentication, and those need regular rotation. If you're not already managing VPN infrastructure, this adds a new operational burden. In those cases, evaluating Databricks' built-in Private Link with Azure Firewall or a managed VPN service might be more sustainable long-term. The configuration time for a basic setup is roughly two to four hours depending on your existing network infrastructure. If you're starting from zero with no VPN gateway in place, expect a full day including testing and validation. The ongoing maintenance is minimal once it's stable, but when something breaks, troubleshooting is not trivial. You'll be correlating logs across Azure portal, Databricks workspace events, and your on-prem firewall logs to find the root cause.