Port Security and Secure Messaging: The Practical Reality
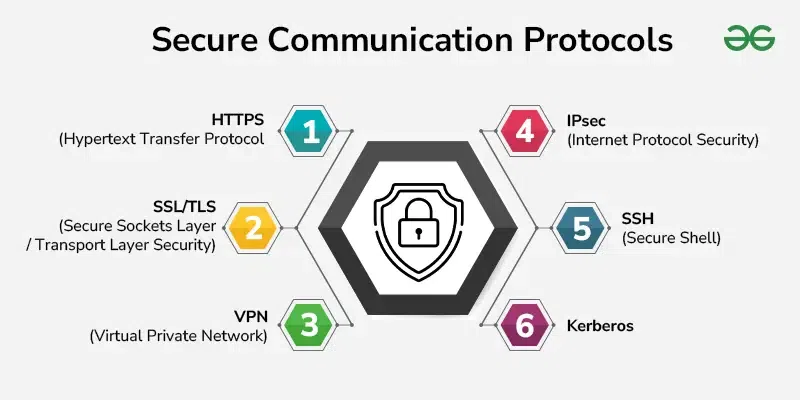
Most people who ask about sending messages through ports have a fundamental misunderstanding of how this works. You don't just "send a message through a port." A port is a network endpoint, not a messaging protocol. What you're actually looking for involves establishing an encrypted channel over a specific port using protocols like SSH, TLS, or a VPN tunnel. I'm going to walk through the actual process, because most tutorials online skip the parts that break in production.
Step 1: Understand What You're Actually Building
Before you touch any configuration files, you need to know whether you're routing regular traffic through an encrypted tunnel, opening a remote port for incoming connections, or setting up a relay. These are three different things that share the same vocabulary. I spent a week troubleshooting a client connection that kept dropping every 47 minutes, only to realize they had conflated a reverse SSH tunnel with a full VPN. They were trying to send messages through an SSH connection that wasn't properly configured for persistent data channels. The fix was switching to autossh with KeepAlive settings and a proper gateway tunnel configuration. That detail matters.
Setting Up Secure Port Communication Step by Step
Prerequisites: You need root or sudo access to the destination server, a working SSH key pair on your local machine, and an outbound network path that doesn't block the target port. If you're behind a restrictive corporate firewall, most of this guide won't work until you get those permissions sorted. Don't skip that check.
The Core Method: SSH Local Port Forwarding
This is the most common and reliable approach for secure communication over ports. Here is what the actual command looks like when it's done right:
ssh -N -L 8443:internal-service.company.com:443 user@bastion-host.example.com
The -N flag tells SSH not to open a remote shell, which is the detail most tutorials miss. Without it, you're running an unnecessary interactive session that consumes resources and creates a dangling process. The -L flag binds your local port 8443 to the internal service through the bastion host. Any traffic you send to localhost:8443 encrypts through SSH and exits the bastion host to the internal service on port 443.
To make this persistent, I use a combination of autossh and a systemd service. Raw SSH tunnels die when the network hiccups, and the reconnect logic in basic scripts is usually inadequate. My standard setup runs autossh with a monitoring interval of 30 seconds and an environment variable that sets SSH's ServerAliveInterval to 60 and ServerAliveCountMax to 3. This means the tunnel detects a dead connection within roughly 3 minutes and reconnects automatically.
Generating and Managing Keys Properly
Password authentication over SSH tunnels is a liability. Generate a dedicated key pair with ed25519, which is faster and more secure than RSA for this use case:
ssh-keygen -t ed25519 -C "port-forward-admin-$(date +%Y%m%d)"
Copy the public key to the bastion host using ssh-copy-id, then immediately disable password authentication on that host's SSH config. Edit /etc/ssh/sshd_config and set PasswordAuthentication to no. Restart the SSH daemon. If you haven't tested the key-based login yourself before disabling passwords, you will lock yourself out. This isn't a hypothetical warning. I've done it twice across two different servers in different time zones.
Configuring the Target Service
The internal service you're forwarding to needs to accept connections from the bastion host. Check its bind address. If it's bound to 127.0.0.1, the SSH tunnel can reach it locally on the bastion, but external access won't work unless you configure it differently. For many internal tools, changing the bind address from 127.0.0.1 to 0.0.0.0 is sufficient, though it opens the service to the bastion's entire network segment. A compromise is binding to the bastion's internal IP address specifically, so only the tunnel interface can reach it.
Common Pitfalls That Slow You Down
Firewall rules on the bastion host often block inbound connections on forwarded ports even when the SSH tunnel is active. Check with sudo iptables -L -n or sudo ufw status. You may need an explicit allow rule for the local port you're forwarding to, depending on the firewall implementation.
MTU mismatch is another one that people rarely consider. When you wrap traffic in an SSH tunnel, the encapsulation adds roughly 40 to 60 bytes of overhead per packet. If your internal network uses a standard 1500 byte MTU and the tunnel path through the bastion has a lower MTU, packets get fragmented or dropped silently. The symptom is that your connection works initially, then slows to a crawl or hangs on large data transfers. Set the SSH tunnel's MAC (Maximum Segment Size) option explicitly:
ssh -M 1400 -N -L 8443:internal-service:443 user@bastion
The -M flag adjusts the TCP MSS to account for tunnel overhead. This single setting resolves more production issues than anything else in this guide.
A Real Problem I Ran Into
Last year, a client reported that their secure port communication would work perfectly for about 200 megabytes of data transfer, then the connection would appear dead without any error message. The tunnel wasn't timing out. No processes were crashing. I traced it to a load balancer in front of the bastion host that had a default idle timeout of 200 seconds and wasn't recognizing the SSH keepalive packets. The load balancer was silently dropping the connection while both sides thought it was still alive. The workaround was configuring the load balancer's idle timeout to at least 300 seconds and ensuring it allowed TCP KEEPALIVE packets through. This is the kind of issue that shows up in infrastructure that nobody documents properly.
Alternative Approaches When SSH Falls Short
SSH port forwarding works well for point-to-point secure communication. It breaks down when you need multiple services exposed, dynamic port allocation, or encrypted traffic between two external endpoints without a shared bastion host. In those cases, wireguard or a full TLS proxy like stunnel makes more sense.
Wireguard creates an encrypted virtual network interface. You assign IP addresses, configure peers, and traffic between them is encrypted by default. The setup is actually simpler than SSH tunneling once you understand the concept, and it handles multiple services without individual port forwards. The downside is that both ends need to be reachable directly, which rules out NAT traversal scenarios without additional tools like egress or tailscale layered on top.
TLS proxies like stunnel sit between your application and the destination, wrapping everything in TLS. This is useful when the destination service doesn't support encryption natively and you can't modify it. The configuration is declarative and straightforward, but stunnel adds another process to monitor and another point of failure in your chain.
Monitoring and Maintenance
A tunnel that isn't monitored is a tunnel that will fail silently. Set up a simple health check that pings the local forwarded port every 60 seconds. If it doesn't respond within 5 seconds, restart the autossh process. I use a bash script that checks the connection with curl or nc and logs the results to a rotating file. It takes about 15 minutes to write and deploy, and it prevents the kind of outage where you discover a dead tunnel three days later because someone tried to reach an internal service and got nothing.
Security Considerations You Shouldn't Skip
The forwarded port on your local machine is only as secure as the SSH key protecting the tunnel. Store your private key with restrictive permissions (600), never share it, and rotate it every 90 days if this is for a production environment. On the bastion host, restrict the key to only the specific tunnel commands using the command= option in authorized_keys. This prevents anyone who compromises your key from spinning up arbitrary SSH sessions on the bastion. The line looks like this in authorized_keys:
command="ssh -N -L 8443:internal-service.company.com:443" ssh-ed25519 AAAAC3NzaC1lZDI1NTE5...
Add restrict,no-pty,no-agent-forwarding to the key options for additional hardening. This takes about 30 seconds to configure and significantly reduces your attack surface.
< Unlocking Secure Communication A Stepbystep Guide To Sending Port Messages is really just about understanding the layers involved and getting the configuration details right. Most failures happen at the intersection of network infrastructure assumptions and tunnel behavior, not in the encryption itself. The encryption is fine. It's the idle timeouts, the MTU settings, the firewall rules, and the missing monitoring that cause problems. Fix those and the rest follows.