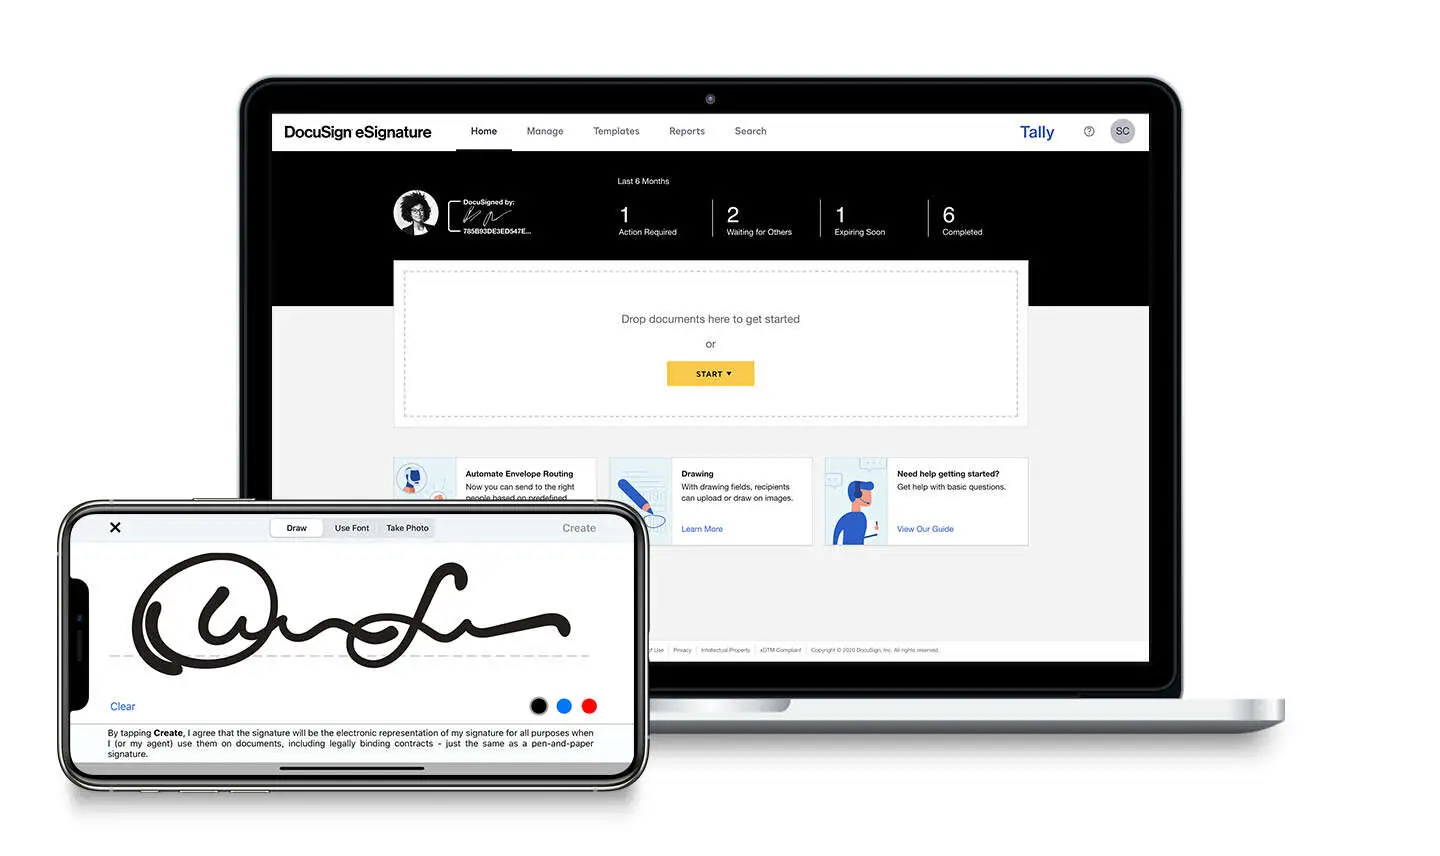
Setting Up Docusign's Developer Environment for Automated Signing
Docusign gives developers a full REST API that lets you send, sign, and manage documents programmatically. The first step is creating a developer account, which you get at docusign.com/lab. Unlike the main sales login, the developer center is free and gives you access to sandbox credentials. You get a client ID and secret within minutes. The main account gives you the ability to build integrations that create envelopes, set tabs, trigger status webhooks, and pull audit trails without any manual intervention. Once you have your sandbox credentials, you authenticate using OAuth 2.0. The authorization code grant flow is the standard method. You construct a redirect URL pointing to docusign.com/e/Authorize with your client ID and requested scopes. The scopes determine what your integration can actually do. If you only need to send documents, requesting the openid profile email scopes is enough. If you want to read templates or access account settings, you need additional permissions. The token endpoint returns an access token that is valid for 3600 seconds. After that, you use the refresh token to get a new one. This matters because most integrations store the refresh token securely and reuse it automatically. I spent about three weeks debugging why certain signed documents would fail validation on the recipient side even though Docusign reported them as successfully signed. The issue came down to certificate profiles. Docusign offers several signing certificate types: DSE (Docusign Standard), CAC/PIV for government ID, and custom certificates that require importing your own PKCS12 file. The default DSE certificate does not embed a signer identity certificate in every PDF. When a receiving system validates the signature using a strict XAdES or PAdES policy, the document fails. The fix was to enable the custom signing certificate profile in the developer account settings and upload a valid certificate from a trusted CA. That added the necessary signing certificate to each signed PDF and made the outputs compatible with systems that enforce higher assurance verification.
Creating Envelopes Programmatically
The core object in Docusign is the envelope. An envelope is a container that holds one or more documents along with recipients, signature tabs, text tabs, and other form fields. To create one, you POST to the envelopes endpoint with a JSON payload. The payload specifies the document bytes, recipients with their email and name, and the tab locations. Tabs can be placed using x and y coordinates, page numbers, or anchor strings. Anchor string positioning uses text like "Signature Here" or "Date Signed" that already exists in your PDF to auto-place tabs. This is useful when you generate documents from a template and cannot guarantee exact pixel positions. Recipients are organized into roles when you use templates. A single template can define an Owner, a Signer, and an Approver role. Your API call just assigns a recipient to each role and fills in the dynamic data. This means you do not need to redefine the entire envelope structure for every transaction. It also keeps the tab configuration consistent across sends, which reduces errors caused by misaligned fields. One thing most guides do not mention is that the document content must be Base64 encoded before you send it in the envelope definition. If you send raw binary or a file path, the API rejects it. The size limit per document is 25MB for sandbox and the same for production. If you are processing large contracts with embedded images, you might need to compress the PDF before encoding it. Failing to compress can push you past the limit and cause the envelope creation to fail silently if your error handling only checks the HTTP status and not the response body.
Status Callbacks and Webhook Reliability
Webhooks are how your application learns about envelope events without polling. Docusign supports status callback notifications for envelope events like sent, delivered, signed, and voided. You configure the webhook URL in the envelope creation payload under the webhookProperties field. The notification includes the envelope ID, the event name, and a timestamp. Your server should verify the request originates from Docusign by checking the signature header. The header uses HMAC-SHA256 over the request body with your integration key. I encountered a situation where a webhook never arrived for a completed envelope. The envelope showed as fully signed in the console but our system had no record of the completion event. The root cause was that the webhook URL was behind a corporate proxy that stripped the Docusign signature header during TLS termination. The fix involved configuring the proxy to preserve the X-DocuSign-Signature header and ensuring our webhook endpoint validated it correctly. Without that validation, accepting webhooks without signature verification is a security risk. Anyone who knows your callback URL could spoof completion events.
Get the Full Details
Common Pitfalls and Limitations
The biggest limitation most teams hit is the rate limit. Sandbox environments enforce stricter limits than production. The default cap is around 10 requests per minute for most endpoints. If you are bulk-sending envelopes or processing a batch of completed documents, you will hit this limit quickly. The solution is to implement exponential backoff with jitter. A simple retry strategy that waits 1 second, then 2, then 4 seconds with a small random component keeps you within bounds without adding significant delay. Another issue is the timezone handling in envelope metadata. Docusign stores timestamps in UTC but many developers forget to convert them when comparing against local business hours. This causes off-by-one-day errors in reports that track signing velocity by region. Store all timestamps in UTC internally and convert only when displaying to users. Docusign also does not support editing an envelope after it is sent. If you need to change a recipient email or add a document, you must void the existing envelope and create a new one. This is a hard constraint in the API. Some teams try to work around this by creating a clone envelope, but that requires reading all the original envelope metadata, copying the documents and tabs manually, and then voiding the first. It is fragile because any field Docusign adds automatically, like envelope ID references or signing order calculations, might not transfer cleanly. Plan your envelope data upfront to avoid this scenario.
The platform is reliable for most standard signing workflows. It handles certificate generation, compliance reporting, and audit trails well. It is less suitable for offline signing scenarios where the signer has no internet access, or for extremely high-volume enterprise deployments where the per-request cost adds up significantly compared to an internal document management system with a simpler signing process. If your use case is mostly internal approval chains with predictable document types, a lightweight library like pdf-sign or a custom PDF stamping approach might be more cost effective. Docusign shines when you need external signing, identity verification, or legal-grade audit trails across multiple organizations.
Practical Tips for Getting Started
Start with the Docusign eSign demo application available in the developer center. It gives you a working UI that lets you send test envelopes without writing code. Use it to understand the request and response structure before building your own integration. The demo app also shows you the exact JSON payload for common scenarios. Store your client secrets in an environment variable or a secrets manager. Never commit them to source control. I have seen multiple teams leak integration keys on public GitHub repositories within days of uploading their code. Use a .env file and add it to your .gitignore immediately. Test thoroughly in the sandbox before switching to production credentials. The sandbox mimics production behavior but isolates you from real signing events. Any envelope you create there will not affect real recipients. Move to production only after your webhook handler, error paths, and token refresh logic are verified end to end.

The documentation at developers.docusign.com is the primary reference. It is generally accurate and updated regularly. The REST API Explorer tool lets you test endpoints interactively with your sandbox credentials, which saves time compared to writing cURL commands from scratch. Use it during development to validate your payload structure before integrating it into your application code.