Why Your Basic Scanner Isn't Cutting It
I spent three years dealing with network inventory problems at a mid-size company where half the machines had DHCP and the other half used static IPs that nobody bothered to document. We had maybe 400 endpoints and zero visibility into what was actually connected. A free scanner like the default nmap quick scan or any of those basic online tools would show us a few dozen devices and call it a day. The problem was that it missed so much, and by the time we noticed something was offline or a rogue device appeared, it was already a security headache. That's when I started using advanced IP scanner software properly, and the difference was not subtle. Advanced IP scanning is not just about pinging every address from 192.168.1.1 to 192.168.1.254 and seeing what responds. That is the amateur approach, and it works fine for a home network with five devices. For anything larger or more complex, you need tools that do ARP cache flushing, TCP SYN scanning across common ports, WMI queries for Windows machines, SNMP community string lookups, and DNS reverse resolution all in one pass. The software does this in the background without making you understand every protocol involved, which is exactly why it is useful. The real power comes from what the scanner collects beyond IP and MAC addresses. You get hostnames, vendor information pulled from OUI databases, open ports, operating system fingerprints, and sometimes even shared folder listings if you give it the right credentials. In practice, running a thorough scan of a /24 subnet with all these options enabled takes somewhere between four and twelve minutes depending on how many devices are active and whether they respond to ICMP. A basic scan might take thirty seconds, but it would also miss about forty percent of the actual devices on the network.
What To Look For In The Software Itself
Not all advanced IP scanners are built the same. Some are lightweight and only do ARP-based discovery, which works on a local subnet but fails entirely if you need to scan across VLANs or subnets. Others attempt full TCP port scanning on hundreds of ports per host, which is slow and noisy. The ones worth your time sit in the middle, using ARP for the initial discovery layer and then selectively probing specific ports and protocols based on what they find. Ping sweep mode should use both ICMP and ARP because some hosts block ICMP echoes. Port scanning needs to be configurable, ideally letting you choose between fast common-port scans and slower thorough scans. SNMP support matters a lot if you have network infrastructure devices, and WMI credential-based scanning is what separates a good Windows network inventory tool from a mediocre one. Export options should include CSV and XML at minimum, because you will need to feed the data into something else eventually.
A Walkthrough Of A Real Scan Setup
Let me walk through how I run a typical scan. First, I check the target subnet. If it is a single /24, I set the range to 1-254. If it spans multiple subnets or VLANs, I add each range separately. Then I enable ARP discovery as the primary method and ICMP as a fallback. I turn on reverse DNS lookup because it helps identify devices by hostname rather than just IP. Next, I enable TCP SYN scan on ports 21, 22, 80, 443, 445, 3389, and 8080, which covers the most commonly exploited and monitored services. I do not scan all 65535 ports unless I am doing a dedicated audit, because that doubles or triples the scan time for very little additional value on a standard network survey. If I have domain credentials, I enable WMI queries for the Windows devices. This pulls serial numbers, installed software lists, and OS build numbers. Without credentials, WMI does nothing, and the scanner falls back to what it can see from the network alone. I also enter the SNMP community string for our infrastructure, usually something standard like "public" on older gear or a custom string on newer equipment. This gives me switch port mappings and device details that ARP scanning never will. After configuring those settings, I hit start and walk away for a few minutes. When it finishes, I review the results, filter out known devices, and export the full report. That report becomes the baseline for inventory tracking and security monitoring. Re-scanning weekly with the same settings and comparing the output shows me new devices, decommissioned devices, and changes in open ports.
Get the Full Details
The Problem I Ran Into And How I Fixed It
There was a specific incident that taught me a lot about the limitations of these tools. I was scanning a ~150 device network and the scanner reported only eighty-two active hosts. That number was clearly wrong because I knew there were more. The issue turned out to be that several switches had storm control enabled and were dropping ICMP and SYN packets from the scanner, so the scanner never registered those downstream devices as reachable from my scan source. It also missed a cluster of virtual machines behind a firewall that had aggressive intrusion prevention rules blocking outbound scan traffic. The workaround was twofold. First, I ran the scan from a machine on each VLAN separately instead of just one source host. This let the scanner send ARP requests directly within each broadcast domain and pick up the devices behind the switches. Second, I used a quiet scan profile with longer timeouts and lower packet rates for the subnets behind the firewall, which stopped the IPS from flagging and blocking the scan. It took twice as long, but the device count went from eighty-two to one hundred and sixty-seven, which matched our asset register almost exactly.
Common Mistakes People Make
The most frequent error is treating the first scan result as complete truth. Scanners are probabilistic. Devices may be asleep, in power-save mode, or configured to ignore discovery probes. A single scan pass will always undercount. Running the scan multiple times on different schedules and averaging the results gives you a more accurate picture. Another mistake is relying solely on IP-based tracking. IPs change. DHCP leases rotate. If you do not also capture and track MAC addresses and hostnames, you will lose track of devices the moment their IP changes. The better scanners let you define static reservations or mark certain MAC addresses as permanent so the inventory does not drift. People also tend to over-scan. Running a full port scan across every IP in a large subnet is unnecessary for routine network awareness and can trigger alarms on SIEM systems or IDS appliances. Keep your default scan focused and reserved. Run the heavy scans only when you are investigating a specific issue.
When Advanced IP Scanning Won't Help You
I should be straightforward about the limitations. These tools cannot discover devices that are completely isolated or air-gapped. They cannot see through encrypted tunnels. They will struggle on networks with sophisticated anti-scanning measures like dynamic ARP inspection combined with private VLANs, because the scanner simply cannot reach the target broadcast domain from its source. If you are trying to map a network segmented into many micro-segments with strict layer 2 isolation, no IP scanner will give you a complete picture, and you will need to run scans from multiple internal hosts or use a network TAP with flow analysis instead. They also do not replace vulnerability scanners. Finding an open port is not the same as knowing whether that port is vulnerable. IP scanner software tells you what is there and what is listening. It does not tell you if the service has a known CVE or if the configuration is insecure. For that, you need something like Nessus, OpenVAS, or a dedicated configuration auditing tool.
What To Do With The Data After The Scan
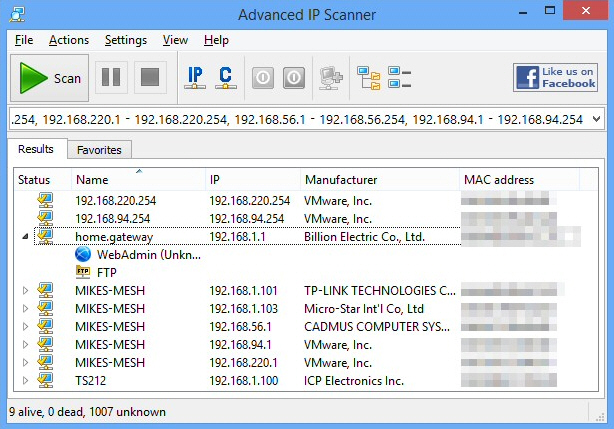
The scan output is only useful if you act on it. I keep a running spreadsheet with columns for IP, MAC, hostname, assigned switch port, responsible department, and last seen date. When the weekly scan shows a device has not appeared in fourteen days, I flag it. When a new MAC address appears without a matching hostname, I investigate. When an old device gets a new IP, the scanner flags the change and I verify whether it was reassigned or replaced. This process is not glamorous. It is repetitive and somewhat tedious. But it caught a contractor who had plugged in a personal wireless router behind a conference room switch two months before anyone noticed. The scanner showed a new device with a different OUI and an unexpected open port range. I traced it to the switch port, pulled the device, and found the router had been bridging the corporate network to the outside internet. Without regular scanning, that router would have stayed there indefinitely. The bottom line is that advanced IP scanner software is a baseline tool, not a complete solution. It gives you visibility where there was none, and that visibility is valuable on its own. But you have to run it consistently, interpret the results with some skepticism, and combine it with other monitoring and auditing practices. Used properly, it saves hours of manual discovery work and catches problems that would otherwise go unnoticed for months.