Setting Up OpenDNS for Your Network
I spent years watching people chase DNS-based ad blockers and parental controls before discovering OpenDNS. Most of them set it up wrong. The configuration itself is straightforward, but the places where it breaks are not obvious. I will walk you through what actually happens when you deploy this, what you need to know before you do, and the one edge case that cost me two hours of troubleshooting on a client network. OpenDNS is a domain name system service owned by Cisco. It sits between your device and the rest of the internet, resolving domain names through their servers instead of your ISP's default resolvers. That single change gives you filtering, phishing protection, and a dashboard showing query logs. The interface is dated. The backend still works reliably.
Unlocking Internet Control And Insight With Opendns A Comprehensive Guide
The free tier handles most home use. You create an account at opendns.com, add your network, and then switch your DNS settings to point at OpenDNS resolvers. The primary IP is 208.67.222.222 and the secondary is 208.67.220.220. That is it for basic setup. You can log into the dashboard afterward and turn on categories like adult content, malware, and phishing under the Security tab. For organizational use, there is the OpenDNS Intelligence plan and the OpenDNS Gateway product, which add more granular controls. These require a subscription and some additional configuration. The free tier is sufficient if you just want to block known bad domains and see what traffic looks like on your network.
How The Filtering Actually Works
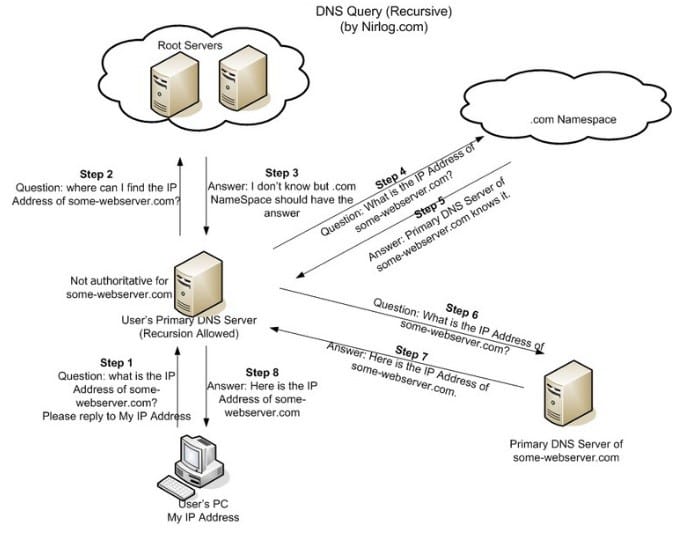
When someone on your network types in a website address, their device sends a DNS query to the OpenDNS server you configured. OpenDNS checks that domain against its blocklists. If the domain is flagged for malware, phishing, or whatever category you have enabled, OpenDNS returns a blocked page IP instead of the real destination. The browser loads the OpenDNS block page. That is the entire mechanism. There is no packet inspection, no SSL decryption, no deep packet analysis happening here. Just DNS-level filtering. This also means certain things simply cannot be filtered at this layer. Encrypted domains through HTTP Strict Transport Security or private resolvers that bypass your configured DNS will not show up in your logs. If someone on your network configures a device to use Cloudflare's 1.1.1.1 or Google's 8.8.8.8 directly, OpenDNS has no visibility into that traffic. I ran into this on a small business network last year. The owner complained that the dashboard showed almost no activity after we enabled it. Turned out the office Wi-Fi had a DHCP option that was handing out Google DNS instead of the OpenDNS IPs we had set up. The fix was removing that DHCP override and making sure the router pushed the correct DNS addresses to all connected devices.
Get the Full Details
Configuration Methods
There are three ways to actually get OpenDNS on your network. The method you choose depends on your equipment and how much control you want. Router-level configuration: Log into your router admin panel, find the DNS settings, and replace the ISP-assigned DNS with the OpenDNS IPs. This covers every device on the network automatically. It is the cleanest approach. Not all routers let you change DNS at the router level though. Some consumer-grade units lock this down or revert to ISP defaults on reboot. Check your router documentation before committing. Individual device configuration: You can set OpenDNS on each computer, phone, or tablet manually. This gives you per-device control but is tedious and easy to mess up. If you forget one device, that device bypasses your filtering entirely. I only recommend this for isolated systems or when router-level changes are not possible.
DHCP-based push: If your router supports it, you can configure the DHCP server to hand out OpenDNS IPs automatically. This combines the coverage of router-level configuration with the convenience of zero manual device setup. Most modern routers support this. Verify that your router's DNS push settings are actually working by checking a connected device after configuration.
Using the Dashboard
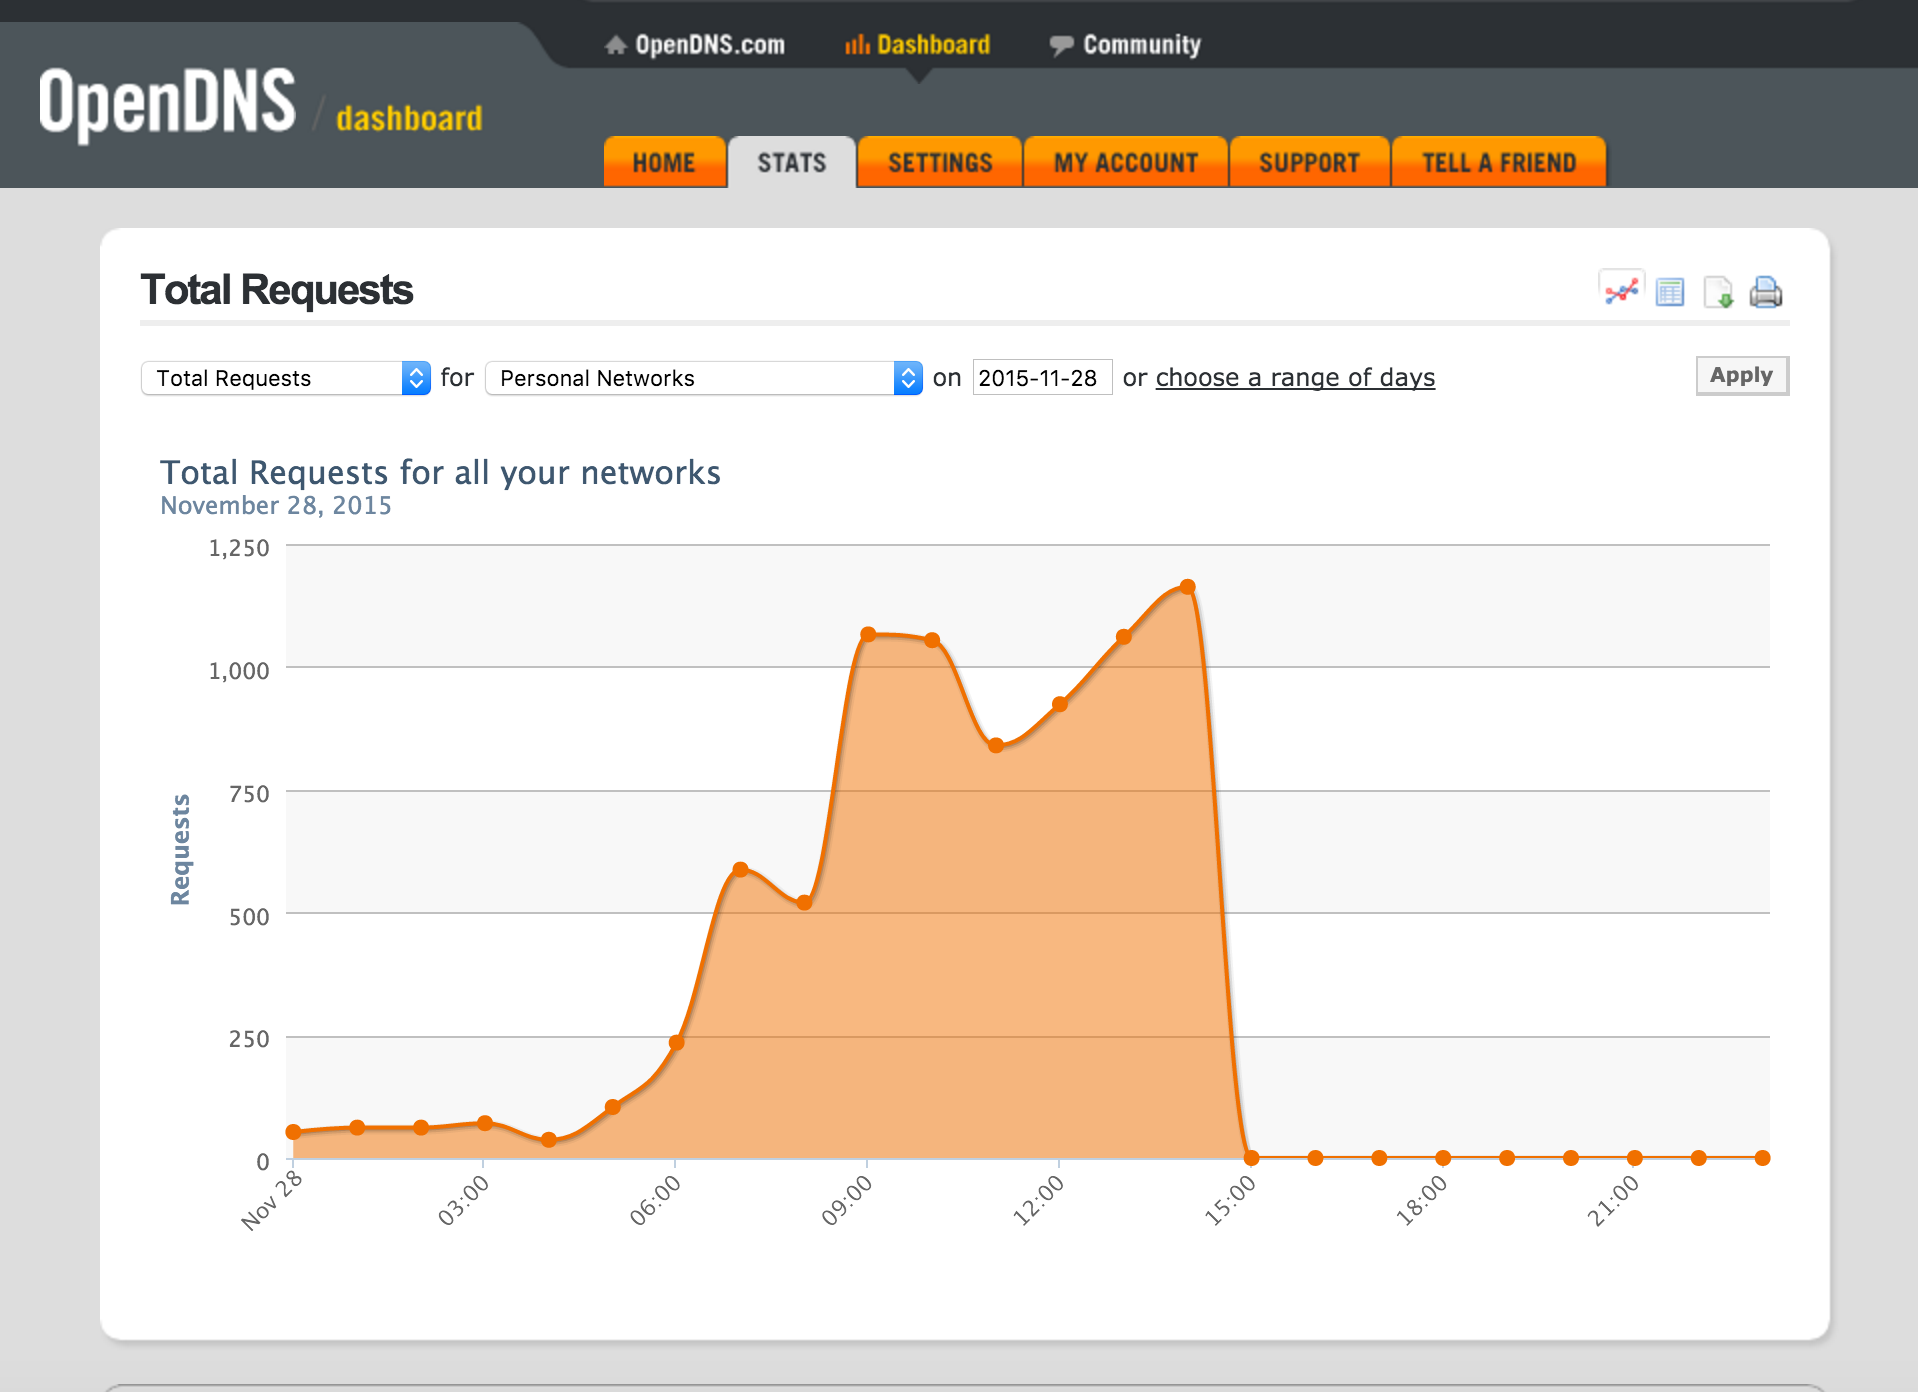
Once your network is pointed at OpenDNS, log into your account and explore the dashboard. The homepage shows recent queries, blocked requests, and category breakdowns. You can drill into specific time ranges and filter by category. The interface is not particularly fast, but it gets the job done. Under the Security tab, you can toggle phishing and malware protection. Under the Parental Controls tab, you can block or allow specific categories. The blocklist and allowlist features let you add individual domains. This is useful for edge cases like enterprise software that uses questionable-looking domains for legitimate purposes. I once had to add a domain to the allowlist because a medical practice's scheduling software was being blocked as suspicious. The vendor never responded to the abuse report, so we whitelisted it and moved on. The Reports section gives you more detailed data. You can export query logs if you need them for compliance or auditing. Be aware that free accounts have limited log retention. Subscription tiers increase this, sometimes significantly.
Common Problems and Workarounds
OpenDNS blocks certain domains that are perfectly legitimate. Streaming services, some cloud platforms, and enterprise software often trigger false positives. The workaround is always the same: add the domain to your allowlist and document why you did it. Without documentation, you will forget and waste time re-allowlisting later. Another issue is cached DNS records. If you change your OpenDNS configuration and a device still resolves through old DNS, it may be using a cached entry. Flush the DNS cache on the device. On Windows that is ipconfig /flushdns. On macOS it is sudo dscacheutil -flushcache; sudo killall -HUP mDNSResponder. On Linux it depends on your resolver implementation. This fixed a client's issue where half the network was unaffected and the other half was still hitting the ISP's DNS after we switched everything to OpenDNS. The affected machines had stale cache entries from before the change. Sometimes OpenDNS itself has outages. They are rare but they happen. During an outage, legitimate domains may return block pages or fail to resolve entirely. There is no workaround except waiting it out or temporarily switching back to your ISP's DNS. I keep a backup DNS list saved somewhere accessible for exactly this scenario.
Limitations You Need to Accept
OpenDNS does not filter encrypted traffic content. It only sees the domain name being resolved, not what happens after the connection is established. If a site uses HTTPS, OpenDNS knows you visited example.com but cannot inspect what you did on that site. This is a fundamental limitation of DNS-level filtering, not a bug in OpenDNS specifically. The free tier has reduced logging retention and fewer filtering categories compared to paid plans. If you need detailed analytics or compliance-grade reporting, you will eventually hit the free tier ceiling. The Gateway product is more capable but requires more technical knowledge to configure properly. DNS-based filtering can be bypassed by anyone who knows how. A technically competent user can configure their device to use alternative DNS resolvers, use DNS-over-HTTPS, or run a local DNS proxy. If you need to prevent determined users from circumventing your filters, OpenDNS alone will not suffice. You would need to combine it with firewall rules, forced DNS enforcement, or a full proxy solution.
When OpenDNS Is Not the Right Tool
If you need deep content inspection, SSL decryption, or application-level control, look at solutions like pfSense with DNS filtering plugins, Pi-hole combined with adguard, or commercial secure web gateways. OpenDNS fills a specific niche. It is easy to deploy, requires minimal ongoing maintenance, and provides decent baseline protection. It is not a comprehensive security solution. Treating it as one will get you in trouble. For most home users and small businesses, the free tier handles the common cases. Set it up at the router level, configure the categories you care about, monitor the dashboard periodically, and adjust allowlists as needed. The setup takes about ten minutes. Understanding what it can and cannot do takes longer, but that knowledge saves you from false assumptions down the road.