Getting Into Your Exostar Account When Everything Feels Broken
Exostar's secure access platform has always been one of those things your security team makes you use without explaining why it exists. The login process itself is straightforward enough if nothing goes wrong. The second something goes wrong — and it usually does — you're navigating a maze of federation providers, expired tokens, and MFA challenges that seem designed to frustrate. Here is the actual sequence that works when your company uses Exostar SecureAccess for file transfers or identity management. I have walked through this enough times across different organizations to say which parts matter and which parts are just theater. Start at your organization's specific Exostar portal URL. Not the generic exostar.com page. Your company provisions a dedicated subdomain or branded login path. If you are landing on the public-facing site, you are already off track. Type in the URL your IT or security team gave you, which typically looks something like yourcompany.exostar.com or a similar pattern depending on how they configured their tenant.
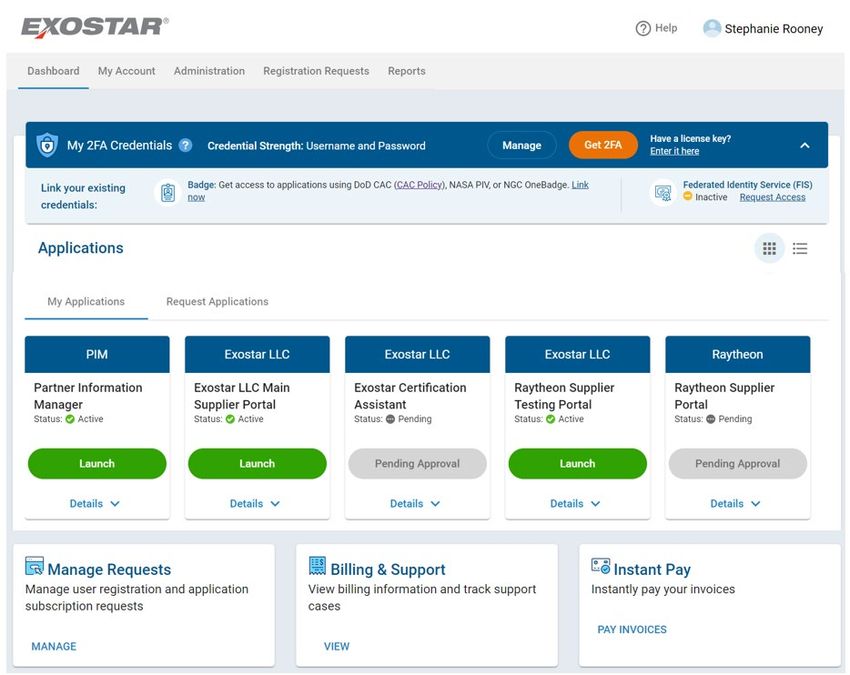
The login page will ask for your corporate credentials first. This is almost always SAML-based federation, meaning it redirects you to your organization's identity provider. If you work at a large company, this is probably Okta, Azure AD, or maybe a legacy LDAP setup. Click through the redirect. Authenticate however your company requires — password, MFA app, biometric, whatever. Then you get bounced back to Exostar with a SAML assertion. This is where most people hit problems. The SAML callback fails silently half the time because your browser has stale cookies from a previous session, or your identity provider's metadata has rotated and Exostar's side hasn't been updated to match. If you get a red error screen after the redirect, clear all cookies for both your IDP domain and the Exostar domain, then try again from an incognito window. It sounds trivial but it solves the majority of "I can't log in" tickets I see in support forums. Once the SAML handshake completes successfully, you land on the SecureAccess dashboard. From there, the interface branches depending on what your organization actually uses Exostar for. Most common scenarios are managed file transfer, partner onboarding, or regulatory document exchange. The menu structure is not intuitive. Look for the "Transfers" or "Files" tab if you are moving documents, or "Partners" if you are trying to connect with an external organization.
One thing that catches people off guard: Exostar uses a concept called "access zones." Your organization configures different zones for different types of data or different partners. If you log in and see an empty dashboard, you are likely in the wrong zone or your account hasn't been provisioned for the zone you need. Contact your Exostar administrator inside your company — not Exostar support, your internal admin — and ask them to verify your zone assignments. This is not something you can fix yourself. For MFA, Exostar supports several methods but your company picks which ones are enabled. Common options include the Microsoft Authenticator app, RSA SecurID tokens, or one-time codes sent via SMS. If you enrolled in an MFA method and it is no longer working, the reset process goes through your IDP, not through Exostar directly. Go back to your corporate identity provider's portal and remove the old MFA registration, then re-enroll. Exostar will detect the change on your next login attempt. Here is the edge case that burned me for weeks. My organization migrated from on-premises AD to Azure AD, and our Exostar tenant was still configured to trust the old AD FS endpoint. Every login worked perfectly up until the SAML callback, where it would fail with a generic error. Exostar support couldn't see the issue because from their side everything looked normal. The problem was entirely on our internal side. The workaround was to have our cloud administrator update the SAML metadata URL in the Exostar tenant configuration and regenerate the signing certificate. Took about twenty minutes once we identified it, but finding the root cause took a month of back-and-forth between three different support teams who all insisted the problem was elsewhere.
Get the Full Details
If you are setting up Exostar for the first time as an administrator, do not skip the session timeout configuration. By default, Exostar sessions are fairly short-lived, typically thirty minutes to an hour depending on your org's policy. For teams that do manual file uploads involving multiple steps, this creates a real productivity drain. You spend twenty minutes filling out transfer forms, click submit, and the session has already expired. Set the idle timeout appropriately for your use case, but balance it against your compliance requirements. Some regulations explicitly require shorter sessions for systems handling sensitive data. Another practical tip that nobody mentions: Exostar's bulk transfer feature is genuinely useful but it requires a specific CSV format that is not well documented in the built-in help. If you need to upload multiple files for a single transfer, export a properly formatted template from an existing transfer, fill in your new data, and import it. The field names matter exactly as shown. Custom fields get dropped silently if the headers do not match character for character. I have seen people spend hours manually entering fifty files when a properly formatted CSV would have done it in ten minutes. The audit logging in Exostar is thorough but the export format is frustrating. It dumps everything into a flat CSV with no real filtering options beyond date range and username. If you need to pull logs for a specific transfer or partner, you are looking at massive files you have to parse manually. I use a simple Python script with pandas to filter by transfer ID and date, then summarize by status. Takes five minutes to set up and saves hours later when compliance asks for something specific.
Password resets go through your organization's standard procedure, not through Exostar. If you forget your password, do not waste time on the Exostar "forgot password" link. It may not even be configured correctly in your tenant. Go straight to your IT helpdesk or your IDP's self-service portal instead. Browser compatibility is another area where Exostar makes assumptions that are not always right. The platform works on Chrome, Firefox, and Edge, but certain enterprise configurations of these browsers with strict cookie policies can cause intermittent failures. If your login works sometimes and not others with no clear pattern, check your browser's cookie and site data settings. Third-party cookie blocking is the usual suspect, especially since SAML flows inherently involve cross-domain redirects. Add both your Exostar domain and your IDP domain to your browser's allowlist for cookies. Mobile access through the Exostar app exists but it is limited compared to the web interface. File uploads work, but bulk operations, custom form filling, and some administrative features are not available on mobile. If your workflow requires mobile access for transferring files on the go, test it thoroughly before relying on it. I have seen people try to complete urgent transfers from their phone only to discover the app cannot handle the specific transfer type they need.
The biggest practical limitation of Exostar that I have encountered is its partner management workflow. Onboarding a new external partner involves multiple approval steps, and the system does not send proactive notifications when a pending approval sits unattended. If your organization has slow-moving approval chains, assume a transfer is stuck until you confirm someone actually clicked approve. Setting up a shared inbox or a regular review cadence for pending partner requests prevents the "my transfer has been stuck for two weeks and nobody told me" scenario. Update frequency for the platform itself is reasonable but changes are sometimes introduced without advance notice. If a feature you relied on stops working after what seemed like no changes, check the Exostar release notes. They publish updates periodically and a deprecation you were not aware of might be the cause.