Setting Up Skyward Employee Access Across Your District
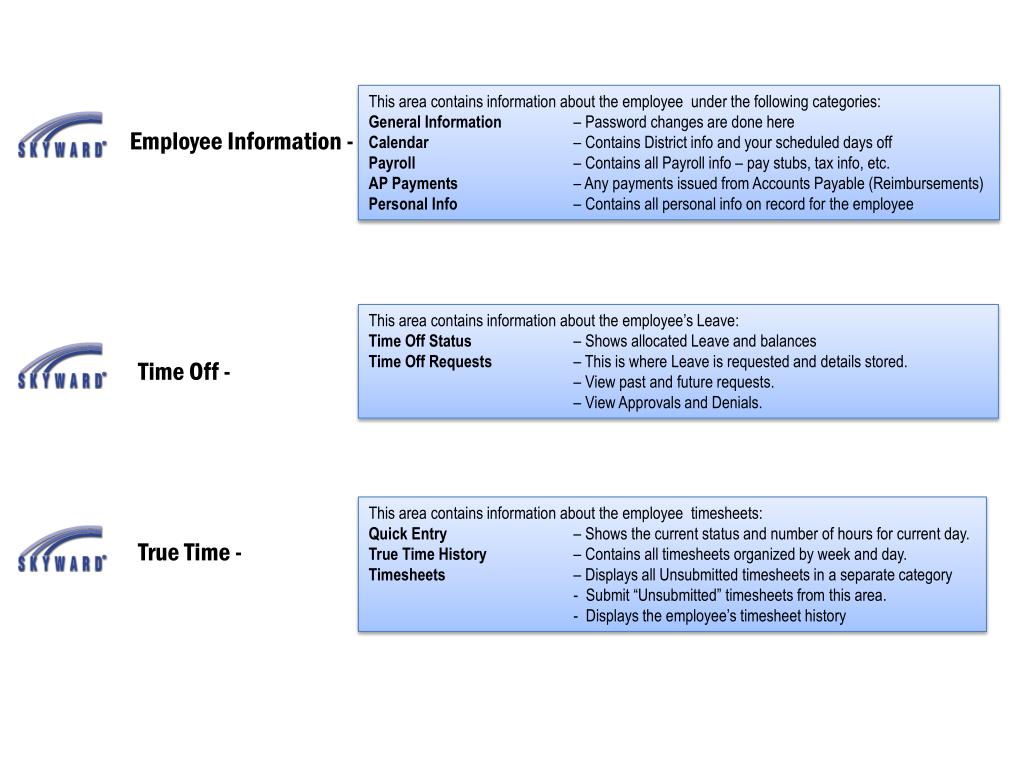
I spent three weeks wrestling with Skyward Employee Access at my last district. The documentation was vague, the support tickets went nowhere, and by the time I figured out how to batch-enable staff logins without breaking the SSO handshake, I had enough scars to write this down for someone else. Skyward Employee Access is essentially the gateway layer between your student information system and the staff who need to get into it. It handles authentication, role-based access, and permission mapping. In a typical Texas ISD with 5,000 to 15,000 employees across multiple campuses, getting this configured cleanly is what separates a smooth start-of-year from three months of helpdesk tickets about password resets and missing permissions.
Unlocking Efficient Employee Management The Power Of Skyward Employee Access Iltexas
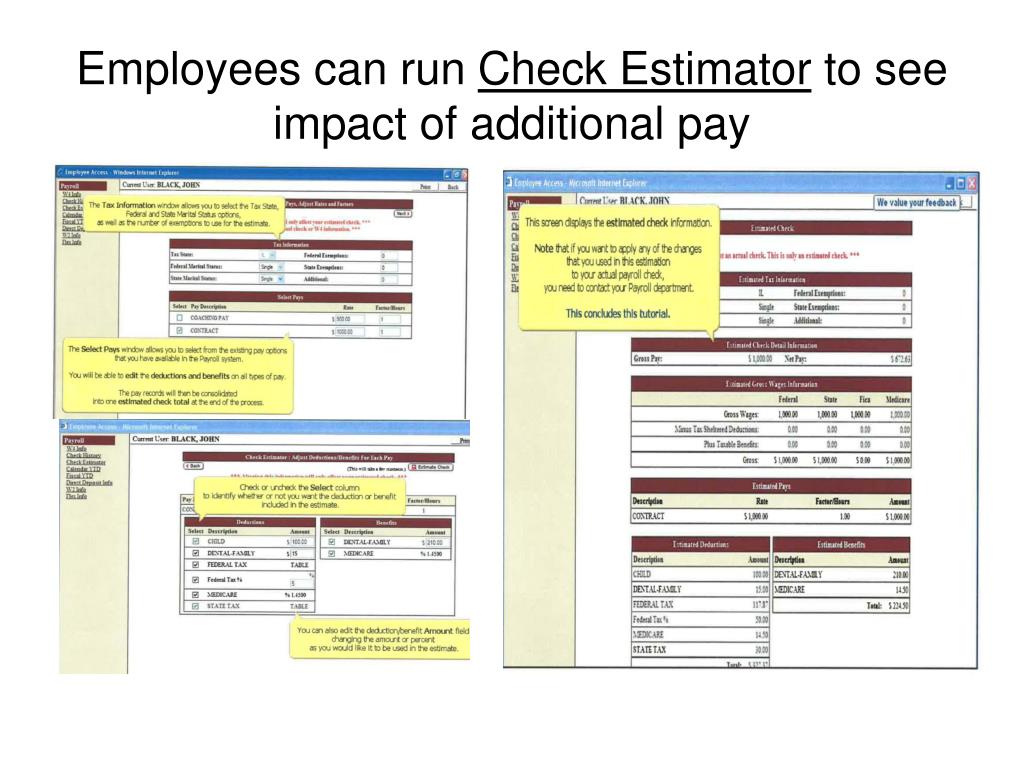
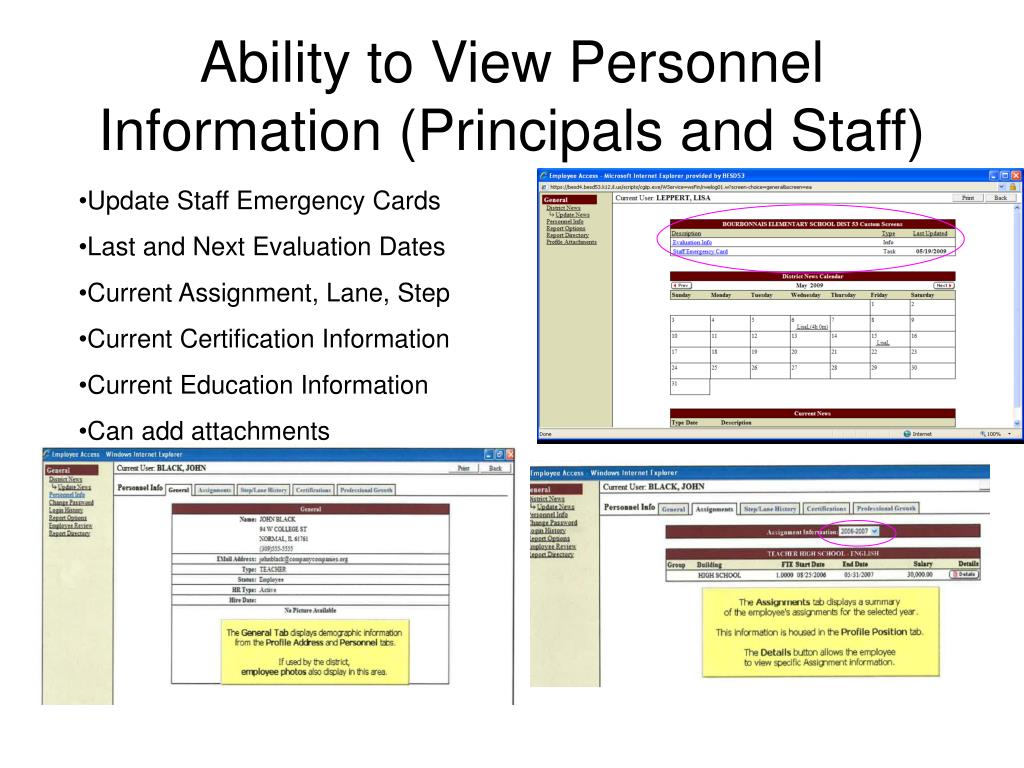
The real value isn't just in the login screen. It's in the permission matrix that flows downstream. When you set up Skyward Employee Access correctly, a new hire gets auto-provisioned to their campus, their role (teacher, admin, custodian) maps to exactly the right modules, and access expires on their termination date without anyone touching it. That's the theoretical model. Here's what actually happens. You start with your HR data feed. Skyward pulls employee records from your HRIS—usually SAP, Workday, or a spreadsheet dump—via FTP or API depending on your contract. Each employee record has a unique identifier, a campus code, a position code, and a status flag (active, leave, terminated). The trick is making sure those position codes map correctly to Skyward's role taxonomy, which isn't standardized across implementations. I found that the default mapping in Skyward's Texas deployment assumes a certain hierarchy of campus roles that doesn't match how most districts actually organize positions. A teacher aide might show up as "instructional support" when it should be "faculty," and that single misclassification blocks access to gradebooks, attendance, and the parent portal. The fix is creating custom role mappings in the Employee Access admin console, which lives under System Administration > Security > Role Mapping. You spend about two days on this step alone if you're thorough.
Next comes the SSO integration. Most Texas districts use Azure AD or Okta for single sign-on. You configure Skyward as a service provider, set up the attribute mappings for email, employee ID, and department, and test the redirect flow. The authentication handshake between Azure and Skyward's access layer uses SAML 2.0, and if your metadata XML is off by even a field or two, users will get a generic "access denied" error with zero diagnostic information in the logs. After SSO is working, you move to the permission sets. Skyward organizes permissions into three tiers: system-level (what modules you can see), function-level (what actions you can perform within a module), and data-level (which records you can access). A principal at a 600-student campus should see their school's data but not other schools. A district-level HR director sees everything. The common mistake is granting "super user" to campus admins because it's easier, which creates data leakage and compliance headaches down the line.
Get the Full Details
What I Wish I Knew Before Starting
The first thing I didn't understand was that Skyward Employee Access doesn't sync in real time. The HR data feed runs on a schedule—usually nightly—and changes to employee status don't take effect until the next cycle. If you terminate someone in the morning and expect them locked out immediately, you're wrong. They'll have access until the sync runs. I worked around this by setting up an automated script that queries the Skyward API and revokes suspicious sessions in real time, though this required a separate service account with elevated privileges that took three support tickets to get approved. The second thing is that role mapping errors compound. One misclassified position code cascades into missing permissions across every module that role depends on. I learned to run a validation report after each feed—System Administration > Reports > Role Coverage Report—which shows you which employees have zero mapped roles and which have overlapping roles that create conflicts. Running this report cut my helpdesk tickets from about 40 per day during the first week of school down to roughly 3 per day by week three.
Known Limitations and Workarounds
Skyward Employee Access has real bottlenecks. The permission model is rigid—you can't create granular data-level filters based on custom fields like "program enrollment" or "transportation zone." If your district needs to restrict access to sub-populations within a campus, you're out of luck with the native tooling. The workaround is building custom reports in Skyward's reporting module and distributing them manually, which adds overhead but gets the job done. Another limitation is the lack of audit trail granularity. You can see that someone logged in and accessed a module, but you can't trace which specific records they viewed or edited. For districts under federal audit or handling FERPA-sensitive populations, this gap matters. The workaround I used was enabling third-party monitoring through Azure Sentinel, which ingests Skyward's auth logs and provides the drill-down visibility that the native platform doesn't offer. The SSO setup also doesn't support multi-factor authentication natively within Skyward. You have to rely entirely on your identity provider's MFA policies. This is fine for most districts, but if you have contractors or subcontractors who shouldn't be in Azure AD, you need a separate guest access configuration that Skyward's documentation barely covers.
Practical Deployment Timeline
If you're rolling this out for a new school year, here's what I'd budget. Week one: HR data feed configuration and position code mapping. Week two: SSO integration with your identity provider. Week three: permission set creation and testing across representative user profiles. Week four: validation report review and helpdesk team training. If you hit the role mapping issues I described, add two more weeks. The total configuration time for a mid-sized Texas district—around 8,000 employees across 60 campuses—runs about 160 to 200 staff hours. That's not including the ongoing maintenance, which averages 10 to 15 hours per month for feed monitoring, new hire provisioning, and role changes when staff move between campuses or positions. I've seen smaller districts try to do this themselves with minimal Skyward training and end up spending six weeks and burning through their IT budget on consultant hours to fix the mistakes. If you have internal staff with experience in identity management and a willingness to dig into the configuration console, it's very doable. If not, budget for a partner who's actually deployed this at scale rather than one who's only configured it once during onboarding.