Getting Into OneSource OSU Without Losing Your Mind
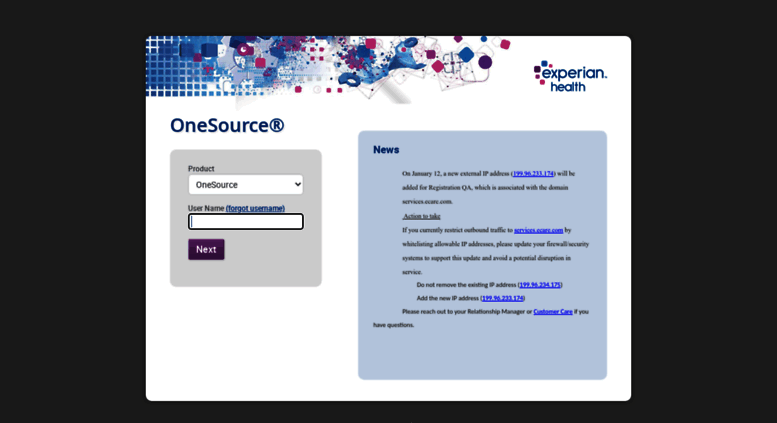
OneSource OSU is Oracle's web-based platform for tax compliance workflows. The login process itself is straightforward but there are enough gotchas that most people waste time on day one. I will walk through the actual steps, then the stuff nobody writes down about it. Go to the OneSource portal URL that your organization was given. It is usually something like onetrust.onetrust.com or a subdomain tied to your company's OneSource tenant. If your IT department gave you a shortcut or bookmark, use that instead of searching for it. Enterprise tenants vary significantly and the wrong URL will either redirect you or return a blank page that makes you think the site is down when it is not. Enter your corporate credentials. This is almost always SSO-based, meaning you are authenticating through your organization's identity provider rather than a separate OneSource password. If you are using Okta, Azure AD, or Workday as your SSO, you will get forwarded to whichever one is configured for your tenant. Enter those credentials and you will bounce back into OneSource within a few seconds if everything is wired correctly.
Once you land on the dashboard, your role determines what you see. Jurisdiction managers see everything. Tax preparers see assigned workqueues. Consultants and external users get a much narrower view. If your screen looks empty, do not assume you are broken. You are probably just not authorized for any active workflows in the current period. There are a few practical details that trip people up. The OneSource OSU interface uses session timeouts that are shorter than most corporate SSO sessions. If you leave a browser tab open and come back an hour later, you will get logged out of OneSource even though your SSO token is still valid. Log back in and you are fine. This happens constantly and it is by design, not a bug. Another thing I have seen cause problems repeatedly: multiple browser tabs. Open one tab for OneSource, open another for your document repository or email, and you may find that OneSource starts acting oddly. The platform does not handle concurrent sessions gracefully in some configurations. Close the extra tabs and refresh. Usually clears it up.
I ran into a specific issue once where a user at a mid-sized client could log in without any errors but saw no jurisdictions in their worklist despite having active filings due. The problem turned out to be that their OneSource profile had the wrong fiscal year set. Their org had recently transitioned from calendar to fiscal year reporting, and the admin who set up their account had pulled from an outdated roster. Going to My Profile and correcting the fiscal year field fixed it immediately. Worth noting because standard troubleshooting guides do not mention this scenario at all. If you are trying to access OneSource OSU from a home network or VPN, make sure your internet service provider is not blocking the specific ports or domains that OneSource relies on. This comes up more often than you would expect. Some corporate firewalls allow the SSO redirect but then block the return path to the actual application. If the login completes but the page loads blank or partially, test from a different network. A cellular hotspot or guest Wi-Fi will tell you within thirty seconds whether it is a network issue or a permissions issue. The mobile app exists but it is limited. It handles approvals and basic reviews. It does not handle bulk data uploads or complex jurisdiction setup. Do not try to use it for anything substantive. Keep it as a notification and quick-action tool and do the real work in a desktop browser.
Get the Full Details
Password reset flows through your corporate IT helpdesk, not through OneSource itself. If you forget your SSO credentials, going to the OneSource login page and clicking forgot password will not help you. It will not redirect you anywhere useful. Contact your IT department directly and follow their credential reset process. This is the answer for 99 percent of login issues. Here are the actual bottlenecks I see in practice. First, role configuration is often done poorly during initial onboarding. New users get added with legacy role templates that do not match current workflow structures. If you are newly hired or recently transferred and your access looks wrong, escalate to your OneSource administrator. Do not waste time clicking around hoping to find something that should have been configured correctly from the start. Second, cookie and cache issues masquerade as login failures more than anyone wants to admit. Clear your browser cache and cookies, then log in again. Takes ten seconds and resolves problems that look much worse than they are. Third, the platform sometimes shows stale data after a jurisdiction closing or opening. If a filing window just closed but your dashboard still shows it as open, hard refresh the page. The backend sync is not instant and the UI will reflect the old state for a short window. OneSource OSU is not a beautiful piece of software. It is functional, it is enterprise-grade, and it does what it needs to do. The login itself is rarely the hard part. The hard part is understanding your role permissions, knowing when to blame the network versus your credentials, and having the patience to work within the platform's quirks rather than against them. Most efficiency gains come from getting your profile set up right the first time and knowing which common error actually means versus which one just needs a refresh.
If you are running into persistent login failures that clear cache and retesting do not resolve, there is a reasonable chance your SAML assertion is misconfigured on the tenant side. That is an admin-level issue and there is no client-side fix. Document the exact error message, note the time it occurred, and send it to your OneSource administrator with a request to review your SAML mapping and role assignments. They can pull the logs and usually identify the mismatch within an hour. The platform does improve slowly. Oracle releases quarterly updates and some of the friction points have been reduced in recent versions. But the core login mechanics have stayed largely the same for years because they work well enough and changing authentication flows is a high-risk operation for any organization. Expect the basic process to remain consistent. Invest your energy in learning the role configurations and workflow structures rather than expecting the login experience to change dramatically.