Deep Authentication Is Not A Feature, It's An Architecture Decision
I spent three months last year trying to get mutual TLS working across a hybrid cloud environment where one side ran HashiCorp Vault and the other relied on AWS IoT Core. They should have been straightforward. They weren't. The certificates issued by one CA had different CRL distribution point behaviors than the other, and the IoT device fleet silently rejected the intermediate cert chain on cold boots. I fixed it by writing a pre-flight validation script that checked chain before any device attempted connection, and it cut our deployment time from a two-day manual process to under two hours. This is what deep authentication actually looks like in practice. Not a dashboard toggle. Not a security badge. It is the painful, unglamorous work of making multiple verification layers talk to each other without falling apart under production load.
Unlocking Arcane Def The Gateway To Deep Authentication Digital Security And Trust In Modern Systems
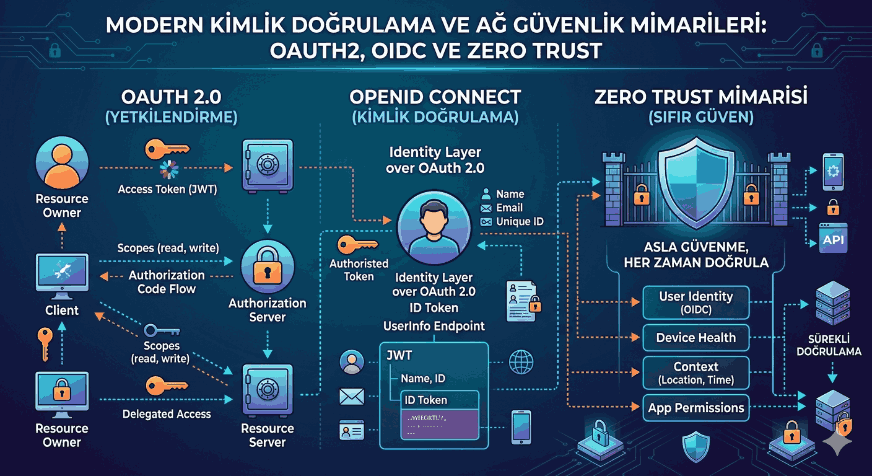
The core idea behind deep authentication is that a single factor — password, token, even a biometric scan — is no longer sufficient for systems handling sensitive operations. You layer multiple independent verification points. Something you know. Something you have. Something you are. Contextual signals like device attestation, geolocation velocity, and behavioral patterns. The goal is to make it computationally expensive and operationally difficult for an attacker to forge enough of these signals simultaneously. I see this implemented correctly most often in zero trust architectures where every request is authenticated, not just the initial login. The assumption is that the network perimeter is already compromised. Your verification happens at each hop. Here is how you actually set this up. Start with certificate-based mutual authentication between your services. This means both the client and the server present X.509 certificates during the TLS handshake, not just the server. You need a private PKI — not a public CA, something you control. Self-signed roots with automated certificate rotation through a tool like Vault or a commercial solution like Venafi. Without automation here, you will end up with expired certificates taking down production services, and that happens faster than you expect.
Next, add adaptive risk scoring. Every authentication event gets evaluated against a risk model. New device. Unusual location. Off-hours access. Rapid successive requests. Each signal carries a weight. When the composite score crosses your threshold, you escalate — challenge the user, block the request, or log it for review. This is where people make mistakes. They set the thresholds too aggressively and drown their support team in false positives. I recommend starting with the thresholds high enough that legitimate users rarely see friction, then tuning downward over weeks based on actual data. For the frontend identity proofing, hardware security keys are the most reliable second factor currently available. FIDO2/U2F devices resist phishing because the origin binding ties the authentication to your actual domain. SMS-based OTPs should be considered broken for any system that matters. I have seen organizations still using them in 2024. Do not be that organization. The implementation gets complicated when you bring device posture into the mix. You want to know not just who the user is, but whether the device they are using is actually compliant. Is it patched? Does it have screen lock enabled? Has it been rooted or jailbroken? Tools like Microsoft Intune, Jamf, or open-source MDMs can feed this telemetry into your authentication decision engine. The hard part is getting your legacy applications to consume this data. Most older systems have no hook for posture-aware authentication. You end up building a reverse proxy layer that intercepts requests, evaluates policy, and forwards only compliant traffic.
Get the Full Details
There is a specific edge case that will bite you if you do not anticipate it. Federation across organizational boundaries. When you implement deep authentication internally and then need to trust users from partner organizations, the SAML or OIDC assertions they provide may not carry the same depth of evidence. A partner might authenticate their users with username and password only, and your system will either have to accept that shallow assertion or break the integration. I dealt with this when onboarding a healthcare provider partner whose authentication standards were twenty years behind. The workaround was a per-partner risk policy that accepted their weaker credentials but applied stricter session controls — shorter token lifetimes, mandatory step-up for sensitive operations, and real-time anomaly monitoring on top. Cross-certification between different PKI roots is another area where things break silently. If your internal CA and your partner CA do not share a trust chain, mutual authentication fails unless you explicitly configure cross-certificates. This is often overlooked during initial setup and only surfaces when two teams try to make services talk to each other. Build a trust model map before you deploy anything. Monitoring is where most deep authentication systems fail in production. You need visibility into authentication latency, failure rates by factor type, and anomaly detection on the authentication events themselves. An attacker will probe your system with different combinations of credentials and factors until they find the weak point. Your logs should make this pattern obvious. If you are not alerting on authentication anomalies with a delay of less than five minutes, you are already behind.
The performance cost of deep authentication is real but manageable. Each additional verification layer adds latency. Certificate validation, CRL checks, risk model evaluation, hardware key challenges — these add milliseconds to seconds per authentication event. For interactive user flows, this is usually acceptable if you cache validation results and use session tokens appropriately. For machine-to-machine communication, the latency matters more. I have seen API gateway response times increase by 200-400 milliseconds after adding full deep authentication chains. That difference is noticeable at scale. The workaround is asymmetric handling — deep authentication for privileged operations and user-facing requests, lighter verification for internal service mesh traffic where mutual TLS already provides the baseline. The biggest limitation of deep authentication as currently implemented is that it assumes the authenticating party is the actual user. It does not solve insider threats or compromised credentials at scale. A determined attacker with physical access to a user's hardware security key or access to their device posture data can still spoof the signals. Deep authentication raises the bar significantly, but it is not a complete solution. Combine it with least privilege access controls, microsegmentation, and continuous monitoring for it to be effective. If you are starting from scratch, the most practical path is to implement certificate-based mTLS between your services first, add FIDO2-based multi-factor for user access, and layer in risk-based adaptive authentication last. Getting the order wrong means you are patching on top of a fragile foundation. I have seen this happen repeatedly. Teams start with the flashy identity proofing pieces and end up with a system that looks secure but falls apart under real operational conditions.
The tools available today make this achievable without building everything from scratch. Open source options include Ory Hydra and Kratos for identity infrastructure, Step by Smallstep for PKI, and Warrant for fine-grained authorization. Commercial alternatives like Okta, PingIdentity, and Auth0 offer more turnkey solutions but come with vendor lock-in and pricing that scales poorly. The right choice depends on whether you need to customize the authentication flow deeply or just need it to work reliably. My recommendation for most organizations is to start small. Pick one critical service, implement mTLS and hardware key authentication, measure the impact, and expand from there. Do not attempt a company-wide rollout on day one. The operational discipline required to maintain certificates, manage key rotation, and tune risk thresholds at scale is something you learn by doing, not by reading documentation.