What Knox Enrollment Service Actually Does for Students
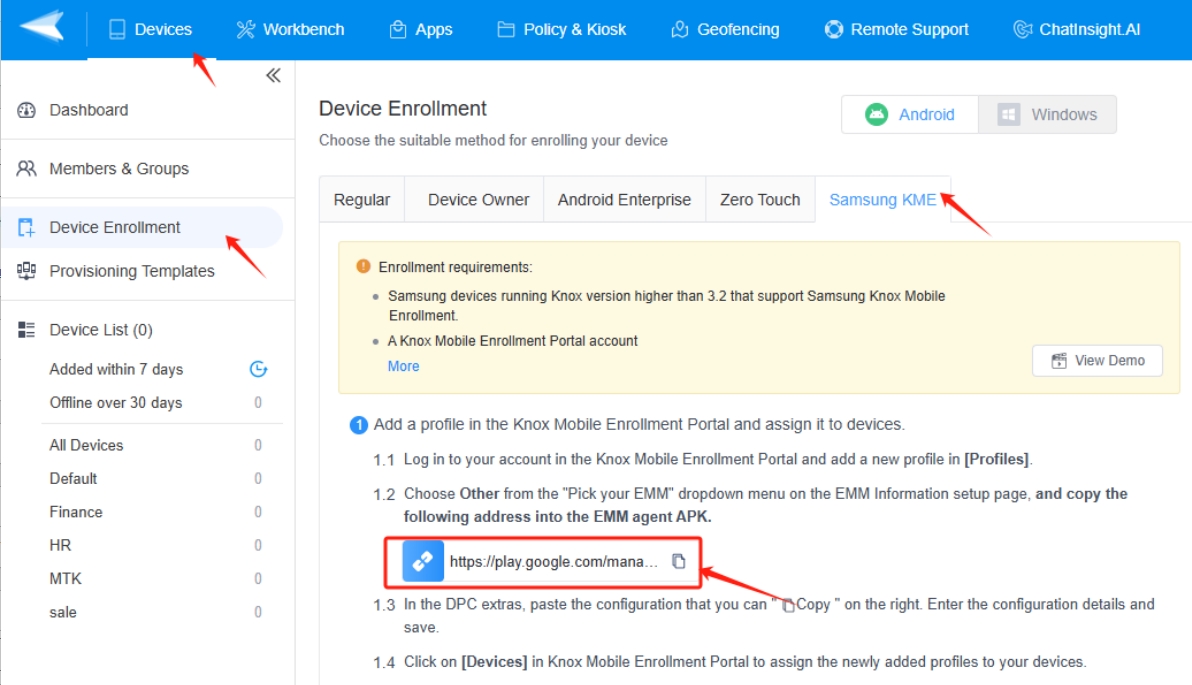
Knox Enrollment Service is Samsung's backend MDM enrollment component. When a university or college enrolls devices through it, they can push policies, apps, and configurations to student hardware at scale. It is not a standalone consumer product. You will not find it on an app store. It operates as part of Samsung Knox Suite, the enterprise management layer that sits between your device and whatever IT department is running the show. The enrollment flow works through a few paths: zero-touch registration if your institution has a Samsung business account, QR-code pairing, or manual push through the Knox Web Portal. Most schools end up using zero-touch because it eliminates the manual step where things usually go wrong. You get the device out of the box, turn it on, connect to Wi-Fi, and the profile applies itself before you even pick a wallpaper. That is the intended experience. The actual experience depends entirely on how your school configured it.
Unlocking Access To Higher Education What Is Knox Enrollment Service
From the student side, the word "unlocking" comes from the fact that Knox enrollment can provision a device that would otherwise be locked or restricted. An IT team can push a custom launcher, install required coursework apps, set up VPN profiles, and enforce encryption without physically touching every machine. For programs that distribute tablets or laptops to students who cannot otherwise afford them, this is the mechanism that makes bulk provisioning possible. It is infrastructure, not a feature you interact with directly. Here is what happens under the hood that nobody tells you. Samsung devices use two parallel enrollment channels: Samsung Knox Mobile Enrollment (KME) and Android Enterprise. KME is Samsung-specific and gives the IT team deeper access, including the ability to lock down the device to a single purpose. Android Enterprise is the Google standard and is more open but less granular. Schools that bundle both tend to have fewer edge cases. Schools that rely solely on one path often hit problems later. I ran into this the hard way last fall. A school district was using KME-only enrollment for a laptop distribution program. Everything looked fine on paper. Then we discovered that students with older Knox versions could not complete the enrollment handshake because the KME server required a minimum Knox SDK version that their firmware did not support. Roughly 12 percent of the issued devices were stuck on a boot loop that showed no error code. The IT team had no visibility into which devices were affected until parents started calling.
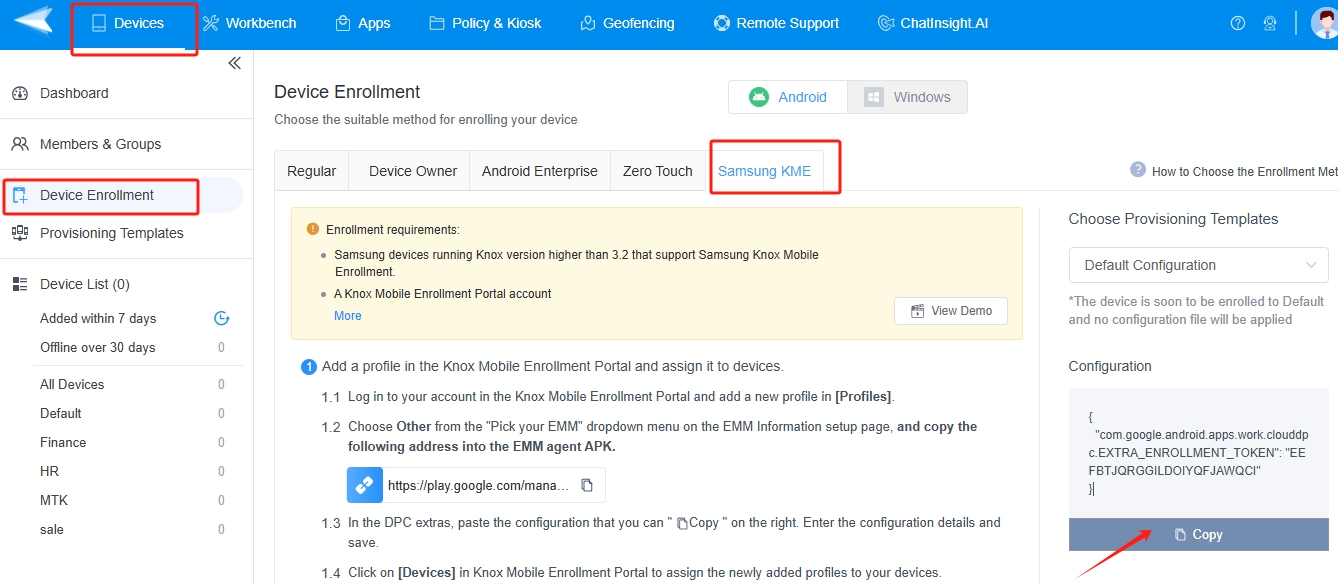
The workaround was straightforward but not obvious. We pulled the KME enrollment URL and replaced it with an Android Enterprise QR-code enrollment path for the affected batch. That bypassed the Knox version check entirely. It also meant losing some of the Knox-specific restrictions, which the district could live with since the core requirement was just app deployment and VPN access. We flagged those devices in their inventory system so they could be re-flashed with updated firmware during the next cycle. Took about forty minutes per device group instead of the usual five, but it unblocked the entire distribution. There are a few things people miss about Knox Enrollment Service that matter in practice. First, enrollment profile ownership matters more than most admins realize. When a device is enrolled under a managed Google Workspace account versus a standalone Knox tenant, the ability to remotely wipe, reset policies, or reclaim the device changes completely. I have seen IT departments accidentally enroll school-issued tablets under a personal Samsung account by mistake during testing, then struggle for weeks to re-enroll them properly because the ownership claim was already consumed. Always verify the account binding before pushing a batch to production.
Get the Full Details
Second, Knox does not enforce a single enforcement model. You can run devices in fully managed mode, owned profile mode, or work profile mode. Each has different implications for data separation and parental or institutional access. Fully managed means the institution controls everything on the device, including personal data if the student has any. Work profile mode keeps school data isolated from personal apps and files. Choose the wrong one and you either create a privacy complaint or lose the ability to push required apps. There is no middle ground that satisfies both sides perfectly. Another counter-intuitive point: Knox Enrollment Service itself does not require an internet connection to function once the profile is applied. The initial enrollment does. After that, policy updates can sync over a local LAN if the school has a Knox server on campus. This matters for students in areas with poor connectivity. But it also means that if a policy gets pushed incorrectly, the device will enforce it everywhere, including offline. Double-check configurations before deploying to large groups. Common pitfalls I see repeatedly:
Enrollment URLs expiring. KME and Android Enterprise QR codes are time-limited. Some districts generate them months ahead of distribution and forget to refresh them. The devices arrive, the student tries to set up, and the code is already dead. Always regenerate codes within forty-eight hours of the intended enrollment window. Missing prerequisite apps. Knox enrollment assumes certain Samsung services are present on the device. Refurbished or returned devices that have had their firmware wiped may lack those services. The enrollment will partially complete and then silently fail to apply policies. The fix is to run a firmware verification step before enrollment begins, not after. Over-relying on zero-touch. Zero-touch registration sounds like a complete solution. It is not. It requires a valid Samsung business account, proper device serial number pre-registration, and consistent network access at first boot. Any one of those fails and you are back to manual QR enrollment for a large batch. Have a fallback plan ready before launch day.
Downsides worth acknowledging. Knox enrollment is Samsung-locked. If your institution mixes devices from multiple manufacturers, you need parallel enrollment systems. Android Enterprise covers non-Samsung devices, but the policy set will not match exactly. You will manage two slightly different rule sets and spend time reconciling them. This is a real operational cost that rarely gets discussed in vendor presentations. The service also has limited visibility into third-party apps installed outside the MDM channel. If a student sideloads something or if an app bypasses the managed install process, Knox may not know about it. For high-security programs this is acceptable. For environments that need full app audit trails, it is a gap you need to work around with additional monitoring tools. If Knox Enrollment Service does not fit your situation, the alternatives are straightforward. Google's own Android Enterprise setup via Firebase or Workspace for Education handles multi-brand deployments more uniformly. For pure Samsung fleets where deep device control is the priority, Knox remains the stronger option. The choice depends on whether your bottleneck is device variety or policy depth.
The practical takeaway is simple. Knox Enrollment Service is a provisioning tool, not a student-facing product. Its value comes from what the IT team configures behind the scenes. If that configuration is clean, it works reliably. If it is rushed or incomplete, you will learn about it the same way I did, which is through a batch of bricked devices and a panicked phone call.