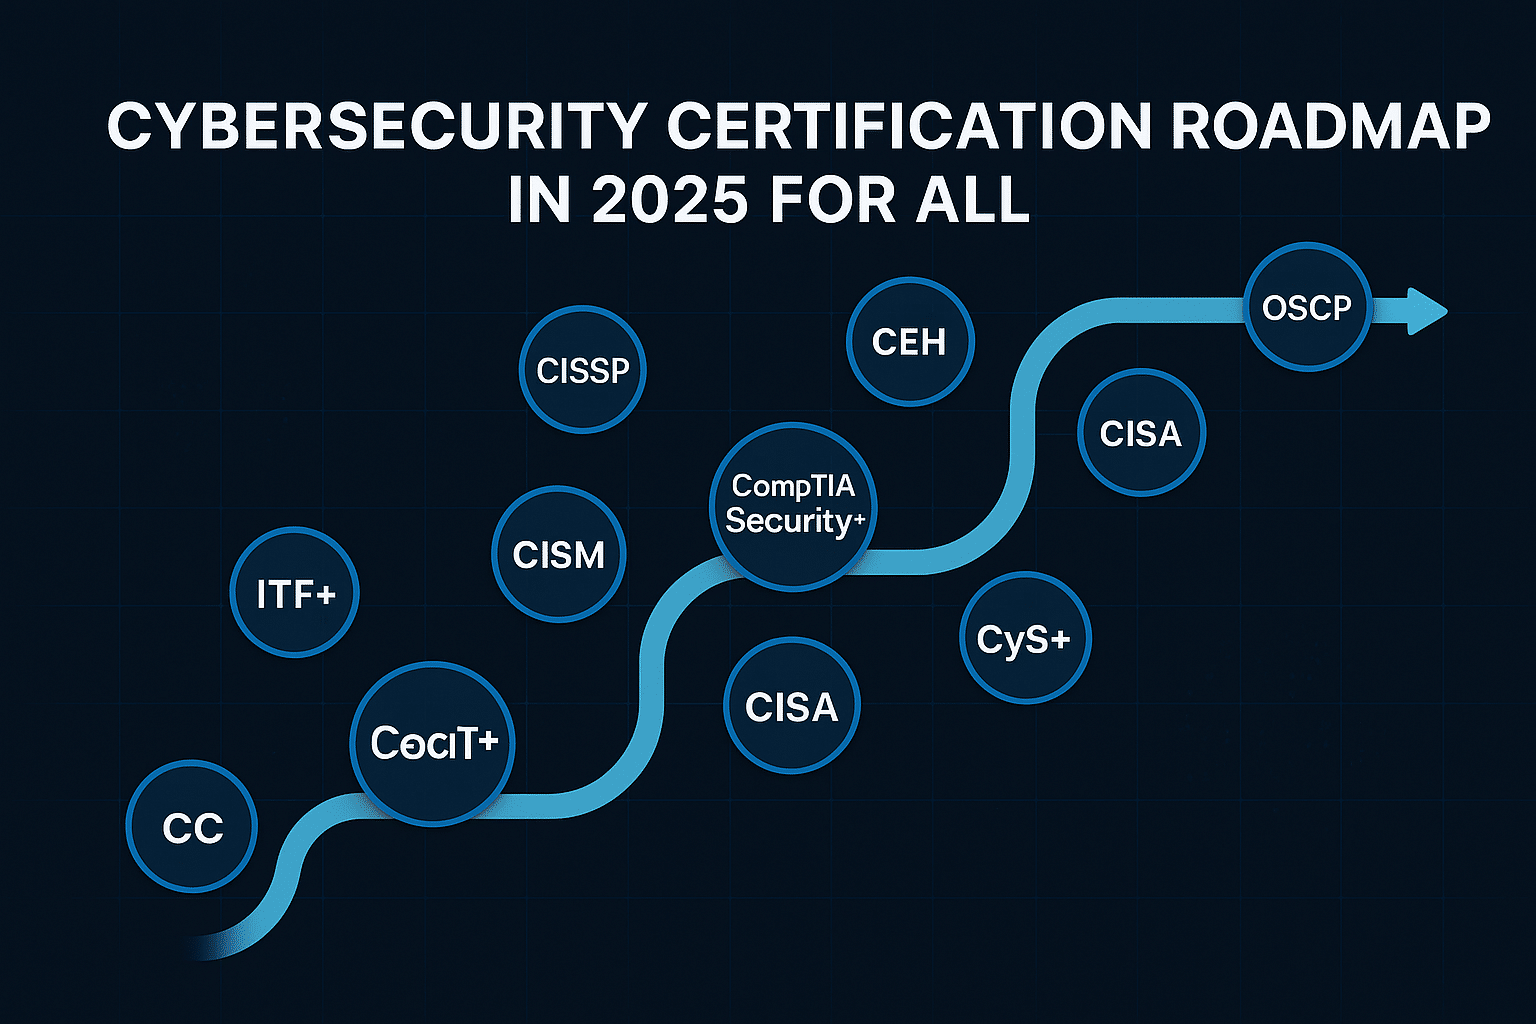
Getting a Security Certification Isn't Simple, But It's Doable
Most people approach certification roadmaps with the wrong expectation. They think picking one exam and studying for six months will unlock a career change. That rarely works out cleanly. The reality is messier, and the people who figure this out early tend to build stronger careers because of it.Unlock Your Cybersecurity Future Your Security Certification Roadmap
Let me walk through how I actually navigated this space, including where the standard advice falls apart. The problem isn't that certifications are hard. It's that there are too many of them and they overlap in confusing ways. CompTIA Security+ covers infrastructure basics. CISSP assumes you already know infrastructure basics and then tests your ability to make decisions under ambiguity. SANS/GIAC exams are brutally detailed. CEH is more about methodology than hands-on skill. Starting without a filter means burning money and time on exams that don't move the needle for where you actually want to go. I once wasted three weeks studying for the CISSP because I had pre-ordered the review course before I'd even confirmed I met the experience requirement. The exam itself was a slog of best-practice scenarios where every answer felt reasonable. I passed, but the cert didn't open any doors for me at the time because I didn't have the five years of documented security work experience attached to it. That's a structural limitation of CISSP — it certifies your knowledge, not your actual job readiness. You can study your way through most of those questions using elimination strategies alone.
The Practical Sequence I Recommend
If you're starting from near zero, here's the order that actually compounds instead of wasting effort: Step 1: Network+ or equivalent practical networking knowledge. You cannot secure what you don't understand. This takes about 4-6 weeks of part-time study if you've never touched networking. The exam covers OSI model, TCP/IP, subnetting, basic routing. Don't skip it. I've interviewed plenty of candidates who claimed Security+ on their resume but couldn't explain what happens when a packet traverses a VLAN across two switches. Step 2: Security+. This is the gatekeeper cert. HR systems use it as a keyword filter. It's coverage is broad but shallow, which is exactly what you need at this stage. Budget 8-12 weeks studying. Use Professor Messer's free videos, the Sybex study guide, and perform cert practice exams until you're scoring 85%+ consistently. The real world version of this material is incident response and basic hardening — the exam won't tell you that, but it should.
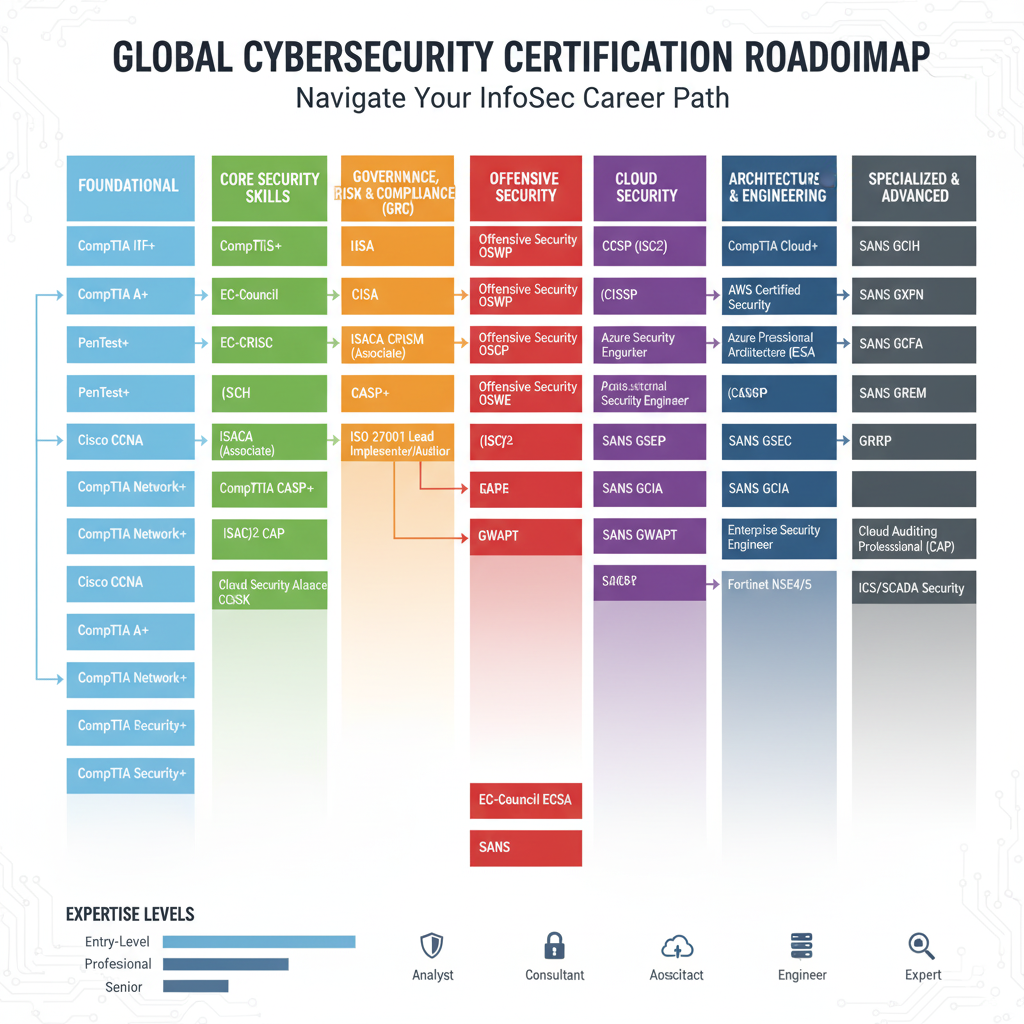
Step 3: Pick a specialization track. This is where most roadmaps fail because they don't have this step. You're either going toward operations and blue team work, architecture and governance, or offensive security and red teaming. Each path has a different next exam. For operations: SSCP or Security+ retention path, then move toward CySA+ or SANS's FOR500 series. For architecture: CISSP, but only after you have the experience hours. For offensive: CEH is the HR checkbox, but OSCP is the actual skill validator. I'd recommend skipping CEH entirely if your goal is real technical competence. It tests recognition more than execution.
Get the Full Details
What Nobody Tells You About the Exam Process
CISSP uses CAT (computerized adaptive testing). That means the exam gets harder or easier based on your answers. If you miss a question, the next one tends to be slightly easier. If you nail a question, the next one gets harder. People who treat it like a static exam often undershoot because they don't adjust their pacing. I learned this the hard way during my second attempt — I spent too long on early questions trying to be perfect, which tanked my confidence trajectory through the adaptive algorithm. OSCP is completely different. It's 24 hours of hands-on penetration testing against real machines. You get a report template and you're graded on both the technical exploit and your written documentation. The pass rate hovers around 55-60%. The key insight most beginners miss: the exam machines are vulnerable to the same public exploits documented in penetration testing methodology guides. The challenge isn't finding the vulnerability — it's documenting it clearly enough that the grader can verify it in your report. I failed my first attempt not because I couldn't root the boxes, but because my methodology section was disorganized and incomplete. The second time I structured my notes as I went, following a consistent template for each machine, and passed on the retake.
The Real Bottleneck: Experience and Credibility
Certifications get you past HR filters. They do not replace experience. The cybersecurity hiring market is genuinely saturated at the entry level right now, and certifications alone won't differentiate you. Here's what actually works: Build a home lab. Not a metaphorical one — set up actual virtual machines, configure vulnerable applications like Metasploitable, run SIEM tools like Wazuh or Elastic Stack, practice detection engineering. Document everything publicly on a blog or GitHub. I've seen candidates with just Security+ land interviews because their GitHub showed practical hands-on work that proved they could actually do the job, not just pass a multiple-choice exam. Contribute to open-source security tools. Even small contributions — documentation fixes, bug reports, minor feature additions — carry more weight than a third-row certification stacked behind Security+. Recruiters and hiring managers recognize genuine engagement with the community.
Where Certifications Completely Fail You
Here's the blunt part: no certification prepares you for the actual day-to-day work in most security operations centers. You'll spend more time writing tickets, chasing false positives, and dealing with stakeholder communication than you will applying the technical material from any exam. CISSP teaches you to think like a manager, which is valuable if you're moving toward CISO-track roles, but it won't help you triage an alert at 2 AM when your SIEM is throwing 4,000 events because a misconfigured firewall rule is firing on loop. GICSP, GSEC, and other SANS certifications are technically rigorous but expensive — often $8,000+ per course when you include the training. The ROI is real if your employer pays, questionable if you're self-funding at that price point. For self-funded candidates, the CompTIA lineage and off-price options like eJPT for hands-on security fundamentals deliver better cost-to-value ratios in the early career stages.
A Note on Timing and Investment
A realistic timeline from zero to employable with certifications looks like 12-18 months of dedicated part-time study alongside building practical skills. Budget $500-1,500 total for entry and mid-level exam fees if you pass on the first attempt. CISSP alone is $749. OSCP is $1,649. SANS courses are in the $8,000 range. Factor in study materials — books, practice exams, subscription labs — and you're looking at roughly double the pure exam fees if you buy everything properly. The people who succeed treat certifications as one input in a much larger system. The system includes hands-on practice, networking within the community, documented proof of skill, and patience through a market that currently favors candidates who can demonstrate actual capability over those who can only demonstrate test-taking proficiency.