Unlock The Secrets Of Your Network With Advanced Ip Scanner Free Download
Samantha
2026-03-30
Why I Keep Coming Back To Advanced IP Scanner
Most people search for a network scanner and end up downloading something bloated with ads or bundled malware. I've been through that. The thing that keeps me reaching for Advanced IP Scanner is that it actually does one job and does it without trying to sell you antivirus three months later. It's Russian-made software that sits quietly in your system tray while it scans, and the results are clean enough for professional use.
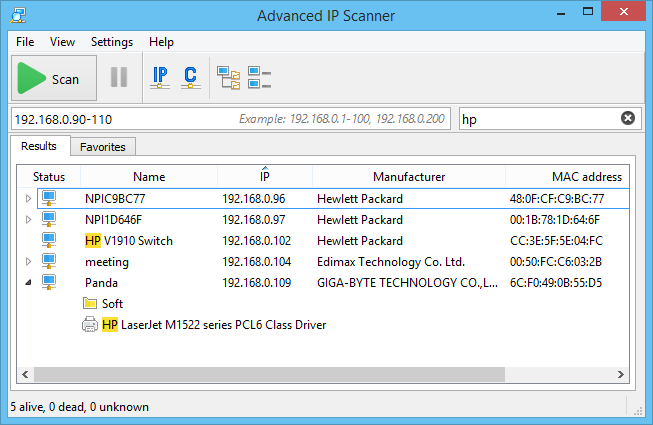
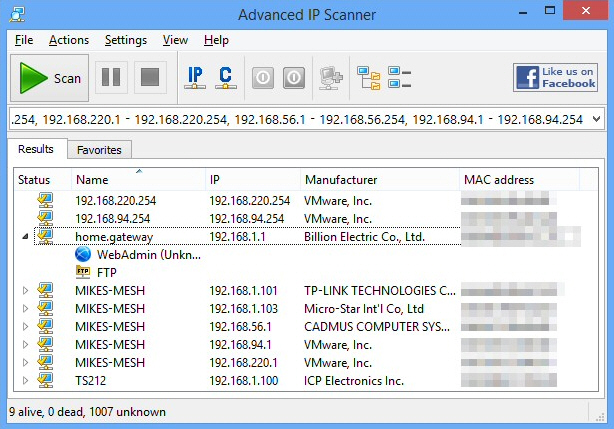
The interface looks like it hasn't been redesigned since 2008, and honestly that's a feature. No animations, no onboarding tutorials, just a toolbar and a results table. You type in your subnet range, click start, and walk away. When it finishes you have a complete inventory of every device on your network with hostnames, MAC addresses, and open ports. That's it.
Unlock The Secrets Of Your Network With Advanced Ip Scanner Free Download
Getting the software is straightforward. Go to the official f-secure site and look for the download link near the top of the page. Don't click the third-party download portals that pop up in search results. Those repackage the installer and add toolbars. The official version is around 6 megabytes and installs in about thirty seconds on a modern machine.
Once installed, open it and you'll see a configuration panel on the left side. The default settings work for most home and small office networks. The scan speed slider lets you control how aggressively it probes each IP. If you're scanning a /24 network with maybe thirty active devices you can leave it on fast. If your network has hundreds of devices and you're worried about flooding switches with ARP requests, drop it to medium or slow.
The real value shows up when you run a scan and the results populate. Every device gets color-coded by manufacturer based on the OUI portion of the MAC address. Apple devices show up in one color, Cisco in another, TP-Link in a third. This is useful for spotting unknown devices. I once had a situation where a contractor brought in a wireless access point and plugged it into a wall jack in the server room. The scanner showed a new Cisco IP phone that wasn't mine, and the hostname field revealed the MAC address immediately. I tracked down the rogue device within ten minutes.
What The Scan Actually Does
Advanced IP Scanner works by sending ARP requests to every address in your specified range. ARP is a Layer 2 protocol, which means it doesn't traverse routers. The scanner can only discover devices on the same broadcast domain as your machine. If you have a VLAN structure or multiple subnets you'll need to run separate scans from each segment or use a different tool that supports ICMP ping sweeps across routed boundaries.
For devices behind NAT, the scanner shows the gateway IP rather than individual internal addresses unless those devices are also responding to ARP. This is a limitation worth noting. Some people assume the scanner is broken when it only shows their router and a couple computers. It's not broken. Your other devices are behind the router and the ARP broadcast never reaches them.
The port scanning component runs after the address discovery phase. It probes common ports like 80, 443, 22, 3389, and a few others. The port list is customizable but the defaults are reasonable for most situations. When you see port 22 open on a Windows machine that you didn't configure, that's worth investigating. Same with port 3389.
Exporting Results Without Frustration
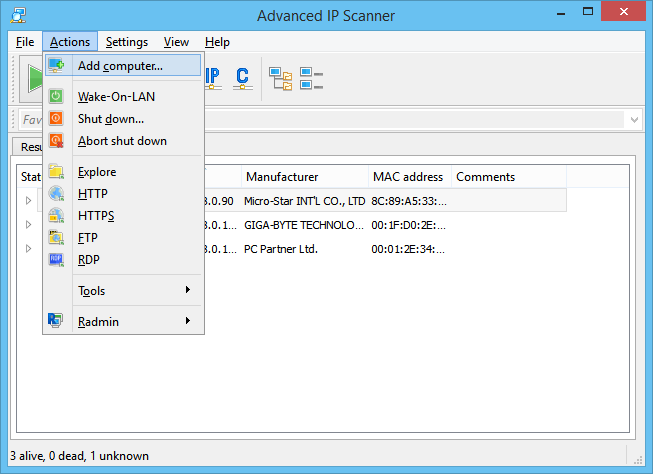
The export function works but it's not intuitive if you've used Excel before. After a scan completes, click the export button in the toolbar. You'll get options for HTML, XML, CSV, and TXT formats. CSV is the most useful for follow-up analysis. I save mine to a folder with the date in the filename so I can track device changes over time.
One thing the export doesn't handle well is large scans. If you're pulling a full /16 range and have thousands of entries, the CSV can get slow to open. I learned that the hard way when I scanned an entire corporate floor and got a file that took forty seconds to load in Excel. The workaround is to filter the results before exporting. Use the built-in filtering to show only live devices, then export that subset.
Known Issues And Workarounds
The biggest headache I've encountered is with macOS devices. The scanner sometimes fails to resolve hostnames for Apple products on certain network configurations. The devices show up with their MAC addresses but the name field stays blank. This doesn't affect the usefulness of the scan since the MAC address alone identifies the manufacturer. If you need hostnames for Macs, pair the scan with a separate DNS lookup or check your DHCP server's lease table.
Another issue is false positives on port scans. I've seen it report port 445 as open on devices where SMB was firewalled but the response time suggested a filtered port rather than a closed one. The scanner doesn't distinguish between filtered and open in its default view. If you need that level of detail, run a manual nmap scan from the command line alongside the GUI tool for confirmation.
Windows Defender sometimes flags the scanner's port scanning behavior as suspicious. This happens because the tool is sending packets to ports that aren't responding, which resembles certain types of reconnaissance activity. The detection is a false positive. You can add an exclusion for the scanner's executable path in Windows Security settings. I did this on all my machines and it hasn't caused any issues.
When Not To Use It
Advanced IP Scanner is not designed for external network scanning or penetration testing. It's a LAN discovery tool with basic port scanning. If you're trying to map a wide area network, scan remote subnets, or perform security assessments on firewalled infrastructure, you need something like Nmap with appropriate permissions. Using this tool against networks you don't own or have authorization to scan is illegal in most jurisdictions.
It also struggles with IoT devices that don't respond to standard ARP or who use non-standard MAC address formats. Smart home hubs, cheap Chinese cameras, and some industrial equipment may show up with generic vendor names or not at all. For those you'll need to check your router's DHCP client list directly.
The Bottom Line
If you need a quick, free way to see what's on your network and don't want to deal with command line tools, this is probably the best option available. It's been around for over a decade, the developer still updates it, and the free version includes everything most people actually need. The interface is dated but functional, and the scan results are accurate for typical home and small business networks.
I've been running scans with it every few months for years, and it still catches devices I didn't know were there. That's why it stays on my desktop.
Gallery Unlock The Secrets Of Your Network With Advanced Ip Scanner Free Download
Advanced IP Scanner - Download Free Network Scanner.
Discover and manage network devices with Advanced IP Scanner - BetaNews
Best Free Advanced IP Scanner: Scan a Network in Seconds
Best Free Advanced IP Scanner: Scan a Network in Seconds
Advanced IP Scanner,A Powerful Network Management Tool - BRIDGE