Restoring Unsigned IPSW Files on iOS
iTunes and Finder will refuse to restore an IPSW file that Apple no longer signs. This is not a software bug. Apple restricts restores to prevent users from downgrading past security patches. When you get an error code like 4013 or 9 during a restore, the firmwareserver is most likely rejecting the file because that iOS version has been unsealed. The process of sideloading an unsigned IPSW requires you to bypass Apple's signature verification during the restore. There are two main approaches, and each works differently depending on your device and what you actually need to accomplish. Most people who stumble across Unlock The Secrets Of Restore Unsigned Ipsw A Comprehensive Guide To Jailbreaking Your iOS Device are trying to either downgrade to a jailbreakable iOS version or preserve their current jailbreak while updating. These goals require completely different workflows.
Method One: Checkm8 Devices and Tethered Solutions
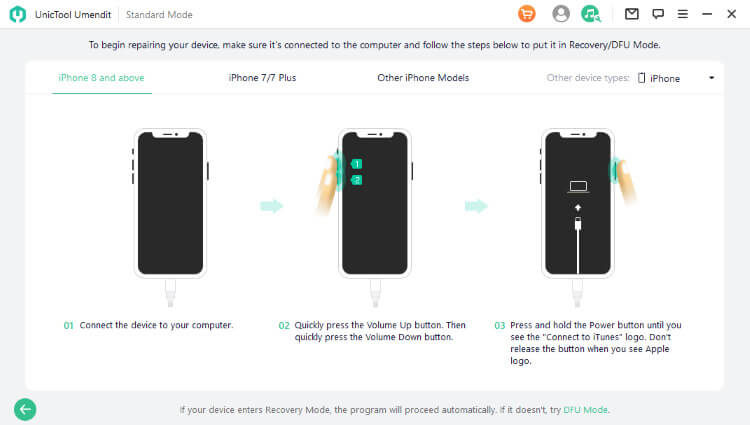
If you have an iPhone 5s through iPhone X, or any A7 to A11 chip device, your bootloader is vulnerable to the checkm8 exploit. This vulnerability lives in the bootrom, which means it cannot be patched by Apple. You can put the device into recovery mode manually every time you power it on, then restore any IPSW you want. Here is how I actually did this. I was running iOS 12.4.5 on an iPhone 7 and wanted to go back to 12.4 for unc0ver jailbreak compatibility. I downloaded the signed IPSW for that version, installed Latest checkra1n on my MacBook, and ran it. The tool puts the phone into DFU mode automatically. I then used iproxy to forward the local port over USB so I could connect to the device's restore interface without iTunes. After that, I ran the restore command directly through the command line instead of going through Finder or iTunes. The key detail nobody mentions upfront is that you need to flash the custom SEP and Baseband before the final restore step, or the device will bootloop immediately after the OS installs. The checkm8 tools handle this for you if you use their wrapper scripts. If you try to do it manually, you will spend hours troubleshooting boot issues.
I ran into one specific problem during my restore. The iproxy connection would drop randomly during the upload phase, and the restore would fail at step 7 out of 9 with a vague error. I found that keeping the device plugged in via a direct USB connection to the computer, rather than through a hub, stabilized the transfer enough to complete the restore. It also helps to use a short USB cable instead of the long official Apple cable, which adds resistance and causes intermittent connection drops during large file transfers.
Get the Full Details

Method Two: Custom IPSW Builders for Signed Firmware
When Apple is still signing a particular iOS version, you do not need the checkm8 exploit at all. You can build a custom IPSW that includes jailbreak payloads alongside the legitimate firmware. This is what most people actually mean when they look into unlocking unsigned IPSW restores. The IPSW itself remains signed by Apple, so iTunes accepts it normally, but the custom build includes modified system files that enable the jailbreak. The toolchain for this involves taking the original IPSW, extracting it, modifying the rootfs with the jailbreak components, repacking it, and then signing the modified bundle with your own developer certificate before restoring it. It takes about 20 to 40 minutes depending on your machine and network speed. I have done this process roughly a dozen times over the last few years, and the most common failure point is forgetting to update the SHSH blob for your specific device model after repacking. If the SHSH does not match the new signature chain, iTunes will reject the file at restore time. Several community tools automate most of this now. Tools like Dopamine and palera1n handle the rebuilding process for A12 through A14 devices running iOS 14 and 15. They work by injecting the jailbreak into the kernelcache before the device boots. You still need a Mac or Linux machine running the tool, and the process requires putting the device in DFU mode manually using a button sequence that varies by model.
What This Actually Gets You
Restoring an unsigned IPSW is only useful if you have a clear goal. If your device is on a newer iOS version that Apple has already patched, and no jailbreak exists for that version, restoring to an older unsigned IPSW is the only path forward. That path requires the checkm8 exploit and gives you a tethered jailbreak, meaning you must re-run the exploit every single time the device reboots. If you are fine with that tradeoff, the whole process takes roughly 45 minutes from start to finish on most setups. If your goal is simply to update your device while keeping a jailbreak, custom IPSW builders are the way to go. You stay on the same iOS version, you get the latest patches for the bugs you care about, and your jailbreak persists across reboots. The downside is that you cannot install features Apple added in newer iOS versions. You are locked to whatever kernel patches the jailbreak tool supports. I learned this the hard way after someone told me a custom IPSW would let them run iOS 16 features on their iPhone 12. It will not. The jailbreak patch targets a specific kernel version, and anything outside that range will not load. You can restore a newer iOS, but the jailbreak components will simply not activate, and you will end up with a standard iOS installation that has no additional capabilities.
Limitations and What Fails Completely
This does not work on A12 and newer devices unless you are using the palera1n or Dopamine toolchains, and even then, support is limited to specific iOS versions. iPhone SE 2022 and later, iPhone 13 and later, and all newer models have no publicly available bypass. Your only option on those devices is to wait for a new exploit to be discovered, which could take months or years depending on Apple's security updates. Another hard limit is iCloud activation. If you restore an unsigned IPSW on a device that has Find My iPhone enabled and you do not have the original Apple ID credentials, the device will remain locked at the activation screen. The checkm8 restore does not bypass activation lock. It only lets you install whatever firmware you want. I once spent an afternoon troubleshooting why a restored iPhone 7 would not pass activation, only to realize I had forgotten to check that detail in the documentation. It is an easy mistake to make. Backup restoration after an unsigned restore is also unreliable. iTunes backups created on a different iOS version may contain incompatible system data. I recommend creating a fresh backup after the restore completes rather than trying to restore an older one. Old backups sometimes cause app crashes and settings conflicts that are very difficult to debug after the fact.

How to Get Started
Check your device model and current iOS version first. If you are on A7 through A11, you can use checkra1n with a custom script to restore any IPSW you download. If you are on A12 or newer, look up whether your specific iOS version has an active jailbreak, because the entire process depends on that existing. Without an active jailbreak payload, restoring an unsigned IPSW is pointless. Download the IPSW you want from a trusted source like ipsw.me, verify the checksum if the tool requires it, and follow the steps for your device category. The whole procedure is not complicated, but it requires attention to detail and patience. Rushing through it usually means dealing with bootloops or failed restores that force you to start over.