Understanding Encrypted Packages for Secure Data Transmission
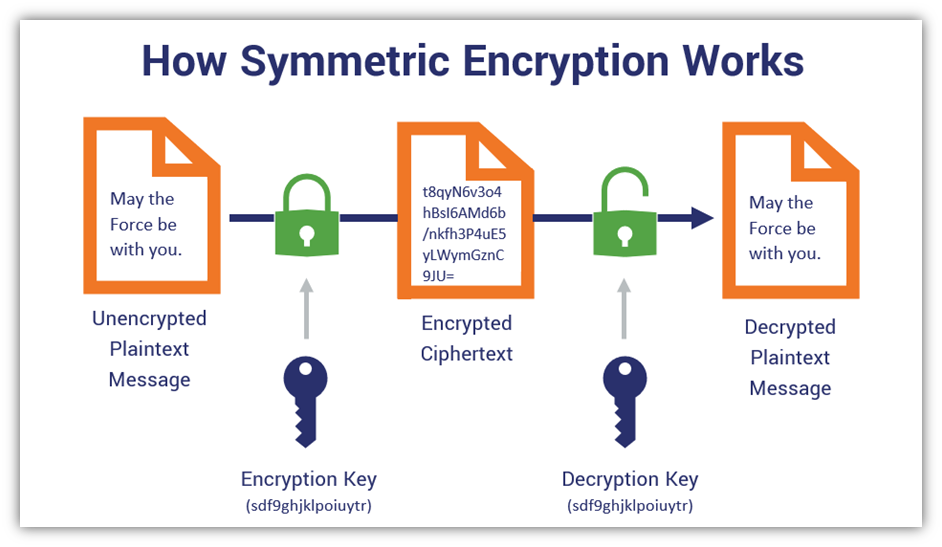
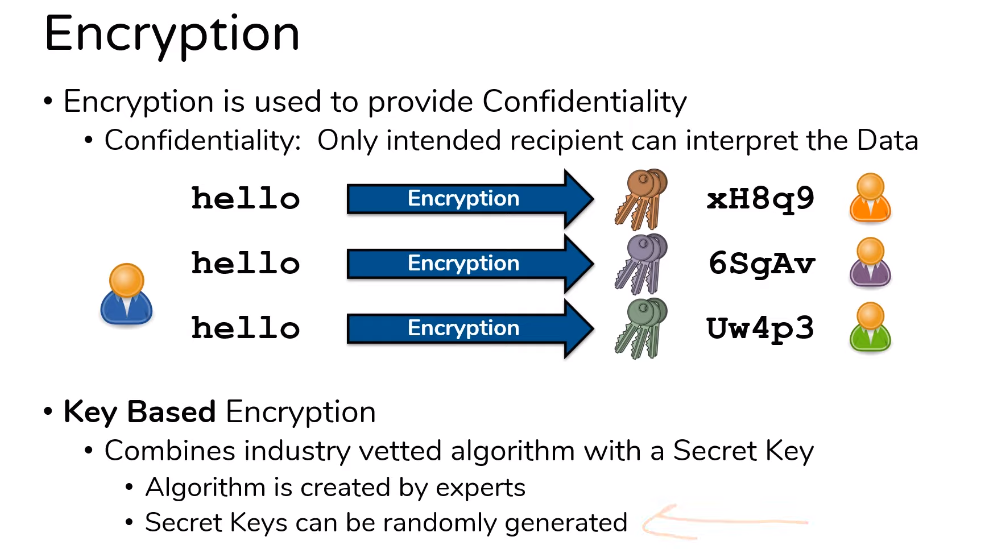
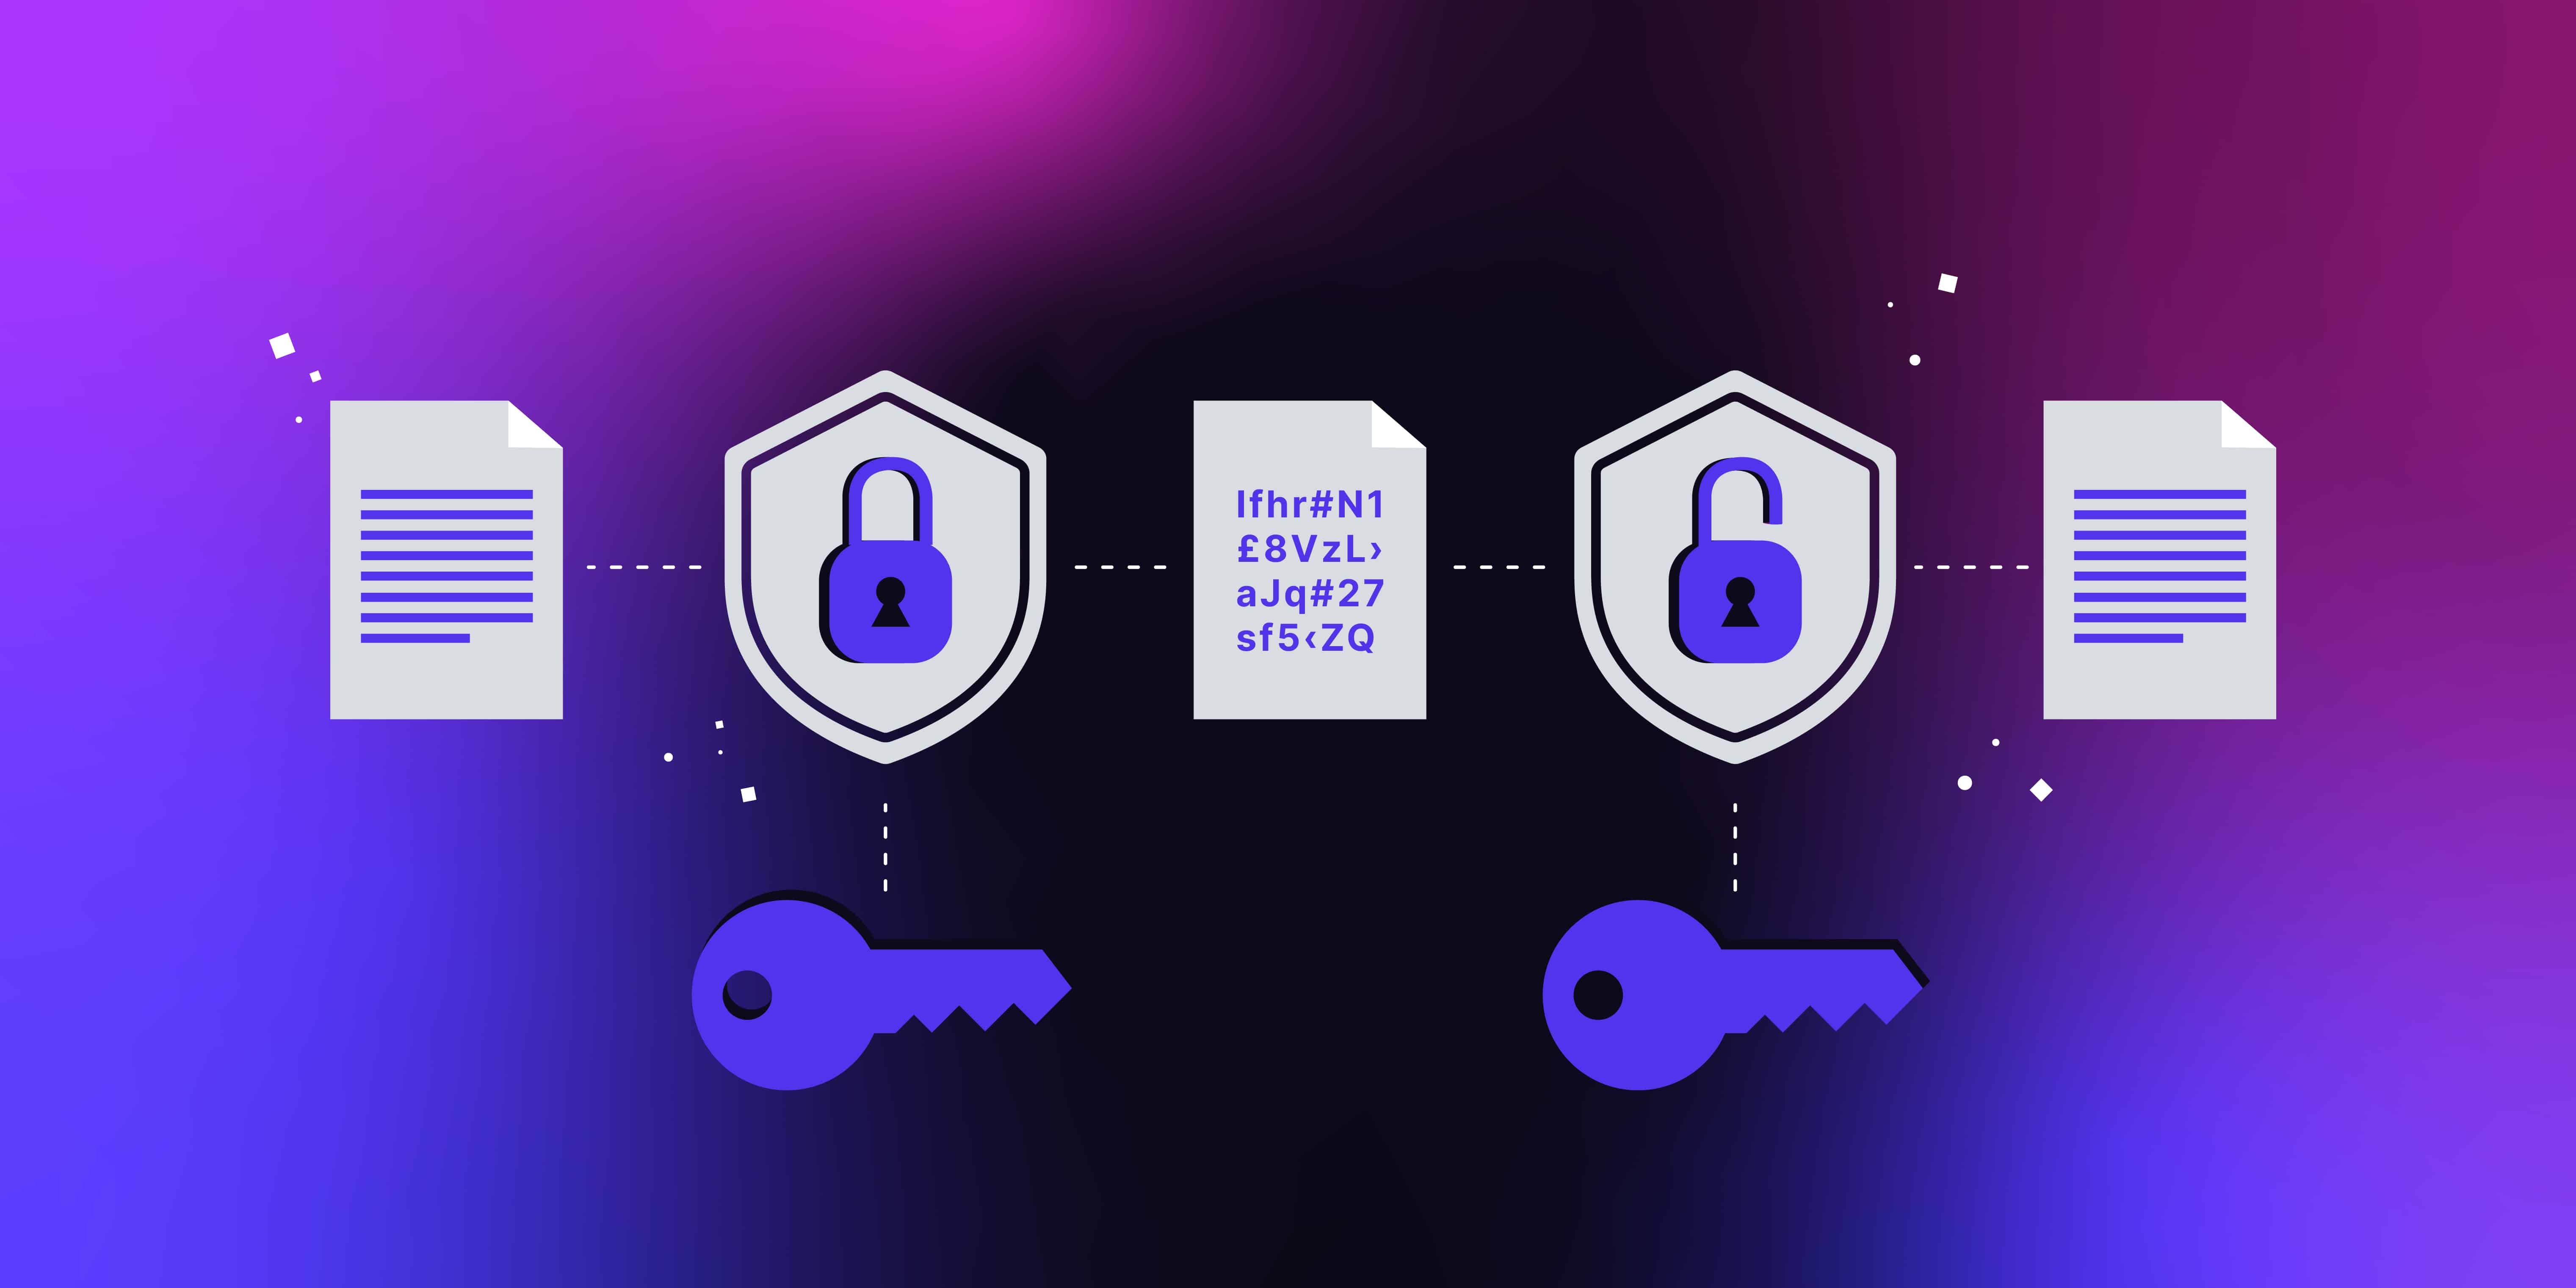
I spent about three years dealing with broken data pipelines before I realized most "encrypted package" failures aren't actually encryption problems. They're packaging and key management problems. The encryption itself is usually fine. It's everything around it that falls apart. An encrypted package is just data wrapped in multiple layers: your payload gets encrypted with a symmetric key, that key gets wrapped with an asymmetric key, and the whole thing gets packaged in a format that tells the receiver what algorithm to use and where to find the unwrapping key. Sounds simple on paper. In practice, you're looking at formats like JWE, SEIP v2, PGP messages, or custom structures that most teams build themselves and then forget how they work six months later. The standard flow goes like this. You generate a random session key. You encrypt your data with AES-GCM or ChaCha20-Poly1305. You encrypt that session key with the recipient's public key using something like RSA-OAEP or ECDH. You package the ciphertext, the encrypted key, the nonce, and the algorithm identifiers together. The recipient unboxes it in reverse order. Decrypt the session key. Decrypt the data. Verify the authentication tag. If the tag doesn't match, you drop it and log it. That's it.
Here's where people mess up. They skip the algorithm negotiation properly and hardcode "AES-256-GCM" somewhere in their config. Then the system gets migrated to a server that runs an older TLS library which doesn't support that cipher suite properly. Or they use ECB mode because it was easier to implement and they didn't know better. ECB mode is bad. Don't use it. Just don't. I once spent two days debugging a payment processing system where encrypted packages were arriving but failing validation silently. The issue turned out to be a newline character getting stripped from the base64 encoding during a proxy hop. The ciphertext was technically correct. The base64 decoding was failing in a way that produced valid but wrong padding. The HMAC check failed silently because the error handling caught it and logged it as a network timeout instead of a decryption failure. We ended up switching to CBOR-based serialization instead of base64 for the wire format. Fixed it in about four hours once we identified the actual problem.
Practical Implementation
For most teams, the path of least resistance is using established libraries rather than rolling your own implementation. NaCl's sealed boxes handle the common case well. libsodium gives you the primitives directly if you need more control. On the Java side, Bouncy Castle has solid support though the API is verbose. Python developers usually go with cryptography.io which is well-maintained and reasonably straightforward. The critical part most people skip is key rotation. Set a hard expiration on your session keys. Something like 24 hours for high-throughput systems, 72 hours for lower-volume ones. When the key expires, generate a new one. Store the old one in a separate vault for decryption of late-arriving data only. Don't keep old keys around indefinitely. That's how breaches happen when someone compromises your key store years after a key should have been rotated. Another thing nobody talks about enough: packet size. Encrypted packages are bigger than plaintext. A 1MB payload with AES-256-GCM and proper key wrapping can easily become 1.2 or 1.3MB depending on your overhead choices. If you're sending these over constrained networks or through message queues with size limits, you'll hit boundaries you didn't expect. I've seen systems silently drop large encrypted messages at 64KB boundaries because the middleware had a default limit and nobody checked the configuration. Fragment your data before encrypting if you're dealing with anything larger than a few hundred kilobytes.
Get the Full Details
Common Failures and Workarounds
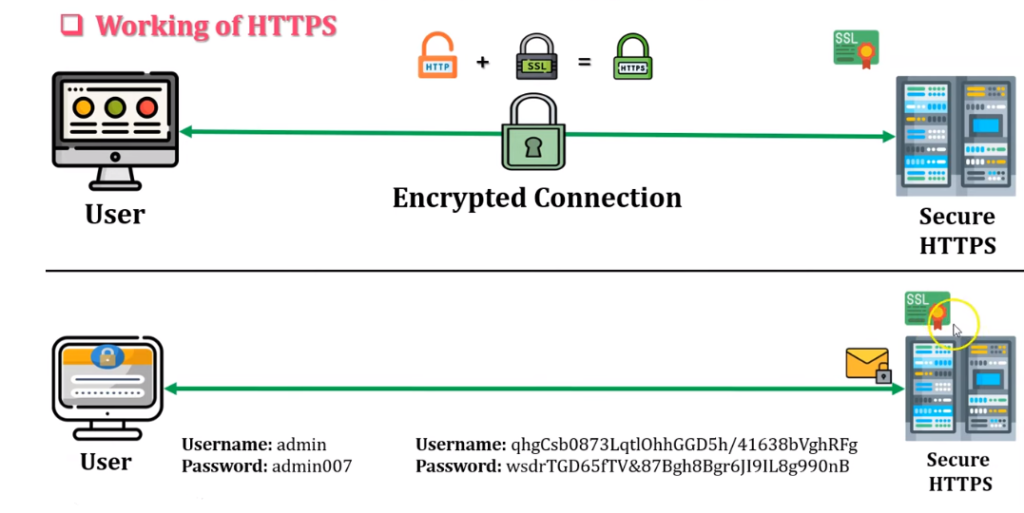
Timestamp-based replay attacks are real. If your encrypted package doesn't include a timestamp or a monotonic sequence number inside the authenticated data, an attacker who captures a valid package can resend it later. The decryption will succeed. The application will process the same transaction again. Include a timestamp with a reasonable tolerance window, or better yet, use sequence numbers that the receiver validates for uniqueness. This adds maybe 8 bytes to your package overhead and prevents a class of attacks that shows up in audit reports more often than people expect. Null byte injection in key material is another edge case worth mentioning. If you're reading keys from environment variables or configuration files and there's trailing whitespace or null bytes, your derived keys will be wrong. The package won't decrypt. You'll see authentication failures that look random because the key derivation function produces a completely different output from slightly different input. Trim your key material. Validate the length. Fail fast if something looks wrong instead of trying to decrypt and seeing what happens. There's also the problem of mixing encryption schemes haphazardly. Some teams encrypt at the database level, then again at the application level, then the transport layer adds TLS on top. Now you have three different key management systems, three different rotation schedules, and nobody knows which layer is supposed to protect what. Pick one layer for application-level encryption. Do not stack them. TLS handles transport. Don't duplicate effort above it unless you have a specific threat model that requires it, and if you do, document why clearly.
Performance Considerations
AES-GCM hardware acceleration makes a measurable difference on modern processors. If your CPU supports AES-NI, you're looking at roughly 500MB/s to 1GB/s for encryption throughput on a single core. That's plenty for most workloads. Without hardware acceleration, you're looking at maybe 50-100MB/s. ChaCha20 is faster than software AES on systems without AES-NI, which is why it's becoming the default in many newer libraries. If you're deploying on older hardware or in containerized environments where the host CPU doesn't support AES extensions, test your throughput before you commit to AES-GCM. Key generation should use a cryptographically secure random number generator. In Python that's secrets.token_bytes(). In Node.js it's crypto.randomBytes(). In Go it's crypto/rand. Do not use Math.random() or any PRNG that isn't designed for cryptographic use. I've seen this mistake in production code at companies that should know better. The encrypted package looks fine. The keys are predictable. Anyone who can observe enough traffic can reconstruct the key material. If you need a starting point for implementation, the libsodium documentation at sodiumoxide.github.io has worked examples in multiple languages. The NaCl library itself at nacl.cr.yp.to has reference implementations. For teams building in enterprise Java environments, look at the JWE support in Nimbus JOSE+JWT or the built-in JWE classes in Java 9 and later. These give you standards-compliant encryption without having to manage the low-level details yourself.