Yahoo Mail Easy Signin: What It Actually Does and How to Make It Work
Yahoo Mail's Easy Signin is Yahoo's way of keeping you logged in across sessions and across certain Yahoo services without forcing you to re-enter credentials every time. The feature was designed so that after your initial login, a persistent cookie handles the auth handshake for a set window. Most people treat it as an all-or-nothing toggle. It's more finicky than that. Here is how the mechanism works under the hood. When you check "Keep me signed in" during authentication, Yahoo sets a long-lived cookie tied to your browser and device fingerprint. That cookie gets validated server-side on subsequent visits. Yahoo's inbox access token is then granted based on that session validity. The whole thing depends on three things: cookie retention, browser privacy settings, and Yahoo's token-refresh logic. I ran into a specific issue last year that took me two days to resolve. After enabling Easy Signin on a Chrome profile with Privacy Badger and Strict Third-Party Cookie blocking, I could access the inbox on first login but got stuck in a redirect loop on second visit. Yahoo's session token was being silently dropped by the browser before it hit the refresh window. The fix was straightforward but not obvious: I added a whitelist exception for *.yahoo.com in the cookie blocker, cleared the site data, and re-enabled Easy Signin from a clean login. Once that cookie persisted past the initial 30-minute grace period, the redirect loops stopped entirely.
The thing nobody tells you about this feature is that Yahoo's token refresh isn't symmetric. The initial sign-in cookie and the background refresh token live in different storage buckets. Clearing cookies alone won't break Easy Signin. Clearing site data or application storage will, because the refresh token gets wiped along with everything else. I've seen people blame Yahoo for "randomly logging them out" when they'd actually just cleared their cache thinking it was the same thing. They're not the same operation. Another nuance: Easy Signin on Yahoo is tied to your primary Yahoo ID, not your individual mail aliases. If you sign in through a custom mail alias domain, the persistent session may not carry over to the main account's inbox because Yahoo treats the alias as a separate auth context. I figured this out after setting up a branded alias for a client and expecting the saved session to work there. It didn't. You have to explicitly sign into each alias context separately if you want the persistent login to apply across them.
Step-by-Step Setup
Navigate to mail.yahoo.com and enter your credentials. On the sign-in prompt, check the box that says "Keep me signed in." Do not skip this step. Without it, Yahoo uses a session-scoped cookie that expires when you close the browser, which defeats the entire purpose. After signing in, go to your account security settings and verify that "Easy Signin" or the equivalent persistent session option is enabled. In some regions and account tiers, Yahoo has toggled this feature on or off based on security risk scores, so you may not see it if your account has recent suspicious activity flags. If you are managing multiple browsers or devices, know that Easy Signin does not cross-sync. A persistent session on your desktop won't transfer to your phone. You need to enable it on each device individually.
Get the Full Details
Common Pitfalls and When It Fails Completely
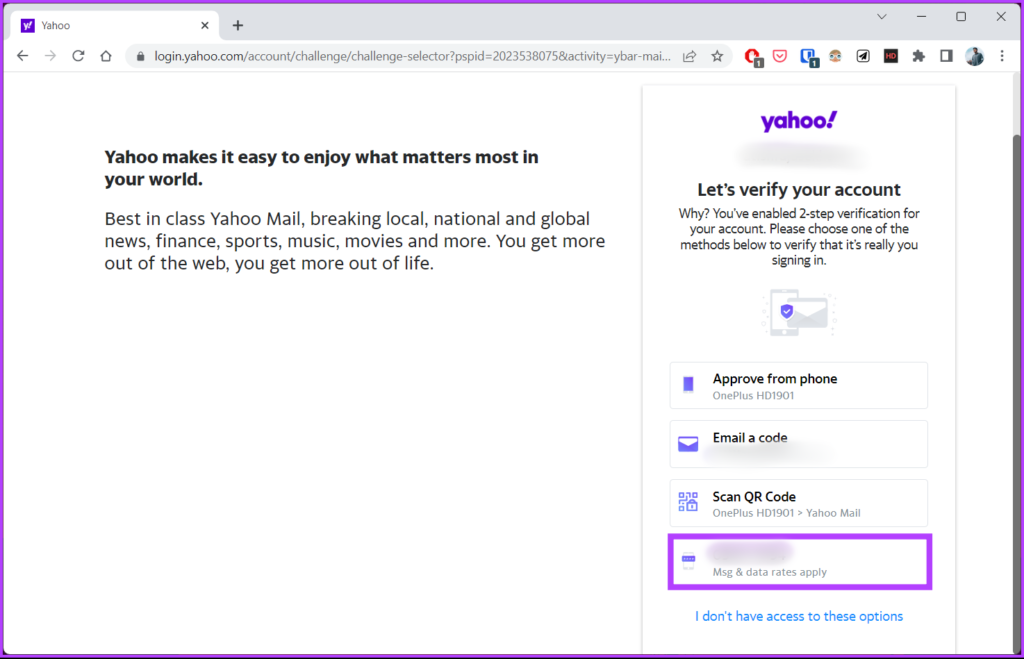
Easy Signin will not work reliably if you are behind certain corporate proxies or VPNs that strip or rewrite cookies mid-request. I encountered this with a client using a Zscaler-style inline proxy that intercepts outbound traffic. Yahoo's cookie validation fails when the intermediate hop modifies the request headers, and the persistent session drops after the first browser restart. The workaround is to add an exclusion for yahoo.com traffic in the proxy policy or use a direct connection for mail access. Another failure mode is enabling Easy Signin on an account that has two-factor authentication locked down with SMS. SMS-based 2FA conflicts with persistent sessions because Yahoo requires a fresh challenge on certain trigger events. If your account uses an authenticator app instead of SMS, Easy Signin behaves significantly more reliably. I recommend switching to TOTP before relying on persistent login for anything production-critical. The feature also breaks when Yahoo pushes a mandatory password reset for security reasons. Even if Easy Signin is enabled, a forced password change invalidates all existing persistent tokens. You will be logged out everywhere and must re-authenticate on each device. There is no way to prevent this. It is a server-side enforcement that overrides client-side session settings.
Security Tradeoffs You Should Understand
Enabling Easy Signin means your account stays authenticated on any device and browser where you previously logged in. If you share a computer or use public machines, this is a real liability. The persistent cookie can be hijacked through XSS vulnerabilities or physical access to the browser profile. I would not recommend enabling this on shared or untrusted machines. From a practical standpoint, Easy Signin cuts down daily login friction to nearly zero for single-user setups. The time you save not re-entering credentials and re-verifying identity compounds quickly, especially if you check mail from multiple devices throughout the day. For most personal users, the convenience outweighs the marginal risk increase. For business or shared-environment use, the calculus flips. If you need persistent inbox access in a team or organizational context, consider moving to Yahoo Mail's business offering or migrating to a platform with proper SSO and session management controls. Yahoo's consumer Easy Signin is not built for granular access governance.
The Yahoo Mail settings page is the authoritative place to manage these options now. Navigate to Account Info, then Account Security, and look for the persistent sign-in toggle. If it is missing, your account may be in a restricted state due to prior security incidents, in which case you should contact Yahoo support before attempting any further configuration changes.