Understanding IP Addresses Without the Hype
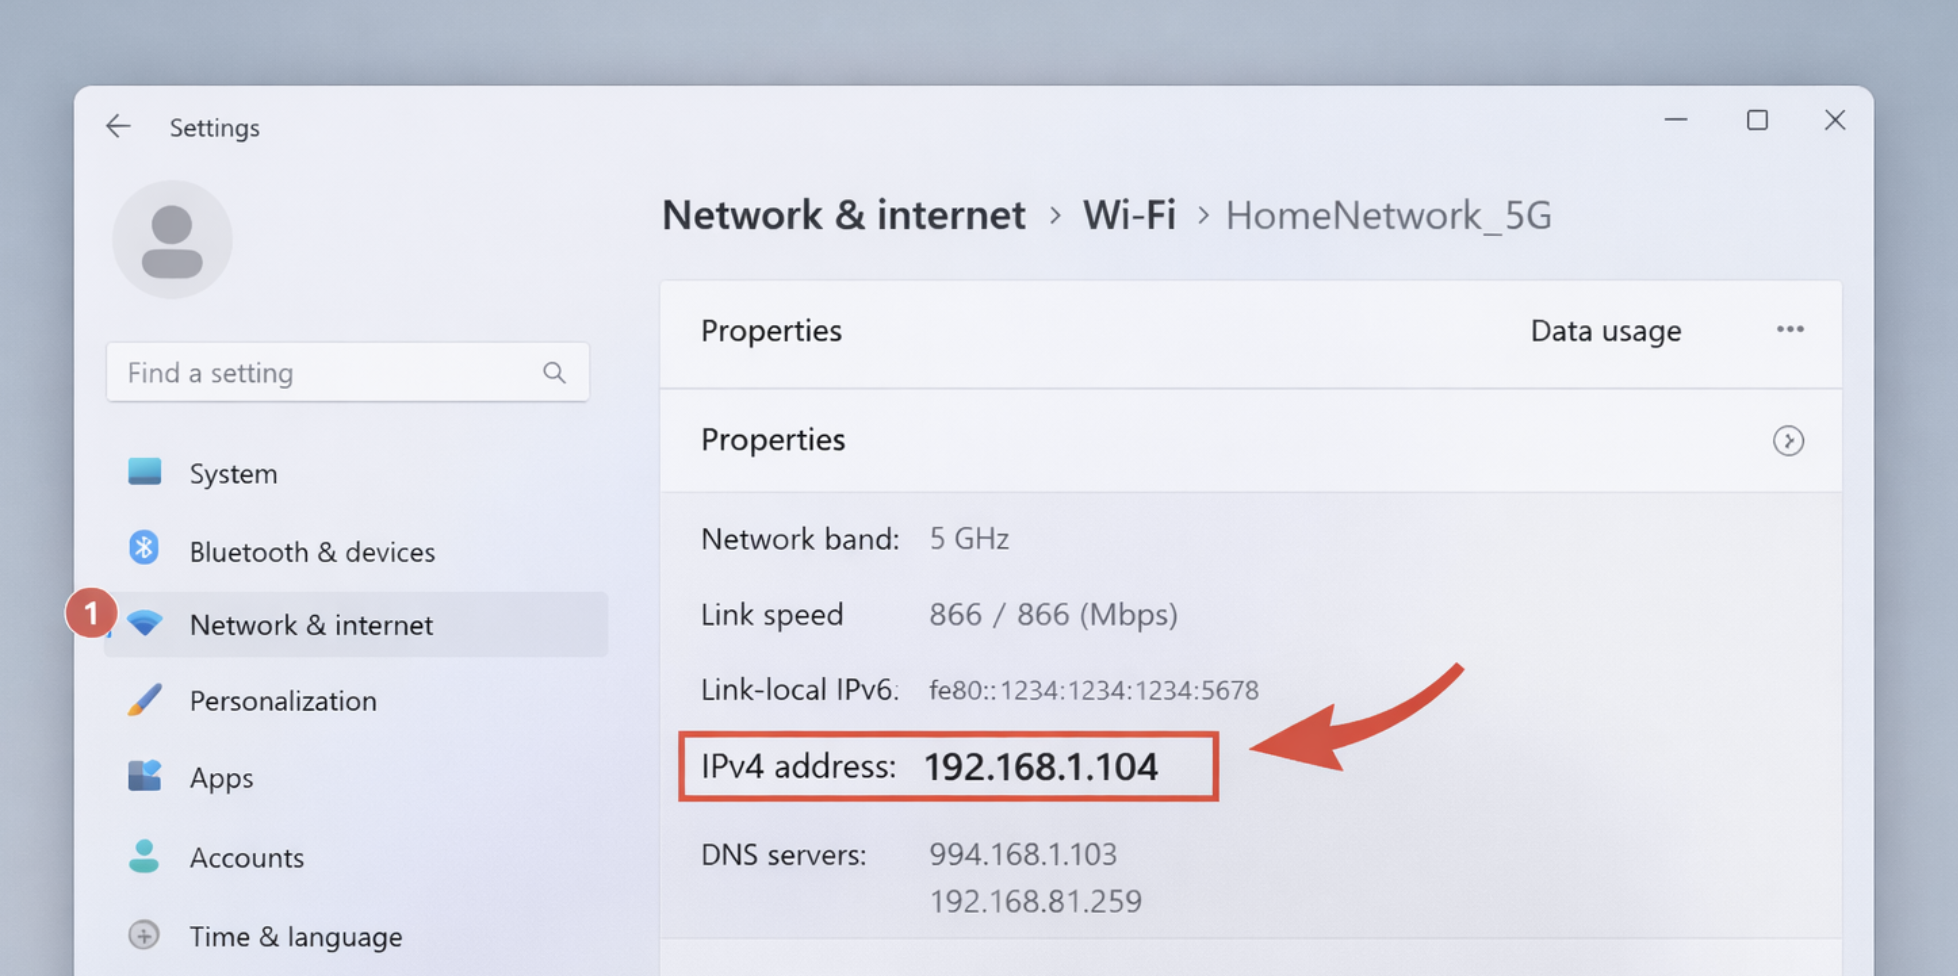
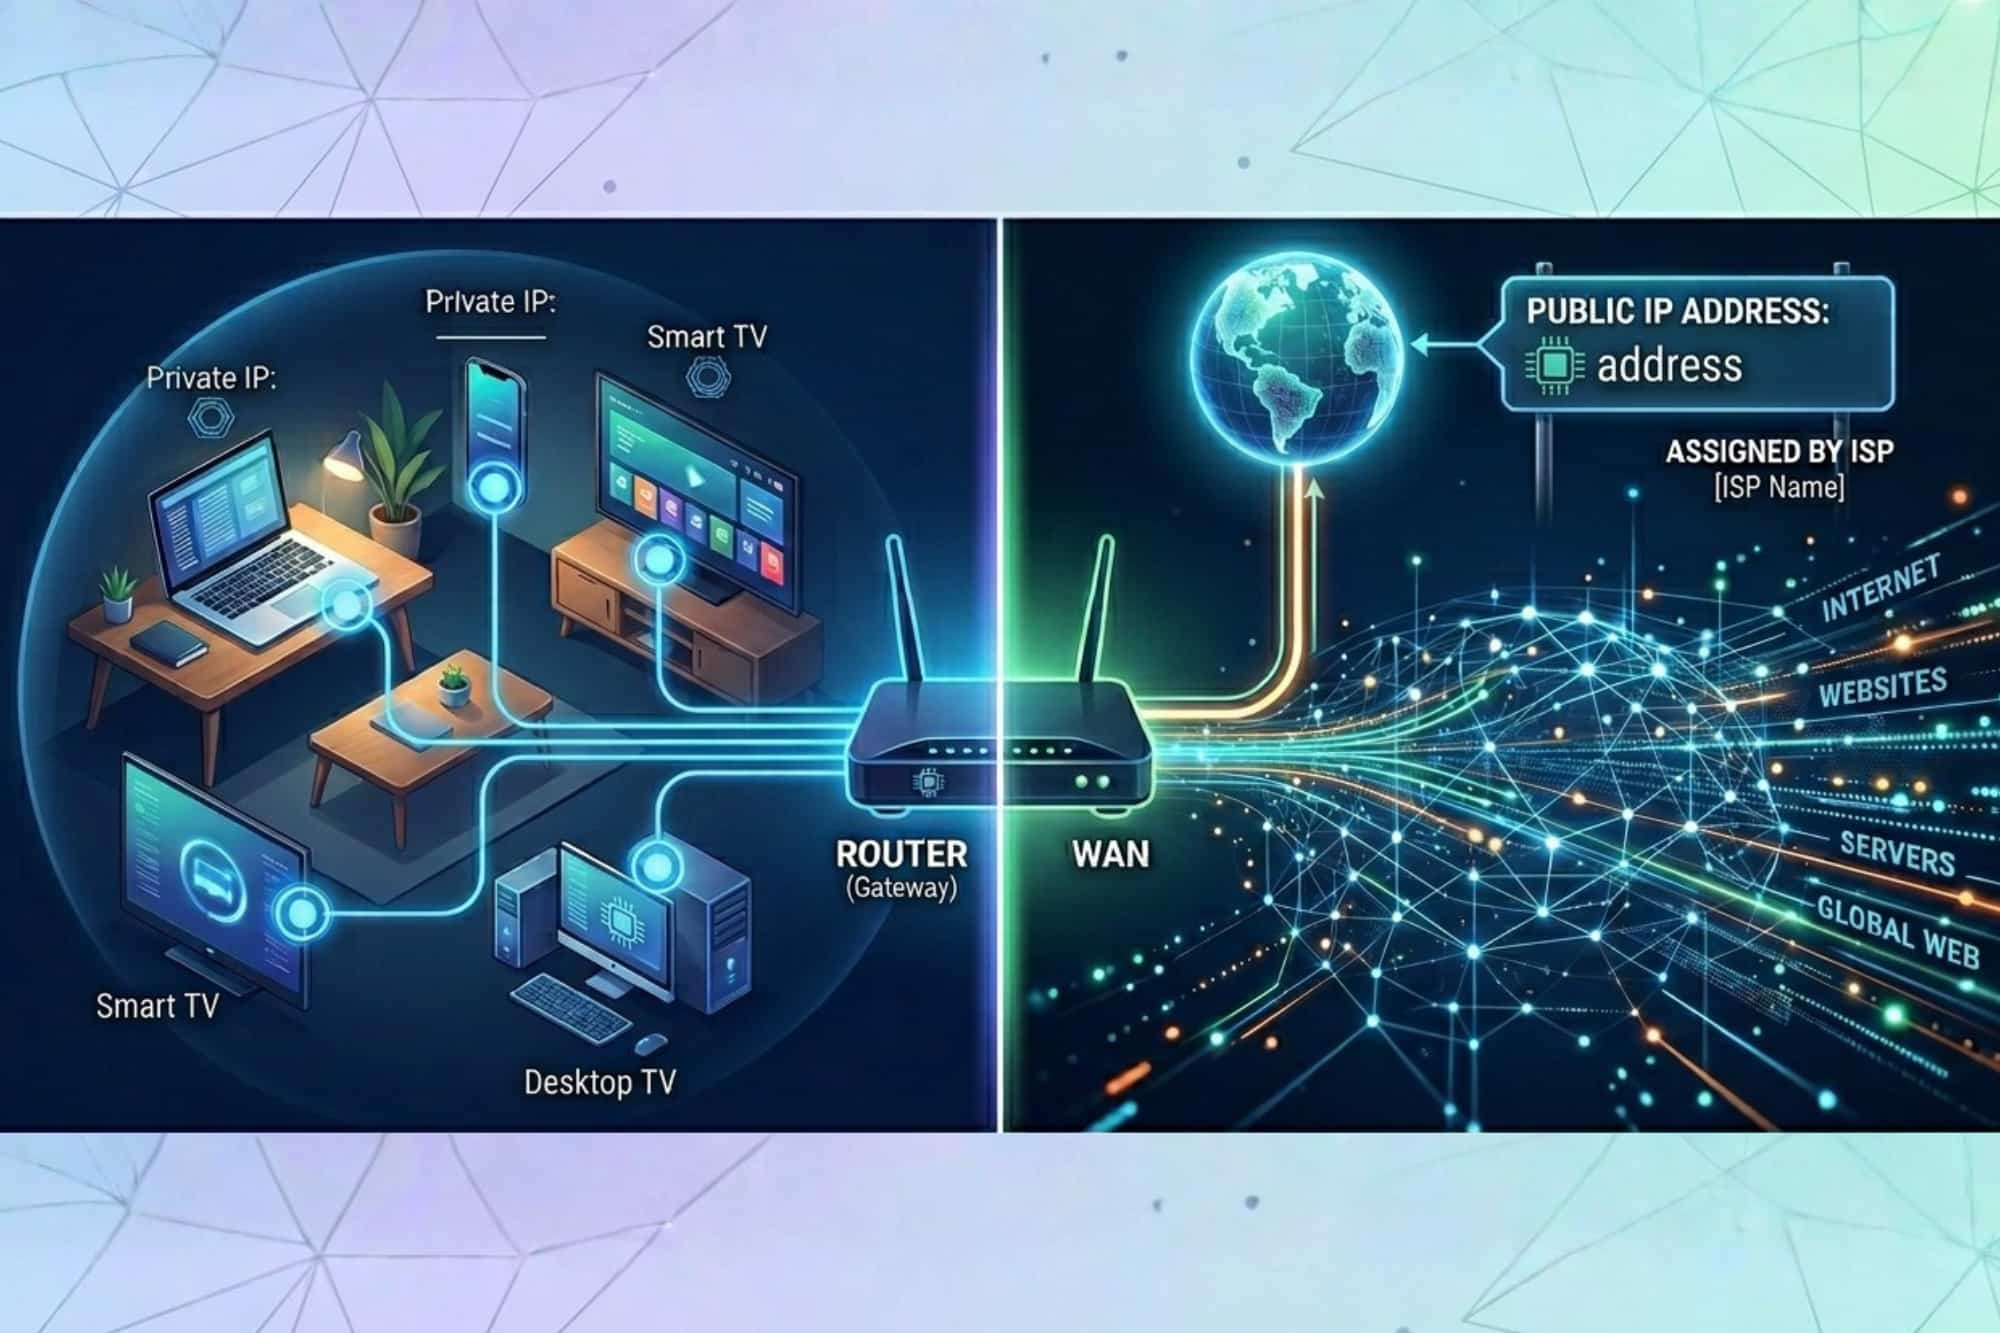
An IP address is just a numeric label assigned to each device on a network. That's it. Nothing mystical about it. You've probably seen one if you've ever checked your WiFi settings — something like 192.168.1.42 or 10.0.0.7. Those are private addresses your router handed out. Then there's your public IP, the one the rest of the internet sees, usually provided by your ISP. I spent about three years working in network administration before moving into devops, and the thing most people get wrong is thinking your IP address is some kind of fixed identity. It isn't. For residential connections especially, it changes. Sometimes daily, sometimes after a router restart, sometimes not at all for months. There's no pattern you can predict.
Unlock The Power Of Your Ip Address A Quick And Easy Guide
Let me walk you through what you can actually do with this information, starting with something most beginners don't realize: checking your public IP isn't as straightforward as looking at your network adapter settings. When I ran into this confusion repeatedly with clients, I'd tell them to open a browser and visit whatismyip.com or use the curl command from their terminal. `curl ipinfo.io` gives you the address along with geo data in JSON format. Takes about four seconds. The real question is why you'd want to do this repeatedly. Here's the practical side: if you're running a home server, your ISP might block certain ports entirely, or they might assign you a dynamic IP that forces you to constantly update DNS records. I had a situation once where my VPS host couldn't reach my home SSH server because the IP changed during a brief power outage, and the reverse DNS entry had stale pointers. Fixed it by setting up a lightweight DNS updater script that polled the ISP endpoint every six hours and pushed changes to Cloudflare's API. Runs on a Raspberry Pi, uses about 50 megabytes of RAM while idle. Most people don't need to think about any of this. If you're just browsing the web or checking email, your IP address handles itself in the background without any input from you. The confusion usually starts when someone tries to host something publicly or set up port forwarding, and then they hit walls they didn't expect. NAT traversal, symmetric NAT, carrier-grade NAT — these are the terms that show up when your connection refuses to accept inbound traffic despite correct router configuration. Carrier-grade NAT is particularly annoying because it means your ISP is sharing a single public address across dozens of customers, which makes direct inbound connections impossible regardless of what you do in your router settings.
If you need a static IP for legitimate purposes, most ISPs will charge extra for a business-grade plan. Residential plans almost never include one unless you negotiate. The workaround some people use involves VPN services or reverse tunneling tools like ngrok or frp, but those introduce latency and depend on third-party infrastructure you don't control. I generally recommend against ngrok for anything beyond testing because the free tier has rate limits and the connections route through their servers, which is a privacy consideration worth thinking about if you're handling sensitive data. Another thing nobody mentions: IPv6 changes how all of this works. If your ISP provides IPv6, you typically get a globally routable address on each interface, and the whole dynamic DNS problem becomes less relevant because IPv6 addresses can be stable and configured manually. The catch is that most residential firewalls and ISP equipment still default to blocking inbound IPv6 traffic, so you gain address stability but not necessarily connectivity. I learned this the hard way when I configured a server with IPv6 and spent two days troubleshooting why external hosts couldn't reach it, only to find the upstream router was dropping IPv6 packets despite the address being publicly valid. For most users, knowing your IP address and understanding that it might change is enough. Setting up dynamic DNS if you need remote access, accepting that carrier-grade NAT exists and working around it if your use case demands inbound connections, and keeping your firewall rules tight are the practical steps. Anything beyond that usually means you're solving a problem that doesn't exist for your typical workload.
Get the Full Details

Common IP-Related Problems and Fixes
When someone calls me saying their website isn't accessible from outside their network, the first thing I check is whether they actually have a public IP or if they're behind carrier-grade NAT. About sixty percent of the time it's the latter, and no amount of port forwarding on their router will fix it because the translation happens at the ISP level, not their equipment. The telltale sign is comparing your router's WAN IP against what whatismyip.com reports — if they don't match, you're behind CGNAT. Another frequent issue: people change their IP address and then wonder why their SSH keys or SSL certificate pinning stops working. These mechanisms bind to the address, so a change breaks the trust chain. The fix is either to use DNS-based identification instead of raw IP addresses or to update the affected configurations after each change. I prefer DNS because it's less fragile, though it does require running a DNS server or paying for a dynamic DNS service. Port scanning your own IP from outside your network is a legitimate troubleshooting step, but it's worth noting that many consumer routers and residential firewalls will silently drop probes rather than respond with rejection packets. This makes it look like a port is closed when it might actually be filtered. Distinguishing between filtered and closed requires tools like nmap with specific timing and flag options, and even then the results aren't always conclusive depending on the firewall implementation.
If you're looking to rotate or manage IP addresses programmatically — for scraping, automation, or testing purposes — the options range from paid proxy services to setting up your own exit nodes. Each approach has tradeoffs. Proxy services are convenient but you're trusting someone else with your traffic. Self-hosted solutions give you control but require infrastructure and technical overhead that most people don't want to maintain. I've run small TOR exit nodes for testing and found that the monitoring and abuse reporting requirements are more work than they're worth unless you have a specific reason to operate one. The bottom line is that IP addresses are simpler than most guides make them sound. They identify devices, they can change, and they become complicated only when you try to do something non-standard with them. If your use case stays within normal browsing, streaming, and cloud service consumption, you don't need to manage your IP address at all. It just works.