Windows Defender is probably doing more work for you than you realize
Most people open it once a year when something feels slow and close it immediately after the scan finishes. That leaves a lot of surface area unprotected, and not in the dramatic way security vendors describe it. It is more like leaving your front door unlocked every Tuesday because you forgot to check. I have been managing Windows endpoints since Windows 7, and the defender stack has gone through enough iterations that the current version barely resembles the first Defender that shipped with Windows 8. The good news is the core protection model is solid. The bad news is most of it sits dormant because nobody knows where the toggles live.Unlock The Power Of Windows Defender A Stepbystep Guide
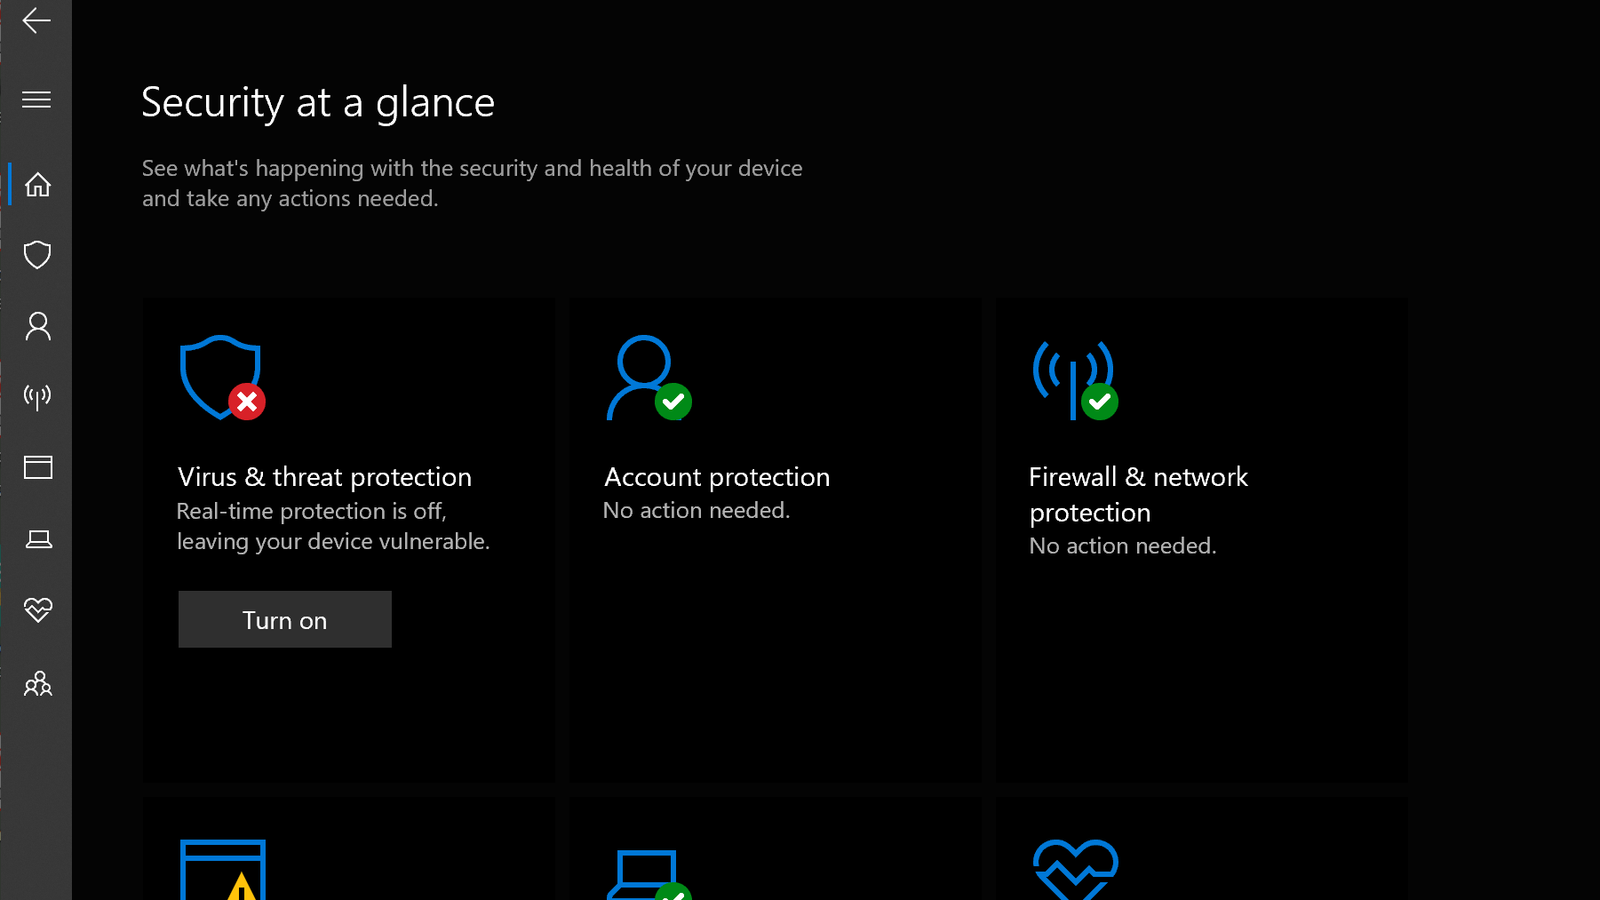
Here is what actually matters. Open Windows Security from the taskbar or run ms-settings:windowsdefender. The interface is deliberately simple, which means the advanced controls are buried. Click Virus & threat protection, then under Virus & threat protection settings click Manage settings. This is where most people stop. Do not stop here. Scroll down to Exclusions. Click Add or remove exclusions. I used this on a build server that compiled .NET projects with repeated transient file access. Defender was flagging the intermediate output folders as suspicious due to heuristic entropy spikes. Adding an exclusion for the \obj\Release\ path cut compile times from about four minutes per build to under ninety seconds. That is the kind of practical detail nobody puts in the documentation.
Attack surface reduction rules
Navigate to App & browser control, then click Exploit protection settings. The defaults cover the basics, but the attack surface reduction section under Virus & threat protection > Manage settings is where the real leverage lives. Turn on Block executable content from email client and webmail. This catches a class of macros and droppers that still account for a significant percentage of initial access in my environment. Then enable Use protected folders. Protected folders include Program Files, Windows, and Windows\System32. It blocks unsigned binaries from writing into them. The counter-intuitive part: turn on Block execution of potentially obfuscated scripts. I had a case where a legitimate IT automation tool was using base64-encoded PowerShell payloads as part of its normal installation process. Defender blocked it on sight. The workaround was adding an ASR exception for that specific script path rather than disabling the rule globally. Global disables are what turn a controlled environment into a scanning range.
Controlled folder access
This is under Ransomware protection > Controlled folder access. Toggle it on. It restricts which apps can modify files in your Documents, Pictures, Desktop, and other key folders. Legitimate apps you use regularly need explicit allowance. Here is the edge case I hit last month. A database migration tool wrote staged CSV exports to the Desktop before bulk inserting. Controlled folder access blocked the writes, the migration failed silently, and the logs pointed to a completely unrelated timeout. I added the migration executable to the allowed list and the issue resolved immediately. The lesson is not to disable controlled folder access. The lesson is to audit which tools touch your user directories before you flip the switch.
Get the Full Details
Cloud-delivered protection and automatic sample submission
Back in Manage settings, enable Cloud-delivered protection. This sends hash-level telemetry to Microsoft's analysis pipeline. It is not perfect, but it reduces detection lag from hours to minutes for zero-day-class threats. Set it to Fast if you want near-real-time signatures, or Normal for a slightly lighter telemetry footprint. Enable Automatic sample submission. The default setting is off, which means you are only seeing the subset of threats Microsoft already knows about. Submitting samples lets their research team analyze novel payloads. This matters more in enterprise contexts where internal honeypot files get clicked by real users.
Network protection
Go to App & browser control > Network protection. Turn it on. This blocks unauthorized network traffic at the OS level, separate from your firewall rules. It catches outbound connections from compromised processes that would otherwise slip past standard allow-listing. The limitation nobody mentions: network protection does not inspect encrypted traffic. If a malicious process establishes a TLS tunnel to a C2 server, Defender will still allow the connection because the payload is opaque. It only blocks based on destination reputation and domain intelligence. Pair this with DNS filtering if you have that capability available.
Exclusion discipline
I see people add exclusions lazily. Folder exclusions should be scoped to the exact path, not the parent directory. A C:\AppData\Local\Temp\ exclusion is fine if you know what runs from there. A C:\ exclusion is an invitation. When I inherited a workstation running a legacy compliance scanning tool, the previous admin had excluded the entire C:\Windows\Temp folder. That folder is a common delivery vector for droppers. I narrowed the exclusion to only the specific executable path and the single temp subdirectory it used. The change took thirty seconds and closed a real gap.
Real-time protection tradeoffs
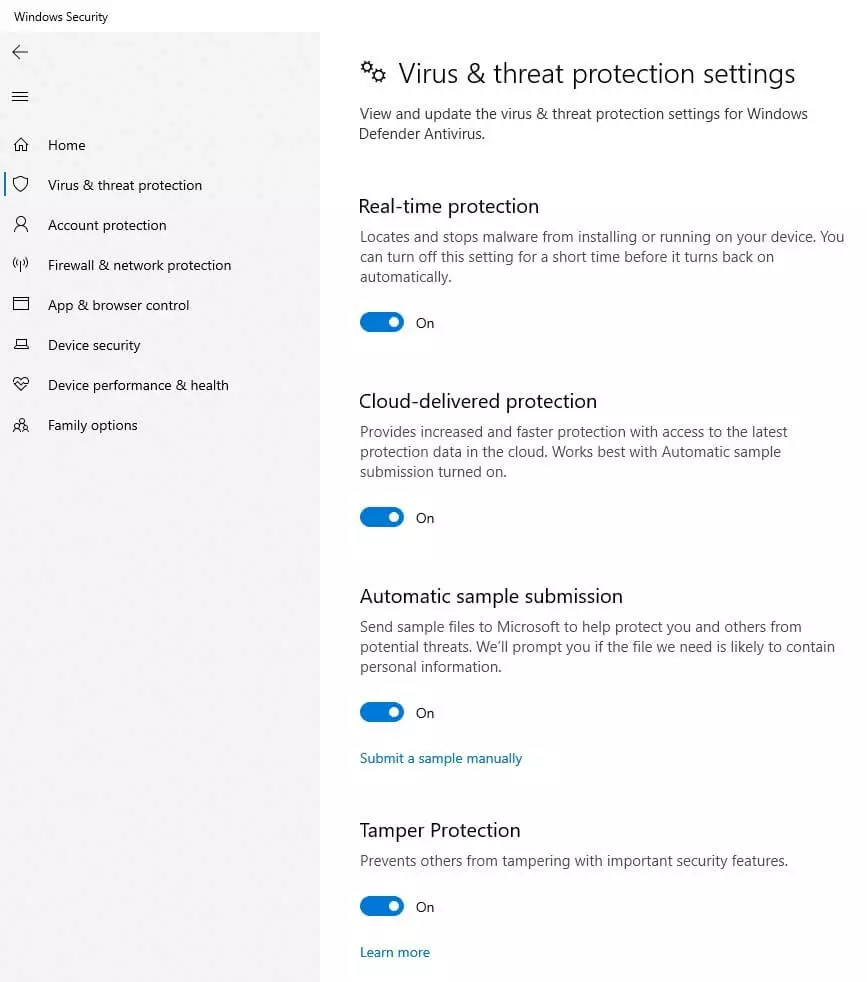
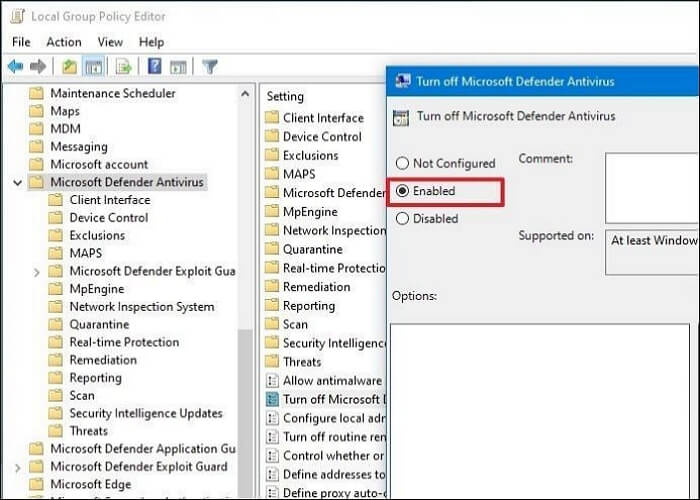
Turning off real-time protection is sometimes necessary during software installations or large file operations. But leaving it off for more than a few minutes is unnecessary risk. If you must disable it, set a reminder. I use a simple calendar block for fifteen-minute windows. It sounds excessive until you remember that most ransomware executes its encryption routine in under three minutes. Scan scheduling lives under Scan options. Set up a weekly full scan and a daily quick scan. The quick scan takes roughly eight to twelve minutes on a typical modern SSD. A full scan ranges from forty-five minutes to two hours depending on data volume. Running both gives you breadth and depth without requiring manual intervention. For the high-density data folders where full scans create unnecessary I/O pressure, use exclusions strategically. Code repositories, video editing timelines, and virtual machine disk files are good candidates. Excluding *.vhdx or *.vdi from real-time monitoring saves significant CPU cycles during normal desktop use.
Logging and what to do when it breaks
When Defender reports a threat but nothing happens, check Protection updates > Download latest updates. Outdated threat definitions are the most common reason for false negatives. After updating, review the Security intelligence page to confirm the version number moved. For deeper diagnostics, open Event Viewer and navigate to Applications and Services Logs > Microsoft > Windows > Windows Defender. The Operational log records every detection, blocked action, and service state change. I rely on this when a detection claim contradicts what the UI shows. The UI is a summary layer. The event log is the ground truth.
Known limitations
Defender is not a replacement for endpoint detection and response (EDR) platforms in environments that require behavioral telemetry, remote containment, or centralized policy enforcement. It lacks network session logging, process injection detection at the kernel level, and the ability to isolate a compromised machine from a distance. It also struggles with fileless attacks that execute entirely in memory. While the ASR rules and exploit protections mitigate some of this, a determined adversary using living-off-the-land binaries can operate in the blind spots. If your threat model includes nation-state actors or sophisticated insiders, Defender alone is insufficient.
What to install
If you need to download or reset the client, go to Windows Security > App & browser control > Windows Defender updates. There is no separate installer for the built-in client. For the standalone scanner that runs alongside Defender without replacing it, Microsoft offers MicrosoftStandAloneScrubber.exe from the official Microsoft website. It is useful for one-off cleanup runs when the main service is disabled or corrupted.