IPsec VPNs Are Evolving Faster Than Most Networks Can Keep Up
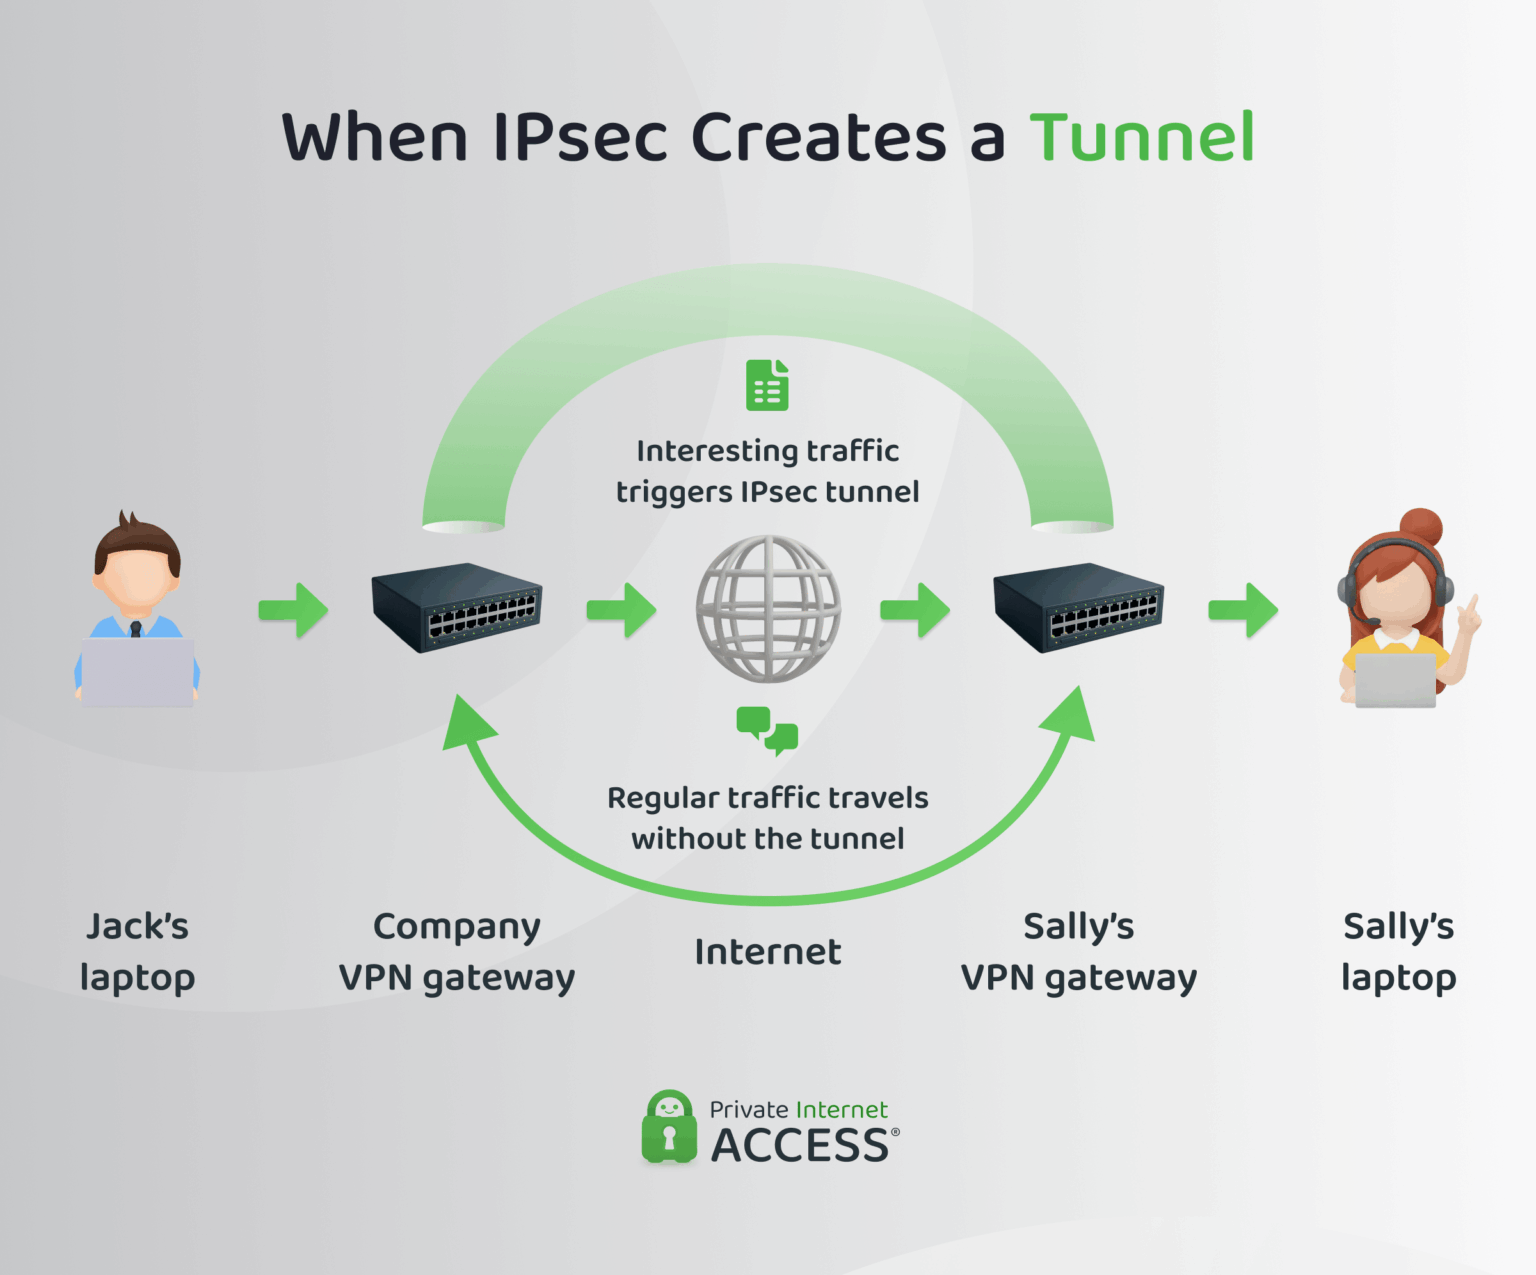
Most people still think IPsec is just that gray box in their firewall doing encryption and nobody questions it. The protocol itself has been around since the late 90s, but the ecosystem around it shifted dramatically over the last few years, and if you haven't updated your implementations, you are probably running something more vulnerable than you realize. I need to talk about what actually changed, not the marketing version of what changed. The shift started with IKEv2 replacing IKEv1 as the default negotiation protocol in every serious vendor's stack. IKEv1 had structural problems, particularly with its Mode Configuration extension and the way it handled SA (Security Association) rekeying under load. IKEv2 cleaned that up, added native MOBIKE support for mobile users, and made dead peer detection essentially mandatory rather than optional. The result was fewer configuration foot-guns and less debug time when tunnels dropped unexpectedly.
Unlock The Power Of Secure Networking Whats New In Ipsec VPN
One of the bigger changes nobody talks about enough is how AEAD (Authenticated Encryption with Associated Data) ciphers became mainstream. Earlier IPsec implementations used AES-CBC with HMAC-SHA separately, which meant two distinct cryptographic operations per packet. Modern stacks now default to GCM and CCM modes, which combine authentication and encryption into a single pass. The performance difference is measurable. On hardware that supports AES-NI, moving from CBC-HMAC to AES-GCM typically reduces CPU overhead by roughly 30 to 40 percent on tunnel throughput. Not having AES-NI basically kills the advantage, and you will notice it immediately when routing more than 100 megabits through an older device. I ran into a specific problem last year that illustrates why these updates matter in practice. I was working with a client who had three remote offices connected via site-to-site IPsec tunnels using a mix of hardware from different vendors. Two sites were using newer equipment with strongSwan-based implementations supporting OCB-AES and SHA3-512, while the third office was still on a legacy gateway stuck at AES-CBC and SHA1. The tunnel to the third office kept renegotiating every forty-five minutes under moderate traffic loads. The root cause was not MTU issues or ISP jitter. It was the nonce reuse vulnerability in how the older implementation handled IKE rekey sequences. The workaround was implementing a manual phase 1 proposal override forcing both ends to negotiate using SHA256 and AES-GCM-128, then setting the DPD interval to ten seconds with a retry count of three. That stopped the renegotiation loop immediately. I wish I had seen that specific failure mode documented anywhere before I hit it. It was not in any vendor knowledge base. Another change worth understanding is how IPsec handles fragmentation now. Older implementations would fragment packets before encryption, which created a class of attacks where an adversary could reconstruct fragments across multiple captured sessions. Newer standards, particularly RFC 7383, introduced IPsec fragmentation that happens after encryption, meaning the outer IP header carries the necessary information without exposing the original packet structure to intermediate devices. This also means path MTU discovery behaves differently across VPN tunnels. If you are running UDP-based applications through your IPsec tunnel and seeing intermittent timeouts, check your PMTU settings first. It is almost always the issue.
The move toward cloud-native IPsec deployments is also reshaping how these networks operate. Traditional hardware concentrators are being replaced by software-defined VPN gateways that scale horizontally. Services like AWS Site-to-Site VPN and Azure VPN Gateway use IPsec/IKE as the transport layer but abstract most of the configuration away. The tradeoff is reduced visibility into the actual tunnel parameters. You can still specify encryption suites and pre-shared key rotation intervals, but you are trusting the provider's implementation details. For regulated environments, this is a real concern. If you need full auditability of your IPsec negotiations, you are better off running your own strongSwan or LibreSWAN cluster behind the cloud gateway. There is also the matter of certificate-based authentication replacing pre-shared keys in enterprise deployments. PSKs are convenient for home labs but they are fundamentally weak for anything beyond that. A single shared secret across dozens of sites means one compromised device jeopardizes the entire network. Certificates eliminate that problem, and modern tools like OpenSSL and easy-rsa make certificate management manageable. The learning curve is real though. I spent approximately six hours debugging a tunnel that refused to come up because the CA certificate chain on one endpoint was missing an intermediate certificate. The logs showed an authentication failure but gave zero indication that the chain was incomplete. Check your certificate chains before you check anything else when certificate-based IPsec fails to negotiate.
Get the Full Details
What You Should Actually Check in Your Current Setup
If you want to assess whether your IPsec implementation is current, look at these specific items. First, verify your IKE version. Anything under version 2 should be considered deprecated for production use. Second, check your cipher suites. AES-CBC should not appear in any production proposal. Third, confirm that Perfect Forward Secrecy is enabled on your phase 1 negotiations. DHE or ECDHE groups are the standard now. Fourth, verify your dead peer detection settings. Ten-second intervals with three retries is a reasonable baseline. Fifth, audit your certificate expiration dates if you are using certificate authentication. Certificates expiring mid-tunnel can cause cascading failures across your entire VPN infrastructure. There are scenarios where IPsec is simply the wrong tool. If you need zero-trust access controls, per-application authorization, or dynamic policy evaluation based on user identity and device posture, IPsec cannot deliver that. It operates at the network layer by design. For those requirements, something like WireGuard or a full zero-trust network access platform is more appropriate. WireGuard specifically has become the preferred alternative for many use cases because its codebase is roughly four thousand lines compared to IPsec's hundred thousand plus. The reduction in attack surface is significant, and the performance characteristics are consistently better, especially on resource-constrained devices. I migrated a client from IPsec to WireGuard last year for their field workforce VPN. The configuration went from approximately forty-five minutes of troubleshooting to about twelve minutes of actual configuration. That is not a marginal improvement. But WireGuard is not a drop-in replacement either. It does not have native support for NAT traversal in the same way IPsec does, it lacks built-in key rotation mechanisms, and it does not provide the same level of integration with existing RADIUS and LDAP directories. If your organization depends on those integrations, the migration requires additional infrastructure. There is no clean path from a mature IPsec deployment to WireGuard without planning for that gap.
The practical takeaway is that IPsec is not dying, but it is no longer the default assumption for new deployments. The protocol remains solid for site-to-site connectivity where you need compatibility with existing firewall and routing infrastructure. For remote user access, the landscape has fragmented, and you need to evaluate your specific requirements before committing to any single solution. The updates to IPsec itself, particularly around AEAD ciphers, IKEv2 improvements, and cloud-native gateways, make it viable for many environments that previously had no good alternative. Just make sure your implementation matches what the protocol can actually do today rather than what it did ten years ago.


