Website Security Isn't Something You Install Once
Most people treat site security like a checkbox. They slap on a plugin, change their password, and call it done. That approach falls apart within six months because the threat landscape doesn't freeze while you're not looking. I spent years managing infrastructure for small-to-mid-size web properties before moving into consulting. The sites that survive tend to be the ones treated like living systems, not static installations. Here's how that actually plays out. The phrase keeps showing up in SEO-heavy landing pages that sell you a newsletter subscription disguised as education. The underlying advice is usually sound, but the packaging makes it easy to skip over the actual mechanics. Let's get into what matters. Your hosting environment determines the ceiling of your security posture. Shared hosting with five hundred other tenants means a vulnerability on a neighbor's site can cascade into yours through cross-contamination. I once worked with a client whose WordPress install was fine by every metric. The compromise came from a PHP mail header injection exploit running on a sister account in the same cPanel. No amount of WordPress hardening would have prevented that.
Practical first move: Move to a VPS or dedicated environment where you control the server stack. If budget is tight, at minimum verify that your host isolates accounts properly and offers firewall-level protection between tenants. Ask them directly. Most will admit they don't. That tells you something.
Update Discipline Beats Fancy Tools
The statistics are boring but consistent. Over sixty percent of compromises involve outdated software versions with known patches. This isn't theoretical. I've seen it repeatedly. A client was running a theme from 2019 that hadn't been touched since. The developer stopped supporting it in 2021. Someone found the exploit on a public vulnerability database and automated the attack. The site went down on a Tuesday morning. Setting up automated updates sounds simple but most platforms handle core updates fine while plugins and themes are left to rot. My workaround was setting up a staging copy of each site. Updates hit staging first, run for forty-eight hours, then promote to production if nothing breaks. This added maybe twenty minutes per update cycle but caught three legitimate compatibility issues before they reached users.
Get the Full Details
SSL Is Not Optional And It's Not Enough
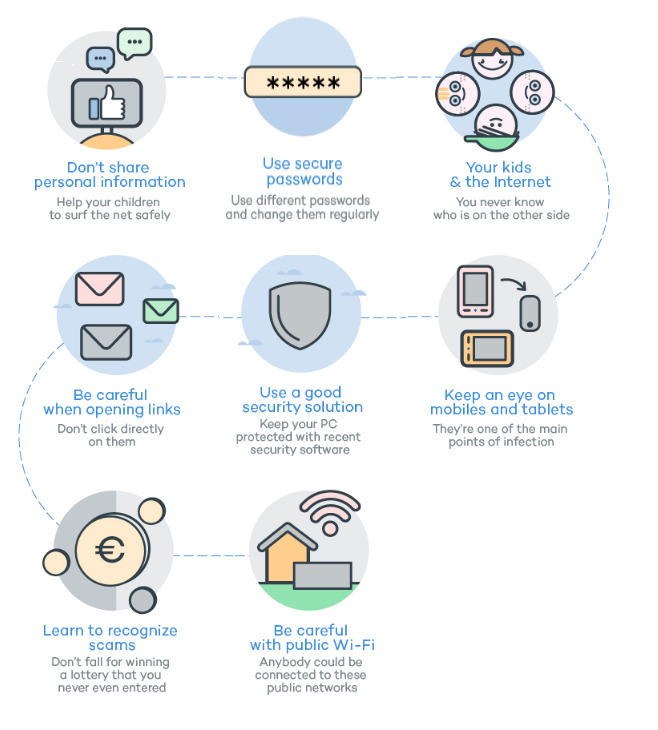
H T T P S encrypts traffic between the visitor and your server. It does nothing about malware on your server, phishing on your content, or insecure forms that pass data in plain text through JavaScript. I still see people confuse having a green padlock with being secure. It's like putting a deadbolt on a screen door and calling it a mansion. What to actually do with SSL: Enable H T T P Strict Transport Security headers. Set the max-age to at least one year. This forces browsers to always use encryption, preventing downgrade attacks where a MITM strips your SSL mid-connection. It costs nothing and takes thirty seconds to configure on most servers. Most people don't bother.
Authentication Is Where Everything Breaks
Passwords alone are a losing proposition. The average business login sees thousands of brute force attempts daily from compromised credential lists sold on dark web forums. Using the same password anywhere is inviting disaster. I had a client who used one password across twelve different platforms. When a random fitness app leaked their credentials, every other service fell within forty-eight hours. Multi-factor authentication should be non-negotiable on everything that touches your site. Admin panels, hosting dashboards, email accounts, DNS registrars. Even hardware key support when available. YubiKeys cost about twenty dollars and dramatically raise the barrier for attackers. I recommend enrolling them on every account that supports it. Yes, even your email provider. Your email is the master key to everything else.
Backups Are Useless Without Testing
Every hosting provider claims to back up your data. That's marketing language for "we might have your files somewhere." The critical step nobody does is actually restoring from those backups on schedule. I audit this constantly during security assessments and find that roughly half of clients have unverified backup systems. Some have backups that fail silently. Others have backups of incomplete directory structures. The test: Pick one backup, restore it to an isolated environment, verify file integrity, check database connections, and confirm the site functions normally. Document the process with timestamps. Do this quarterly at minimum. When you actually need the backup under pressure, you want to know it works, not discover it doesn't at 3 AM.
Monitoring Changes Everything
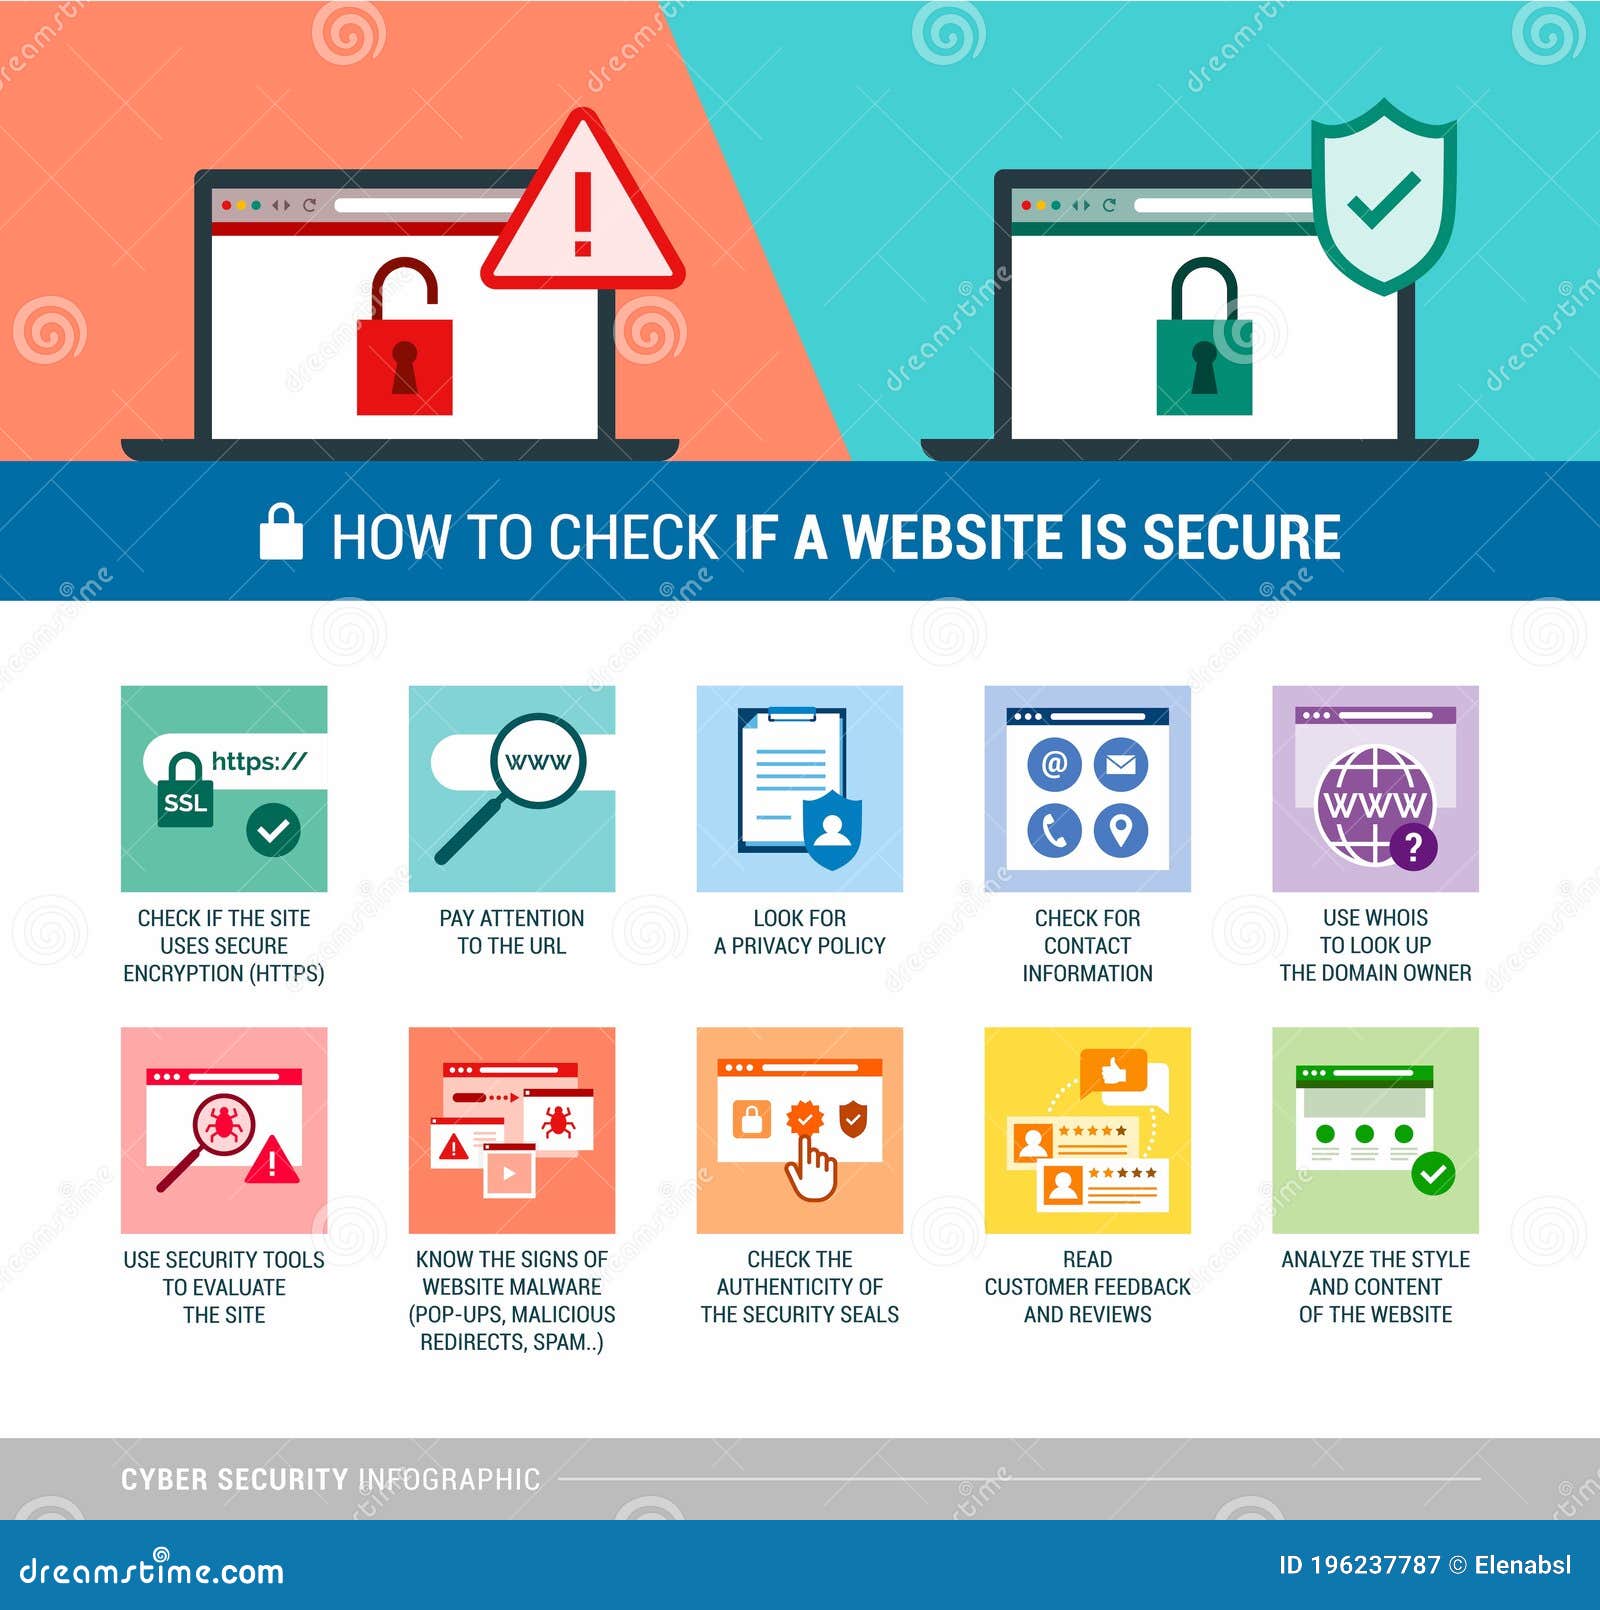
You can't detect a breach if you're not watching anything. Basic monitoring includes file integrity checking, login attempt logging, and uptime alerts. More advanced setups add behavioral analysis and anomaly detection. I set up a combination of Wordfence for WordPress sites and fail2ban for server-level intrusion prevention. Wordfence monitors file changes and flagging unauthorized modifications. Fail2ban bans IPs after repeated failed login attempts. A useful detail: Configure your monitoring tools to send alerts to a separate communication channel. If your admin email gets compromised, having alerts route only there gives attackers notice of your detection capability. Use a secondary email or a Telegram bot for security notifications instead.
Content Security Policy Headers
C S P headers are one of the most underutilized defenses available. They tell browsers exactly which sources your site is allowed to load scripts from. A properly configured C S P prevents most cross-site scripting attacks by blocking inline scripts and unauthorized external sources. Most developers avoid them because configuration can be finicky and breaking changes appear immediately in production. My approach: Start in report-only mode. The header detects violations without blocking them. Run it for a week, collect the violations, fix your code, then switch to enforcement mode. This avoids the common pitfall of deploying a C S P that breaks half your functionality and then disabling it out of frustration.
The Hard Truth About Free Tools
Free security plugins and tools are fine for basic protection but they create a false sense of completeness. Wordfence's free version covers scanning and basic WAF functionality. It doesn't cover behavioral analysis, advanced threat intelligence feeds, or centralized management across multiple sites. When you're running a single small site, that's probably adequate. When you're managing fifteen sites, you'll hit limitations fast. What to expect: Paid security suites like Patchstack or Sucuri offer centralized dashboards, priority support, and more comprehensive rule sets. The tradeoff is monthly cost and depending on the provider, potential vendor lock-in. I recommend starting free, evaluating your actual needs after three months of operation, and upgrading only when you can point to specific gaps rather than vague anxiety.
Human Factors Remain The Weakest Link
Technical controls fail when humans bypass them. I've seen admins disable two-factor authentication because it slowed down their workflow. I've seen them reuse passwords because the password manager seemed complicated. Security is only as strong as the person making decisions about it. This isn't theoretical. Practical advice: Document your security procedures in a simple checklist. Not a forty-page policy manual. A one-page reference that anyone on your team can follow. Include the common shortcuts people take and explain why they shouldn't. Keep it visible. Update it when procedures change. Review it quarterly.
When Things Go Wrong
No amount of preparation eliminates risk entirely. You will get compromised eventually if you maintain a public web presence long enough. The difference between a minor incident and a catastrophic one comes down to preparation. Have an incident response plan written down before you need it. Know who to contact, what information to gather, and what steps to take in the first hour. The first hour matters most: Document everything. Take screenshots. Preserve logs. Don't immediately restore from backup and hope it fixes the problem. Restoring from a compromised backup just restores the compromise. Identify the entry vector, patch it, then restore clean. The timeline from detection to containment should be measured in hours, not days.
Resources Worth Keeping Around
The Mozilla Observatory provides free security header analysis. Check your site there regularly. Nixstats offers monitoring with security-focused alerts if you manage multiple servers. The OWASP top ten list remains the best baseline reference for understanding common vulnerabilities, even though it gets updated periodically. NIST has framework documentation that's surprisingly accessible for small operations without compliance requirements. Browser security headers can be verified directly through developer tools. Network tab shows request headers. Console logs reveal C S P violations in real time. This diagnostic approach catches configuration issues faster than waiting for an external scanner to run weekly. The landscape shifts continuously. New vulnerabilities surface in popular platforms within days of disclosure. A guide written today may already be slightly outdated on specific version numbers. The principles remain stable though. Layered defense, regular verification, and acknowledging that perfect security is impossible are the foundations worth building on. Everything else is detail work.