Understanding Sideloading on Modern iOS
iOS has always been a walled garden, but Apple has given developers enough tools that you don't actually need to jailbreak your device to install apps from outside the App Store. The current landscape revolves around a few different technical paths, and most of the sites and forums talking about "iOS god apps" are just repackaging the same basic information with dramatic headers. I've spent years watching these services come and go, and there's a lot of noise to cut through. The core concept here is sideloading. You're taking an IPA file and installing it on your device using certificates or entitlements that Apple's signing system allows. The three main routes people actually use are AltStore, TrollStore, and Sideloadly. They work differently and have very different limitations. AltStore uses your own Apple ID with a free developer certificate. It re-signs apps every seven days unless you have a paid developer account or a special enterprise certificate. It works on all devices running iOS 12 and above. The catch is the refresh cycle. If you go more than seven days without connecting to your computer, the apps expire and stop working. I spent three weeks on vacation once without doing this and came home to twelve broken apps. Annoying but manageable.
TrollStore is different entirely. It exploits a vulnerability in iOS that allows permanent code signing without re-signing. Once it's installed, apps stay installed indefinitely. The problem is it only works on specific iOS versions — mainly iOS 14 through 16.2 on certain devices. Apple patches these vulnerabilities, so the window of opportunity keeps shrinking. If you find a TrollStore-compatible device, use it immediately before any update closes the door. Sideloadly is essentially a GUI wrapper around the same signing process as AltStore, but it's more reliable for bulk operations. It handles certificate management better and supports iTunes backups for restoration. I switched from AltStore to Sideloadly after one too many failed resign cycles where my IPA files would corrupt during the signing process. The difference was noticeable — Sideloadly completed installations that AltStore kept failing on. Enterprise certificates are the wildcard in all of this. Some "ios god" app stores distribute apps using compromised enterprise certificates. These let you install directly from within a browser without any computer connection. The downside is that Apple revokes these certificates regularly. When that happens, all the apps you installed through that certificate stop working overnight. I've seen it happen. You spend hours setting up a third-party app store, then one morning everything is dead. The certificate gets revoked without warning and there's nothing you can do about it.
Here's something most guides don't mention: the actual IPA files matter more than the installation method. A lot of these third-party app stores modify the IPA before distributing it. They strip analytics, change bundle IDs, and sometimes inject adware into the code. I found this out the hard way when an app that claimed to be a premium streaming solution started pulling data through an unknown domain. Checked the IPA source and the entitlements were pointing to a server I'd never heard of. Deleted it immediately. Another thing nobody warns you about is the sandbox restrictions. Even when you successfully sideload an app, it still operates within iOS sandboxing. This means features like push notifications, background app refresh, and certain API calls work differently or not at all compared to App Store versions. A lot of users blame the sideloading method when really the issue is just how iOS treats unsigned or self-signed code. Apps that rely heavily on system integrations are the most affected. Photo editing apps with live integration, fitness trackers that need health data access, these hit walls regardless of how cleanly you installed them. The practical setup process starts with choosing your method based on your iOS version and device. Check your exact model and firmware first. If you're on an older iOS version that supports TrollStore, grab it while it's available. For everyone else, you'll need a computer and the AltStore or Sideloadly route. Download the appropriate tool from the official GitHub repositories — not from random mirrors. There are fake copies of both tools with malicious payloads sitting on third-party download sites.
Get the Full Details

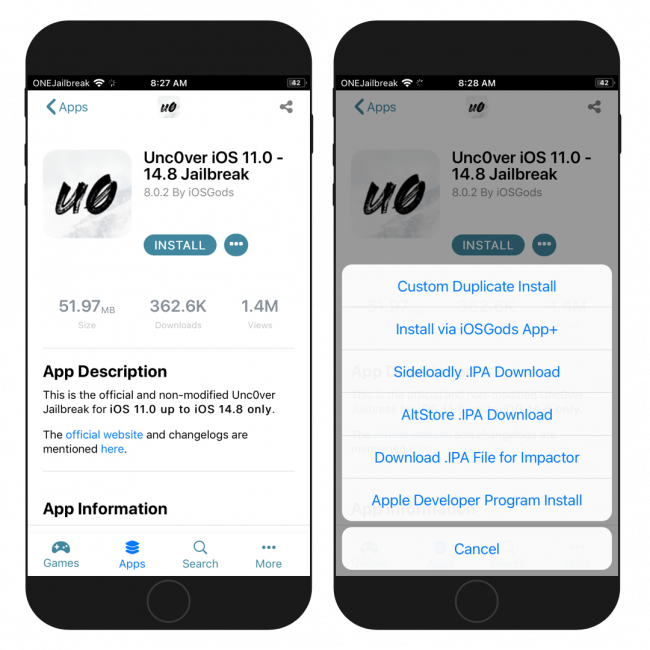
Once installed, you'll connect your device, authenticate with your Apple ID, and add your sources. Most ios god app collections organize their IPAs into webpages where you download the file directly, then open it in the sideloading tool. The process takes about two minutes per app if everything goes smoothly. Failed attempts usually come down to expired certificates, corrupted IPA files, or conflicting bundle identifiers from apps you already have installed. Backup strategy is important. Before you start sideloading apps, make a full device backup through Finder or iTunes. If something goes wrong with your certificates or your Apple ID gets flagged, you want to be able to restore without losing data. I learned this after Apple temporarily suspended my developer account for unusual activity and I had to wipe and restore my device. Two hours of work that could have been thirty minutes. The honest assessment is that this isn't as seamless as these guides make it sound. You'll deal with certificate expirations, occasional app failures, and the constant tension between wanting newer features and needing to stay on a compatible iOS version. But for apps that aren't available through legitimate channels or for region-locked content, the effort is usually worth the tradeoff. Just don't expect it to work perfectly every time, and don't trust any service that promises you'll never have to deal with these problems again.