Getting Started With The Meta Developer Platform
The Meta Developer Dashboard is where you go when you need to build something on top of Facebook's infrastructure. It sounds straightforward until you actually sit down to configure an app and realize there are about forty permission scopes, three different authentication flows, and a review process that can take anywhere from twenty minutes to six weeks depending on which features you request access to. I spent three hours last year figuring out why my access token was being rejected, only to discover I had selected the wrong app mode in the settings. Basic stuff, but easy to miss when you're rushing.
Unlock The Power Of Facebook With Meta Your Ultimate Guide To Facebook Developer
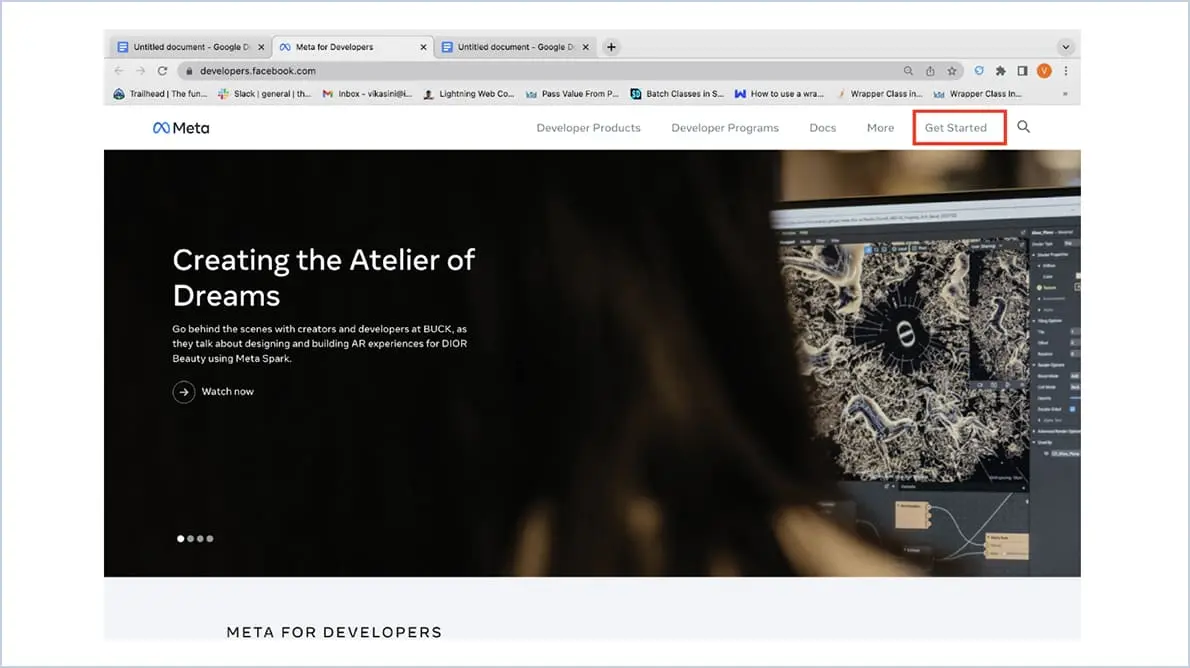
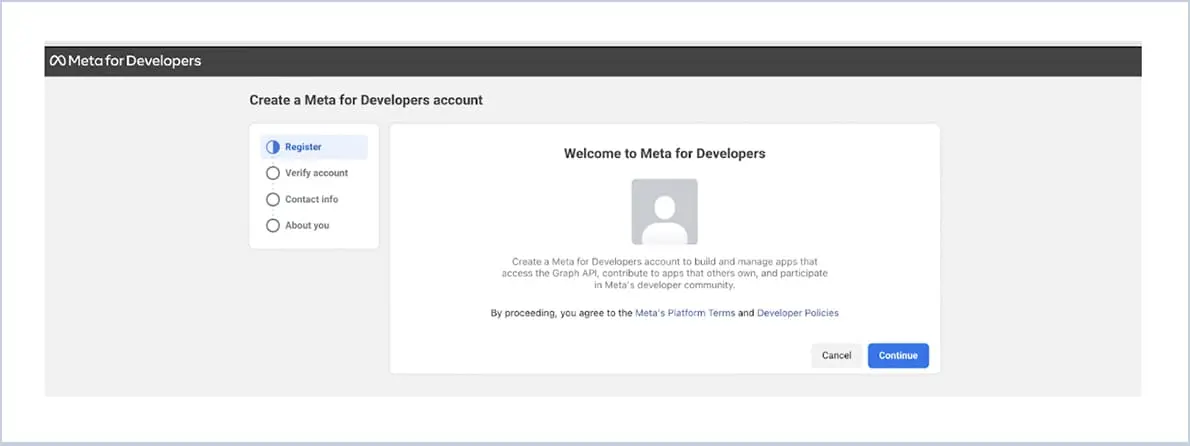
Here is how the whole thing actually works, not the polished version they show in promotional material. You start by creating a Meta for Developers account at developers.facebook.com. Once logged in, you click Create App and pick a category that matches what you're building. The category choice matters more than most people realize because it determines which default permissions and features are pre-enabled. If you pick Business for a consumer-facing tool, you will spend time reconfiguring things later. I picked the wrong category on my first project and had to recreate the app entirely because some settings are locked after creation. After the app is created, you get an App ID and App Secret. The App Secret is not something you hardcode into a client-side application. I learned that the hard way when a junior developer on my team pushed credentials to a public repository. You store it server-side, in environment variables, and you rotate it regularly. Meta lets you generate new secrets from the app settings page without destroying existing ones, which is useful.
Understanding The Graph API
The Graph API is your primary interface for reading and writing data. It uses RESTful endpoints structured around objects like users, pages, posts, and groups. A typical request looks like fetching the authenticated user's profile data by hitting a specific endpoint with a valid access token in the query parameters or authorization header. The access token system is where most beginners hit walls. There are user tokens, app tokens, and page tokens, and they are not interchangeable. A user token is tied to a specific person who has granted permission through OAuth. An app token is just the App ID and App Secret combined and is useful for server-to-server calls that do not require user context. A page token represents permission to act on behalf of a Facebook Page, and it is derived from a user token that has the manage_page permission. I once tried using a user token to post to a Page and got a confusing error that took me two days to untangle. The fix was generating a long-lived page token through the Graph API Explorer and caching it properly. Access tokens expire. User tokens generated through the standard flow last about an hour. You can exchange them for long-lived tokens that last sixty days using the token exchange endpoint, but even those expire. The only tokens that do not expire are page tokens, and only if the page admin has granted permanent permission through the initial OAuth dialog. If that admin uninstalls the app or changes their password, you lose the token and have to go through the flow again. This is important to plan for if you are building something that runs unattended.
OAuth And Permission Scopes
When you ask a user to log in through your app, Meta presents a permissions dialog. Each permission you request has a scope string like publish_to_groups or read_insights. The dialog shows all requested scopes at once, which means users often approve things they do not fully understand. Meta requires you to justify each scope during the app review process, and reviewers reject apps that request unnecessary permissions. I had an app rejected twice because I included read_insights without a clear explanation of why the app needed page analytics data. The fix was removing the permission entirely and finding an alternative way to get the same data through a different endpoint that did not require that scope. The login flow itself has changed over the years. The old JavaScript SDK approach still works but is considered legacy. The current recommended approach uses the Meta Login Kit for web and the corresponding SDKs for mobile platforms. For web integrations, you initialize the SDK with your App ID, call the login method, and handle the response in a callback. The response contains an authorization code that you exchange for an access token on your server. Never do the token exchange client-side. I have seen this mistake happen repeatedly in open source projects, and it exposes your App Secret to anyone who inspects network traffic.
Get the Full Details
App Review And Approval
If your app accesses any data beyond the basic profile fields or serves users outside your development team, it needs to go through Meta App Review. This is not optional. Apps in development mode can only be used by roles assigned to the app: admin, developer, tester. Once you add a non-role user, the app must be reviewed or those users will not have access to restricted features. The review process requires you to provide screenshots of the login flow, a description of each permission you are requesting, and a testing account that reviewers can use to evaluate your app. I learned that the testing account should have a real profile with a profile picture and some activity, not a blank or suspicious-looking account. Reviewers reject apps with test accounts that look like spam. One of my reviews took eight days because the reviewer could not log in with the test credentials I provided. The issue was that the test account had two-factor authentication enabled, which the reviewer did not know about. Disable 2FA on test accounts before submitting for review.
Common Pitfalls And Edge Cases
Rate limiting is one area that causes problems. The Graph API enforces different rate limits depending on the endpoint and the type of token being used. Business endpoints have stricter limits than personal endpoints. If you hit the limit, you get a 429 error with a retry-after header telling you how long to wait. I built a script that processes page insights in bulk and ran into rate limits constantly. The solution was implementing exponential backoff with jitter and batching requests where the API supported it. Some endpoints allow batch operations where you can combine up to ten requests into a single HTTP call, which cuts down on both rate limit hits and latency significantly. Another issue is webhook validation. If you set up webhooks to receive real-time updates about changes to your object, Meta sends a verification request when you configure the endpoint. You need to respond with the exact challenge string they provide, or the subscription fails silently. I wasted an afternoon debugging a webhook that appeared to never fire because the initial verification handshake was failing due to a trailing slash mismatch in the callback URL. Webhook URLs must match exactly as configured. Data retention is another thing people overlook. Meta does not guarantee that data you fetch through the API will remain available indefinitely. Fields can be deprecated, endpoints can change, and access can be revoked. I once relied on a custom field that was quietly removed during a platform update, which broke a reporting feature in production. Always check the changelog and version your API calls to a specific Graph API version rather than relying on the latest. Pinning to a version gives you stability, though you still need to test when Meta announces deprecation warnings for older versions.
What The Platform Cannot Do
It is worth noting what you cannot do, because the marketing material makes it sound like the API gives you broad control. You cannot scrape profiles. You cannot access message content unless the user explicitly grants the permissions and even then it is limited. You cannot post on behalf of a user without their explicit action triggering the publish flow. You cannot bypass the app review process to access restricted features, no matter how much you pay or how many contacts you have at Meta. The platform is designed for integrations, not for automation that replaces human interaction. Anyone promising you a workaround for these limitations is selling something that will get your app banned. If you need to process large volumes of social data, the official API is the wrong tool. Third-party data aggregators or official partnership programs exist for that use case, but they come with their own costs and restrictions. The developer platform is meant for building genuine integrations where users opt in and understand what data is being shared. The platform documentation has improved over the years but still has gaps, particularly around edge cases and error handling. When the docs do not cover something, checking the changelog and looking at Stack Overflow threads from the past year usually surfaces what you need. The community here is smaller than it used to be, but the active developers tend to be experienced enough to give accurate answers. Just make sure you include your App ID and the exact Graph API version you are using when asking for help, because behavior can differ between versions.