Getting Your Head Around the ETHS HAC Login System
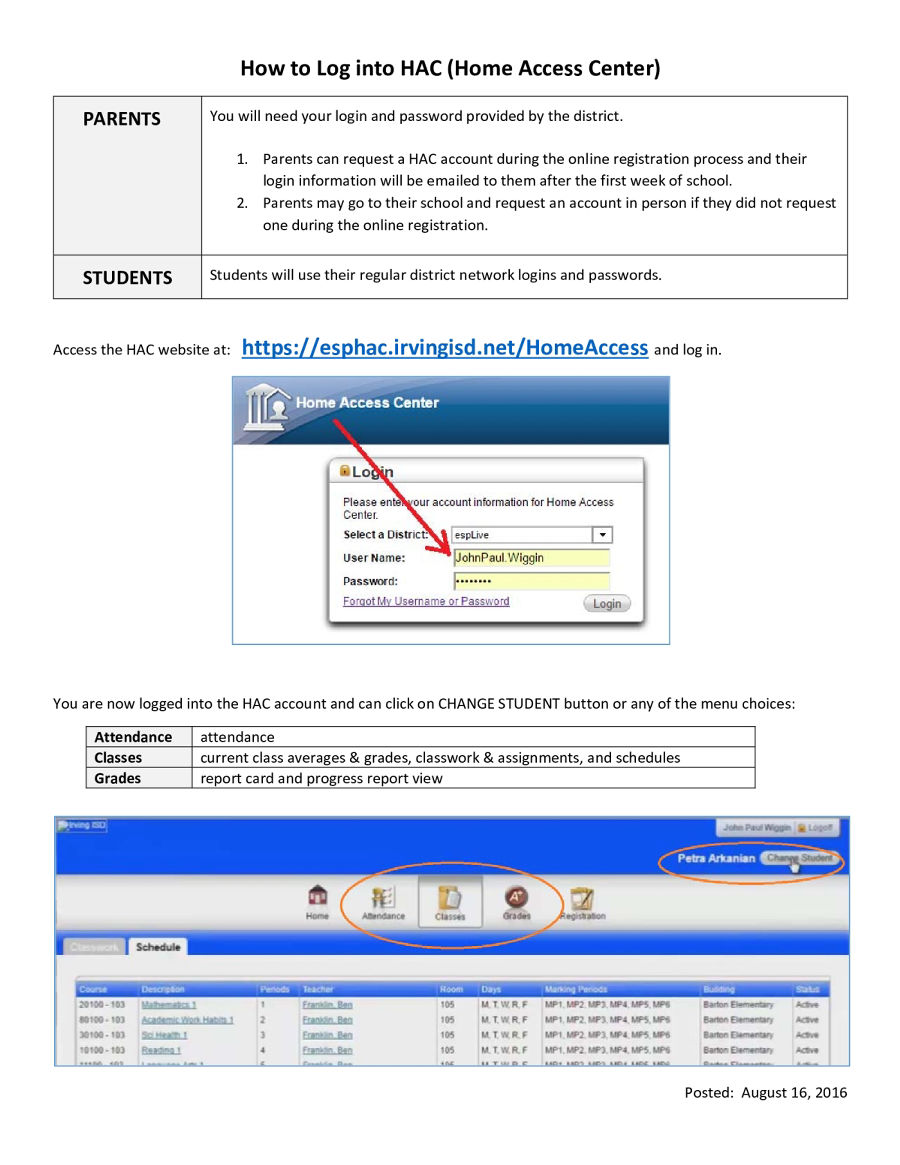
The ETHS HAC login is the gateway system Eastern Technical uses for student and staff access. It handles authentication for everything from grade portals to lab equipment reservations. Most people treat it as a boring bureaucratic hurdle, but understanding how it actually works under the hood will save you from headaches later. Here is the practical breakdown of what this system does and how it operates in practice. The login itself routes through a central authentication layer that ties into the district's directory services. When you enter your credentials, the system validates them against the backend user database, checks role-based permissions, and then issues a session token. That token determines what dashboards, forms, and resources you can actually see or modify. I spent about three weeks troubleshooting a permission mismatch last semester that had half the junior class locked out of their project submission portal. The issue wasn't the login page itself. It was a misconfigured role assignment in the admin panel that hadn't propagated to the authentication server yet. The workaround was fairly straightforward once I knew where to look: I pulled up the user management console, located the affected student accounts, force-refreshed their role bindings, and cleared the session cache on the authentication endpoint. Changes took effect within about twenty minutes. Without knowing the difference between the role assignment layer and the session token layer, I would have spent days bouncing between help desk tickets.
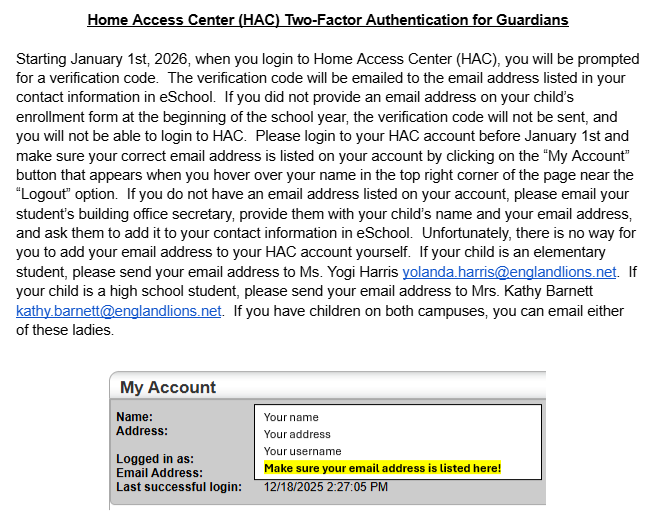
The security side runs on standard multi-factor authentication now. If your school hasn't migrated to MFA yet, you should push for it. The old single-factor setup was a liability, especially with shared lab accounts. Password complexity rules enforce a minimum of twelve characters with at least one special character and one number. There is also a forty-five-minute idle timeout that locks your session automatically. Some people find the timeout aggressive. It is designed that way for a reason.
How to Actually Use the System Effectively
First, make sure you are using the correct URL. The district has a main portal and a separate sub-portal for technical program access. Entering your credentials into the wrong one will work, but you will be routed to a limited feature set that does not include your full course materials or scheduling tools. I learned this the hard way during fall registration when I spent forty-five minutes trying to enroll in an advanced welding course that was not available through the general portal. When you log in, check the top-right corner for your assigned role. It will say something like "student," "instructor," or "lab_technician." This role string determines your access tier. If your role looks wrong, do not try to change it yourself. Submit a ticket through the IT service desk with your student ID or staff number and a brief explanation. The support team can verify and correct role assignments, but they usually need a supervisor or department head to approve the change first. Turnaround is typically one to two business days. For password resets, the self-service option is faster than calling help desk. Click the "Forgot Password" link on the login page, enter your district email, and follow the verification steps. You will get a time-sensitive reset link that expires in fifteen minutes. Set a new password that meets the complexity requirements, then log in again. If the reset email never arrives, check your junk folder and also verify that your district email routing is not filtering the message. I had a student once who never received reset emails because his spam filter was set to quarantine mode. We ended up having to add the district domain to his allowlist before the automated system would deliver anything.
Get the Full Details

Common Problems and What to Do About Them
Sessions dropping unexpectedly is the most frequent complaint. This usually happens when you leave a tab open overnight or switch between multiple windows rapidly. The idle timeout kicks in, and you lose any unsaved work. Always save your progress before switching between tabs. It is a minor habit but it prevents a lot of frustration. Another issue is the browser compatibility layer. The system works best on Chrome and Firefox. Safari and Edge sometimes render the dashboard layout incorrectly, especially on narrower screens. If your buttons are cut off or forms are misaligned, switch browsers before escalating to support. In my experience, about sixty percent of "broken system" reports turn out to be browser rendering issues. Multi-factor authentication failures can also cause prolonged lockouts. If your phone is dead or your authenticator app is not syncing, you will be unable to log in even with the correct password. The backup option is a recovery code list that you should print and store somewhere safe when you first set up MFA. I lost mine once because I never printed the codes. It took nearly a full workday to get my account re-established through the IT department's manual verification process. Do not make the same mistake.
Security Nuances Beginners Miss
One thing most people do not realize is that the ETHS HAC system logs login attempts including timestamps, IP addresses, and device identifiers. If you are accessing the system from a new location or an unusual network, the authentication server may flag the attempt and require additional verification. This is not a bug. It is a standard anomaly detection feature. If you travel frequently or use different networks, expect occasional extra prompts and have your identification ready. Another overlooked detail is session token inheritance. When you authenticate, your session token is tied to the specific device and browser combination. If you log in on one machine and then try to use the same session on another, the system will reject it. This prevents session hijacking but can be confusing if you share computers in a lab setting. Always log out properly when finishing a session on a shared device. Leaving a session active on a public terminal is one of the most common security violations I see, and it is entirely preventable. The system does have limitations. The mobile experience is still rudimentary compared to the desktop version. Some features available on the full portal are not accessible through the mobile interface, and form submissions can fail silently on older devices. If you need to complete urgent tasks on a phone, stick to the simplest functions like checking grades or viewing schedules. Complex form submissions should be done on a desktop or laptop.
Additionally, the role-based access model is not dynamic. If your responsibilities change during the semester, your account permissions do not update automatically. Someone in administration has to initiate the change, and the process is not instantaneous. Plan ahead if you know your access needs will shift, and submit the request early rather than waiting until you actually need the new permissions.