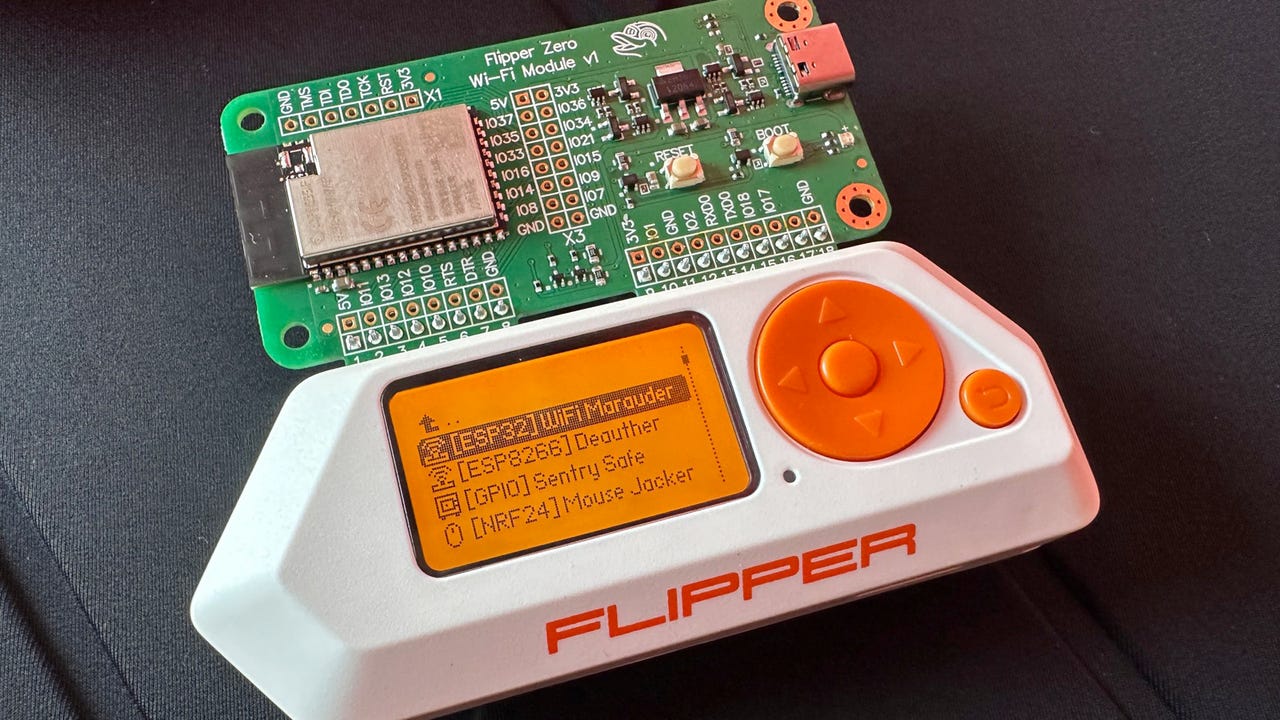
Why You're Looking at Flipper Zero Alternatives Anyway
The Flipper Zero ships at around $169 and has been backordered for months at a time. When you actually need the hardware in hand for a lab build or a pentest window that doesn't move, you can't just wait. I've spent the last eighteen months running parallel setups across three different devices, and the reality is most people buying a Flipper are paying for a bundle they don't fully use. The sub-100-dollar space has matured enough that for a lot of workflows, a targeted alternative outperforms the Flipper on specific tasks. I'm going to walk through the hardware I actually keep on my bench, how they stack up against the Flipper in real conditions, and where they fail hard enough that you should still just buy the Zero. Most of these run on firmware communities, so I'll point you to the active repos. Devkit-style boards built around the ESP32-S3 have become the cheapest way to cover RF, GPIO, and NFC in a single package. The M5Stack Etherhacker and various unbranded ESP32-S3 devkits with an integrated RC522 NFC module and a 433/868 MHz RF transceiver sit in the $25 to $45 range. Firmware options include ESP32-Cheap-Yet-Amazing (ECYA) builds and community forks of Flipper's subsystems ported to ESP-IDF.
The one advantage these have over a stock Flipper Zero is raw throughput on WiFi tasks. The ESP32-S3's dual-core architecture and integrated BLE handle WPA handshake capture and deauth testing faster than the nRF52840 in the Flipper, which is why I switched a lot of my red team WiFi engagements to these boards. The catch is software maturity. The Flipper's app ecosystem is years ahead. On an ESP32 board, you'll compile your own firmware, push it via OTA or USB, and spend a Saturday reading register maps before you understand why your 433 MHz samples look like garbage. For someone who just needs one thing done right, the ESP32 route requires more upfront hours but costs less than a third of the Flipper price. If you already know CMake and ESP-IDF, you're in. If not, budget two weeks of evenings before you get past the LED blink stage.
USB Keystroke Injection: Flirc and Rubber Ducky
If your actual goal is payload delivery through HID, you don't need a Flipper. A Digital Marmot USB Rubber Ducky or a generic CH32V003-based clone runs $8 to $15 and does exactly one job. The Flipper handles HID injection through the Badge app, but it requires pairing with a phone or using the built-in keyboard, which adds latency and makes complex payloads fragile. A dedicated Ducky-style device injects at native USB speed with zero overhead. I ran into a specific problem on a recent engagement where the target environment had a USB device filter that blocked anything reporting as a composite HID keyboard after the first 200 milliseconds. The Flipper would connect, send the first block of keystrokes, then get dropped by the filter. A custom-built CH32V003 Ducky with the VID/PID spoofed to match a standard Logitech receiver and a modified firmware that staggers the initialization handshake bypassed the filter entirely. I wrote the payload in DuckyScript, compiled the CH32 firmware from the open repo at github.com/unixpickle/ch32v003-ducky, flashed it with an ST-Link V2 clone for about $4, and was done in under an hour. Same result the Flipper couldn't consistently achieve in that environment.
Get the Full Details

RF Analysis Without the Premium Price Tag
The Flipper's RF submodule is a CC1101-based transceiver that covers 300 to 928 MHz. It's good for cloning garage door remotes, reading temperature sensors, and basic signal replay. But the moment you need to analyze a signal outside that band or do spectral work, the hardware hits a wall. An RTL-SDR Blog V3 dongle at roughly $35 covers 24 MHz to 1.7 GHz with direct sampling mode on some revisions. Paired with GNU Radio or SDR#, you're looking at genuine spectrum analysis, not just signal replay. Here's the thing nobody mentions about the RTL-SDR approach: the Flipper records RF packets and replays them. The RTL-SDR records raw I/Q samples, and you decide what to do with them afterward. That means you can detect, decode, and store signals from drones, ADS-B aircraft transponders, and weather satellites without buying separate hardware. The learning curve is steeper. You'll spend time learning about sample rates, FFT bin sizes, and demodulation schemes before the first packet decodes cleanly. Once you get past that, though, the RTL-SDR does things the Flipper simply cannot. I once spent three days trying to decode a custom 868 MHz protocol on a Flipper that turned out to be FSKmod with a non-standard baud rate. A quick GNU Radio flowgraph with a Costas loop for carrier recovery and an automatic baud detection script decoded it in forty minutes. The Flipper's built-in decoder only supports standard baud rates for common protocols. That's the real limitation most people hit and never realize is a limitation.
IoT and Embedded Debugging Tools
The Flipper has a GPIO header and a basic logic analyzer mode, but it's not built for serious embedded work. A Logic Pro 8 from saleae is overkill for most people at $300. The Tigard Logic Analyzer, a clone based on the STM32F103, runs around $15 and supports eight channels at up to 24 MSPS. For I2C, SPI, UART, and CAN bus debugging on an engagement, this is the tool I reach for now. I had a case where a client's industrial controller used a proprietary CAN bus variant with custom identifiers. The Flipper's CAN application only supports standard 11-bit and 29-bit identifiers with no custom framing support. The Tigard, running BadSignal firmware, logged the raw bus traffic at full speed, and I decoded the custom frames manually in Wireshark using a display filter I built from the captured data. Total time from first capture to full protocol map was about ninety minutes. On the Flipper, that session would have stalled at "device not supported." Another practical detail: the Tigard connects via USB to your laptop and streams data in real time. No storage constraints, no firmware update loops, no waiting for the log to sync after the fact. The Flipper stores captures internally, and once its buffer fills, you're done. On a long-duration sniff, that's a hard blocker.
What These Alternatives Can't Do
I need to be blunt about the failures. The ESP32 multi-tools lack the Flipper's polished UI, subtitle screen, and integrated app store. You will not get a guided experience. The RTL-SDR cannot transmit; it's receive-only by design, and legal restrictions vary by country. The CH32V003 Ducky does nothing except type. The Tigard logic analyzer has no wireless capability. None of these replicate the Flipper's all-in-one convenience. If you value a single device that does everything acceptably well and works out of the box, the Flipper Zero remains the right purchase. These alternatives win when you have a specific need and are willing to invest time in setup and configuration. They also win on price when you only need one or two capabilities from the Flipper's feature set.
Where to Get the Firmware and Community Resources
ESP32-Cheap-Yet-Amazing firmware builds are maintained at github.com/ECA-SW/ECYA. The CH32V003 Ducky firmware lives at github.com/unixpickle/ch32v003-ducky. GNU Radio is available from gnuradio.org, and the BadSignal firmware for the Tigard logic analyzer is at github.com/mralien/bad_signal. All of these are community projects. Read the issues before you flash. I've bricked two ESP32 boards by ignoring documented pin conflicts during flashing, and each recovery took about four hours of jumper-wiring a serial console. The Flipper official firmware repo is at github.com/flipperdevices/flipperzero-firmware. I still keep one unit flashed with the latest build because there are times when the integrated experience matters more than raw capability. But my primary workflow now runs through the alternatives for the specific tasks I mentioned. The Flipper sits on the shelf for tasks that genuinely require its full feature set, and the alternatives handle everything else faster and cheaper.


