Extranet landing pages aren't what most people think they are
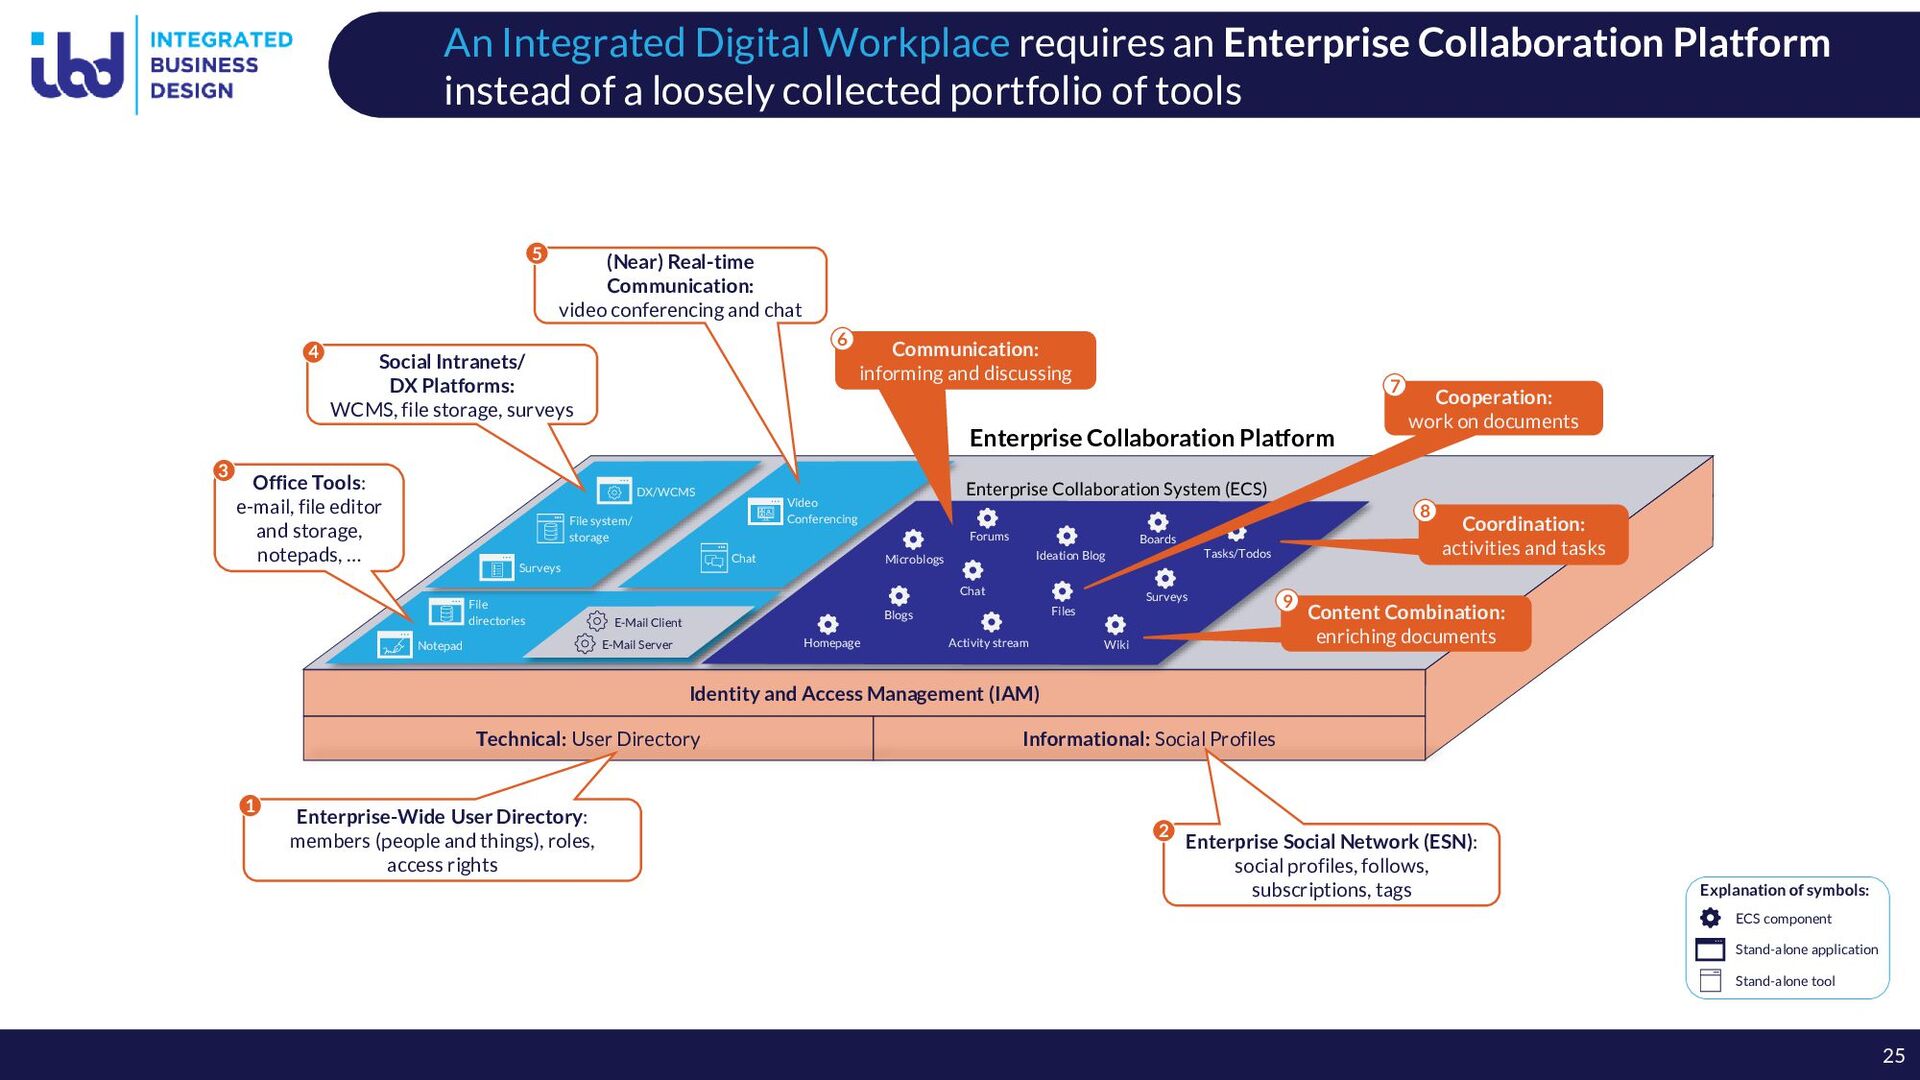
I spent a good chunk of 2023 untangling a mess where a mid-sized manufacturing firm had bolted six different partner portals onto their network without any centralized authentication layer. Each portal had its own login system. Some used basic HTTP auth. One was completely open to anyone who guessed the URL pattern. It took about three weeks just to map the attack surface. The fix wasn't fancy. It was an extranet landing page with SAML-based SSO redirecting to the appropriate backend service based on claims. That was a messy example. Most implementations are far more boring. And that's usually the problem. People treat extranet landing pages as just another web page with a form on it. They're not. They're gateways. The difference matters when you're dealing with external suppliers, contractors, or joint venture partners who need controlled access to internal systems without seeing everything. The modern extranet landing page is really a centralized routing and authentication layer. It sits between your external users and your internal services. Instead of each department building their own portal with their own security model, you give them a single entry point. That entry point handles identity verification, session management, and then routes the user to whatever resource they've been granted access to. Simple in theory. Messy in practice because nobody agrees on what "simple" means until something breaks at 2 AM.
Unlock Secure Collaboration How Extranet Landing Pages Are Transforming Enterprise Connectivity
Before I get into how to actually set one up, I want to address the word transformation in the heading. A lot of vendors use that word loosely. An extranet landing page doesn't transform anything by itself. It enables a specific pattern of connectivity that would otherwise require custom development on every internal system that needs external access. That's the distinction. It's an enabler, not a magic solution. The basic architecture looks like this. You have an external-facing web server or reverse proxy. It accepts incoming connections from outside your network. It presents a landing page that collects or detects identity credentials. Once authenticated, it validates the user's access rights against a directory or IAM system. Then it establishes a session and proxies their requests to the appropriate backend service. The backend services don't know the user came from the outside. They only see validated requests coming from the landing page infrastructure. For authentication, SAML 2.0 is the standard if you're dealing with enterprise identity providers. OIDC works well for modern applications, especially if some of your partner systems are cloud-native. OAuth 2.0 comes into play when you need delegated authorization, like allowing a partner application to make API calls on behalf of a user. In practice, most enterprise deployments I've seen combine all three. SAML for the initial identity handshake. OIDC for session token issuance. OAuth for granular permission delegation.
Here's where it gets less clean. Your organization probably has five different directories. Active Directory, a cloud LDAP instance, maybe two SaaS-based user stores that nobody consolidated. The extranet landing page needs to query all of them, merge the results, and produce a single authoritative user record for each external visitor. We called this the "identity unification problem" in my last project. It consumed about forty percent of our implementation timeline. The workaround was to create a lightweight synchronization layer that pulled from all sources on a fifteen-minute interval and presented a single lookup table to the landing page. It's not elegant. It works. The routing layer is equally important. A partner from Company A should never see Company B's resources. This sounds obvious. It's where things fail. I once audited a deployment where the routing logic was based entirely on URL path matching. A consultant figured out that changing a single path segment let him access a procurement dashboard he shouldn't have had. The fix was to move to claim-based routing. The landing page checks the authenticated user's roles and attributes, then determines the route. URL paths become irrelevant to authorization decisions. This alone would have prevented the breach.
Get the Full Details

Building the actual implementation
If you're building this from scratch, the foundational piece is your reverse proxy configuration. NGINX, HAProxy, or Traefik all work. I prefer Traefik for newer deployments because its dynamic configuration means you can add new backend services without restarting the proxy. Each backend gets defined as a separate entry point with its own TLS certificate and access policy. The landing page lives on the outermost layer and acts as a dispatcher rather than serving content itself. Session management needs its own careful thought. External users shouldn't share sessions with internal users. This isn't just a policy preference. It's a practical boundary. When sessions are shared, cookie injection attacks become trivially easy. Keep extranet sessions in a separate cookie domain with strict SameSite attributes. Set reasonable timeouts. Ninety minutes of inactivity is standard. Anything longer and you're asking for session hijacking. Anything shorter and your users will complain, which they will regardless. The landing page itself should be minimal. A login form or a button that triggers SSO redirect. No marketing content. No product descriptions. Nothing that gives an external user information about your internal systems. I've seen landing pages with helpful links like "Forgot your password? Contact IT support at ext-support." That's a free reconnaissance gift to anyone probing your network. Just give them a login mechanism and a privacy notice. That's it.
Logging and monitoring are where most teams cut corners and then pay for it. You need detailed audit logs for every access attempt, successful or not. Log the source IP, the authentication method used, the user identity resolved, the target service, and the authorization outcome. Forward these logs to your SIEM. Set up alerts for patterns like multiple failed authentications from a single IP, access attempts outside business hours for partner accounts, or any request to an admin-level resource from an external identity. The alert for after-hours access alone has caught three unauthorized access attempts at my last two workplaces. Performance is another area people underestimate. An extranet landing page introduces latency that internal users never experience. Every request from outside your network goes through identity verification, possibly a redirect to an external IdP, session establishment, and then routing to the backend. That's three to five round trips before the user sees anything. Under normal load this adds about 200 to 400 milliseconds per request. Under load, when your IdP is slow or your session cache is warm, it can spike to several seconds. Implement response caching at the proxy layer for non-authenticated requests. Use a distributed session store instead of in-memory sessions. Keep backend connection pools sized appropriately. These aren't optional optimizations. There's a specific edge case I ran into that I think deserves attention. We had a partner organization that used a residential ISP with CGNAT. Hundreds of their employees shared a single public IP address. Our WAF was flagging this as a DDoS pattern and blocking them entirely. The standard rate-limiting rules couldn't distinguish between a coordinated attack and a legitimate office behind carrier-grade NAT. We solved it by implementing a per-cookie-session rate limit instead of per-IP rate limit. Each user gets their own quota based on their authenticated session, not their shared IP. It's a small change in the proxy configuration but it resolved the issue completely. Don't skip this consideration if your partners are mid-sized companies.
What these systems don't do well
I want to be explicit about the limitations because the vendors selling this space rarely mention them. An extranet landing page does not protect your internal systems from compromised partner credentials. If a supplier's account is hijacked, the landing page has no way to distinguish that from a legitimate login. It trusts the identity provider. This means your IAM hygiene has to be excellent across all connected organizations. You need mandatory MFA for all external accounts. You need periodic access reviews. You need automated deprovisioning when partners leave their organizations. The landing page is only as secure as the credentials flowing through it. Another limitation is the single point of failure problem. Everything external traffic hits your landing page. If it goes down, every partner relationship goes down with it. There's no bypass. This is why high availability isn't optional. You need at least two nodes in different availability zones, ideally behind a global load balancer with health checks. We had a deployment where a misconfigured auto-scaling policy took down both nodes simultaneously during a traffic spike. Six hours of lost partner connectivity. The incident report was four pages long and none of it was anyone's fault individually. It was a systemic design gap. Compliance overhead is significant and often underestimated. If you're handling any regulated data through an extranet landing page, that data falls under your compliance scope. HIPAA, PCI-DSS, SOC 2, GDPR. Whatever applies to your industry. The landing page itself becomes a controlled system that needs documentation, penetration testing, and audit trails. We budgeted three months of compliance work for a project that we initially estimated at six weeks of engineering time. The engineering was straightforward. The documentation and audit requirements were the heavy lift. Factor this in or your project will slip.
There's also the integration burden. Every internal system that wants external access needs to be adapted. Some can use existing SAML integration. Some need API key provisioning. Some need custom header injection so the backend knows the request came through the extranet gateway. Each integration is a separate project with its own testing and deployment cycle. A typical enterprise might have fifteen to thirty systems needing external access over a two-year period. That's fifteen to thirty integration projects, not one. The landing page enables them all, but it doesn't eliminate the work. If your organization has fewer than five external partner systems and minimal compliance requirements, a full extranet landing page implementation is probably overkill. A well-configured VPN with role-based access controls and a simple web portal might serve you better. The landing page approach pays off at scale. Below that threshold, you're building infrastructure for problems you don't have yet. I've seen three teams in the past two years do exactly this. They built full extranet platforms for eight partner relationships. All of them regretted the complexity. A simpler approach would have been sufficient and would have saved an estimated three to six months of development time.
The practical checklist
When you're actually ready to build this, here's what I'd prioritize. Define your identity sources first. Know exactly where your external users come from and how they authenticate before you touch a single line of proxy configuration. Map out the authorization model next. What roles exist? What resources does each role access? Document this before implementation because you'll revise it three times during testing anyway. Then build the proxy layer. Start with a single backend service and expand from there. Add logging and monitoring in parallel with the proxy configuration, not after. You don't want to deploy a system you can't observe. Test with real partner credentials, not synthetic test accounts. Synthetic accounts don't exercise the same code paths as real ones. Finally, plan your incident response. Write down exactly who gets called when the landing page goes down and what the rollback procedure is. We wrote ours on a whiteboard. It worked well enough for the first outage. After the second, we formalized it into a runbook. The technology keeps evolving. Zero Trust architectures are pushing more organizations toward this pattern. Cloud-native service meshes are absorbing some of what extranet landing pages traditionally handled. But the core problem remains the same. External users need controlled, secure access to internal systems. Landing pages are a practical solution to that problem. They're not glamorous. They don't transform anything by themselves. But they work when designed carefully and maintained consistently. That's about as honest as it gets.