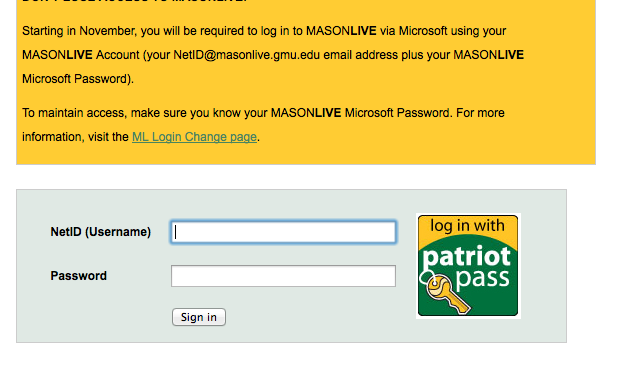
Getting Locked Out of Mason Email: What Actually Happens
You type your credentials. They get rejected. The page spins. A generic error message appears that tells you nothing useful. This happens more often than people admit, and the usual fixes listed on support pages don't always work because they're written for people who understand how the underlying systems connect. They don't. Mason email runs on a Microsoft 365 tenant with some custom configurations layered on top. That means you're dealing with Azure AD authentication, Exchange Online mailboxes, and sometimes on-premises Active Directory sync depending on your account type. When any piece of that chain breaks, the symptom is always the same: you can't log in. The cause could be anything from a stale password hash to a blocked IP range to a conditional access policy change you didn't know about.
Unlock Mason Email Login The Ultimate Guide To Secure Access Troubleshooting
Here's the practical sequence. Start at the bottom and move up. Most people skip ahead and waste time on solutions that don't apply. Step one: verify which account you're actually trying to use. Mason has different domains and account types. Student accounts, faculty accounts, staff accounts, and external collaborator accounts all live in slightly different parts of the identity infrastructure. If you're a student who graduated three years ago and is now trying to access an old mailbox, the unlock path is completely different from a current student who mistyped their password. Check your username format. It should match what's in your official Mason directory listing, not what you remember from four years ago. Step two: try the password reset flow through the official portal. Go to the Mason IT help site and initiate a reset. Do not use third-party tools or workarounds. When I was dealing with a locked faculty account last fall, I tried a cached credential approach that involved clearing browser data and using incognito mode. It didn't work because the lockout was tied to the Azure AD identity, not the browser session. The reset portal fixed it in about three minutes. I still hear people insisting on the incognito method like it's some kind of insider trick. It isn't.
Step three: check for conditional access blocks. This is where it gets messy. Mason has implemented conditional access policies that can block login based on location, device compliance, or risk level. If you're traveling or connecting from a new network, your account might be flagged as risky even if your credentials are correct. The workaround here is to register your device through the MySignIns portal at https://mysignins.microsoft.com. Review your recent sign-in activity there. If you see a blocked attempt, you can often approve it or mark it as safe from your phone or another trusted device. I had a colleague who couldn't log in for two days because her laptop hadn't been marked as compliant after a Windows update. She was resetting her password repeatedly, which changed nothing. The real issue was device compliance status. Step four: clear authentication caches. On Windows, this means clearing the Credential Manager entries for Office, Microsoft, and any Mason-related services. On Mac, it means removing entries from Keychain Access. On mobile devices, it means removing and re-adding the Outlook or Office 365 app. Stale tokens persist longer than most people expect. A token from six months ago can sit in your credential cache and cause the authentication server to reject your current valid password because it's trying to validate against an old session state. I've seen this cause lockouts that lasted weeks because nobody thought to look at the cached credentials. They kept resetting passwords that were already correct. Step five: contact IT support with specific information. If none of the above works, you need to escalate. But do not call and say "I can't log in." That gets you a generic troubleshooting script. Provide your username, the exact error message, when the problem started, what you've already tried, and whether you're on campus or remote. This saves everyone time. The support team can look up your account in the admin console and see exactly which component is failing. Without that detail, they're guessing.
Get the Full Details
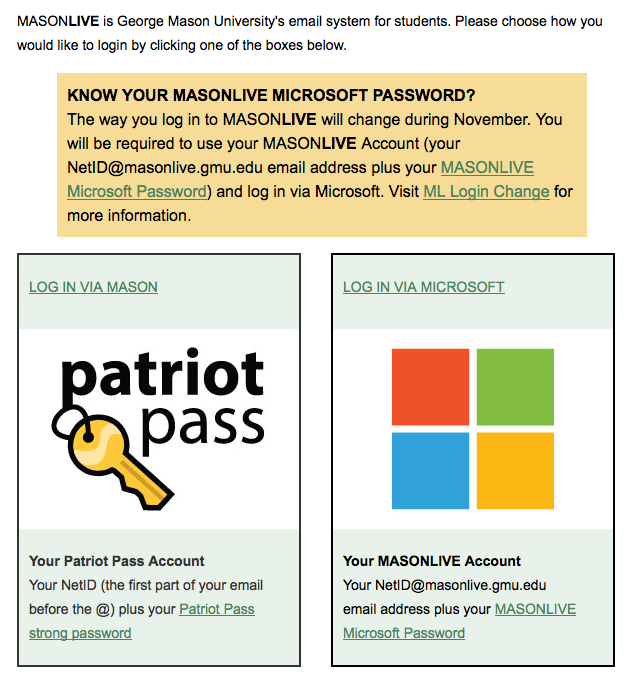
There are edge cases that don't fit neatly into any of these steps. One that comes to mind: an account that appears unlocked but still refuses credentials because of a synchronized attribute mismatch between on-premises AD and Azure AD. This happens when someone's account was migrated or recreated and the proxy addresses or UPN doesn't match what's expected. The fix requires a manual sync or a support ticket to the identity team. There is no self-service path for this. I ran into it with a departmental account that had been decommissioned and then recreated under the same name but with a slightly different primary SMTP address. Password resets did nothing. Device compliance checks passed. It took a ticket to the directory synchronization team to resolve it, and they had to update the cloud attributes to match the on-premises object. That took about forty minutes once the ticket was filed, but getting to that point required ruling out everything else first. Another thing worth noting: Mason's email system sometimes has maintenance windows or temporary outages that aren't widely advertised. If everyone in your department is having the same problem at the same time, it might not be your account. Check the IT status page before spending an hour on credential resets. The overall process usually takes between fifteen minutes and an hour depending on which layer the problem sits in. If it's taking longer than that, you're likely deeper in the infrastructure than a standard user troubleshooting path can reach, and it's time to move to formal support with the details you've gathered along the way.

