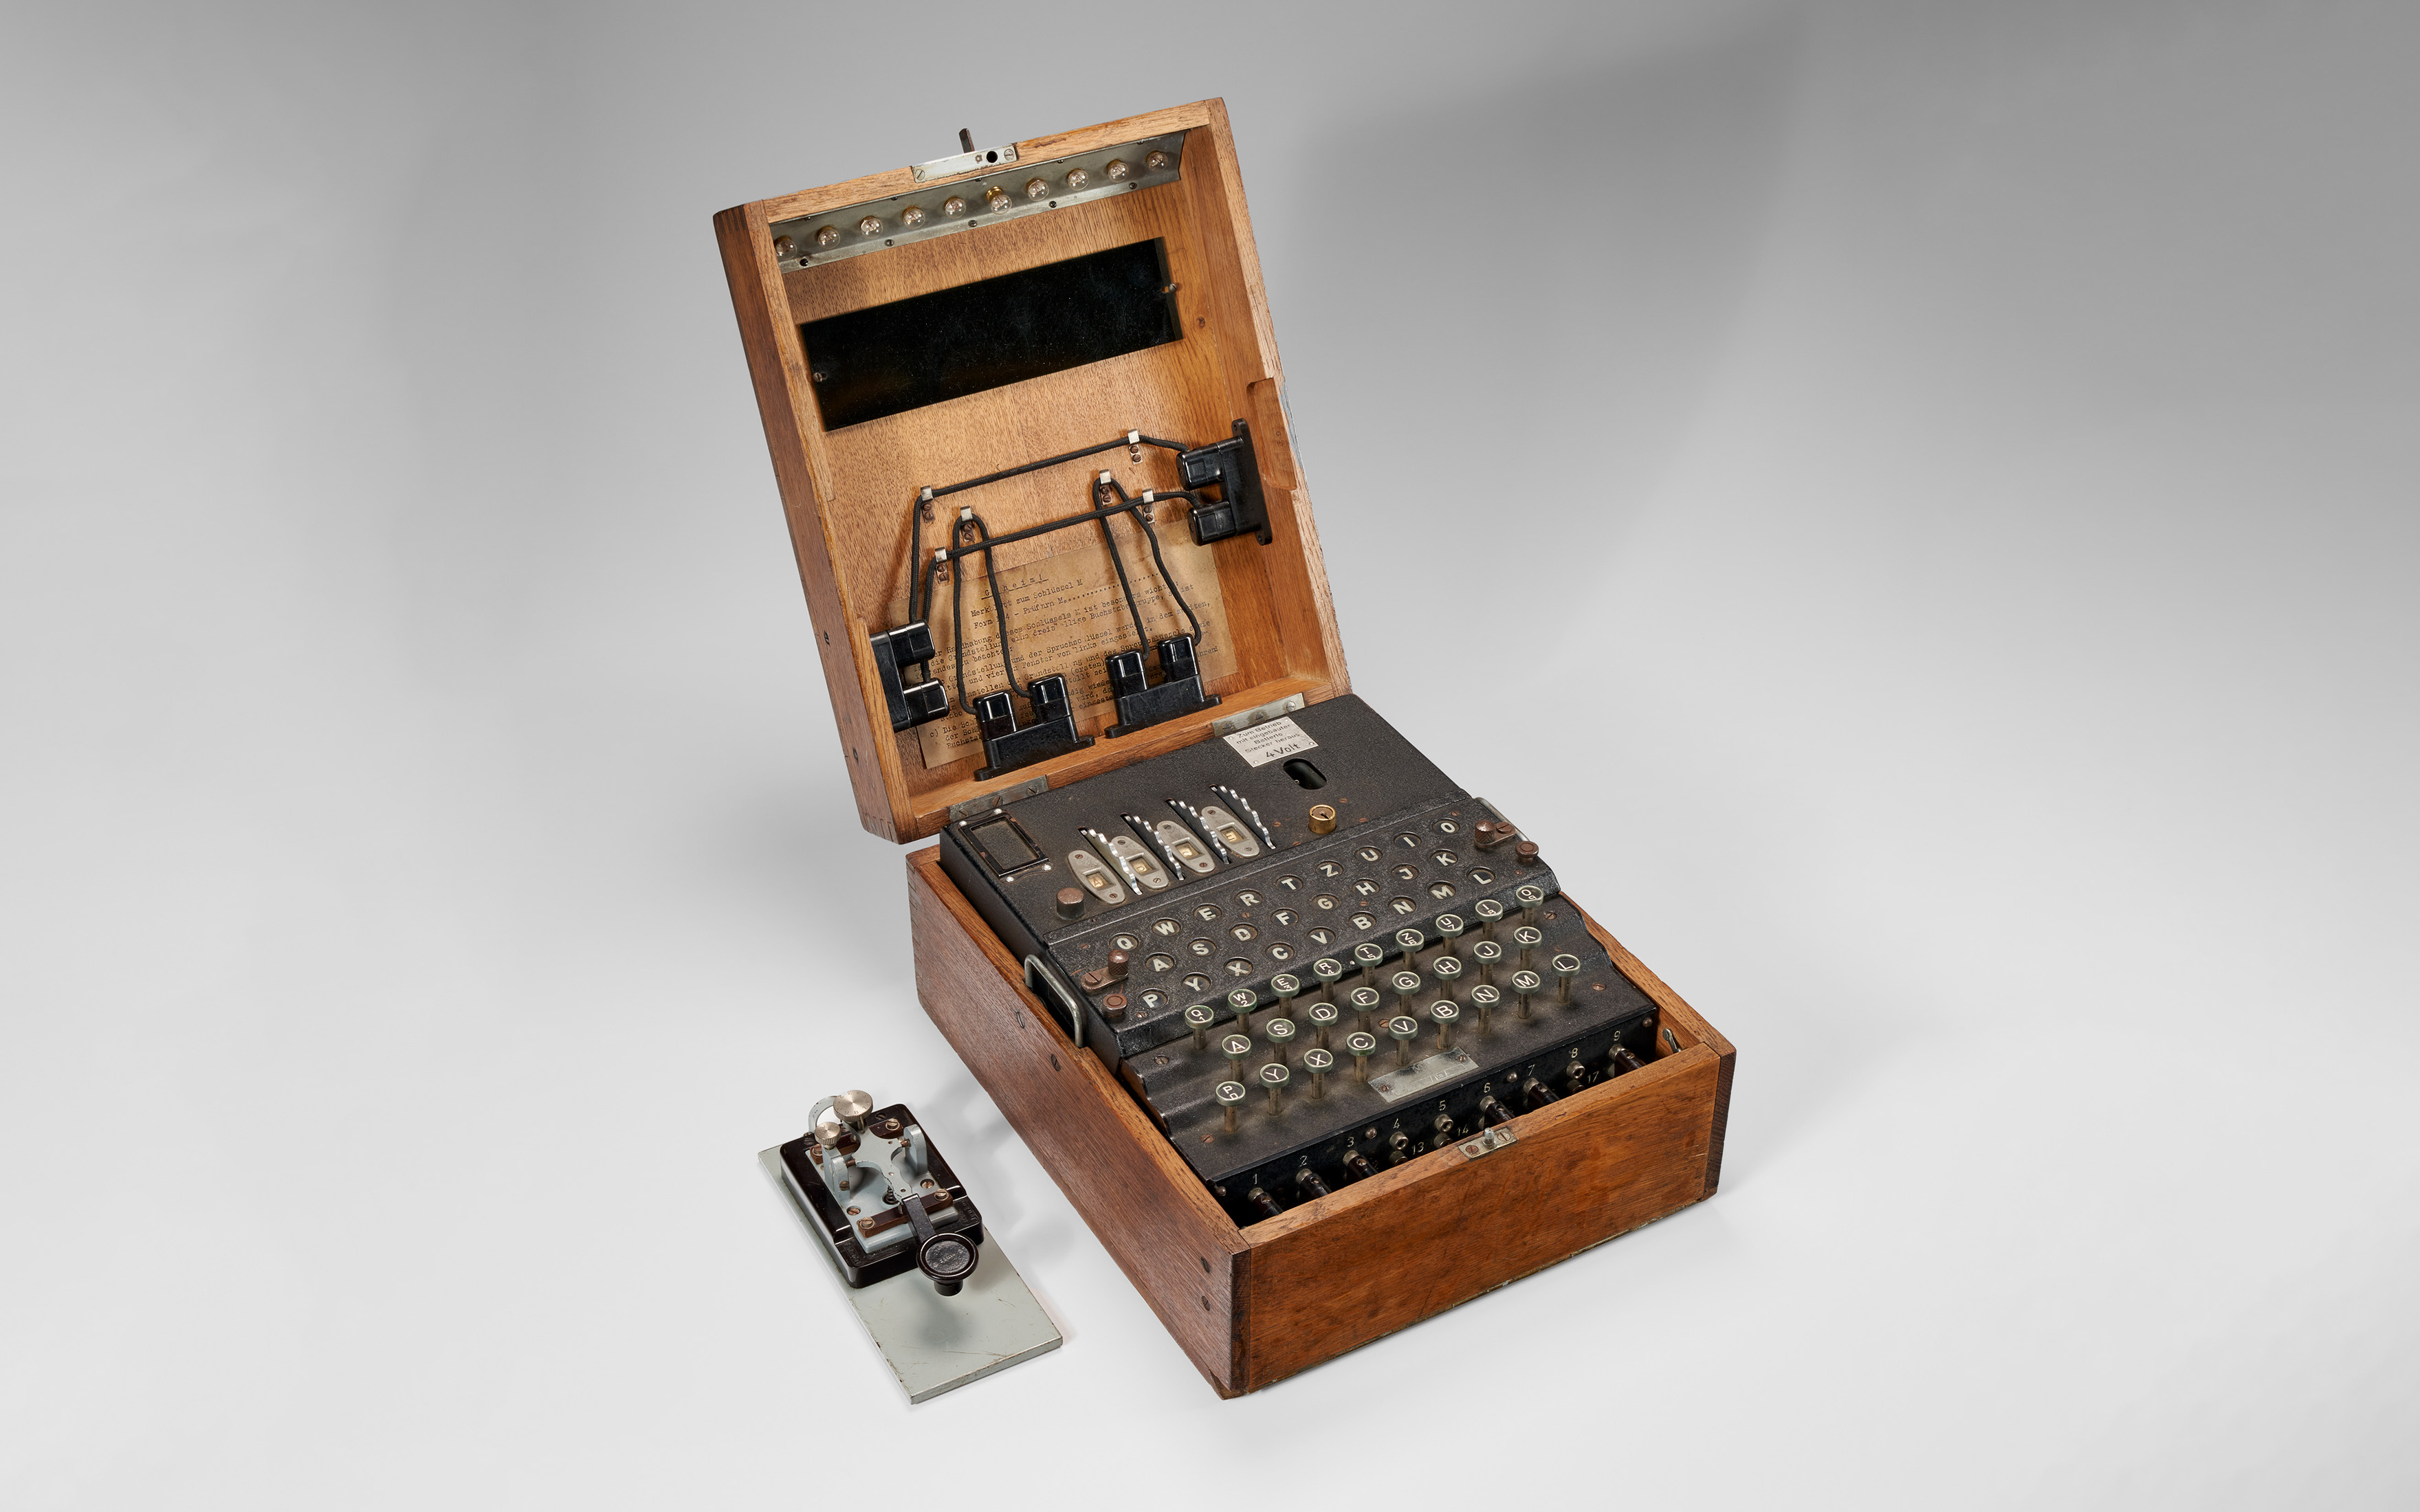
How the Enigma Machine Informed the Way We Think About Encryption Today
The Enigma machine was an electro-mechanical cipher device used primarily by Germany during World War II. It used a series of rotating wheels, called rotors, to substitute letters in a message. Each press of a key sent the electrical signal through the rotors at a different arrangement, producing a completely different output letter. That basic idea—taking plaintext and running it through a mathematical transformation that scrambles it into unreadable ciphertext—is still the foundation of every encryption system in use today. I spent years working on cryptanalysis and then moved into information security. One thing that comes up constantly in my field is people confusing the Enigma with modern encryption as if they are the same category of problem. They are not. The Enigma was a deterministic mechanical process with a small, discoverable keyspace. Modern encryption uses keys that are so large brute-forcing them is functionally impossible with any hardware we currently possess. Understanding where the Enigma succeeded and where it failed helps explain why we build systems the way we do now.
Unlock Enm How Enigma Machine Decryption Shaped Modern Cybersecurity
The term Unlock Enm How Enigma Machine Decryption Shaped Modern Cybersecurity sounds like a search query someone pasted together, but the core question behind it is legitimate. How did cracking the Enigma change the field? The answer lies in the methods developed at Bletchley Park and what those methods still look like in practice. Alan Turing and his team did not crack the Enigma by guessing. They built a machine called the Bombe, which exploited the fact that the Germans made predictable errors in their procedures. The daily key settings were chosen from a limited menu. Operators sometimes repeated the indicator twice at the start of a message. These mistakes created a statistical pattern that the Bombe could test against. It was one of the first times a systematic, automated approach was used for what we would now call cryptanalytic analysis. I remember a project I worked on a few years back involving encrypted USB drives using an older implementation of the AES algorithm. We ran into a problem where certain devices would fail to decrypt large files after a firmware update, and the error messages were useless. The issue turned out to be a bug in how the device handled padding in certain block sizes. I wrote a small Python script that tested different padding schemes and buffer sizes until I found one that worked consistently across the affected models. It took about forty-five minutes to isolate and fix. That experience reminded me of the same iterative debugging approach the Enigma teams used, except instead of electrical relays, we had hex dumps and packet captures.
The Enigma had several design flaws that made it vulnerable. The most critical one was the reflector. A reflector sent the electrical signal back through the rotors, which meant that no letter could ever encrypt to itself. If the letter A was pressed, the output could never be A. That seems like a minor quirk, but it is a massive weakness. Cryptanalysts used this fact to eliminate entire categories of possible settings. Modern ciphers do not have this problem because they are not built on reflector designs. Another weakness was the rotor wiring and stepping mechanism. The rotors advanced in a predictable pattern, and the initial settings were chosen from a relatively small range. Someone with enough computational power could test every possible combination. That is what the Bombe did on a physical scale. Today, a modern supercomputer could test the Enigma keyspace in a fraction of a second. The lesson here is that keyspace size matters enormously. The Enigma's effective keyspace was roughly 10^114, which sounds large, but the procedural flaws reduced it to something far smaller in practice. Modern encryption uses keys that are measured in bits. A 256-bit key has 2^256 possible values, which is approximately 1.16 x 10^77. That is exponentially larger than anything the Enigma offered. Testing every possible value for a modern key is not feasible with any known technology. You would need more atoms than exist in the observable universe to build a machine capable of that task.
Get the Full Details
The shift from mechanical to electronic encryption happened gradually. The Colossus computer, built during the war to crack the German Lorenz cipher, was a different beast from the Enigma effort. It was one of the first programmable electronic computers. The transition from physical machines to software-based algorithms changed everything about how encryption was deployed. Now you do not need a room full of wiring and relays. You need a CPU and an algorithm. One counter-intuitive point that many beginners miss is that the hardest part of modern encryption is often not the math. It is the implementation. Algorithms like AES and RSA are well understood and have stood up to decades of analysis. The failures usually happen at the edges. A developer accidentally hardcodes a key. A server misconfigures its TLS settings and exposes itself to downgrade attacks. An application stores encryption keys in plaintext on disk alongside the data it protects. I have seen all of these in real environments, and they are far more common than broken algorithms. Another thing people get wrong is thinking that encryption alone solves security. It does not. Encryption protects data at rest and data in transit. It does not prevent someone from stealing your hardware, forcing you to decrypt a drive, or phishing your credentials. I once audited a company that had invested heavily in full-disk encryption but stored their encryption keys in a shared network folder accessible to anyone with a basic user account. The encryption was theoretically strong. In practice, it was meaningless because the key was sitting in the open.
The Enigma teams also pioneered what we now call known-plaintext attacks. If you know part of the plaintext and you see the corresponding ciphertext, you can work backward to narrow down the key space. This concept is still used today. Modern cryptanalysts use similar techniques when testing new protocols. The difference is the scale and the tools. What took weeks with paper and pencils now takes minutes with specialized software. There is a practical takeaway for anyone working in cybersecurity. Study the history of these systems. Understanding why the Enigma failed teaches you about the importance of rigorous key management, the danger of predictable patterns, and the necessity of independent verification. None of these lessons are unique to the 1940s. They apply directly to the systems you are building or auditing today. If you want to experiment with basic encryption concepts, there are open-source implementations of the Enigma available online. Running one yourself helps you understand the mechanics without any of the legal or ethical complications of dealing with actual classified systems. I used a simple Enigma simulator for a training exercise a while back. The goal was to demonstrate to a group of junior analysts why procedural discipline matters as much as mathematical strength. Half the group guessed at the key settings within minutes. The others followed the proper analysis steps and found the pattern in under an hour. The exercise was effective because it made the theory concrete.
The legacy of the Enigma is not just that it was cracked. It is that the cracking process created an entirely new discipline. Codebreaking became computer science. The people who worked on it laid the groundwork for everything from modern software engineering to artificial intelligence. Without that work, we would not have the tools or the frameworks we rely on today.