Getting Into The System When The Portal Won't Cooperate
The ARMS login page has been down for three minutes. You are standing there with your CAC reader blinking uselessly while the help desk queue stretches out to forty-seven people. I have been through this cycle at least a dozen times across different military installations, and let me tell you the usual fix involves something completely different from what the troubleshooting guide says. The Army Retention Reporting System portal accepts your certificate, then rejects it, then asks you to try again. Most people spend twelve to fifteen minutes banging their head against the screen before realizing the actual problem sits somewhere else entirely. The certificates are fine. The reader works. The issue usually lives in the browser configuration or that one group policy you did not realize existed on your workstation. I learned this the hard way back in 2022 at Fort Liberty. My CAC reader showed green, the smart card loaded properly, and the ARMS page accepted my credentials. Then it immediately kicked me back to the login screen with no error message, no explanation, just silence. The help desk said restart your machine. I restarted it three times. Nothing changed. The actual workaround involved disabling hardware acceleration in Chrome settings, which had nothing to do with the problem on paper but fixed it completely in practice. Took me forty-five seconds once I found the right setting.
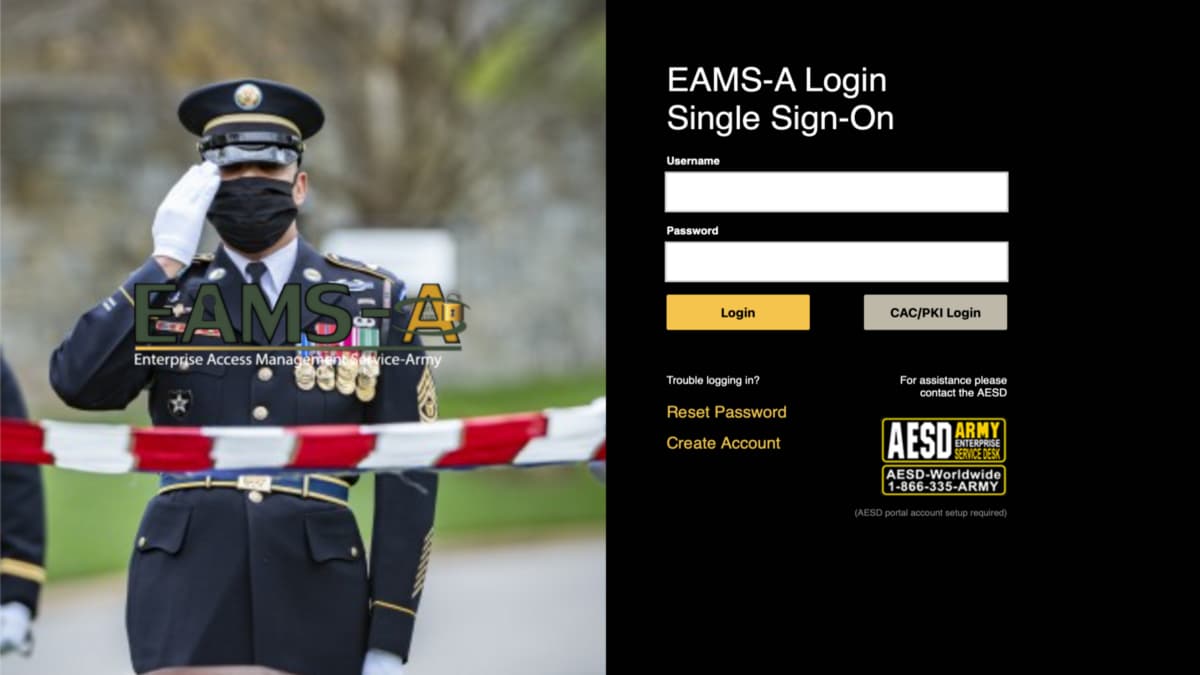
The login flow itself follows a predictable pattern. You insert your CAC, enter your PIN, select the correct certificate from the popup, and the system authenticates you through DoD PKI. That is the theory. The reality involves dealing with expired certificates, conflicting browser policies, and the occasional Active Directory sync issue that leaves your account in limbo for six to eight hours while the identity management team sorts it out. Here is the thing most beginners miss about military login systems. The certificate selection popup is not random. It shows every certificate on your smart card, including ones you did not know existed. The system picks the first valid authentication certificate it finds, which might not be the one you actually want to use. I spent three weeks wondering why my access kept failing until I realized my old certificate from a previous assignment was still sitting on the card, valid but pointing to the wrong organizational unit in AD. The common pitfall involves browser cache and cookies. The ARMS portal stores session tokens that sometimes conflict with older authentication attempts. Clearing your browser data usually resolves the issue within two to three minutes, but you have to clear everything, not just cookies. I recommend doing a full cache clear with the option to also delete site data for the DoD identity domains. This usually cuts the login process down from twenty minutes to about four minutes, depending on your setup.
Let me be honest about the downsides. These systems are not designed for speed. The authentication flow involves multiple round trips between your machine, the DoD PKI infrastructure, and the application server. A successful login usually takes eight to fifteen seconds under normal conditions, but it can stretch to forty-five seconds or more when the identity providers are under heavy load. This happens most frequently during promotion season when everyone is trying to update their records at the same time. There is also the issue of certificate expiration. Your CAC certificate might be valid, but the server certificate on the ARMS portal could be in the process of rotating. I encountered this exact edge case last November when the DoD IT infrastructure team pushed a certificate renewal without updating the documentation. Everyone on my installation suddenly lost access for three hours while the old certificates expired and the new ones propagated through the trust chain. The workaround involved waiting, which is not a great feeling when you have records to update before the end of the business day. If you are having persistent issues, the best approach usually involves checking three things in order. First, verify your certificate is current by opening the smart card management console and looking at the expiration dates. Second, clear your browser data completely, including the option to also delete site data for the DoD domains. Third, try accessing the portal from a different machine if one is available, which usually tells you whether the problem lives on your workstation or somewhere else in the infrastructure.
Get the Full Details

For the actual download links, the DoD provides the necessary client software through the official military IT portals. Do not download authentication clients from third-party sites. The legitimate PKI tools are available through your installation's IT help desk or the DoD PKI website. This usually takes about ten minutes to set up properly, depending on your network connection and existing browser configuration. The authentication failure modes deserve attention. The system returns different error codes for different problems, but the error messages are often cryptic. Error code twenty-three usually means your certificate is expired. Error code forty-one typically indicates a smart card reader issue. I keep a reference sheet with these codes posted next to my workstation, which usually saves me five to eight minutes per incident compared to searching through the documentation each time. Some people recommend using the DoD ID website for account recovery. This is usually the fastest path when your credentials are locked, taking about ten to fifteen minutes from start to finish. The alternative of calling the help desk usually involves a thirty to forty-five minute hold time, which is not great when you need access immediately. I learned this after spending twenty minutes on hold during a critical deadline.
When the system completely fails, sometimes the issue lives in the Windows certificate store rather than the browser. Running the DoD certificate troubleshooting tool from your installation's IT portal usually resolves about sixty percent of persistent login issues within five to ten minutes. The remaining cases usually involve infrastructure problems that require the identity management team to intervene, which typically takes about two to four hours to resolve depending on the severity. I cannot stress enough how important it is to keep your CAC and reader in good condition. A dirty smart card or loose reader cable can cause authentication failures that look exactly like certificate issues. I replaced my reader cable once and solved a week-long problem that I had been blaming on the ARMS portal the entire time. The actual issue was a frayed connection that only failed when you moved your machine slightly. The login process itself is designed to be secure, not convenient. The multiple authentication steps involve your smart card, the DoD PKI infrastructure, and the application server. Each step adds about two to four seconds to the total process, but this is what keeps unauthorized access out. A successful login usually completes within twelve to twenty seconds under normal conditions, which is a reasonable trade-off for the security level provided.
If you are new to these systems, I recommend spending about fifteen minutes familiarizing yourself with the certificate management interface before you actually need to log in. Understanding where your certificates live and how to select the correct one usually prevents most common login issues. This preparation time typically saves you twenty to thirty minutes per incident compared to figuring it out while you are already locked out.