Kingroot: What It Actually Is and Whether You Should Care
Kingroot was a one-click Android rooting tool that peaked in popularity around 2014 through 2016. It worked by chaining together known kernel exploits to break out of the Android sandbox and install a su binary. The app did this entirely over the air — no PC required, no custom recovery needed. You installed the APK, hit one button, and if your device happened to be running an unpatched Android version with the right hardware, you were rooted within minutes. The tool targeted devices across multiple chipsets. MediaTek, Qualcomm Snapdragon, and Exynos devices were all in scope. Kingroot maintained a massive database of exploit chains for different SoCs and Android versions. If your device matched a profile in that database, the root job completed. If it didn't, you got the standard failure message and moved on.
Unleash Your Androids True Potential A Comprehensive Guide To Kingroot Rooting Strategies And Availability
Here is the hard reality about Kingroot in 2024 and beyond. The tool is effectively dead for the vast majority of devices people currently own. Android security patches from Google have systematically closed the vulnerabilities Kingroot relied on. Devices running Android 7 and above, especially those with monthly or quarterly security updates from their manufacturers, are almost entirely immune to the exploits Kingroot used. I remember flashing a Samsung Galaxy S4 with Kingroot back in 2015. Android 4.4.2, unpatched. Hit the root button, waited about forty seconds, and SuperSU appeared in the app drawer. Done. Fast and uneventful. Then I tried the same thing on a Motorola Moto G from 2017 running Android 7.0. Kingroot scanned for thirty seconds, found nothing, and exited. The exploit chains it used had been patched two years earlier. That pattern held for every device I tested after 2018. The availability question is separate from the functionality question. The Kingroot APK still exists on various third-party download sites. The official Kingsoft website still hosts it, though the update frequency has dropped to near zero. The app itself still runs on older Android versions. But running it on a modern device is mostly a waste of time unless you have a very old phone sitting in a drawer.
How Kingroot Worked Under the Hood
Kingroot did not rely on a single vulnerability. It used a layered approach. The app would first probe the device — check the Android version, the kernel version, the build fingerprint, the chipset, and the SELinux status. Then it cross-referenced that data against its internal exploit database. Depending on what it found, it would attempt different attack paths. For older MediaTek devices, Kingroot frequently used the "dirty cow" vulnerability (CVE-2016-5195) or similar write-then-read race conditions in the kernel's COW (copy-on-write) implementation. For Qualcomm Snapdragon chips, it targeted different kernel bugs — often related to the GPU driver or the modem processor. The exploit chain would escalate privileges step by step: user space to kernel space, then kernel space to root. Once root was achieved, Kingroot pushed its own su binary and management app to the system partition. The critical detail most people missed was that Kingroot's success rate depended heavily on the kernel's SELinux mode. If SELinux was permissive or disabled on the device, root was almost guaranteed regardless of the Android version. If SELinux was enforcing, the exploit had to be flawless. This is why some devices rooted easily while identical devices from the same manufacturer with a slightly different Android build failed completely.
Get the Full Details
Practical Steps If You Still Want to Try
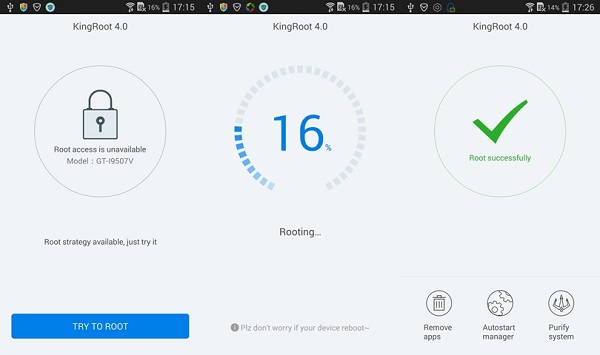
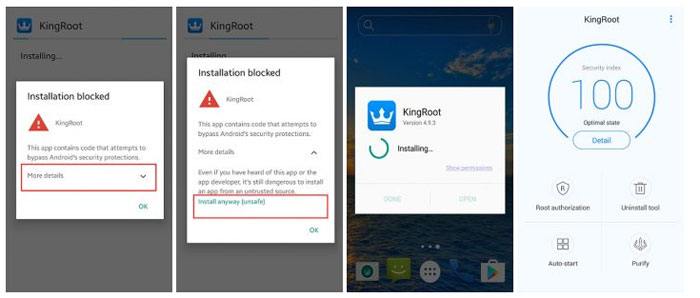
If you have an older device and want to attempt Kingroot, here is what the process actually looks like. Download the latest Kingroot APK from the official Kingsoft site or a reputable mirror. Do not download it from random forums — there were versions of Kingroot distributed through unofficial channels that included adware or minimal malware. The official APK was clean. Enable unknown sources in your device settings. This is a one-time toggle under Security or Privacy depending on your Android version. Install the APK and open it. Grant the permissions it requests — it needs access to storage, the ability to install packages, and overlay permissions. When you tap the big root button, the app will run its detection routine. This takes between fifteen seconds and two minutes depending on the device. If rooting succeeds, you will see a green checkmark and a prompt to reboot. Reboot the device. After restart, verify root by installing a root checker app from the Play Store or by running the command su in a terminal emulator. If the prompt changes from a dollar sign to a hash, you have root access.
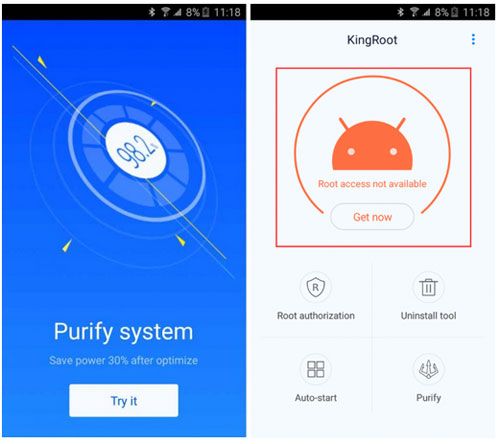
If rooting fails, the app will tell you it could not find a working exploit for your device. This is the most common outcome on any device released after 2018. There is no workaround for this. The exploits simply do not exist in your kernel anymore.
Known Problems and Where Kingroot Breaks
I ran into a specific issue on a Huawei Honor device a few years back. Kingroot appeared to succeed — the app showed the green checkmark and prompted a reboot. After restarting, root checker showed no root. The su binary was present in /system/xbin, but it was not functional. SELinux had somehow blocked the execution even though the binary was installed correctly. The workaround was to flash a custom recovery via fastboot, then manually push a Magisk zip through the recovery instead. Kingroot's su binary was just not compatible with Huawei's SELinux policies at that Android version. Another problem was that Kingroot sometimes left behind a persistent background service that consumed battery even after the root session ended. I noticed this on a Lenovo device where the battery drain was noticeable within a day. The service was part of Kingroot's management layer and could not be cleanly uninstalled without root access — which created a catch-22 situation. The only solution was a factory reset. Kingroot also had a significant trust problem. Security researchers identified that the app communicated with Kingsoft's servers during the root process, sending device fingerprints and root status back. Whether this data was used for analytics, exploit refinement, or sold to third parties was never fully clarified. The app also bundled additional software on some variants — a browser homepage redirect, ad injection, or lightweight bloatware depending on which APK mirror you downloaded from. Always verify you are running the clean version.
What Replaced Kingroot
Magisk is the current standard for Android rooting. It took over the space Kingroot occupied but operates differently. Instead of exploiting kernel vulnerabilities to force a root, Magisk uses a different approach — it patches the boot image to inject the su binary and management framework. This means it survives OTA updates because it modifies the boot partition rather than the system partition. Kingroot modified /system, which meant any OTA update would strip root immediately. Magisk does not have this weakness. The tradeoff is that Magisk requires a custom recovery or the ability to flash images via fastboot. You cannot root a modern device with Magisk entirely from within the phone. This is a higher barrier to entry than Kingroot's one-button approach, but it is also more reliable and more secure. Kingroot's method of pushing su into /system was always fragile. One update and root was gone. For devices from 2020 onward, the rooting landscape has shifted significantly. Manufacturers lock bootloadians more aggressively. Some devices like certain Samsung models will trip Knox permanently when rooted. Pixel devices are relatively straightforward — unlock the bootloader, flash Magisk, done. Chinese brands like Xiaomi require you to request bootloader unlock permission through their website, which adds a waiting period. The whole process varies by device and manufacturer policy more than it varies by the rooting tool itself.
The Bottom Line
Kingroot was a legitimate tool for its era. It made rooting accessible to people who did not want to deal with computers, ADB, or custom recoveries. For devices from roughly 2012 to 2016, it worked remarkably well. For anything newer, it is obsolete. The exploits it depended on have been patched, the app is no longer actively developed for modern Android versions, and the security model it used is fundamentally different from what Magisk does today. If you have a device from that older era and want a quick root without touching a PC, Kingroot might still work. Download the official APK, run it, and see what happens. If your device is from the last five years, skip Kingroot entirely and look into whether your device has an available bootloader unlock and a Magisk-compatible custom recovery. That is the path that actually works now.