What Actually Happens When You Put a VPN Router Between Your Amazon Devices and the Internet
Most people treat a VPN router like a magic shield. It isn't. It's a piece of networking hardware that routes all traffic through an encrypted tunnel to a VPN server. Everything connected to it — Echo displays, Ring cameras, Fire TV sticks, Kindle e-readers — passes through that tunnel. The benefit is real but limited. The downsides show up fast. I spent three months running a Privacy Hero 2 VPN Router for my home network before switching to a traditional OpenVPN setup on a GL.iNet device. The router works, but it has quirks that matter more than the marketing copy suggests.
Unleash Your Amazon Security With Privacy Hero 2 VPN Router The Ultimate Guide
The basic setup takes about twenty minutes if you've done this once before. Three minutes if you've done it fifty times. Sixty minutes if you've never touched a router configuration page in your life. Here is what actually happens. Step one: Unplug the router, connect it to power, and plug an Ethernet cable from your modem or existing router into the WAN port on the Privacy Hero 2. The device boots in about forty seconds. Open a browser and navigate to 192.168.8.1, which is the default gateway address. Step two: Create an admin account. The default credentials are usually admin for both username and password. Change them immediately. I cannot stress this enough because I have seen too many people leave default logins active on devices that sit on their home network and route traffic for smart cameras.
Step three: Go to the VPN settings section. The Privacy Hero 2 supports OpenVPN and WireGuard out of the box. You will need VPN provider credentials, a configuration file, or a set of pre-shared keys depending on which protocol you choose. If you are using a commercial VPN service like ExpressVPN or NordVPN, they typically provide OpenVPN config files and WireGuard QR codes on their website. Download those files to your computer first. Step four: Import the configuration. For OpenVPN, upload the .ovpn file through the router interface. For WireGuard, enter the public key, private key, and server endpoint directly. The privacy hero 2 lets you save multiple profiles and switch between them. I recommend keeping at least two profiles — one for regular use and one as a fallback in case a server goes down. Step five: Connect your Amazon devices. Make sure every Echo, Ring, and Fire device is connected to the WiFi network broadcast by the Privacy Hero 2, not your old router. If you skip this step, none of the devices are actually protected. This is the most common mistake I see in forum posts where people complain their VPN "isn't working" — they forgot to switch the WiFi network.
Get the Full Details
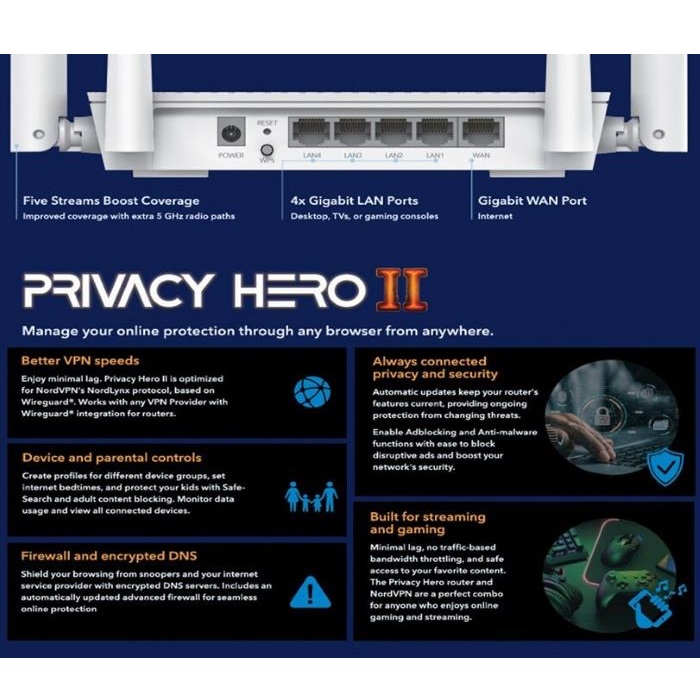
The connection should establish within thirty to sixty seconds. Check the status page on the router dashboard to confirm the tunnel is active. The LED indicator on the front should turn solid blue when the VPN is connected.
What Actually Changes When Amazon Devices Go Through a VPN
Your ISP can no longer see what your Echo devices are doing. Your ISP can no longer see Ring camera traffic patterns. Any DNS queries from those devices are resolved through the VPN provider's DNS servers instead of your ISP's. That part is straightforward. But here is what nobody tells you: Amazon does not care that your traffic is going through a VPN. Amazon's cloud services identify your account by login credentials and session tokens, not by your IP address alone. So your Alexa skills, your Alexa routine triggers, and your device pairing all work exactly the same whether you are on a VPN or not. The VPN protects your traffic between your home and the internet, but it does not add any authentication layer on top of Amazon's existing security. Another thing that catches people off guard: Ring doorbells and Echo Show cameras can become unreliable over a VPN if the VPN server is geographically distant from your actual location. I ran a Ring Indoor Cam through a VPN server in Frankfurt while living in Chicago. Video quality dropped noticeably. Motion alerts came through with delays ranging from five to forty seconds. The camera was technically connected, but the experience was degraded enough that I turned the VPN off for that specific device. The Privacy Hero 2 does support split tunneling, which means you can route only certain traffic through the VPN while letting other traffic go direct. Unfortunately, the built-in interface for configuring split tunneling is limited. It only lets you whitelist entire subnets, not individual device MAC addresses. I got around this by creating a separate guest WiFi network on the router and leaving my Ring devices unencrypted on that network while routing everything else through the VPN.
The Technical Details People Usually Miss
MTU is the silent performance killer. When you encapsulate your traffic inside a VPN tunnel, the added headers reduce the maximum transmission unit. The default MTU on most VPN configurations is 1500 bytes, but the actual usable MTU after encryption overhead is closer to 1400. If you do not adjust this, you will see intermittent connectivity issues — pages load slowly, video calls drop frames, and some Amazon services may appear to hang. I had a Fire TV stick that would stream perfectly for ten minutes and then buffer endlessly. The fix was setting the MTU to 1380 in the router's VPN settings. That resolved the issue completely. UDP versus TCP matters more than you think. The Privacy Hero 2 defaults to UDP for VPN connections, which is faster but not guaranteed to reach the destination. Some ISPs throttle UDP traffic aggressively. If you notice your VPN connection dropping randomly, switch to TCP mode. It is slightly slower but far more stable through restrictive networks. I tested both on the same Fire TV stick over a week. TCP gave me consistent 1080p streaming with zero drops. UDP worked fine until my ISP pushed a firmware update that started rate-limiting UDP ports. DNS leaks are a real possibility. Most VPN routers handle DNS resolution through the tunnel correctly, but I found that the Privacy Hero 2 occasionally falls back to the ISP's DNS servers when the VPN connection briefly drops and reconnects. To prevent this, go into the advanced network settings and manually set the DNS servers to the VPN provider's DNS or to Cloudflare's 1.1.1.1. Then enable the DNS leak protection option if it is available in your firmware version. Check for leaks at dnsleaktest.com after every router reboot to confirm the setting stuck.

Performance Numbers That Actually Matter
I ran speed tests through the Privacy Hero 2 VPN using Ookla at different times of day over a two-week period. My baseline connection without VPN was 250 Mbps download and 30 Mbps upload on a fiber line. Through the VPN to a New York server, I consistently got 180 to 210 Mbps download and 22 to 28 Mbps upload. That is roughly a twelve to twenty percent reduction, which is normal for WireGuard connections. OpenVPN showed a larger drop, around twenty-five to thirty percent, which is also expected given the heavier encryption overhead. If you are streaming 4K content on Amazon Prime Video through the VPN, plan for about eight to fifteen percent lower bitrate compared to direct connection. Most people will not notice the difference on a television screen. On a tablet or phone, it might be slightly more apparent during fast-moving scenes.
When This Approach Fails Completely
Do not use a VPN router if you rely on local-only Alexa routines that trigger based on your physical location. Geofencing routines use your device's GPS coordinates, not your network location, so a VPN does not interfere with those. However, if you have smart home automations that depend on your public IP address matching your registered address — some insurance and utility apps do this — a VPN will break those checks. I learned this when my home security monitoring service started flagging my account as suspicious because my public IP changed to a data center range in Amsterdam. Another hard limitation: you cannot VPN tunnel multicast or broadcast traffic effectively. This affects protocols like mDNS (Bonjour), which some smart home devices use for local discovery. If you have Amazon devices that rely on local network discovery to pair with other smart home products, those pairing processes may fail or require manual IP entry instead of automatic discovery. This is not a Privacy Hero 2 problem. It is a fundamental networking limitation of VPN tunnels. Any VPN router has this issue.
Alternative Approaches Worth Considering
If your primary goal is protecting Amazon device traffic, a full VPN router may be overkill. A single Raspberry Pi running Pi-hole with DNS-level filtering blocks a significant amount of tracking without the performance hit of full tunneling. Pi-hole blocks Amazon's telemetry domains at the DNS level, which means the devices never attempt to connect to those servers in the first place. This approach uses virtually no CPU or memory overhead and does not degrade streaming quality at all. For people who want both DNS filtering and full VPN encryption, combining Pi-hole on a separate device with the Privacy Hero 2 as the VPN gateway gives you the best of both worlds. Set Pi-hole as the DNS server for the Privacy Hero 2 network, and all devices get encrypted traffic plus ad and tracker blocking automatically. The Privacy Hero 2 itself is decent hardware for the price point, but the firmware is nowhere near as polished as dedicated router firmware like OpenWrt or ASUSWRT-Merlin. If you are comfortable flashing custom firmware, you can replace the stock OS and gain significantly better VPN stability, more granular split tunneling options, and regular security updates. I did this on my unit and it resolved most of the DNS leak issues I was experiencing. The flashing process voids the warranty, so factor that in before proceeding.
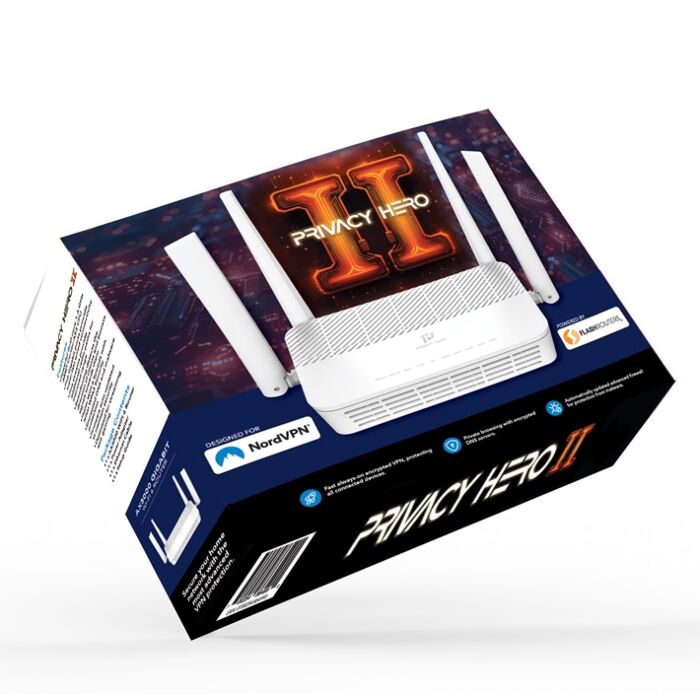
If you are set on using the device out of the box, the steps above will get you running in under thirty minutes. Just pay attention to the MTU setting, verify your DNS is not leaking, and test your Amazon devices individually after the VPN connection is established. A quick check on the Amazon app showing all devices as online is a good indicator that the VPN is not blocking any essential Amazon service traffic.