Cloudflare WireGuard Proxy Setup Guide
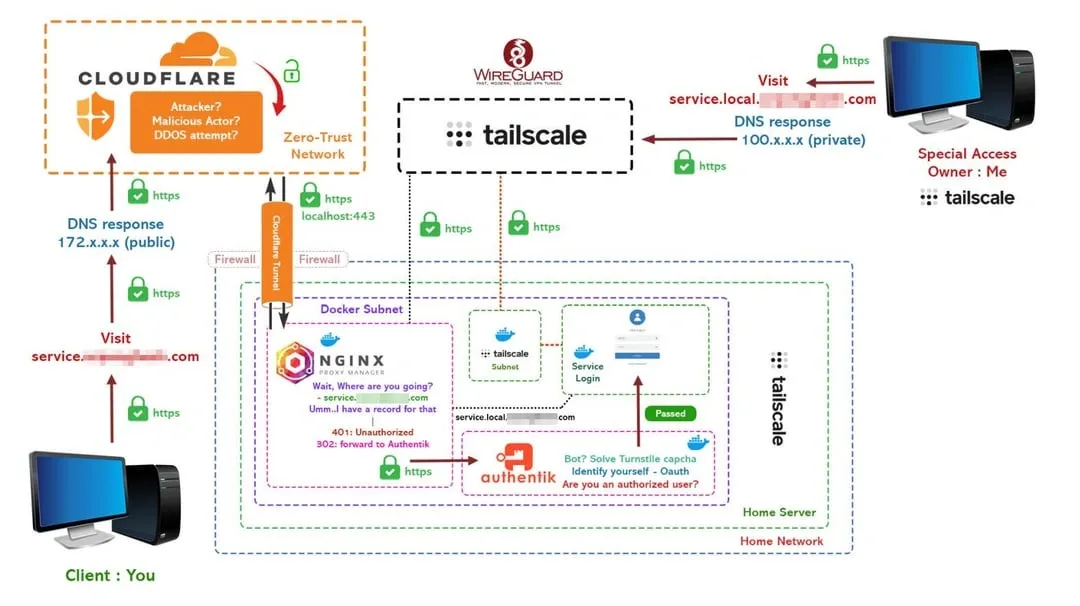
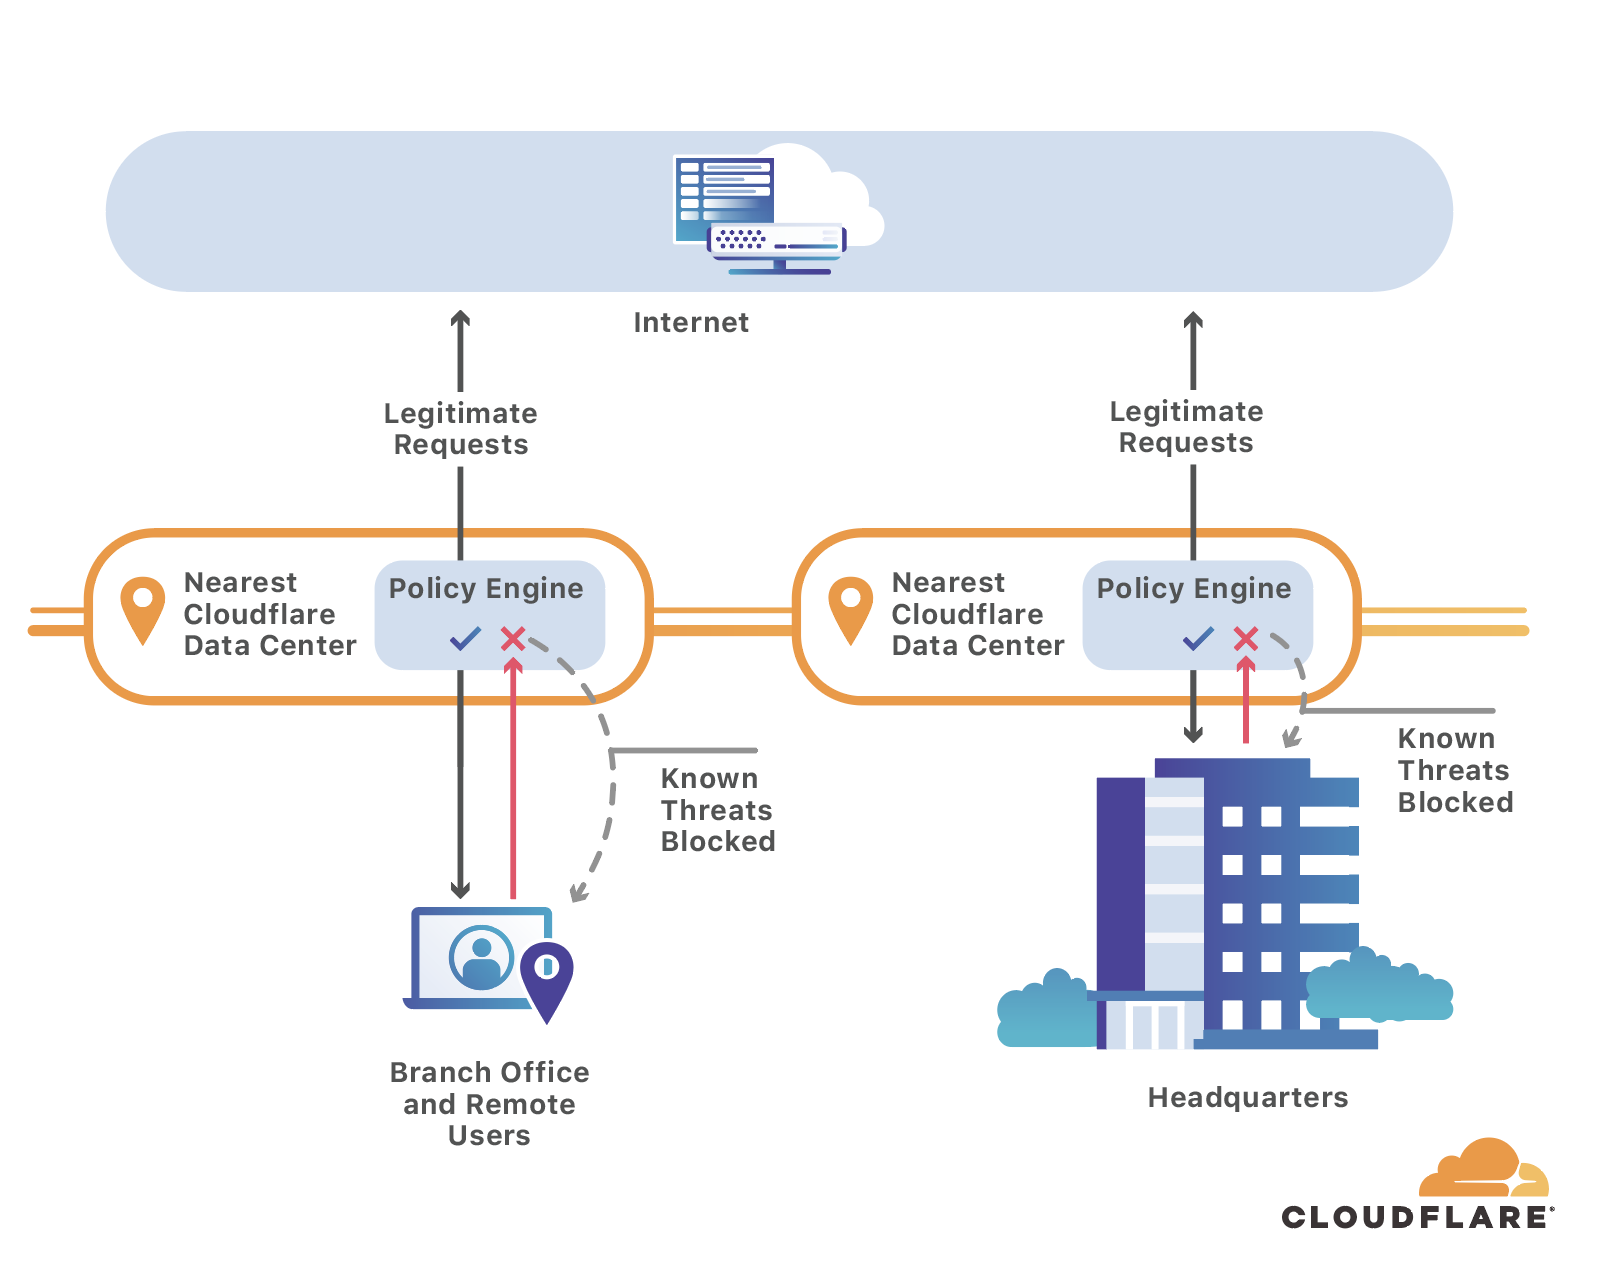
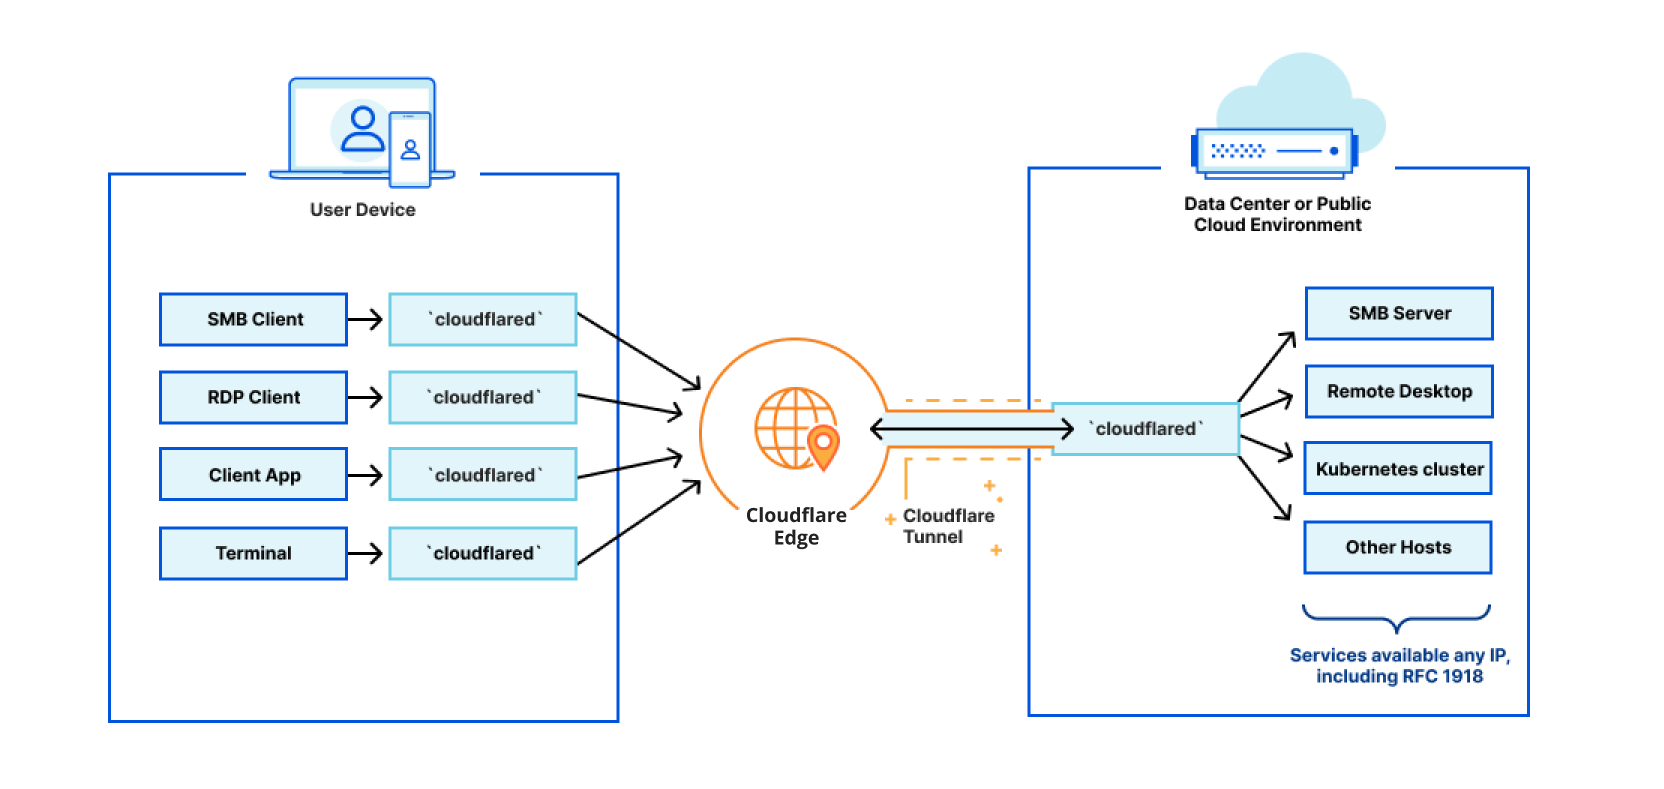
Cloudflare offers a WireGuard-compatible endpoint you can use to route traffic through their network. It is not exactly a traditional VPN in the way most people think, but it functions as a smart proxy layer between your device and the internet. The interface gives you a QR code or a configuration block, and once you import it into your system, your traffic gets tunneled through Cloudflare's edge nodes before egressing toward its final destination. The setup process starts with a Cloudflare account and Zero Trust access. You do not need the paid tier for basic WireGuard functionality, but the free tier comes with a 100-device limit and the bandwidth cap that goes with it. Log into the Zero Trust dashboard, navigate to Networks, then WireGuard, and create a new peer. Cloudflare generates a public and private key pair, spits out a configuration file, and gives you a QR code for mobile devices. That is the easy part. The actual value comes from understanding what you are routing and what you are not. Cloudflare's WireGuard endpoint sits at 162.159.192.1 or similar addresses depending on your region. Your device gets assigned a Cloudflare IP in the 100.x.x.x range. All traffic exits through Cloudflare's network. The important detail that most guides skip: your traffic still passes through Cloudflare's infrastructure. They can see it. They log it. They have policies they enforce. This is not anonymous routing. It is intelligent routing with caching and optimization benefits attached.
The configuration file you download looks something like this in plain text: [Interface]
PrivateKey = your_private_key
Address = 100.x.x.x/32
[Peer]
PublicKey = cloudflare_public_key
Endpoint = 162.159.192.1:51820
AllowedIPs = 0.0.0.0/0
PersistentKeepalive = 25 That AllowedIPs line is where things get interesting. Setting it to 0.0.0.0/0 routes everything through Cloudflare. If you want split tunneling, you can restrict it to specific subnets. I set mine to route only traffic for specific services while leaving local network traffic on the direct path. It makes a noticeable difference in latency for internal resources.
On Linux, you can install WireGuard tools with a standard package manager command and import the config directly. On macOS, the WireGuard app from their website handles imports cleanly. Windows has a native client now, which is a relatively recent development and still has occasional quirks with DNS resolution that I have not fully figured out. Android and iOS both support it through the WireGuard app or the Cloudflare 1.1.1.1 app, which wraps the same tunnel in a more polished interface. Here is a practical issue I ran into that took me about three hours to resolve: after setting up the WireGuard tunnel on a Debian server, DNS lookups started failing intermittently. The tunnel was up, traffic was flowing, but half the domains would hang for several seconds before resolving. The problem was that the system resolver was trying to use the Cloudflare-assigned DNS (which routes through the tunnel) while the tunnel itself depended on DNS resolution to function. Circular dependency. The workaround was straightforward once I found it — set the DNS server in the WireGuard config to a fixed external resolver like 1.1.1.1 directly, and add a systemd-resolved configuration that bypasses the tunnel for DNS queries on the initial connection phase. After that, it has been stable for over a year. One counter-intuitive thing about Cloudflare's implementation: the protocol they use is WireGuard, but the routing intelligence is all Cloudflare-side. Your client does not negotiate mesh paths or multiple endpoints the way a self-hosted WireGuard setup might. You get one endpoint, one peer, and that is it. The optimization happens on Cloudflare's side as traffic traverses their network. This is both a limitation and a feature. You lose fine-grained control over path selection, but you gain automatic optimization across Cloudflare's global Anycast network without managing anything yourself.
Get the Full Details
Another thing people miss: MTU. WireGuard adds overhead to your packets, and if you do not adjust your MTU settings, you will experience fragmentation issues that manifest as slow transfers and broken connections on certain services. Cloudflare's documentation suggests an MTU of 1280 for the tunnel interface, but in practice I found 1400 works better for most use cases without causing fragmentation. You set it with the ip link command on Linux or in the adapter settings on other platforms. Testing with ping -M do -s 1472 gives you a quick way to find your optimal value. Performance characteristics vary significantly depending on your location relative to Cloudflare's PoPs. If you are in a major city with multiple Cloudflare PoPs nearby, the latency impact is usually minimal, often less than 10 milliseconds added to your base connection. In regions with sparse Cloudflare presence, you might see 30 to 50 milliseconds of additional latency. The real benefit shows up in throughput consistency rather than raw speed. Cloudflare's network tends to smooth out congestion that you would normally experience on a peering-poor residential connection. I have seen download speeds more than double on connections that were previously throttled by ISP routing. There are genuine limitations worth being honest about. Cloudflare terminates your traffic at their edge, which means they control the egress point. If you are using this for privacy-sensitive work, understand that Cloudflare logs exist and their retention policies are not trivial. They claim minimal logging for the free tier, but the details are buried in their terms. For high-security environments, a self-hosted WireGuard instance with your own exit node is the only real option. Cloudflare WireGuard is optimized for performance and ease of use, not operational independence.
Another practical constraint: the 100-device limit on the free Zero Trust plan is per organization, not per user. If you are running this across a team or family with multiple people and devices, you will hit the ceiling quickly. The paid plans scale this up, but the pricing jumps noticeably once you move past the free tier. For a single user on a laptop and phone, the free tier is perfectly adequate. For anything more, budget accordingly. The download and setup resources are straightforward. Cloudflare's WireGuard configuration generator is accessible directly from the Zero Trust dashboard under Networks and WireGuard. There is no separate software download required — the configuration file contains everything your WireGuard client needs. The official WireGuard app for each platform handles the import, and that is the entire installation process. Most people have it working within five minutes of creating the peer in the dashboard. I have been running Cloudflare WireGuard tunnels in production for about two years across several different setups. The DNS resolution issue I mentioned earlier is the kind of problem that does not show up in any documentation until you hit it. The MTU tuning is another one of those things that seems minor until your large file transfers start failing silently. Once you sort those out, the setup is genuinely low-maintenance. I have not had to touch mine in months. That is about as good as network infrastructure gets.
Common Pitfalls and Optimization Notes
Firewall configuration on your local machine is an area where people commonly make mistakes. After enabling the WireGuard tunnel, some applications continue routing through the default interface instead of the tunnel. This is especially noticeable with Steam, certain gaming clients, and enterprise software that hardcodes outbound interfaces. The fix is usually adjusting the application's network settings or using policy-based routing on Linux to force specific processes through the wg0 interface. DNS leakage is another frequent issue. Even with AllowedIPs set correctly, your operating system may still resolve DNS through your default gateway rather than through the tunnel. On Linux, configuring systemd-resolved to use the tunnel's DNS server explicitly prevents this. On Windows, the built-in DNS settings in the WireGuard adapter configuration need to be set manually, as the client does not always apply them automatically on first connection. For maximum effectiveness, consider pairing the WireGuard tunnel with a custom hosts file or local DNS caching if you are routing a lot of repeated requests. Cloudflare's network handles caching well on their side, but having a local cache like dnsmasq or the built-in Windows DNS cache reduces lookup overhead and makes the tunnel feel snappier, especially on first visits to frequently accessed domains.
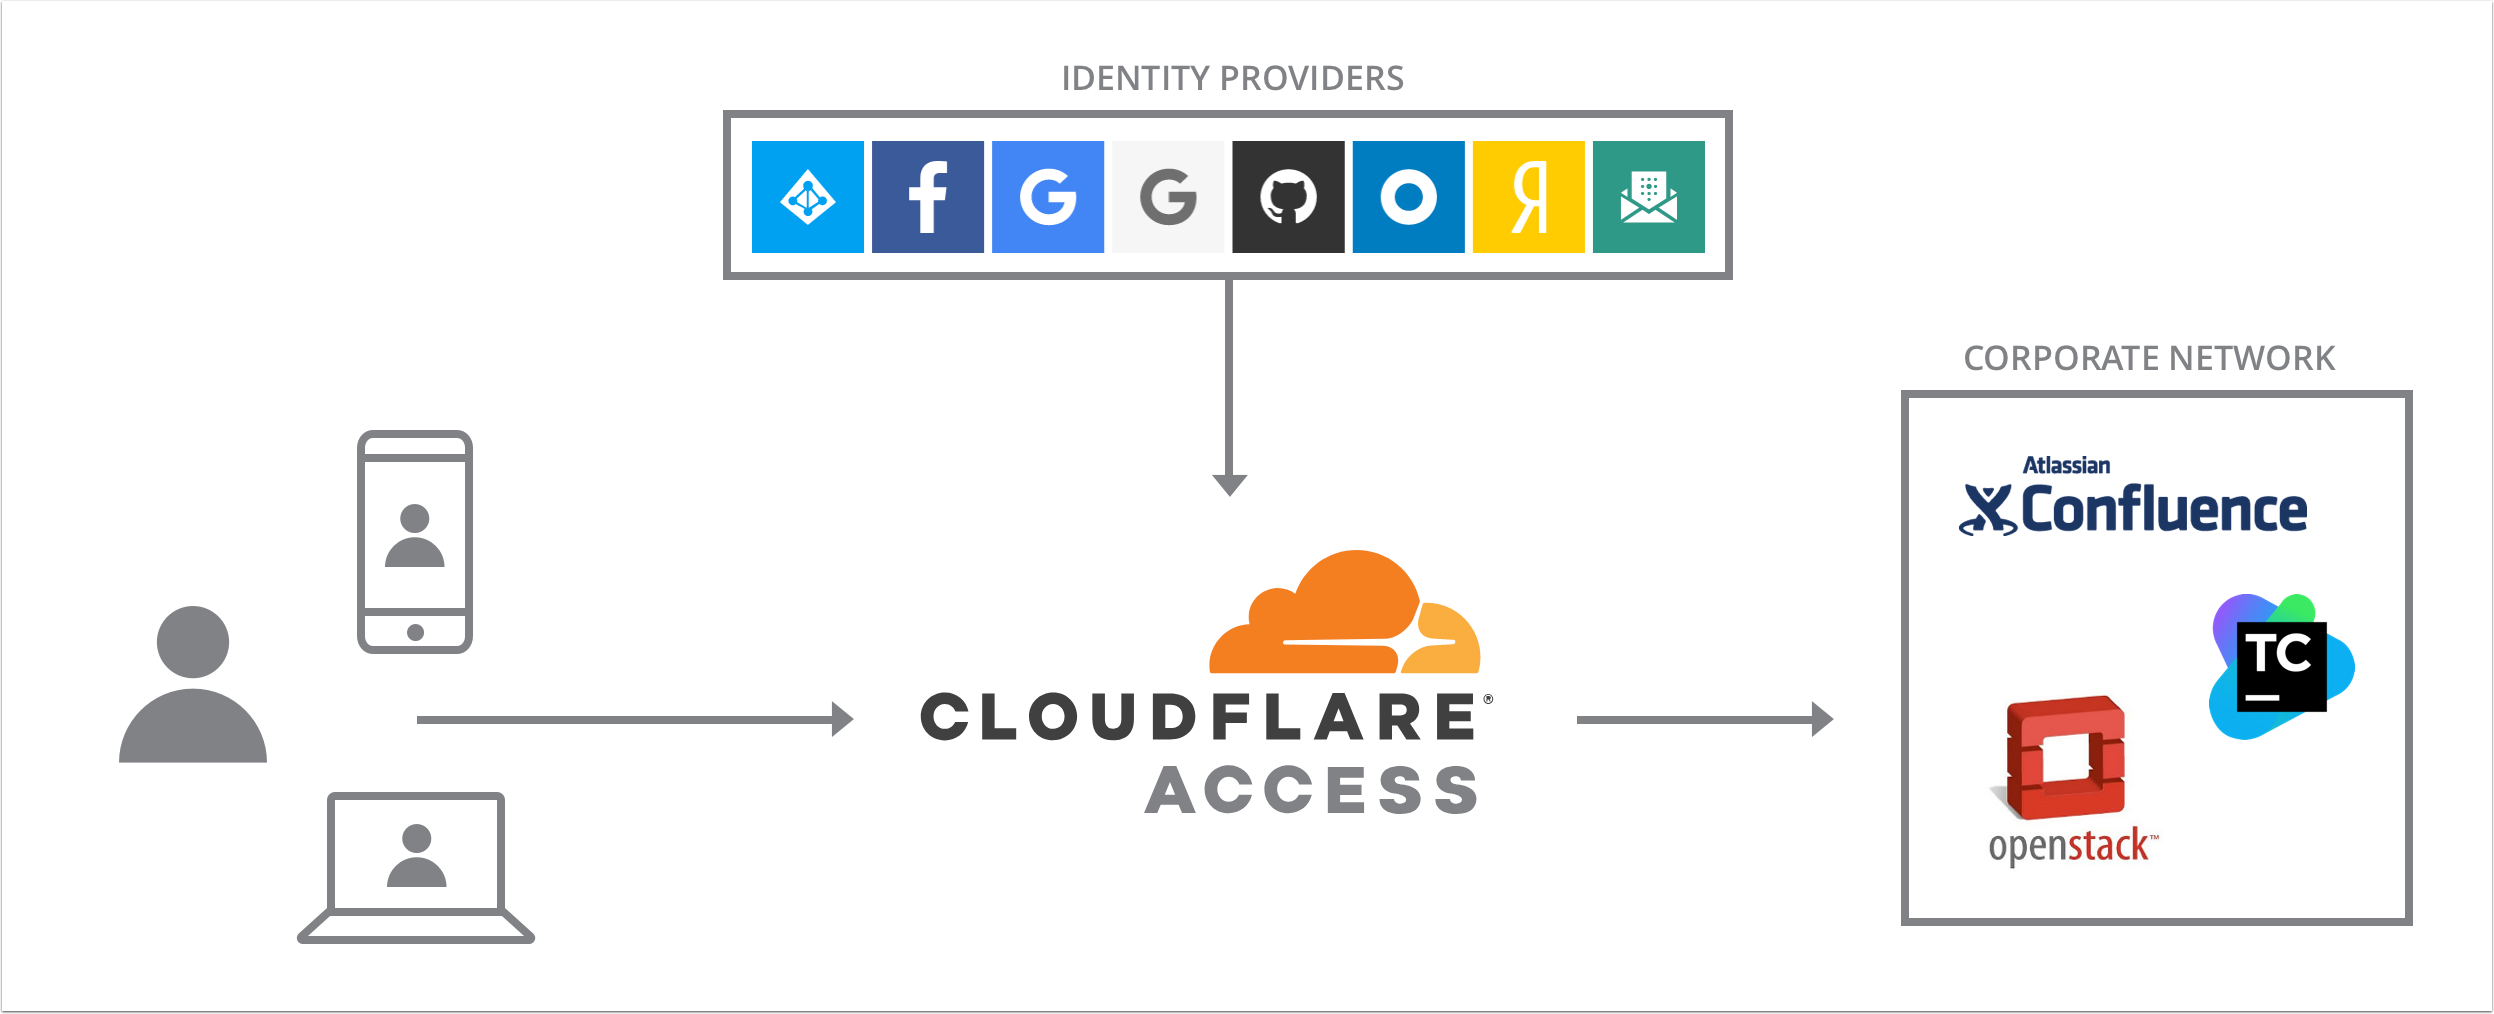
The setup is straightforward enough that there is almost no reason not to try it. The configuration takes minutes, the performance impact is usually positive, and the zero-trust dashboard gives you visibility into usage that you do not get from most consumer VPNs. The trade-offs around logging and egress control are real, but for most people using this as a performance and reliability optimization rather than a privacy tool, Cloudflare's WireGuard implementation is genuinely one of the best free networking tools available right now.