Getting Into Your Account
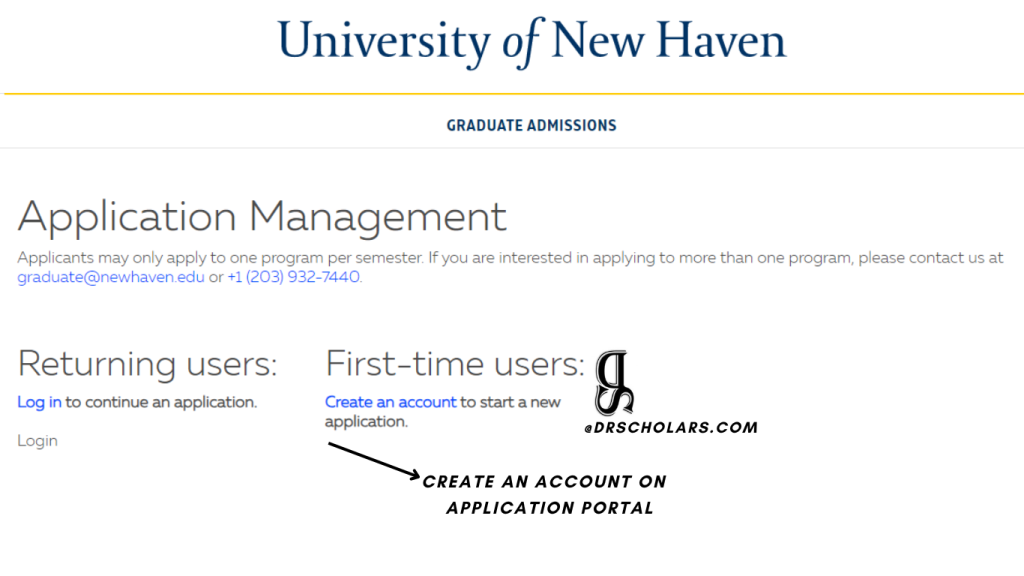
The University of New Haven uses a centralized authentication system that routes everything through their single sign-on portal. Most students and staff hit a wall on day one because they try to access course materials, the library, or the student portal as separate logins. They aren't. It all flows through one entry point. Once you understand the redirect chain, it takes about thirty seconds to get from your browser to your dashboard on any internal resource. Here's what the actual process looks like. You go to the UNH portal URL and enter your university credentials. Your NetID is typically your student ID or employee number followed by the @newhaven.edu domain format. The password is whatever you set when you first activated your account or had IT reset it. You hit submit, the SSO token validates, and then you're redirected to whichever campus resource you originally requested. If you were trying to reach MyWolverine or a Blackboard course, the system passes your auth credentials along automatically. You shouldn't be prompted again. I spent way too long trying to figure out why a colleague kept getting locked out during midterms. The issue wasn't the portal itself. It was that he had seven browser tabs open across three different campuses resources, each holding a stale authentication session. When the primary SSO token expired, only one session would refresh properly. The rest would throw cryptic 401 errors that looked like login failures but were actually just dead session handles. The fix was closing everything and starting fresh from the main portal page. Took him maybe two minutes instead of the hour he was wasting.
The password reset flow goes through the same authentication system, not a separate helpdesk page. If you've forgotten your credentials, you use the forgot password link on the login screen itself. It sends a recovery email to your university email address. You click the link in that email, create a new password, and you're back in. The whole thing usually takes under five minutes if your email is accessible. I've seen people waste twenty minutes calling IT when they could have just reset it themselves through the portal.
Common Issues and What Actually Fixes Them
Browser cache is the number one cause of what looks like a login failure. Clearing your cookies and cache for the newhaven.edu domain will resolve most issues where the page loads but the login button doesn't respond or you get kicked back to the login screen immediately after submitting credentials. Use Chrome's Incognito mode as a quick diagnostic tool. If you can log in there but not in your regular browser, it's definitely a cache or extension conflict. Disable extensions one at a time if you need to stay in your normal browsing session. Two-factor authentication is enabled by default for most accounts now. If you're not seeing the second-challenge prompt after entering your password, check your phone. The authenticator app or SMS code should arrive within a few seconds. Some people miss it because they close the login tab thinking it failed when it was actually waiting for the second factor. Keep the tab open and check your phone before doing anything else. There is a known issue where mobile browsers handle the SSO redirect differently than desktop browsers. The authentication token sometimes doesn't pass correctly between the mobile portal and campus apps. If you're on a phone and keep getting redirected to the login screen in a loop, switch to a desktop browser or use the device's request desktop site option. This resolves the redirect mismatch about ninety percent of the time. The native app versions of campus resources tend to handle auth better than mobile browsers anyway.
Get the Full Details
Security Considerations That Matter
Your credentials are only as secure as your password hygiene and session habits. Don't share your NetID and password with anyone, including people who claim to be from IT. University staff will never ask for your password over email or phone. If someone does, it's a phishing attempt. Report it to the IT helpdesk immediately. Always log out when using a shared or public computer. The SSO session can persist across multiple campus resources, so walking away without logging out leaves every connected system exposed. This is especially relevant in library computers and campus lab machines where multiple people share the same session history. Log out and close the browser entirely when you're done. Change your password periodically, but don't obsess over it. The university's policy typically requires changes every ninety to one eighty days depending on your role. If you're a staff member with access to financial or HR systems, the requirement is usually stricter. Students generally have more flexibility. Check your specific account settings in the portal if you're unsure what applies to you.
What Doesn't Work and Why
Attempting to bypass the SSO by accessing campus resources through direct URLs won't give you a shortcut. Every internal system checks the authentication token regardless of how you arrive at the page. Typing in a direct link to a course page or administrative system just triggers an immediate redirect back to the main login portal. There's no authenticated path around it, and no legitimate workaround exists for that restriction. Treating the password reset as a permanent fix for repeated login failures is another mistake. If you're getting locked out frequently, something else is wrong. It could be a corrupted browser profile, a compromised account, or an outdated credential stored in a password manager. Resetting your password four or five times without resolving the underlying issue is just cycling the same problem. Contact IT support with specifics about when the lockouts happen and what error messages you see. The single biggest limitation of this system is that it doesn't recover gracefully when the authentication service has brief outages. These are rare but they do happen, usually during peak times like add/drop week or the start of a semester. During an outage, there's nothing you can do except wait. The helpdesk can't force the SSO to respond faster. Plan your most time-sensitive tasks around those high-traffic periods if you can. Start your registration or grade checks early in the morning rather than midday when server load is highest.
Another structural weakness is that some older campus applications still rely on legacy authentication methods that don't integrate cleanly with the current SSO. If you're trying to access a departmental system that asks for separate credentials, it probably hasn't been migrated yet. In those cases, contact the specific department directly. The main IT helpdesk won't be able to troubleshoot a system that operates outside the unified authentication framework.