What You Actually Need to Know
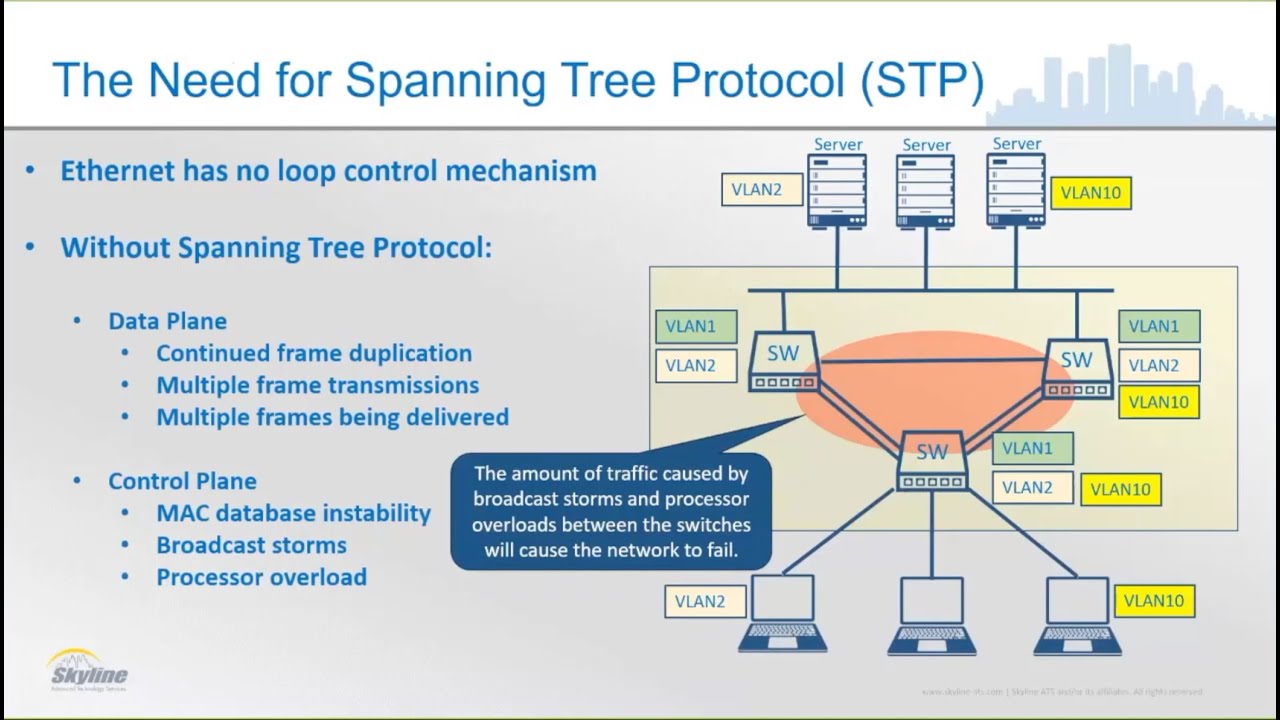
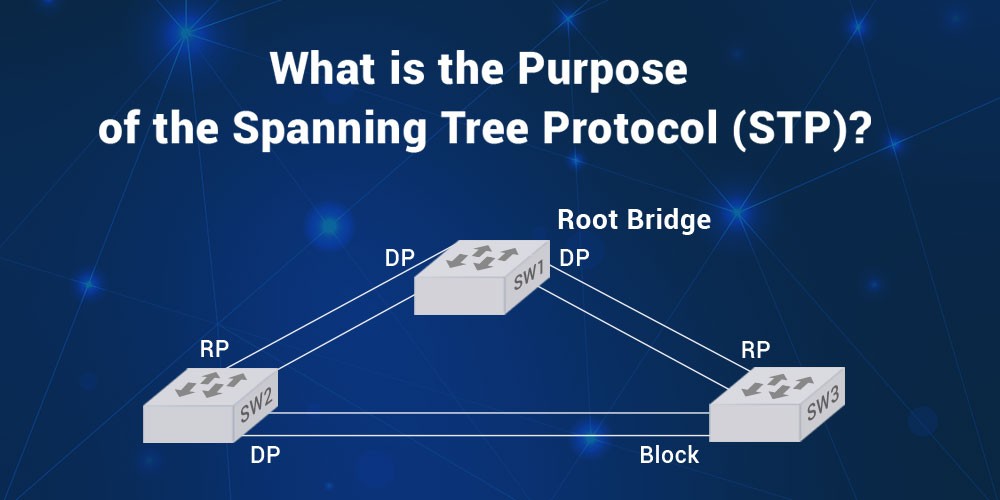
Most networks run Spanning Tree without anyone understanding it until something breaks. Then it's 2am and you're looking at a switch that won't converge. I've seen this happen in production enough times that I stopped waiting for someone else to figure it out. The basic idea is simple: STP prevents layer-2 loops by selectively blocking redundant paths. All the interesting stuff is in the details people skip reading about. Bridge Protocol Data Units get exchanged between switches every 2 seconds by default. Each bridge listens, evaluates path costs, and decides which ports should forward and which should block. The bridge with the lowest bridge ID becomes root. All other bridges select a root port based on lowest cumulative path cost to the root. Each segment gets one designated port. Everything else blocks.
Understanding The Spanning Tree Protocol The Unsung Hero Of Network Protocols
It's called the unsung hero because when it works, nobody notices. When it fails, the entire network goes down or behaves unpredictably. You'll often hear people say they don't need to understand STP deeply because modern switches handle it automatically. That's true until it isn't. The moment you add a new switch, reconfigure a VLAN, or upgrade firmware, assumptions break and you're back to figuring out why your users can't reach the printer. Here's something most guides don't emphasize enough. PortFast and BPDU filtering are not the same thing, and mixing them up will cause you real problems. PortFast puts an access port straight into forwarding state, skipping the listening and learning phases. BPDU filtering prevents a port from sending or receiving BPDUs entirely. If you enable BPDU filtering on a port that later gets connected to another switch, that switch won't know a layer-2 loop exists. It will forward frames indefinitely until the network collapses. I've seen this configuration error more times than I care to count. The safe approach is to use PortFast only on genuine end-host ports and never combine it with BPDU filtering unless you have a very specific reason and have tested the hell out of it. Another thing people get wrong is how portFast actually interacts with the spanning tree process. When you enable portFast on a switch port, the port transitions to forwarding immediately, but it still participates in STP. It still sends and receives BPDUs. The port is just allowed to skip the 30-second forward delay timer. If a BPDU arrives on a portFast-enabled port, the port loses its edge status and goes back through the normal convergence process. This is actually a safety feature. It catches misconfigured cables and rogue switches. You need to know this behavior exists because troubleshooting a port that keeps bouncing between forwarding and blocking often traces back to a BPDU arriving on an edge port it shouldn't be on.
The Convergence Problem Nobody Talks About
Traditional STP convergence takes 30 to 50 seconds. RSTP brings that down to 1 to 2 seconds under normal conditions. But the real-world convergence time depends heavily on your topology, your cable plant, and whether anyone has misconfigured anything along the way. In my experience, RSTP convergence is fast when the topology change is simple. When you have multiple switches with mismatched priorities, inconsistent VLAN configurations, or varying spanning tree versions running on different ports, convergence becomes unpredictable and sometimes painfully slow. I once spent three hours tracking down why a particular VLAN would intermittently drop for about 45 seconds every few hours. The network had 12 switches, eight VLANs, and a mix of 802.1D and 802.1w enabled on different ports. The culprit turned out to be a downstream switch that had STP priority set to 32768 instead of the expected value, which meant it was trying to become root for certain VLANs while simultaneously receiving superior BPDUs from the actual root. The switch would briefly accept root status, then lose it, causing a flap that propagated through the entire VLAN. The fix was auditing every switch's spanning tree priority across every VLAN and standardizing them. It took about four hours of configuration work but the problem never came back.
Get the Full Details

Practical Configuration Tips That Actually Matter
Set your root bridge manually. Don't let the default bridge ID election decide your network topology. The default priority is 32768 for every switch, which means the switch with the lowest MAC address becomes root. That's rarely the best choice for your core switch. Set the root bridge priority to something like 4096 on your intended root and 8192 on your backup root. This gives you predictable topology and faster failover when something goes wrong. Use link costs appropriately. STP uses path cost to determine the best route to the root. Older equipment uses the original IEEE cost values where 10Mbps links cost 100 and 100Mbps costs 19. Modern equipment uses revised cost values where 10Mbps costs 200000 and 10Gbps costs 2. If you mix old and new cost tables, your spanning tree calculations will be wrong. You'll see traffic taking suboptimal paths or loops forming because switches disagree on what the best path actually is. Check your cost tables and make sure all switches in the same STP domain are using the same reference. The command varies by vendor but the concept is the same everywhere. Enable LLDP-MED or CDP immediately if you haven't already. These protocols tell switches about each other and help with STP troubleshooting enormously. Without them, you're flying blind when trying to figure out what's connected where and why a particular link is behaving strangely. I can't count the number of times I resolved an STP issue in minutes just by looking at the CDP neighbor table instead of spending an hour tracing cables manually.
When STP Fails Completely
There are scenarios where STP simply cannot protect your network. Large flat layer-2 domains with more than seven switches in a spanning tree instance will hit the max forward delay limit. STP has a hard limit on how many hops a BPDU can traverse before being considered invalid. Exceed this and you get topology instability. If your network requires more than seven switches in a single STP domain, you need to redesign it with VLANs, inter-switch links, and possibly a different layer-2 boundary strategy. Another scenario where STP fails is in wireless mesh networks and some types of industrial Ethernet deployments. The protocol wasn't designed for dynamic topologies where links appear and disappear based on environmental conditions. In these cases, you'll see constant reconvergence events and network instability. Consider using a different protocol or implementing proper layer-3 boundaries at the edge of these problematic segments. The most dangerous failure mode is when someone disables STP on a port or switch to "improve performance." This never improves performance in a meaningful way and will almost certainly cause a loop that brings down your entire VLAN. I've seen this happen in data centers where someone turned off STP on a specific port because they thought it was causing unnecessary overhead. The resulting broadcast storm took down three floors of the building for about 20 minutes while they traced the problem back to the disabled spanning tree. STP overhead is measured in negligible CPU cycles. A layer-2 loop overhead is measured in lost data, frustrated users, and your reputation taking a hit.
Check your BPDU guard configuration regularly. BPDU guard shuts down a port that receives a BPDU when it shouldn't. It's the most effective protection against rogue switch connections on access ports. Make sure it's enabled on all edge ports and verify it's working correctly during your regular maintenance windows. A misconfigured BPDU guard can either fail to protect you or shut down legitimate ports unexpectedly. Test it by connecting a small unmanaged switch to a BPDU guard-enabled port and watching what happens. The port should go into error-disable state immediately. If it doesn't, your configuration is wrong and you need to fix it before something worse happens.