Android mods are everywhere and most people have no idea what they are dealing with
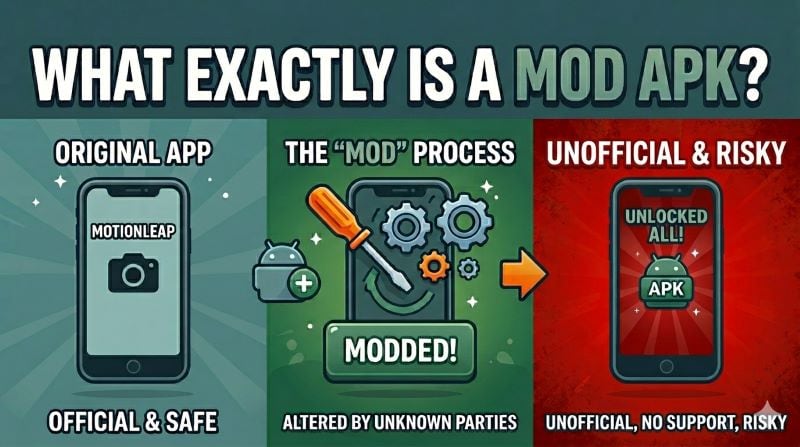
You've seen them. The modified versions of apps promising unlocked premium features, ad-free experiences, or cracked game currency. They circulate on forums, Telegram channels, and random websites. The appeal is obvious. The risk profile is messy. I spent years troubleshooting device bricking issues that traced back to poorly modified APKs before I started paying close attention to how these actually work. APK modification involves taking an Android application package, decompiling it, altering the source or resources, and recompiling it. Common modifications remove ad SDKs, unlock paid features by bypassing license checks, or alter game values. Some people do this to preserve software that has been abandoned by its developer. Others use it to run apps on devices the original developer never supported. I've seen both sides. The process starts with downloading the original APK. Then tools like apktool decompile it into a readable directory structure containing Smali code, resource files, and manifests. You edit what you need to edit. You rebuild the APK. You sign it with a keystore so the system will install it. That final signing step alone caused me three days of headaches in 2019 when I was trying to patch a banking app for testing purposes. The app used certificate pinning. A standard re-sign broke the trust chain immediately. I had to strip out the pinning verification from the Smali code manually before it would run at all. Took me about six hours of trial and error.
Benefits exist but they are narrow and situational. You can run discontinued software without relying on third-party mirrors that may have been tampered with. You can remove telemetry from apps that collect more data than they need. You can test how an app behaves under conditions the developer didn't intend, which is genuinely useful for security research. A modified app can also be smaller and faster if you strip out unused resources, sometimes cutting the APK size by forty percent or more depending on what you remove. The risks are where things get complicated. Most modified APKs come from sources with no quality control. I have personally seen mods that looked legitimate but included a minimal keylogger that ran quietly in the background. It would intercept text input from messaging apps and phone number fields. The developer of the mod wasn't the one who added it either. Someone had taken a popular mod, rebundled it with malicious code, and released it under the same name. This happens constantly and the infected version usually outsells the original because it gets indexed higher in search results. Beyond malware, there is the legal dimension. Distributing modified APKs that bypass license verification violates the original developer's terms and copyright in most jurisdictions. Using them is generally a gray area that varies by country and by the specific app. Google removes apps from the Play Store that facilitate circumvention. They also revoke developer accounts. The enforcement is uneven and mostly targets distribution rather than individual use, but that distinction doesn't protect you if your device gets flagged for suspicious behavior.
Technical risks matter more to most people than legal ones. Modified apps often break on OS updates. An app compiled against an older Android version with replaced native libraries can crash on Android 14 if the modder didn't update the ABI compatibility layer. I saw this with a popular camera mod that stopped functioning after a security patch changed how the Camera2 API handled permission callbacks. The modder released a fix two months later. Most people never got it. There is also the problem of signature conflicts. Android requires that all updates to an app carry the same signing key. If you install a modified version and then try to update it through normal channels, the signature mismatch will block the update entirely. You end up stranded on an old version with known vulnerabilities that will never get patched. I managed this by keeping a clean copy of the original APK alongside any mods I tested, so I could always roll back. It works but it adds friction to something that should be simple. The future of mobile apps is moving away from the kind of open modification environment that existed in the early Android days. Google's Verified Access feature in Android 14+ checks whether an app's signature matches its declared publisher. Play Integrity API makes it harder for modified apps to claim they are authentic. Banking apps, payment services, and streaming platforms are implementing increasingly aggressive anti-tamper mechanisms. Root detection alone took years to refine across the industry. Now companies are moving toward runtime integrity checks that scan for common modification frameworks like Xposed modules and Magisk.
Get the Full Details

This doesn't mean modding is dead. It means the window for safe, stable modification is narrowing. Developers who need custom app behavior are shifting toward official APIs and plugin systems. Companies like Unity and Unreal are building mod support directly into their engines, which gives users a legal and safer path to customization. For individual users, the trend points toward walled gardens with official subscription models and fewer cracks to fall back on. If you want to experiment with APK modification, start with open-source apps where the intent is clear and there is no business model to circumvent. Use a dedicated test device, not your primary phone. Verify checksums against the original APK before and after modification. Check the mod's reputation across multiple independent sources, not just one forum thread. And keep in mind that any mod you install gives that mod author the same access level as the original app, which is often permission to read your files, contacts, and network traffic. I still modify apps occasionally for legitimate research and personal projects. The process is straightforward once you understand the toolchain. The judgment call about whether a specific mod is worth the risk is the harder part. There is no clean answer that covers every situation.