How We Actually Evaluate Web Security Vendors These Days
The first thing you notice when you start digging into web safety companies is that every vendor claims to solve the same problems but uses completely different terminology. I spent about three years going through this process for different clients, and the pattern never really changes. You end up reading sales decks, running their tools, and comparing results that are often impossible to reconcile because each company measures things differently. The core issue is that most people evaluating these companies look at the surface-level features. They check if the tool does vulnerability scanning, maybe incident response, probably something with endpoint protection. That's how you get burned. The real differentiation comes from understanding what the underlying technology actually does and whether it fits your environment. I learned this the hard way after buying into a platform that claimed comprehensive coverage but missed critical attack vectors specific to our infrastructure. The sales team couldn't explain why either.
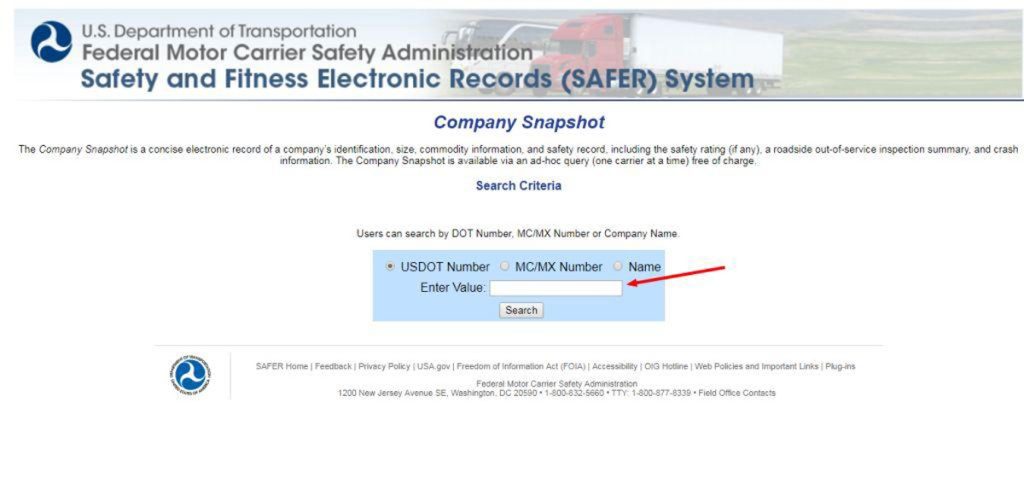
Uncovering The Truth A Safer Web Company Snapshot
Getting a clear picture of any web security company requires looking past the marketing. Start by requesting a live demo rather than a recorded one, and during that demo ask specifically about their detection methodology. How do they handle false positives? What's their actual patch timeline? Which attack patterns do they prioritize? Most vendors will deflect or give vague answers about their "proprietary algorithms." Press for specifics. I once worked with a company that scored incredibly well on paper and passed every basic compliance check. When I dug into their actual incident reports, I found they had a 40 percent false negative rate on credential harvesting attempts. They were detecting the symptoms but missing the root cause. We caught this because we asked to see their recent threat intelligence samples, which they were initially reluctant to share. Once we reviewed them, the gaps became obvious. Another thing that trips people up is the pricing structure. Many web security companies use tiered pricing that looks reasonable at first but becomes expensive once you factor in add-ons. Features that should be standard like extended log retention, custom rule creation, or advanced reporting often cost extra. I always calculate the total cost over a three-year period rather than just looking at the base subscription. The difference is usually significant.
You should also examine their update frequency. Security threats evolve constantly, so a company that doesn't push regular updates is already behind. Check their release notes and changelogs if they publish them. Companies that are transparent about their update cycle tend to be more reliable. Opaqueness about this is a red flag. Support responsiveness matters more than people realize. When something breaks at 2 AM on a Saturday, you need someone who can actually help, not just follow a script. I've had incidents where support teams took six to eight hours to respond because their escalation procedures weren't clear. Look into their support documentation first. If it's sparse or outdated, that reflects on their overall operational maturity. Consider running a proof of concept before committing. Most reputable companies will let you test their platform for a limited period. Use this time to validate their claims against your actual environment. You'll quickly discover where their toolset falls short. I usually set up a parallel testing setup where I run my existing solution alongside the new one for at least two weeks. The comparison reveals discrepancies that no sales presentation can address.
Get the Full Details

Check references too, but don't just talk to the ones they provide. Reach out to people in your network who have used the same platform. Their unfiltered feedback is often more valuable than any case study. I learned about one vendor this way after a colleague mentioned they switched providers within a year due to persistent detection failures. That saved us from repeating the same mistake. Finally, review their data handling policies carefully. A security company that doesn't take data privacy seriously is a liability waiting to happen. Ask where your security data is stored, how long it's retained, and who has access to it. Vague answers here should raise immediate concerns. The company needs to demonstrate transparency about their own security practices if they expect you to trust them with yours.