What People Miss When They Set Up Private Endpoints
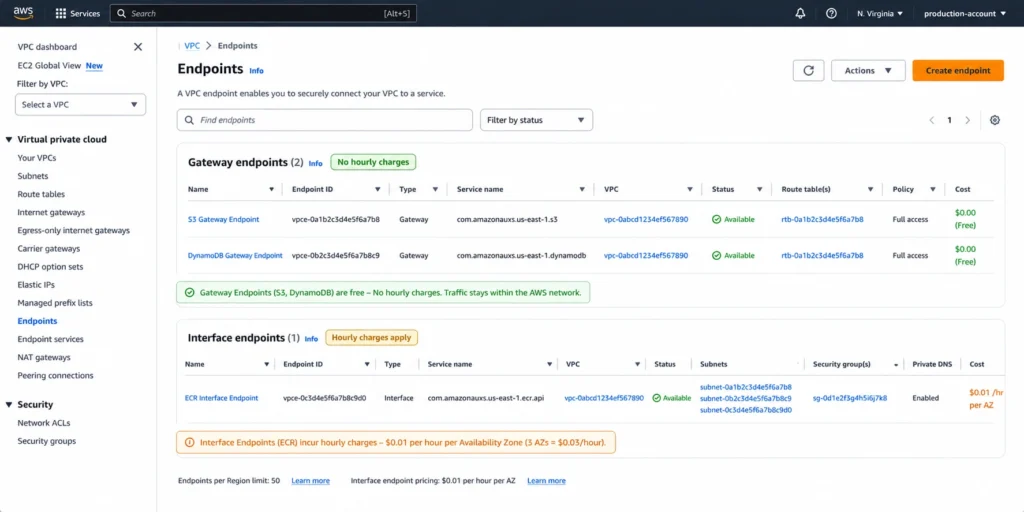
Most teams configure private endpoints once, then forget about them until the monthly bill shows up. That is when you notice the numbers are higher than expected. The pricing models across AWS, Google Cloud, and Azure are not identical, and they penalize certain usage patterns in ways that are easy to overlook during architecture reviews. I set up a private gateway endpoint for S3 last year in a multi-account setup. It looked clean in Terraform, cost almost nothing on the surface, and then I noticed data processing fees stacking up on the outbound side. Turns out Gateway endpoints don't charge for data transfer between the endpoint and the service within the same region, but they absolutely charge for data processed through them in certain configurations. I had to audit traffic routes across twelve accounts before I caught it. The fix was routing specific VPCs through NAT gateways instead of using interface endpoints for services that already have gateway support. AWS Gateway endpoints like S3 and DynamoDB have a hourly charge per endpoint plus a per-GB data processing fee. The hourly rate is currently six cents per endpoint per month which sounds negligible. The data processing fee is the thing that adds up, especially when you have heavy internal traffic. Interface endpoints are different. They charge an hourly fee per availability zone where the endpoint exists, plus a per-GB data processing charge. If you run interface endpoints across three AZs for a service, you are paying triple the hourly rate. I saw a production environment with eight interface endpoints distributed across three AZs and the monthly cost ran over four thousand dollars just in endpoint fees before any data processed through them.
The real hidden cost on AWS is Route 53 private DNS resolution. When you enable private DNS for an interface endpoint, AWS creates hosted zone entries and resolves internal domain names. That works fine until you need to resolve the same endpoint from multiple VPCs with different CIDR ranges, or when you have cross-VPC traffic via peering. You end up managing duplicate records or hitting throttling limits on DNS queries. A small team I consulted for spent three days untangling a DNS resolution loop that turned out to be caused by overlapping VPC CIDR blocks with identical endpoint DNS names. They solved it by switching to explicit DNS namespaces in the VPC settings rather than relying on the default private DNS association.
Google Cloud Pricing Structure
Google Cloud calls this Private Service Connect and the pricing model is simpler on paper but less transparent in practice. There is a forwarding rule cost per endpoint, a per-GB data egress charge, and a network service tier selection that most people get wrong. The forwarding rule itself runs about five dollars per month per endpoint. Data egress from your VPC to the private service follows standard network egress pricing, but only if you are crossing zones. Traffic within the same zone is free. That seems reasonable until you realize that cloud run services and certain managed services route across zones by default even when you think they should stay local. I worked on a migration where a team moved their internal API from a regional endpoint to a Private Service Connect endpoint and the monthly bill jumped by twelve thousand dollars because they had assumed intra-zone traffic was free across their entire deployment. It was not. The services were spread across four zones and the traffic patterns were not what anyone had modeled. Network service tier matters more than most people expect. Google Cloud has Standard and Premium tiers. Premium costs more per GB but uses Google's global network. When you are using Private Service Connect, the Standard tier can actually be cheaper for cross-zone internal traffic because Premium applies higher per-GB rates to egress that crosses availability zones. A production analytics pipeline I reviewed was running on Premium tier by default and paying roughly double what it should have for egress within the same region. Switching to Standard tier dropped the networking cost by nearly sixty percent without any change to latency or reliability.
Get the Full Details
There is also the issue of service attachment limits. Google Cloud enforces a default quota of fifty service attachments per VPC network. This is configurable but the request process takes time and not every org has the approval path ready. I encountered a situation where a growing platform team hit this limit mid-quarter and had to redesign their service mesh topology to consolidate multiple endpoints under fewer attachments. The workaround involved grouping related microservices behind a single load balancer fronting the private service connect rather than creating individual attachments for each service.
Azure Private Endpoint Costs
Azure charges per endpoint per hour, per GB of data processed, and then adds in the cost of the underlying load balancer infrastructure in some cases. The hourly rate is currently around fifteen cents per endpoint per month which is roughly two to three times what AWS charges for the same thing on an hourly basis. The per-GB processing fee is about eight cents per GB which again is on the higher end compared to the other providers. What people do not always account for is the public IP requirement for certain configurations. When you set up a Private Link service through Azure Portal or ARM template, you can choose to associate a public IP or skip it. Skipping it saves money but breaks compatibility with certain client configurations that expect a resolvable public endpoint for health checks or monitoring integrations. I spent an afternoon debugging a monitoring tool that was failing because the private endpoint had no public IP and the health check probe was using the wrong resolution path. Adding a dedicated IP address back in solved it but added roughly eight dollars per month per endpoint to the cost. Azure also has a private link resource cost that is separate from the endpoint cost. This is the managed private endpoint object itself and it carries its own hourly fee. Some enterprise configurations bundle multiple private endpoints under a single private link service but the billing does not simplify the way you might expect. Each endpoint object still incurs its own charge. A customer I advised had forty-two private endpoints across their production workloads and was paying over two hundred dollars per month in endpoint fees alone before data processing. Consolidating to a hybrid approach using a few load-balanced private links reduced that to approximately seventy dollars monthly while maintaining the same connectivity coverage.
Comparison And Practical Guidance
The cheapest option on paper is AWS Gateway endpoints for S3 and DynamoDB because the data processing fees are zero for traffic within the same region. But Gateway endpoints only work for those two services. Everything else requires Interface endpoints and the costs scale linearly with availability zones. Google Cloud tends to be the most predictable billing model but the network tier decision can double your costs if you pick wrong. The forwarding rule flat fee is easy to calculate upfront. The variable costs depend entirely on your traffic patterns and zone distribution. Azure sits in the middle on pricing but the management overhead is higher. Private link resources, endpoint objects, and load balancer configurations create multiple billing line items that are easy to misattribute. Their documentation separates these costs clearly but the Azure portal billing view does not always make the relationships obvious without custom cost allocation tags.

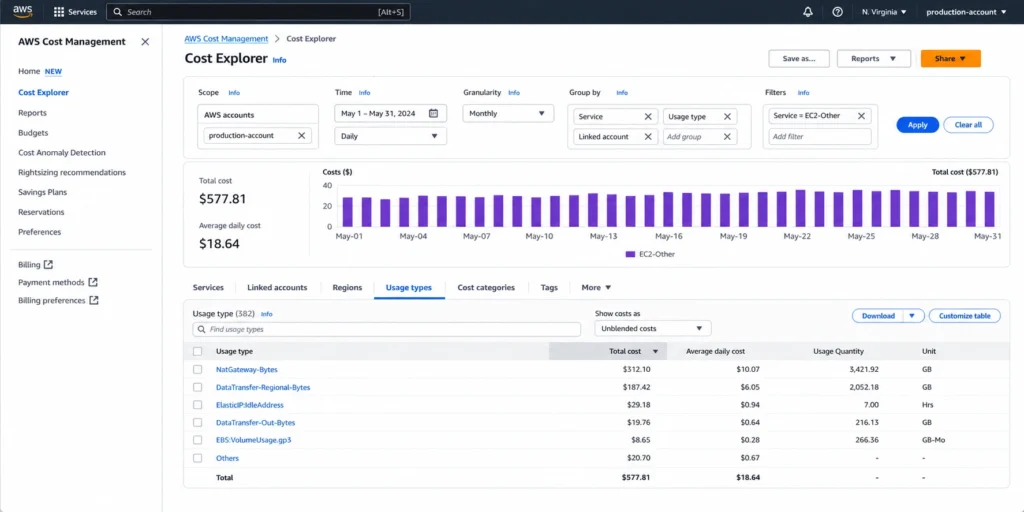
For workloads with high internal data transfer, AWS is generally the most cost effective if you can use Gateway endpoints. For multi-service environments where you need interface endpoints across many availability zones, Google Cloud often comes out ahead on total cost. Azure is competitive for smaller deployments but the per-endpoint cost adds up quickly once you pass the ten endpoint threshold. The single biggest source of unexpected cost across all three providers is not the endpoint fee itself. It is the traffic that flows through endpoints in ways the original architect did not anticipate. Internal service to service traffic that crosses zones, DNS resolution overhead from repeated queries, and data processed through endpoints that could have used public endpoints with VPC peering instead. I recommend mapping actual traffic flows before committing to private endpoints for every service. Even a rough estimate based on production logs from a similar staging environment will usually reveal at least one endpoint that would be better served by a different connectivity pattern. If you are already committed to a provider and want to audit existing costs, export the billing data with resource group or project breakdown for the last ninety days and filter for the relevant service categories. AWS gives you this under Cost Explorer filtered by Usage Type containing endpoint. Google Cloud billing exports include the service attachment and forwarding rule line items separately. Azure Cost Management lets you filter by resource type but you may need to add custom tags to track private link resources consistently.