What Happens When You Install MySQL and Skip the Password
You install MySQL, you start using it, and weeks later someone points out your root account has no password. That's a very common trajectory. The short answer is that MySQL doesn't have a single universal default password. It depends entirely on your operating system, your installation package, and which version you're running. But if you want to Uncover The Default Password Of MySQL Protect Your Database From Unwanted Access you need to understand where the system actually keeps credentials and what each installation path does by default. MySQL 5.6 and earlier often installed the root account with an empty password, at least on initial setup. That means anyone who could reach the database process on the server could log in as root without typing anything. MySQL 5.7 changed that by generating a random temporary password during the server's first startup and writing it into the error log. MySQL 8.0 continues this behavior. On Linux systems installed via apt or yum, you'll typically find the temporary password inside /var/log/mysqld.log or /var/log/mysql/error.log. The relevant line looks something like: [Note] A temporary password is generated for root@localhost: abc123!@#xyz. On macOS with Homebrew, the server starts and sets a blank password for root by default. On Windows using the MySQL Installer, the setup wizard forces you to set a password before the installation completes, but there's a checkbox to leave it blank that some people click by accident or convenience. Docker images for MySQL set the root password based entirely on the MYSQL_ROOT_PASSWORD environment variable you provide at container launch. If you didn't set that variable, the behavior varies by image tag, which is why people keep hitting walls.
There's also the debian-sys-maint account that appears on Debian and Ubuntu installations. That's not the root account. It's a maintenance user created during package installation with a password stored in /etc/mysql/debian.cnf. It has broad privileges on the system but is meant for package management, not for application connections. People often confuse it with the actual default root credential.
Where to Look When You Need the Password
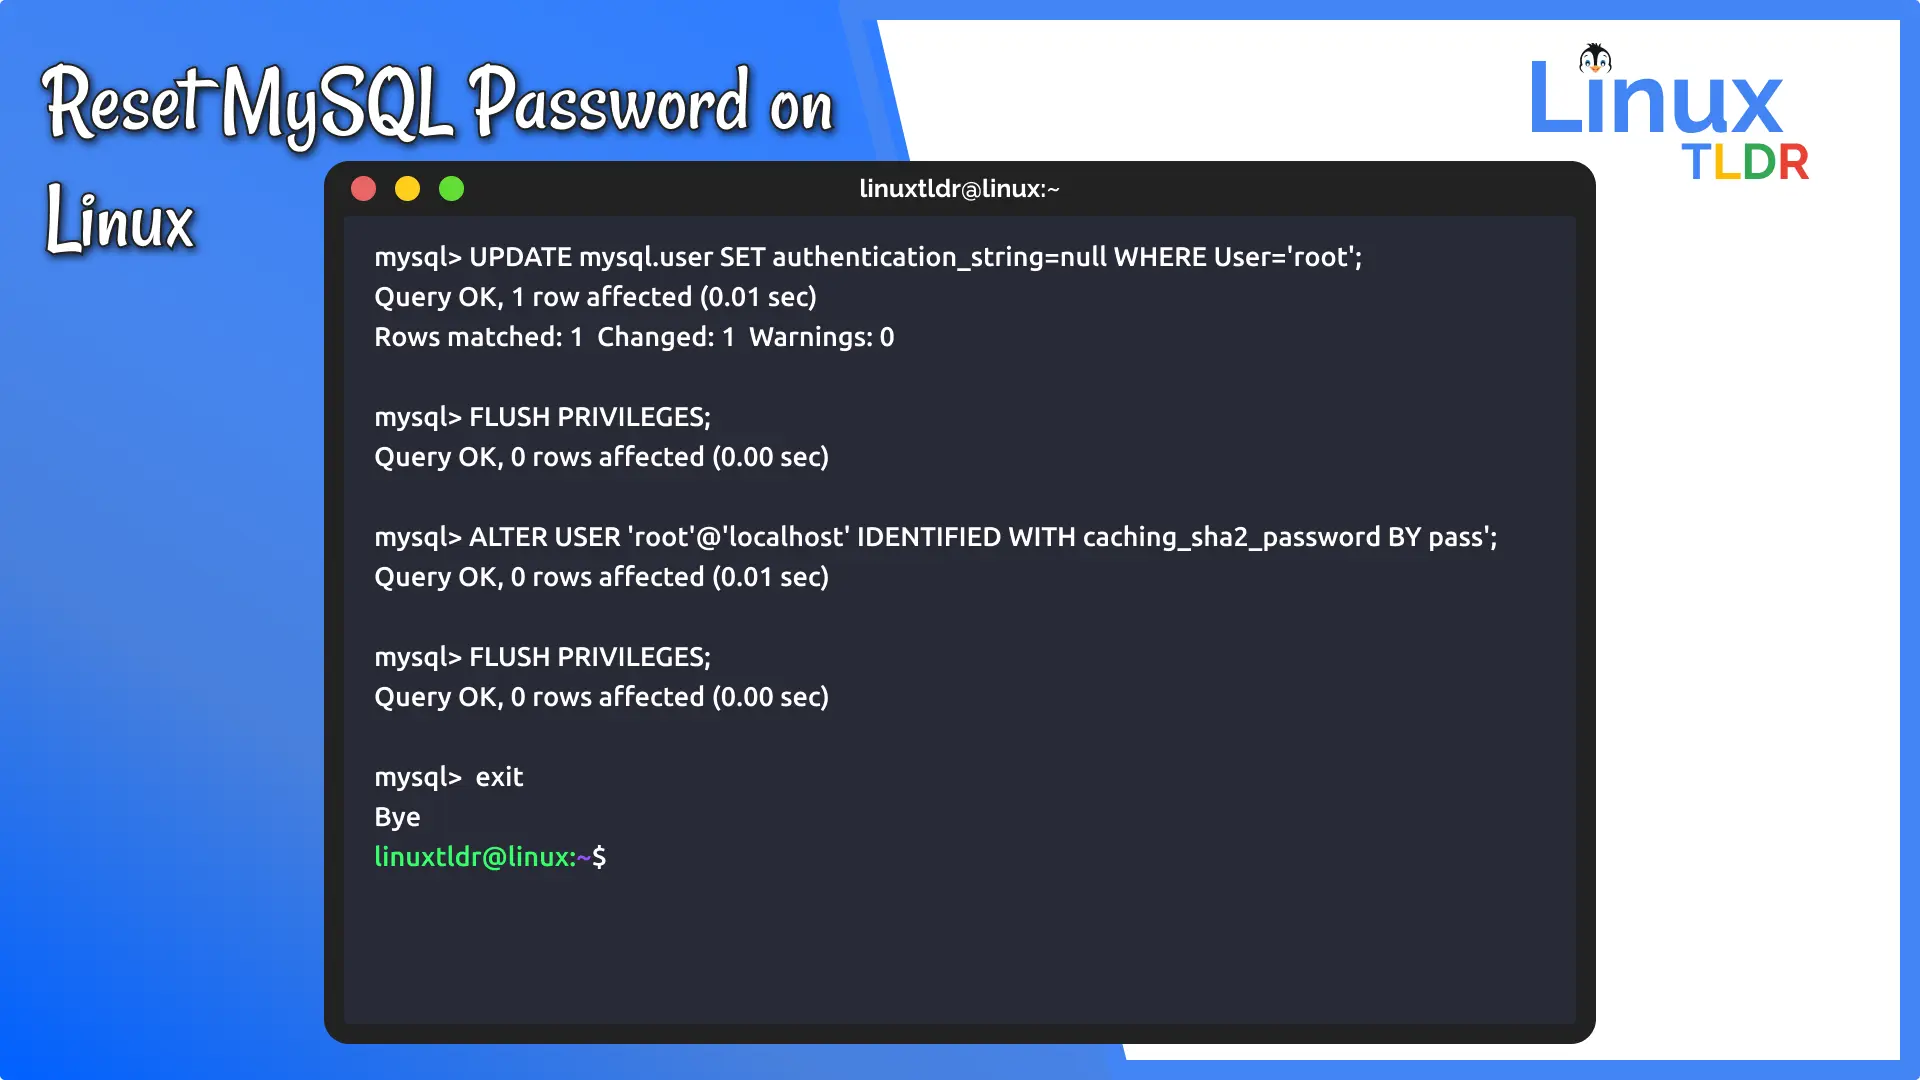
The error log is the primary place. On a fresh 5.7 or 8.0 installation, that temporary password expires after the first successful login, so you need to capture it before you log in. Once you change it, the old temporary password is gone and you can't recover it. That's intentional. If the server is already running and you can't access the error log for any reason, there's another path. You can restart the server with the skip-grant-tables option, which bypasses authentication entirely. You then connect without a password, flush privileges, and set a new root password directly. This is a recovery procedure, not a regular workflow. I've done it probably a dozen times over the years, usually because someone deployed a application server, pointed it at a database, and then couldn't find the password anywhere. The skip-grant-tables method works, but it leaves the server running without authentication until you reset things, so you need to be careful on a machine that's reachable from the internet. There's a detail most tutorials miss. When you start MySQL with skip-grant-tables on MySQL 8.0, the plugin authentication layer can interfere. If the root account uses auth_socket or caching_sha2_password, a plain password change might not stick the way you expect. The safest sequence is: start with skip-grant-tables, connect, run FLUSH PRIVILEGES, set the password using ALTER USER 'root'@'localhost' IDENTIFIED BY 'newpassword', and then restart normally. Skipping the FLUSH PRIVILEGES step is a common mistake that causes the change to fail silently.
Get the Full Details

Changing the Password After You Find It
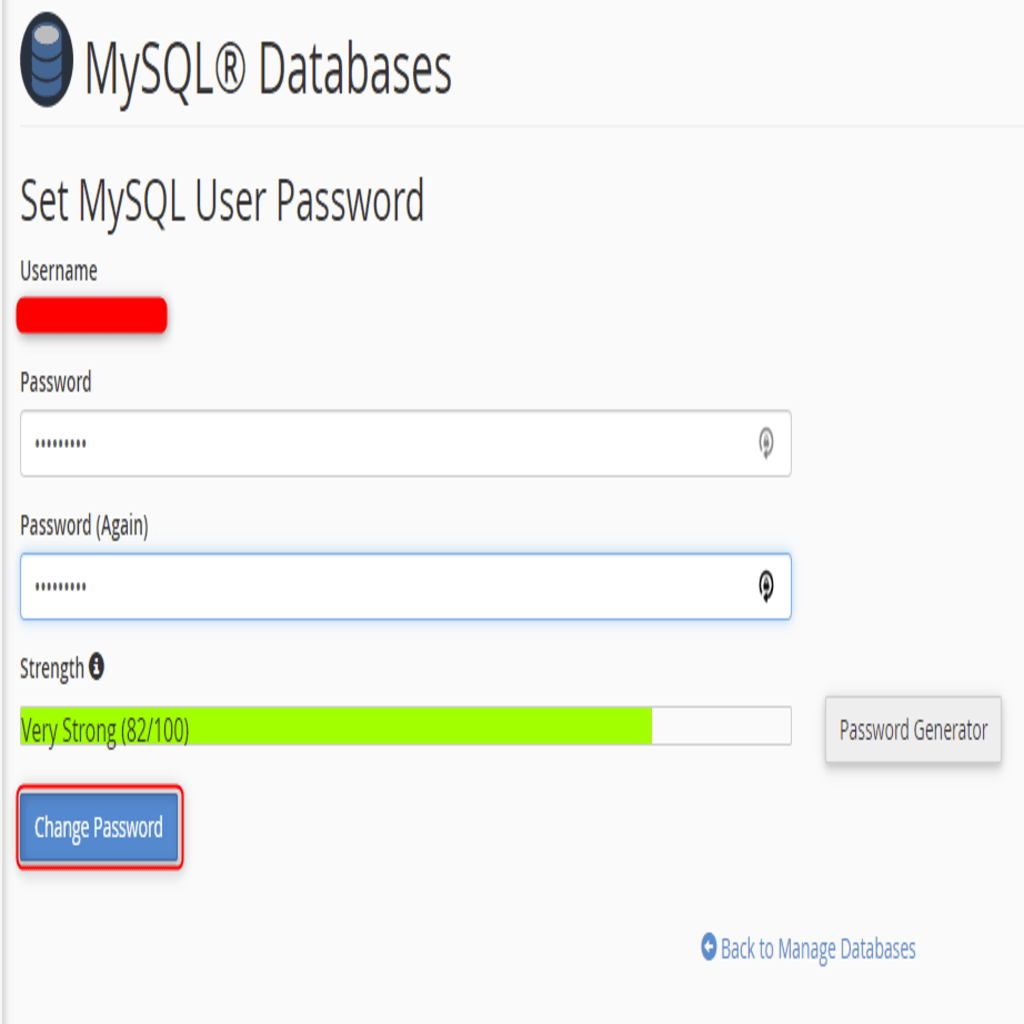
Once you know the current credential, the fix is straightforward. Connect to the server and run: ALTER USER 'root'@'localhost' IDENTIFIED BY 'a_strong_password_here'; That command works on both MySQL 5.7 and 8.0. The password needs to meet whatever complexity requirements your server enforces, which is controlled by validate_password policy. If you don't have that plugin installed, almost any string works. If it is installed, you need uppercase, lowercase, a number, and a special character, and the minimum length is usually eight characters by default.
For application accounts, the same command applies. Change the username and host to match the account you're updating. You should never have an application connecting as root. That's a separate issue that compounds the risk dramatically, but it's extremely common on small projects and hobby deployments.
Real Problems I've Seen With Default Credentials
I once inherited a server where someone had installed MySQL inside a VM for a staging environment and forgotten to change the root password. The VM was accessible through a VPN, which seemed safe at the time. Someone later scanned that network range and tried common empty-password combinations against any exposed MySQL ports. The account hadn't been touched in over a year. The logs showed dozens of connection attempts from external IPs before I locked it down. The workaround wasn't complicated, but the time spent auditing which databases had data and whether anything had been exfiltrated took a full morning. Another edge case is MySQL on shared hosting panels like cPanel or Plesk. These systems create per-user accounts with randomized passwords stored in their own databases or configuration files. The default root password for the underlying MySQL instance is usually irrelevant in those setups because the panel controls access. But the panel itself can have its own default credentials, which creates a second layer of risk. I've seen servers where the panel was secure and the database was fine, and others where both were weak. The pattern is consistent: someone set up the stack quickly and never revisited the credentials.
Limitations and When This Approach Doesn't Help
The methods above assume you have server-level access, either through SSH or physical console. If you're working with a managed database service like Amazon RDS, Google Cloud SQL, or Azure Database for MySQL, you don't control the installation or the error logs. The provider generates credentials for you and you can't access the system in the same way. In those environments, the solution is to use the provider's password reset tool, not skip-grant-tables. Trying to force a server-level recovery on a managed instance will fail because you don't have root access to the underlying OS. There's also the issue of password expiry. The temporary password generated on first startup expires after a single use or after a set period. You can't query MySQL for the temporary password once it's expired. There's no fallback command that returns it. If you missed writing it down during installation, you're back to the skip-grant-tables route or a provider reset tool.
Practical Steps to Secure the Installation
After you've changed the password, run mysql_secure_installation. It's a script that walks through several hardening steps: removing anonymous users, disabling remote root login, removing the test database, and reloading privilege tables. On a fresh install, this takes about two minutes and eliminates the most obvious attack vectors. The script is included with all standard MySQL packages. For remote access, you should not allow root to connect from any host other than localhost. If an application needs to connect from another machine, create a dedicated user with a strong password and restrict that user's host to the specific IP address or subnet it needs. The GRANT statement for that looks like: CREATE USER 'appuser'@'192.168.1.0/24' IDENTIFIED BY 'strong_password';
GRANT SELECT, INSERT, UPDATE, DELETE ON mydatabase.* TO 'appuser'@'192.168.1.0/24'; This limits the blast radius if that password is ever compromised. It also makes auditing much easier because you know exactly which host each account is allowed from. If you're managing multiple MySQL instances or a fleet of servers, consider using a secrets manager instead of hardcoding passwords in configuration files. HashiCorp Vault, AWS Secrets Manager, or even a simple encrypted environment file stored outside the repository will prevent the most common leak path, which is committing database credentials to version control.
What I Recommend After All This
The strongest single action you can take is to ensure every MySQL installation has a strong, unique password set at creation time and never left as an empty root account. The secondary action is to audit all accounts regularly. Run SELECT user, host FROM mysql.user; and review every entry. You'll often find test accounts or old application users that should have been removed. The tertiary action is to bind the MySQL port only to the interfaces that need it. If the database should only serve local processes, set bind-address to 127.0.0.1 in your my.cnf file. That alone prevents most external probing attempts. The temporary password in the error log exists for a reason. It's a one-time bootstrap credential designed to force you to set something real before you start using the server. Treating it as optional is what creates the majority of the exposure in production environments.