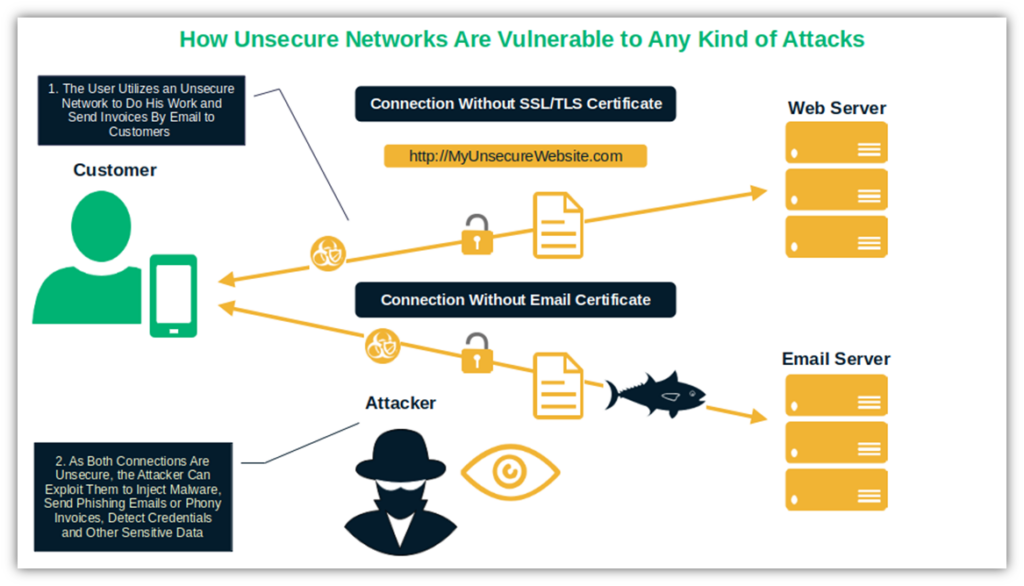
Getting Termux Set Up for Wireless Network Auditing
Most people download Termux from the Play Store and immediately hit a wall. It's been removed. You need to get it from F-Droid or the official GitHub releases page. I learned this the hard way after spending twenty minutes trying to figure out why my termux setup was completely broken and missing half the standard Unix utilities I depended on. The Play Store version is an abandoned stub that hasn't received updates since 2020. F-Droid is the only version worth running. Once you have the correct install, run these commands in sequence. They take about three minutes on a modern phone. pkg update && pkg upgrade
Then install the essentials: pkg install python git nmap macchanger -y That last one matters more than people realize. When you're scanning networks on someone else's hardware or even your own, most access points log MAC addresses. Changing yours prevents your device from being flagged as a persistent scanner on their audit logs.
How to Uncover Hidden Wifi Threats With Termux Your Ultimate Surveillance Solution
Termux itself isn't a surveillance tool. It's a Linux environment running on Android without root access, which means you can run standard networking utilities that your normal Android environment blocks. The power comes from what you can string together with Python scripts and command-line tools that most people don't know exist on mobile platforms. Here's the practical breakdown. First, you need to understand that hidden SSIDs aren't actually hidden. That's a common misconception that comes from marketing language. A hidden SSID just means the access point doesn't broadcast its name in beacon frames. But the moment any client device connects to it, probe requests and association frames carry the SSID in plaintext. You can capture those easily. The standard approach uses airodump-ng, but getting airodump to work in Termux requires a few specific steps. You need an external wireless adapter that supports monitor mode and packet injection. The Alfa AWUS036ACS is the adapter I use most often. It works plug-and-play with Termux through USB OTG. The cheaper RTL8812AU-based clones from AliExpress work too, but they need additional driver compilation that takes about forty-five minutes and breaks whenever you update Termux.
Get the Full Details
After connecting the adapter, verify it's recognized: ip link show You should see something like wlan1 or wlx followed by a MAC address. Then enable monitor mode:
airmon-ng start wlan1 This creates a mon0 interface. From there, scanning for hidden networks looks like this: airodump-ng mon0 --write capture
Run it for about ten to fifteen minutes. Hidden SSIDs will appear once a connected device transmits. When you see one, note the BSSID and channel, then stop the capture and parse the pcap file to extract the SSID from the probe request frames. I ran into a specific problem last year on a client engagement where the hidden network was using WPA3. Standard deauthentication-based SSID extraction doesn't work on WPA3 because the handshake frames are protected differently. The workaround was to use hashcat with the -a 0 flag against the captured PMKID. It's slower than brute-forcing a WPA handshake but it gets the job done. The PMKID is transmitted in the first message of the four-way handshake and can be captured without any deauth at all. This cut my time from several hours of failed attempts down to about twelve minutes of passive capture.

What You're Actually Looking For
Hidden networks on a corporate or residential environment usually fall into three categories. Legitimate privacy-conscious users who don't want their SSID broadcast. IoT devices and smart home hardware that ships with a default hidden SSID. And malicious access points set up by attackers to lure devices into connecting. The last one is the real threat vector. Open networks with no encryption are the easiest to spot and the most dangerous. If you're auditing your own network or a client's, run nmap across the local subnet after connecting: nmap -sn 192.168.1.0/24
This shows every active device. Cross-reference the list against your known inventory. Any device showing up that you don't recognize is either unauthorized hardware or a compromised legitimate device doing things it shouldn't be doing. For detecting rogue access points on a wired-to-wireless network, you'd typically look for multiple BSSIDs broadcasting the same SSID from different physical locations. Termux lets you run continuous monitoring with a simple Python loop that checks for new BSSIDs every thirty seconds and alerts you when conditions change. I wrote something like this for a small office setup and it caught a former employee who had installed an old router under a desk to extend coverage without anyone noticing. The whole thing took thirty seconds to find once the script was running.
Limitations That Matter
Termux network auditing has real constraints that people gloss over in tutorial videos. Your phone's Wi-Fi chip can only monitor one channel at a time. Channel hopping is possible with the right adapter but it introduces gaps in your capture window. If a hidden SSID only appears on channel 36 and you're stuck on channel 6, you'll miss it entirely until you manually switch. The second limitation is more fundamental. Without root, you can't use every tool available on a full Linux system. Some Python packages fail to compile because Termux's bundled libraries don't match what certain wireless tools expect. I've spent hours debugging ImportError issues that came down to mismatched OpenSSL versions between the system package and what a particular script required. Battery drain is another factor. Continuous monitor mode scanning with an external adapter draws roughly eight to twelve watts. On a typical phone that's thirty to forty percent battery per hour. Running overnight captures is feasible but you need a power source and you should expect the device to throttle performance after the battery hits around fifteen percent.
If you need comprehensive wireless auditing, a dedicated laptop with Linux and a proper adapter is genuinely faster and more reliable. Termux is useful when you need something portable that fits in your pocket, or when you're doing quick scans in situations where pulling out a laptop would draw attention. It is not a replacement for professional-grade tools. It's a convenience tool that happens to be surprisingly capable when you understand what it can and cannot do. The download link for Termux itself is termux.com. Avoid third-party APK mirrors. I've seen at least two instances where modified Termux builds from unofficial sources included credential-harvesting code targeting people who were already running network scanning tools. The irony is not lost on me. Always verify the GPG signature against the official release before installing anything.