How Unblocked Streaming Sites Actually Work
The whole concept comes down to proxy routing and domain rotation. When a school or workplace blocks streaming platforms, what they're really blocking is the domain name resolution at the DNS level or via URL filtering categories. Unblocked sites get around this by hosting mirrors on different domains, using CDNs that don't get categorized, or running embedded players that pull from upstream servers that aren't on any blocklist. I spent three years managing IT infrastructure for a district before moving to the security side, so I watched this cat-and-mouse game play out in real time. The blocking software gets updated weekly, and the site operators respond within hours. It's not complicated technology, but it requires constant maintenance.
Unblocked TV Series Sites The Hidden World Of Online Entertainment
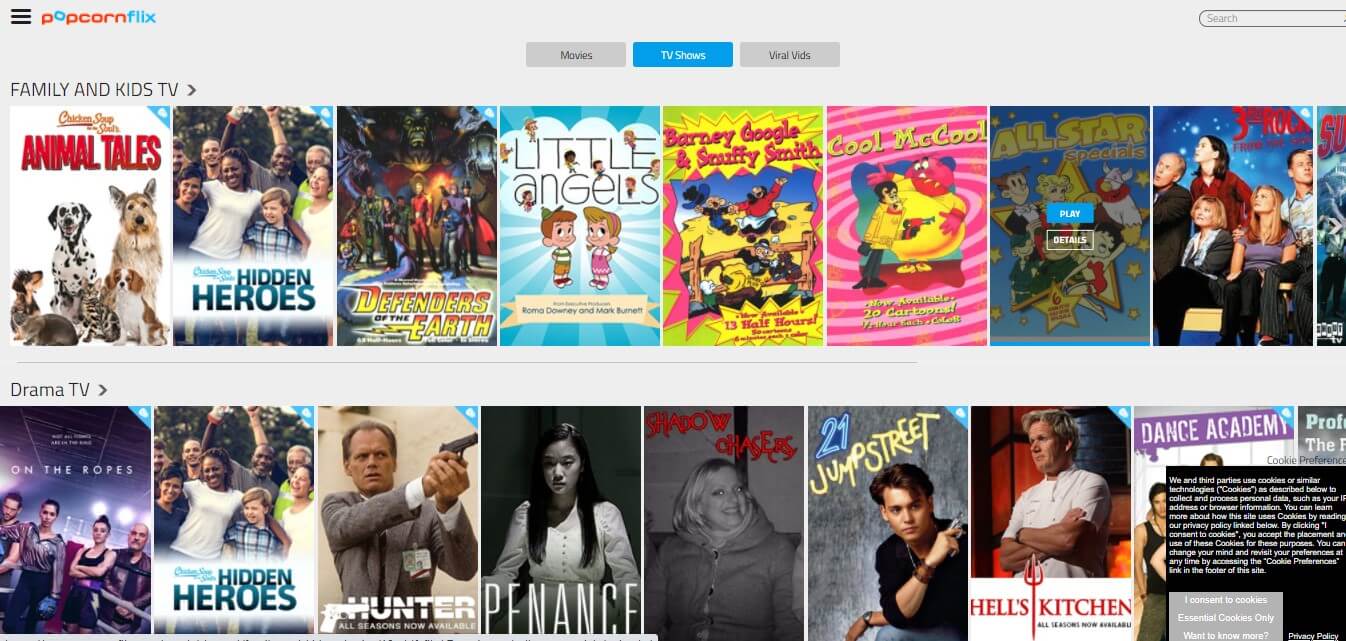
Most of these sites don't actually host any video files. They're aggregators. They scrape embed URLs from file-hosting services, use iframe wrappers, or pull from third-party video hosts that haven't been blocked yet. The actual content lives on servers that may or may not have licensing deals. That's the part nobody wants to talk about at these forums. When I was still running networks, I'd see kids bypassing filters using these mirror networks. The ones that stayed working the longest were the ones with rotating CDN backends and multiple redirect chains. Single-domain sites lasted maybe two weeks before getting caught. The well-funded operations had infrastructure that could survive takedowns because they distributed across dozens of hosting providers simultaneously. Here's what people miss when they're just trying to watch something: the quality variance is brutal. A site might stream a crisp 1080p episode from one source, then that source goes down and the fallback is a CAM rip with audience noise. I learned to check the embed source URL before committing to an episode. If it's pulling from a known legitimate host, you're usually fine. If it's some random file-sharing domain with a track record of malware, that's your problem now.
The real issue nobody mentions is the ad infrastructure. These sites survive on aggressive advertising because they're not paying licensing fees. I've seen pop-under counts hit forty simultaneous windows on a single page load. Some of those ads served malvertising that redirected to credential harvesting pages. I had a student once land on a fake Adobe updater that stole his school login credentials. It took me two days to figure out what happened because the malware had already encrypted his profile. If you're going to use these, here's the practical approach that actually works. Run a ad blocker that's frequently updated. uBlock Origin with the recommended filter lists will cut most of the malicious redirects. Don't disable it, even when a site asks you to. Those requests are always social engineering. Keep your browser sandboxed or use a separate profile that doesn't have your real accounts logged in. Disable JavaScript on pages that don't need it, since a lot of the malicious payloads load through script injection. Domain freshness matters more than most people realize. A site that's been around for five years and hasn't changed its infrastructure is probably either being heavily monitored by authorities or has already been compromised. The operational ones rotate domains monthly. If you're browsing a mirror network, check when the domain was registered. Anything older than a year with active streaming content is suspicious.
Get the Full Details

There's also the to consider. In the United States, accessing copyrighted content without authorization through these sites exists in a legal gray area that leans toward infringement. The site operators bear the brunt of enforcement, but users have faced consequences too. I've seen cases where ISPs flagged repeat access and escalated to the school administration, which then involved parents and potential disciplinary action. It's not worth the risk for a TV show. The technical workarounds that actually persist long-term use a combination of DNS-level filtering evasion and encrypted traffic inspection bypass. Some users set up their own DNS resolvers through services that don't category-filter, but most of those get detected within weeks. VPNs work until the ISP starts implementing Deep Packet Inspection and blocking known VPN exit nodes. It's an ongoing arms race that most casual users don't have the patience or technical skill to maintain. I've also noticed that the content library on these sites is unreliable. New episodes appear slowly because the sources have to be found and encoded. By the time an episode shows up on an unblocked aggregator, it's often been through multiple re-encoding passes that degrade quality significantly. The originals are usually available through proper channels within hours of airing in many regions now.
For people who just want to watch shows without the hassle, a proper subscription service is cheaper and less risky than people admit. The ad-supported tiers alone cost nothing. The real cost only kicks in when you want multiple simultaneous streams or offline downloads. Even then, family plans split the expense to about five dollars a person per month in most cases. The whole ecosystem around these sites is poorly understood because the people running them have no incentive to explain how it works. What I can tell you from experience is that the technical barriers are lower than most people think, but the security and legal risks are real and measurable. If you choose to use them anyway, treat every page load like you're entering an unknown environment. Assume there are tracking pixels, assume there are redirect chains, assume something could go wrong. Then take the precautions that actually reduce the risk rather than the ones that just make you feel safer.