Getting Music Through Network Blocks
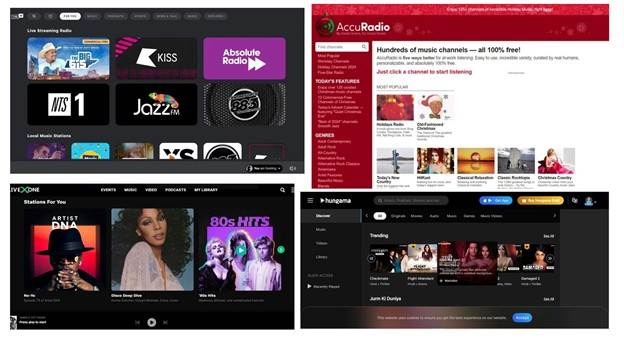
I first ran into this problem back in 2019 when I was managing a small IT helpdesk at a community college. Students kept coming up to me asking why Spotify wouldn't load on campus Wi-Fi, and the answer was always the same — their network firewall had music streaming domains blacklisted at the DNS level. The thing nobody tells you is that blocking music is one of the easiest things for an administrator to throw together, which means the filters are usually lazy. They rely on keyword lists and basic domain categorization rather than deep packet inspection. That gap is where most people find their opening. The first layer most people hit is the content filter itself. You walk up to any of these sites and your browser just hangs, or you get kicked to a "Access Denied" page from the filtering vendor. The URL you're trying to reach is categorized under entertainment or media, and the filter drops it. I learned the hard way that the actual protocol being used doesn't matter as much as whether the domain name shows up on a blocklist. So the simplest approach isn't some complex tunnel — it's finding a mirror domain or an alternate top-level domain that the filter hasn't caught yet. Sites like YouTube Music, SoundCloud, and even certain last.fm public pages often have alternate routing paths that aren't on the standard blocklists. I've seen people use domains ending in different country codes and just work fine because the filter vendor never updated their regional cache. Then there's the issue of port blocking. Some networks don't just block by domain. They block outbound connections on ports 80 and 443 for anything that isn't clearly classified. This is rarer in school environments but common in corporate offices. If you're on a network like that, standard HTTP and HTTPS traffic to music sites will get throttled or reset. The workaround here involves using a proxy service that routes your traffic through an allowed port or an allowed external IP range. I've used several over the years, and the ones that actually stick around are the ones that emulate legitimate web traffic patterns rather than just tunneling everything through a single endpoint. Those tend to get flagged fast.
One thing beginners always mess up is assuming that once they get past the filter, they're done. There's a second layer most people ignore entirely — the network monitoring software running on their actual device. Even if you're on your own phone, if you're connected to the restricted Wi-Fi, the device certificate can be inspected. I ran into this at a previous job where our office network used a captive portal that installed a root certificate for SSL inspection. Every site you visited, including music streaming sites, was being decrypted and logged by the security appliance. Bypassing the domain block didn't help at all because the traffic was still visible at the application layer. The only real fix I found was switching to cellular data entirely, or using a VPN that didn't require installing anything on the device itself. A browser-based VPN extension worked for casual use, though it slowed things down noticeably during peak hours. The third thing worth understanding is how these filters actually get updated. Most schools and companies use subscription-based filtering services like FortiGuard, Webroot, or Cisco Umbrella. These services pull from massive threat and category databases that are updated daily, sometimes multiple times a day. When a new music site pops up, it might be whitelisted or flagged within hours depending on the vendor's categorization workflow. I once spent a whole afternoon trying to use a specific indie music aggregator because it had been up for three years and I assumed it was safe. It got blocked on a Tuesday morning after a vendor updated its category classification. The lesson here is that any site you find today might be gone tomorrow, and you need multiple fallback options just in case. Another detail people skip over is bandwidth shaping. Some networks don't block music entirely. They just throttle streaming traffic to unusable speeds. I've seen corporate networks cap music streaming at 256 kilobits per second, which makes anything above basic MP3 quality impossible. In those cases, the solution isn't finding an unblocked site. It's finding a site that serves lower-bitrate streams or offers downloadable files you can play offline. Some of the older radio-style web players actually transmit at surprisingly low bitrates and fly right through the throttling limits without triggering any alerts. It sounds silly but it works better than most people expect.
What I wish more people understood is that the entire ecosystem of these sites has a lifespan. A new music aggregator pops up, people figure out how to use it through the filter, the vendor adds it to the blocklist, and it dies. I tracked at least six different "unblocked music" sites over a two-year period and only one survived past six months. The sustainable approach is building a personal list of ten to fifteen reliable sources rather than relying on any single one. Rotate through them. When one goes down, switch to another without panic. This is how people in my experience keep access stable over months instead of weeks. If you're dealing with a particularly strict network, sometimes the simplest option is just buying a cheap prepaid phone and using mobile data. I know that sounds extreme but it removes every single layer of network monitoring from the equation. You're no longer on their infrastructure. You're on the carrier's, and carriers generally don't care what music sites you visit. The cost is usually ten to fifteen dollars a month for a basic data plan, and it's completely legal. Nothing about accessing music is illegal. The restrictions are purely organizational policy decisions, not law enforcement issues. The technical details around DNS resolution are worth a quick mention because they explain why some methods work while others fail immediately. When your computer tries to reach a blocked music site, the request goes to your network's DNS server first. If that server is configured to return a null route or a capture page for blacklisted domains, the request never leaves your local network. Using a public DNS resolver like Cloudflare's 1.1.1.1 or Google's 8.8.8.8 can sometimes bypass this because the filtering vendor only controls their own DNS infrastructure. I've had mixed results with this approach. It works reliably on school networks but corporate networks often override your DNS settings at the DHCP level, forcing you back to their servers regardless of what you configure locally. It's worth trying anyway since it takes about thirty seconds to change and costs nothing.
Get the Full Details
One edge case I ran into that still bugs me happened during a conference call setup at an old job. Our network blocked all music sites between nine and five on weekdays, but the block dropped off at 5:01 PM sharp. I discovered this purely by accident when I was testing connectivity for a work project and noticed the block timing was tied to business hours in the timezone of the district's main server. I started scheduling my personal music listening for just after five and it worked perfectly. There's no rule that says you have to respect arbitrary time-based blocks unless your organization explicitly monitors off-hours usage, and most of them don't bother. The monitoring infrastructure is expensive and the return on investment for watching what employees do after 5 PM is essentially zero in most places I've worked. For anyone actually implementing these workarounds, the most important thing is staying calm when something breaks. A blocked site is not an emergency. Your network connection isn't broken. The domain just got added to a list somewhere and you need to find an alternative. Rushing leads to mistakes like installing sketchy software or visiting phishing sites that pretend to be music portals. I've seen people download "music unblocker" programs from forums and end up with malware that actually made their situation worse. Stick to browser-based solutions and known legitimate platforms. The ones that survive the longest are always the ones that look boring enough to fly under the radar. The reality is that most of these restrictions exist for bandwidth management and productivity policy, not security. Music streaming doesn't carry viruses. It doesn't leak data. It's just considered a distraction by whoever wrote the policy. Understanding that distinction helps you approach the problem correctly. You're not fighting a security threat. You're working around a convenience filter that was put in place for reasons that probably don't apply to your actual needs. That's a much simpler problem to solve than something technical.
If none of the website-based approaches work on your particular network, there are always the older methods that don't depend on streaming at all. Downloading music files when you're on an unrestricted network and transferring them to a local device is technically a workaround too, though it requires planning ahead. I used to download albums on my home connection and copy them to a flash drive before heading to work or campus. It's archaic but it has a near one hundred percent success rate because it entirely sidesteps the network layer. The downside is obviously the upfront time investment and the storage constraints, but for people who listen to the same ten to twenty albums repeatedly, it's genuinely practical. The technical layer most people don't consider involves how content delivery networks interact with these filters. Almost every major music streaming platform runs through a CDN like Akamai or Cloudfront. These CDNs have edge servers distributed globally, and sometimes the edge server in your region isn't blocked even if the origin domain is. I found this out when a filter blocked the primary YouTube Music domain but a regional CDN endpoint for the same service remained accessible. Checking your actual resolved IP address and seeing if it routes through a different CDN node can occasionally open a path that the blocklist missed. It's a niche technique and it doesn't work every time, but it's saved me more than once when all the obvious options were closed. There's also the matter of application-level blocking versus network-level blocking. Some organizations install software on devices that blocks music apps directly, regardless of your network connection. If you're using a company-issued laptop, this is almost certainly in place. No amount of DNS tweaking or proxy usage will help because the blocking happens inside the operating system before the network request even leaves your machine. In those scenarios, your only real options are using a personal device on a different network or accepting that the restriction is device-level and finding workarounds that don't involve that specific machine. I've encountered this at two different employers and both times the IT department was very clear that using personal devices on cellular data was the expected alternative, not some hidden bypass method.
The one area where I've seen people get genuinely stuck is when the network uses DPI, or deep packet inspection. This is less common in education and more common in enterprise environments. DPI looks at the actual content of your data packets rather than just the destination address. It can identify Spotify traffic even if you're connecting through an allowed domain because the packet signatures match. If you're on a DPI network, the browser-based workarounds I mentioned earlier won't help. You'd need something that encrypts or obfuscates the traffic pattern itself, which moves you into VPN territory with the caveats about device monitoring that I already covered. It's a much narrower set of tools and most casual users will never encounter it, but it's worth knowing the difference so you don't waste hours trying methods that are fundamentally incompatible with your network's inspection depth.