Getting Your DNS Changed Without Overcomplicating It
I changed my DNS settings last week because my ISP had quietly started blocking certain streaming services during peak hours. Nothing dramatic, just gradual timeouts that got worse over the course of a few days. The fix was straightforward but most guides online make it sound way more complicated than it needs to be. I'm going to walk through this the way I wish someone had explained it to me without padding. The core idea behind Unblock Websites With DNS A Quick Guide To Bypassing Restrictions is simple: your computer asks a DNS server to translate domain names into IP addresses. When your ISP controls that server, they can selectively return wrong answers or timeouts for domains they don't like. Switching to a public resolver like Cloudflare's 1.1.1.1 or Google's 8.8.8.8 means those blocks stop working, at least the DNS-level ones.
Unblock Websites With DNS A Quick Guide To Bypassing Restrictions
On Windows, open Network Settings, then change adapter options. Right-click your active connection and go to Properties. Select Internet Protocol Version 4 and click Properties again. Under DNS server addresses, choose Use the following DNS server addresses and enter 1.1.1.1 as primary and 1.0.0.1 as secondary. Save it and restart your browser. That's the basic Windows path. On macOS it's System Settings, Network, your connection, Details, DNS, then click the plus sign to add servers. Same idea, different menu labels. One thing most people skip: flush your DNS cache after changing these settings. Windows users run ipconfig /flushdns in an elevated command prompt. Mac users run sudo dscacheutil -flushcache; sudo killall -HUP mDNSResponder. If you don't do this, your system will keep serving stale cached results for a while and you'll think the change didn't work. I lost about twenty minutes on this exact problem last year. My browser still couldn't reach sites I knew were unblocked at the DNS level because the old cached resolution was still active in my system memory. The flush command fixed it immediately. Linux varies by distribution. Most modern setups use systemd-resolved, where you edit /etc/systemd/resolved.conf and set DNS=1.1.1.1, then run systemctl restart systemd-resolved. Older systems with resolvconf use a different path entirely. I've seen people mix these up and end up with conflicting configuration files, so check what your distro actually uses before editing anything.
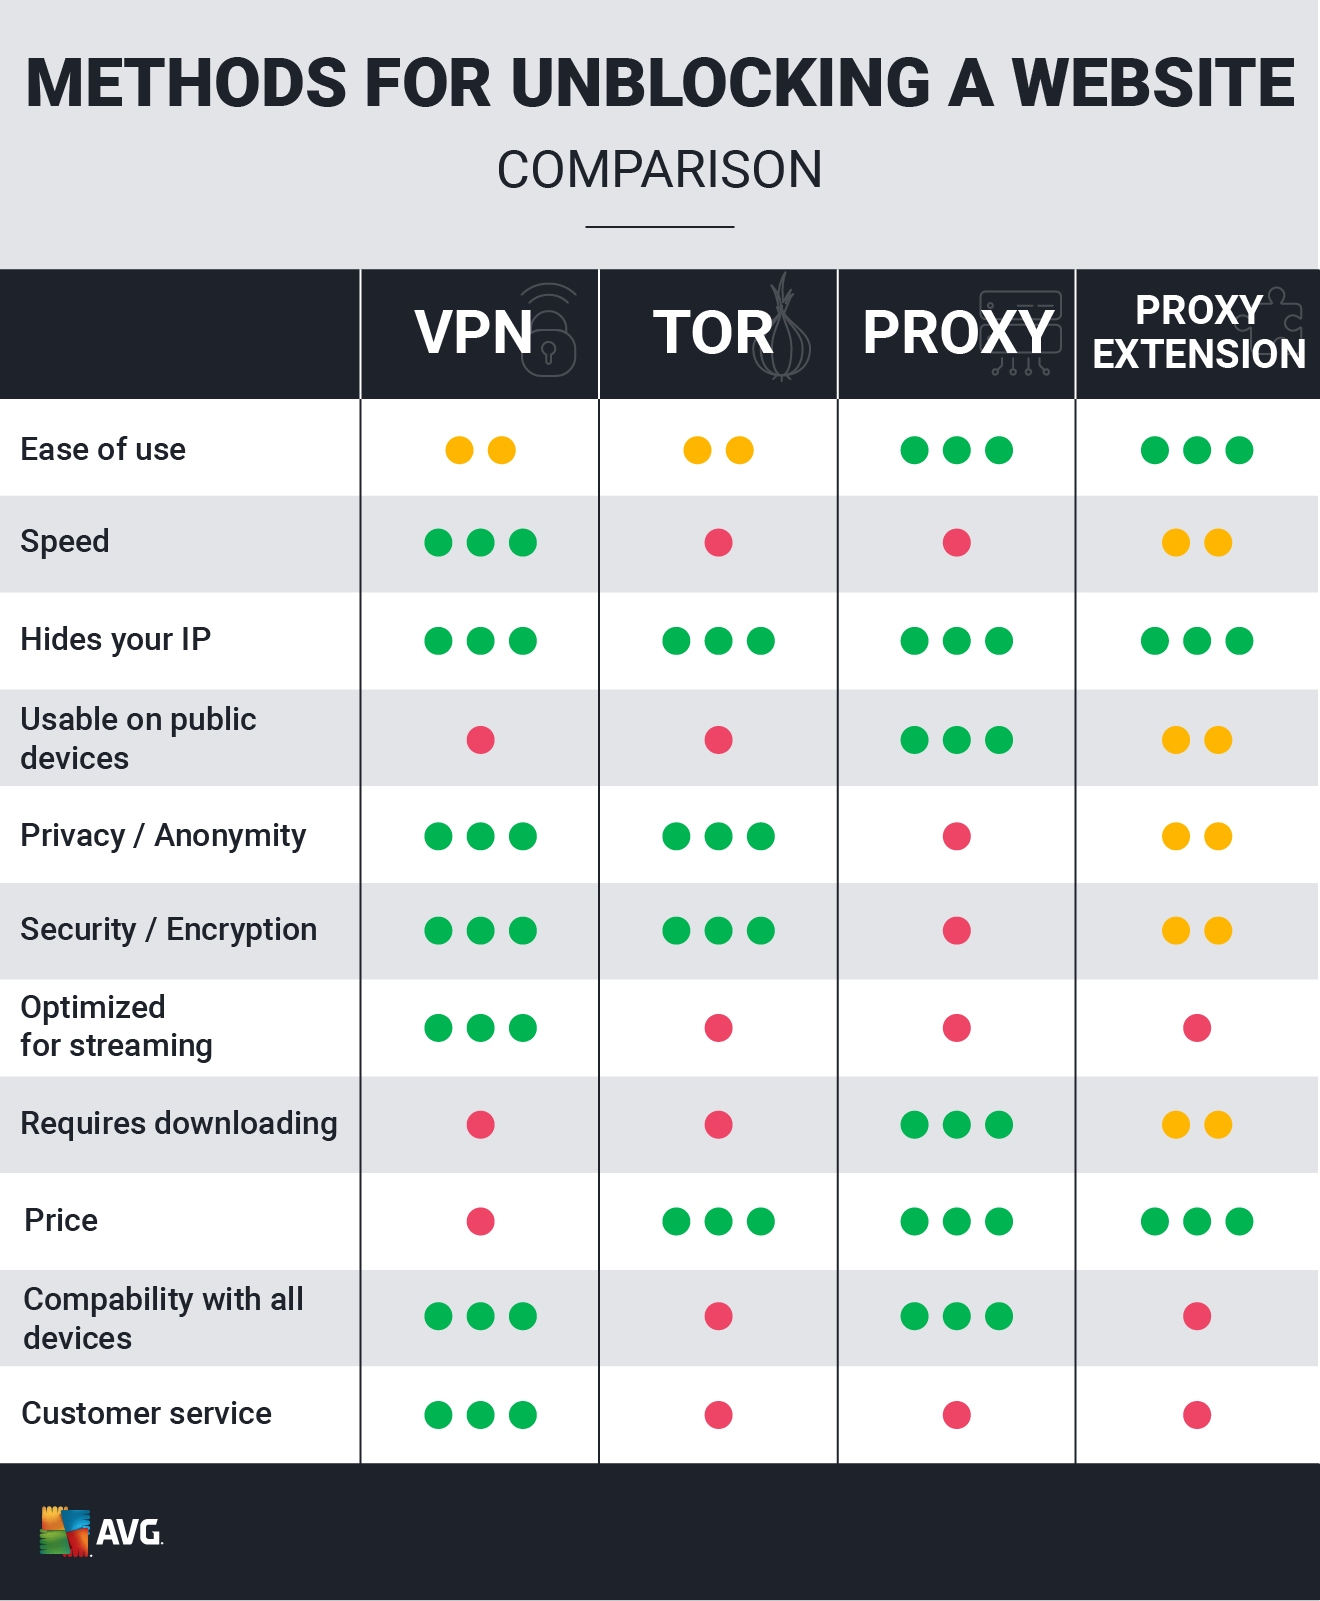
Here's something beginners almost never understand: DNS changes only bypass DNS-level blocking. If your ISP or government is doing deep packet inspection or IP-level blocking, changing your DNS resolver does absolutely nothing. I ran into this when trying to access a news site that had been blocked at the IP level in my region. Switched to Cloudflare DNS, verified the DNS resolution was correct using nslookup, confirmed the domain pointed to the right IP, and still got a connection timeout. The block wasn't at the DNS layer at all. In that scenario, you'd need something like a VPN or Tor to actually get through. Another common pitfall is assuming all public DNS resolvers handle blocking the same way. Cloudflare's 1.1.1.1 doesn't block anything by default. Google's 8.8.8.8 has family shield variants that do filter adult content. Quad9's 9.9.9.9 blocks known malicious domains. If you're switching resolvers to bypass filtering, make sure you're not accidentally moving to one that applies its own filters on top of your ISP's. I once switched from my ISP's DNS to what I thought was a neutral resolver and found out it was Quad9, which was blocking half the software update endpoints I needed. Took me an hour to figure out which resolver was actually causing the problem by testing each one individually. There's also the issue of DNS poisoning and MITM attacks on unencrypted DNS. Standard DNS queries are sent in cleartext, which means anyone on your network path can intercept and modify them. This is less relevant for basic bypassing but worth knowing if you're dealing with an adversary who actively wants to prevent you from unblocking sites. DoH or DoT support varies by operating system and browser. Chrome and Firefox both support DoH natively now. On Windows 10 and later, you can enable DoH through Settings under Network and Internet. On macOS it's under Network settings for your active interface. Using encrypted DNS makes it harder for your ISP to selectively block specific resolvers, though it doesn't solve IP-level blocking either.
Get the Full Details
A practical limitation I want to mention upfront: mobile devices often require app-based configuration for custom DNS rather than system settings. On iOS you go to Wi-Fi settings, tap the info icon next to your network, scroll to Configure DNS, and switch it to Manual. Android is similar but varies between versions and manufacturers. Some carrier-branded Android phones lock DNS configuration behind restricted menus that require developer mode or root access to modify. I had a user call me once because their carrier phone wouldn't accept manual DNS entries at all. They ended up having to configure the DNS on their router instead, which pushed the settings to all connected devices automatically. That's actually the most reliable approach if you have router access, since it covers every device on your network without per-device configuration. Router-level DNS changes depend entirely on your router's firmware. Most stock firmware from ISPs like Comcast, AT&T, or BT gives you zero control over DNS settings. Third-party firmware like OpenWrt or DD-WRT solves this but requires flashing your router, which voids warranties and can brick cheap hardware if you do it wrong. If you have a supported router already running third-party firmware, the DNS settings are usually under Network > DHCP/DNS. If you're not comfortable with that, stick to per-device configuration or ask whoever manages your network to make the change. The other thing people don't consider is that some services detect and block known public DNS resolvers. A few streaming platforms and banking sites will return errors if they see queries coming from 1.1.1.1 or 8.8.8.8 because those IPs are associated with circumvention. This is rare but it happens, and switching back to your ISP's DNS or trying a different resolver is the only workaround. I encountered this with one particular sports streaming service that would accept connections from any IP but immediately drop DNS lookups that originated from known public resolvers. Switching to my ISP's DNS resolved it, though that meant losing access to the other sites that had been blocked by my ISP. It's a trade-off that depends entirely on what you're actually trying to access.
Verify your DNS change worked by running nslookup anyexample.com 1.1.1.1 from your command line. If it returns a valid IP address instead of a timeout or an ISP landing page, the resolver is working. Then visit whatismydnsaddress.net to confirm your public DNS exit point has actually changed. These two checks cover the most common failure modes: configuration saved incorrectly and caching delays making it look like the change didn't apply.