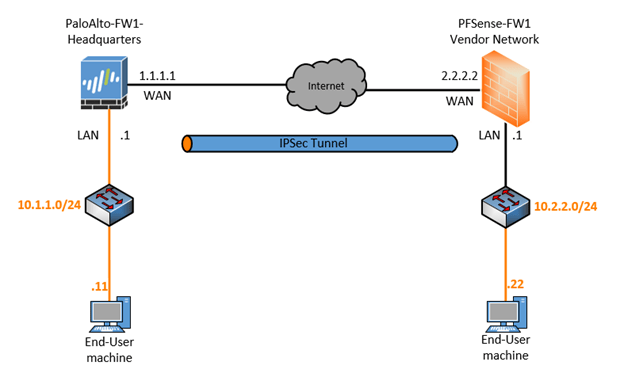
Setting Up IPsec on Palo Alto Firewalls
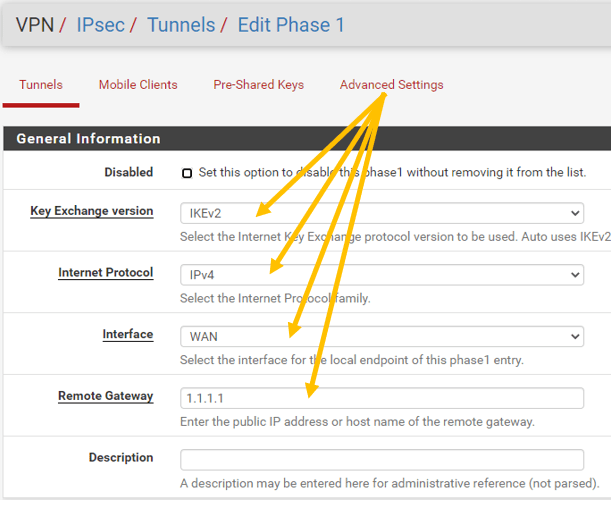
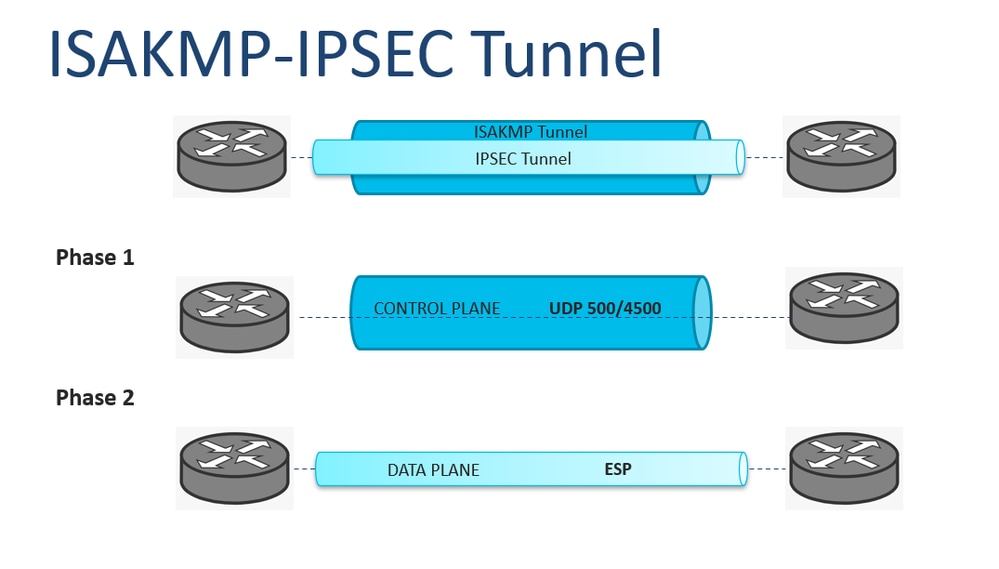
IPsec tunnels on Palo Alto firewalls are straightforward once you understand how Phase 1 and Phase 2 work separately. Phase 1 establishes the secure channel that protects the negotiation itself. Phase 2 negotiates the actual encryption parameters for your traffic. Getting both right matters because a mismatch in either phase kills the tunnel immediately. I spent years fighting dead tunnels caused by what seemed like minor configuration errors. One particular headache was when a partner site used non-standard Diffie-Hellman groups. We were stuck on Phase 1 rekey failures until I realized their firewall was pushing DH Group 14 while our policy defaulted to Group 5. The fix was simply aligning the group numbers on both ends. This kind of mismatch happens constantly. Phase 1 creates the ISAKMP SA. You define the pre-shared key, authentication method, encryption algorithm, hash algorithm, and DH group. Palo Alto recommends using SHA2-256 for hashing and AES-256 for encryption. These are the current industry standards. Older setups sometimes still use SHA1 and AES-128, which work but shouldn't be the default choice anymore.
The pre-shared key itself needs to be at least 20 characters. Shorter keys create vulnerabilities during brute force attempts. Most people reuse the same key across multiple tunnels, which is a security problem you should avoid. Each tunnel should have its own unique PSK. When configuring the proposal, you list the algorithms in order of preference. Palo Alto uses the first matching algorithm from the remote end. This means if your proposal lists AES-256 first and the peer only supports AES-128, the tunnel falls back to the weaker option. Always verify what the remote side actually supports before finalizing your proposal list.
Phase 2 Configuration
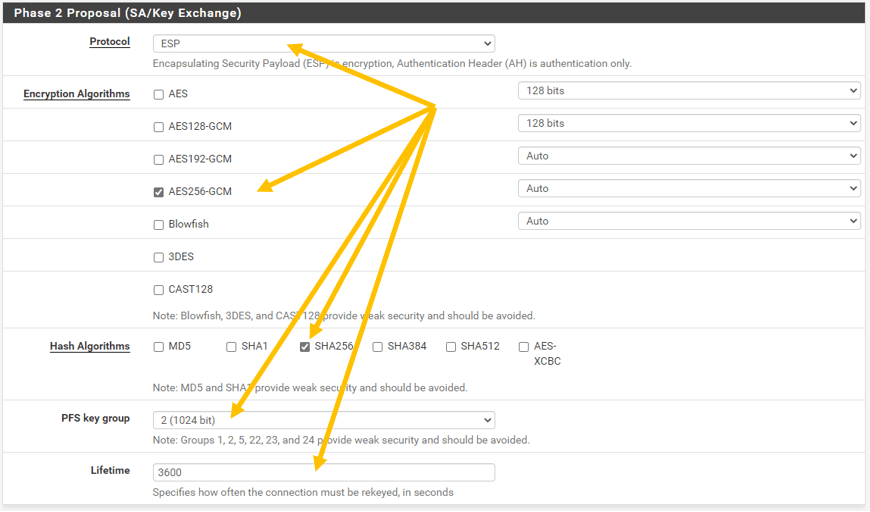
Phase 2 sets up the IPsec SA for actual data traffic. The key difference from Phase 1 is that you're negotiating encryption for the payload, not the control channel. Most configurations use ESP mode with AES-256-GCM or AES-256-CBC. GCM is faster on modern hardware because it provides both encryption and authentication in a single pass. The PFS setting is critical here. Perfect Forward Secrecy forces a new key exchange for each tunnel session. Without PFS, an attacker who compromises one session key could theoretically decrypt all captured traffic from that tunnel. Enable PFS on every tunnel unless you have a specific performance reason not to. The CPU impact on modern Palo Alto hardware is negligible. Dead Peer Detection settings deserve attention. Set the interval to 10 seconds with a hold time of 30 seconds. This combination detects failed peers quickly without generating excessive traffic. I once saw a configuration with DPD disabled entirely. The tunnel stayed in a half-up state for hours because neither end recognized the failure.
Get the Full Details
Common Pitfalls
The most frequent issue I encounter is asymmetric routing breaking the tunnel. When traffic enters one firewall and exits another, the return path doesn't match. IPsec requires symmetric paths because the decryption key is tied to the specific interface and SA. Check your routing table thoroughly before testing the tunnel. NAT traversal causes problems when one end is behind a carrier-grade NAT. Palo Alto handles NAT-T automatically, but only if the local gateway address isn't also the public IP. If you're translating between internal and external addresses, make sure the proxy ARP settings are correct on the outside interface. MTU issues surface occasionally. IPsec adds overhead to each packet. Standard overhead is 50 bytes for ESP with AES-256 and SHA-256. Some packets get fragmented and dropped if the path MTU isn't adjusted properly. Set the PMTUD setting to enable path MTU discovery, or manually reduce the MTU on your tunnel interfaces by 60 bytes to be safe.
Troubleshooting Steps
Start with the Phase 1 logs. Use the command "show security ipsec phase1-statistics" to see negotiation attempts. A failed Phase 1 shows which parameter mismatched. Check the proposal list, the DH group, and the pre-shared key first. These three cause the majority of failures. For Phase 2 issues, run "show security ipsec phase2-statistics". Look for quick mode exchanges. Failed quick modes usually indicate a proposal mismatch or an route mismatch on one end. Verify that the traffic selectors match exactly on both sides. A subnet mask difference of even one bit can prevent the tunnel from establishing. Capture traffic with tcpdump if the logs don't reveal the problem. Run the capture on both ends simultaneously. Look for ISAKMP packets reaching the interface. If you see them on one side but not the other, you have a routing or firewall issue between the two gateways. Fix the underlying connectivity first, then retest the tunnel.
Verification
Once the tunnel is up, verify the security associations with "show security ipsec sa". You should see active Phase 1 and Phase 2 entries with matching SPI values. The transform and key lifetime counters should be incrementing as traffic flows through the tunnel. Test actual traffic flow by pinging across the tunnel. Use large packets to verify PMTUD is working correctly. If pings succeed but larger transfers fail, you have an MTU issue. Adjust accordingly. Monitor the tunnel over several hours. Watch for rekey failures or DPD timeouts. These intermittent issues often don't appear during initial testing but show up under load or after extended uptime. A tunnel that works for five minutes but fails after two hours is still a broken configuration.