Understanding Secure Access Systems and Why They Break
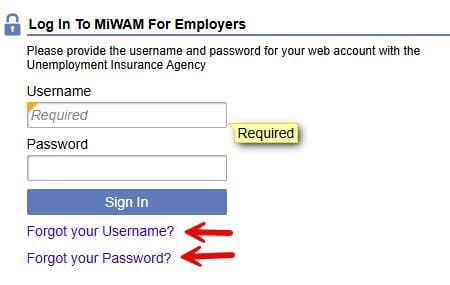
Most people don't think about their identity and access management platform until something goes wrong. That is exactly when you need it to work perfectly. I have spent years troubleshooting these systems, and the pattern is always the same - something small gets misconfigured, a token expires unexpectedly, or a permission rule silently changed through a bulk update nobody reviewed. The result is usually a locked-out administrator or a confused helpdesk. When I first started dealing with Uia Miwam Log In The Comprehensive Guide To Secure Access And Troubleshooting, I assumed it would be straightforward. It was not. The login flow involves multiple hops - the initial SAML assertion, the token refresh, and sometimes a second factor challenge depending on your network location. I remember sitting with a client who could not get past the second authentication step. We spent three hours going in circles before I realized the time sync on their internal server was off by forty-seven seconds. Not minutes, not hours. Forty-seven seconds. Enough to make every refresh token invalid the moment it left the server. That single incident changed how I approach every authentication issue after that. The first thing I check is system clock synchronization across every hop in the chain. Not the workstation, not the browser, the actual backend servers talking to each other. If NTP is drifting, nothing else matters.
How Authentication Actually Works Under the Hood
Before you can troubleshoot a login failure, you need to understand what happens between the moment someone types their password and the moment they land in their dashboard. It is not a simple pass/fail check. The process usually involves the identity provider receiving credentials, validating them against a directory, generating a session token, optionally verifying a second factor, and then passing that token back through whatever gateway or proxy sits between the user and the application. Each step is a potential failure point. Here is something most guides do not mention clearly. The error message you see on the login screen rarely tells you which step failed. A generic "authentication failed" could mean bad password, expired token, inactive account, blocked IP, or a misconfigured service principal. I have seen support teams chase red herrings for days because they trusted the UI error text instead of looking at the actual auth logs. The UI error is marketing. The log entry is reality. Always read the log entry.
Step By Step Login Process
The standard login sequence looks like this in practice. You enter your credentials on the provider page. The provider validates them and returns an authorization code. Your client application exchanges that code for an access token and a refresh token. The access token gets attached to subsequent API requests. When the access token expires, the refresh token kicks in automatically. If the refresh token is also expired or revoked, you get logged out and must start over. Simple in theory. Now add multi-factor authentication, conditional access policies based on device compliance, geolocation restrictions, and certificate-based client authentication on top of that. The sequence gets longer, and every additional condition is a place where things can silently break. I once spent an afternoon troubleshooting what looked like a password problem only to discover the user's device had lost its compliance certificate after a Windows update. The system was rejecting the login before it ever checked the password. The fix was renewing the certificate and restarting the endpoint policy agent. Three minutes total, two hours of investigation.
Get the Full Details
Common Login Failures and What They Really Mean
Error code 401 on the login page does not always mean wrong credentials. Sometimes it means the client application lost its API key or the OAuth scope configuration drifted. Error code 403 usually means your account is fine but your permissions do not cover the resource you are trying to reach. I learned this distinction the hard way when a developer kept resetting his password for a week, convinced he had a credential problem. His account had been demoted from admin to read-only through a bulk policy change nobody told him about. The password was always correct. The permissions were not. Another frequent issue is the dreaded "session expired" loop. You log in successfully, the page loads, and then you get bounced back to the login screen. This almost always points to a token lifetime mismatch between the identity provider and the application. The provider issues tokens valid for fifteen minutes, but the app expects them to last an hour. Or vice versa. The fix is adjusting the token expiry settings on both sides to match, or more commonly, just updating the application configuration to accept the provider's token format. There is also the case of certificates causing login problems. Mutual TLS authentication requires both the client and server to present valid certificates. I encountered a situation where an intermediate CA certificate expired on the server side, which made every client certificate validation fail with a confusing error. The actual client certificates were fine. The server's trust chain was broken. Replacing the intermediate certificate resolved it immediately, but finding the root cause took several log dives across multiple systems.
Tools for Troubleshooting Authentication Issues
You do not need expensive software to diagnose most login problems. A web browser's developer tools will show you every request and response during the authentication flow. Look at the headers, check the status codes, and examine the token contents. If the provider gives you a JWT, you can decode it directly in the browser console without any special tools. The payload will tell you exactly what permissions you have, when the token expires, and which audience it is intended for. This single habit has saved me countless hours. For deeper investigation, packet captures are useful but often overkill. I prefer checking the server-side authentication logs first. Most identity providers maintain detailed logs showing each step of the login process with timestamps and error codes. These logs are far more informative than anything you can see from the client side. If the provider logs show a successful authentication but the application still rejects the user, the problem is almost certainly on the application side, not the authentication side. Another practical tool is testing with a different browser or incognito mode. This rules out cookie issues, cached sessions, and extension conflicts that can interfere with the login flow. Browser extensions, especially password managers and ad blockers, sometimes modify requests in ways that break authentication. A quick test in a clean browser session can eliminate that variable immediately.
Preventive Measures That Actually Work
Most authentication problems can be prevented with basic operational hygiene. Keep your certificates current. Set up alerts for certificate expiration at least thirty days before they actually expire. Check NTP synchronization weekly, not monthly. Verify that your token lifetime settings are consistent across all systems. Document any changes to permission policies and communicate them to affected users before they take effect. I also recommend maintaining a standard test account that you can use to verify the authentication flow after any system change. Something as simple as logging in with a dedicated test user after a configuration update catches problems before real users hit them. This sounds basic, but I have lost count of the number of times a seemingly harmless change broke the login process for everyone because nobody tested it. Another thing that helps is keeping your authentication logs centralized. When problems occur, being able to pull logs from the identity provider, the application server, and the network gateway into one view saves enormous amounts of time. Many organizations keep these logs in separate systems with different retention periods, which makes troubleshooting significantly harder than it needs to be. A simple log aggregation solution can change your mean time to resolution from hours to minutes.

When You Should Escalate
Sometimes the problem is beyond what you can fix with documentation and log analysis. If you suspect a vulnerability, if authentication is being bypassed, or if you cannot determine why users are being rejected despite correct credentials, escalate to your security team. Do not spend days trying to debug a potential breach yourself. Similarly, if a system update is clearly causing widespread authentication failures and no workaround exists, contact the vendor with your findings. Provide them with the specific error codes, timestamps, and steps to reproduce. Generic complaints like "it stopped working" do not help anyone. Authentication systems are critical infrastructure. They are also complex enough that problems will occur occasionally. The goal is not to prevent every issue - that is impossible - but to respond quickly when they do happen. Understanding the flow, knowing where to look, and having the right tools available makes the difference between a five-minute fix and a six-hour outage.