Understanding UCSF's Remote Access Infrastructure
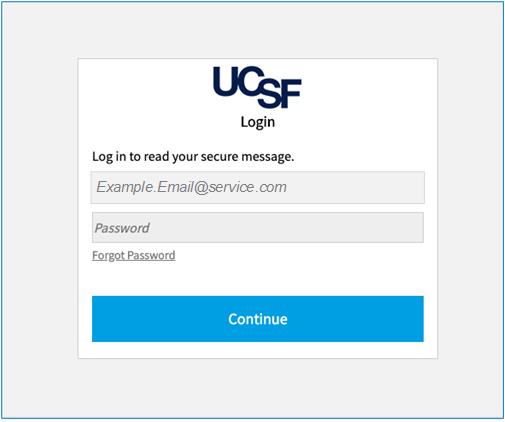
UCSF, like most major academic medical centers, runs a complex authentication ecosystem. Their primary identity platform is tied to central directory services that manage credentials across clinical and research systems. When people search for Ucsf Clairvia Login The Ultimate Secure Access Solution For Modern Healthcare, they are typically looking for the portal through which affiliates, researchers, and clinical staff connect to internal resources from off-campus locations. The reality is more routine than the marketing language suggests. UCSF uses standard identity federation and multi-factor authentication infrastructure. The login process routes through their central directory, verifies credentials against Active Directory, and then applies conditional access policies based on device posture, location, and role. It is not a single product called "Clairvia" but rather a collection of integrated systems that handle authentication, authorization, and session management across the health system. When you attempt to access a UCSF-protected resource remotely, you are redirected to their authentication gateway. The sequence runs like this: you enter your NetID and password, the system challenges you for a second factor through Duo or a similar MFA provider, and then based on your group membership and device compliance status, you are issued a session token that grants access to specific applications. Some systems pull directly from the central identity provider. Others use SAML or OIDC federated trust relationships.
I have spent years troubleshooting connection issues across large healthcare networks, and the UCSF setup follows the same patterns you will see at any major university hospital. The trick is understanding which part of the chain is failing when something breaks. Most login issues are not authentication failures at all. They are usually downstream problems with session cookies expiring, device posture checks flagging outdated certificates, or application-level access policies that have not been updated after a role change.
Common Problems and What Actually Fixes Them
The most frequent issue I encounter involves credential caching on mobile devices. After a password reset or MFA enrollment change, the stored session tokens do not always invalidate properly. The result is a login loop where the system accepts your credentials but then immediately kicks you back to the login screen. Clearing the app cache and reinstalling the remote access client, or simply using a private browsing window, resolves this almost every time. Another persistent problem is the conflict between VPN-based access and SSO-based access. Some UCSF systems require a VPN tunnel for network-level security, while others rely entirely on browser-based federation. Trying to use both simultaneously creates certificate and routing conflicts. If you are hitting timeout errors on one system but not another, check whether you are connected through the VPN client and disconnected from it. Alternating between VPN and direct SSO depending on the application usually sorts it out. I once spent three days debugging an access issue for a researcher who could log into the main portal but could not reach a specific clinical data repository. The problem turned out to be that his directory group membership had been updated to a different OU, and the attribute propagation delay on the downstream system had not caught up. The workaround was submitting a ticket to directory services for immediate replication sync rather than waiting for the scheduled propagation cycle, which normally runs every four hours.
Get the Full Details
What Most People Miss About This Setup
One counter-intuitive detail is that UCSF's authentication gateway does not always honor the same trust relationships across all network segments. A session token issued for research systems may not be valid for clinical operations, even though both use the same login page. This is by design, not a bug. Clinical systems enforce stricter Conditional Access policies because of HIPAA requirements and internal risk tolerance. If you can access one suite of applications but not another with the same credentials, the restriction is almost certainly policy-based, not a credential problem. Another thing beginners overlook is the difference between the guest/visitor access path and the affiliate access path. UCSF maintains separate identity streams for patients, visitors, contractors, and employed faculty. Mixing these up at the login stage will result in access denial even with valid credentials. The guest portal uses a completely different identity provider and does not share any directory entries with the affiliate system. Trying to log into the research portal with visitor credentials will always fail, regardless of how correct your password is.
Practical Limitations to Be Aware Of
The system is not seamless. Session timeouts during active clinical work are a known frustration, particularly on systems that enforce aggressive idle timeout policies. These timeouts are real and intentional from a compliance standpoint, but they do interrupt workflow. There is no official workaround other than adjusting your session management habits, which is not a satisfying answer when you are in the middle of charting or reviewing imaging results. Device compliance checks can also be a bottleneck. If your laptop has an outdated OS version, an expired endpoint protection certificate, or missing security patches, the access gateway will block the connection before you even reach the login screen. This is a common source of confusion because users interpret the block as an authentication failure rather than a device policy enforcement. The fix usually requires running the endpoint compliance tool and allowing it to remediate the detected issues before attempting to reconnect.
Where to Find Official Resources
UCSF's IT service desk and their published knowledge base pages contain the most current guidance on login procedures, supported browsers, and MFA enrollment steps. The official UCSF website and internal affiliate portal should be your primary references rather than third-party sites that may have outdated screenshots or incorrect URLs. Information about remote access configuration, Duo enrollment, and account recovery is maintained through those channels and updated as the underlying infrastructure changes.