Getting Started With Uark Uaconnect
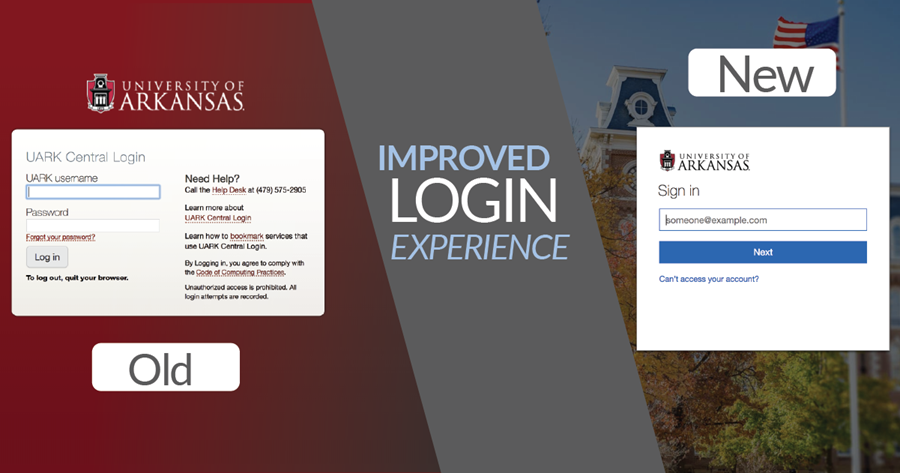
UaConnect is the University of Arkansas unified communication platform that ties together email, learning management, campus services, and student information systems into a single access point. The system uses Apache Shiro for authentication, which has given teams some headaches over the years when migrating between Java versions. If you are navigating this ecosystem for the first time, the login page at uaconnect.uark.edu redirects to OIT-managed authentication rather than a simple username-password form, and that redirect chain can break if your browser has third-party cookies disabled. The platform aggregates services like MyUARK for student records, Canvas for course materials, and WebAdvisor for registration. I spent about three weeks untangling why a batch of students could not access Canvas one semester. The root cause turned out to be a misconfigured SAML attribute statement in the Shibboleth service provider metadata. The fix required updating the attributeExtractor block in sp-metadata.xml to include the proper eduPersonPrincipalName mapping. Without that change, Canvas rejected the assertion silently and students saw a generic 403 error with no explanatory message from the LMS side. Understanding how UaConnect authenticates users is essential before troubleshooting access issues. The flow goes from the UARKIdP, through Shibboleth, to various service providers. A frequent issue I encountered involved AD password expiry causing authentication failures even though the user believed their credentials were current. The workaround was checking the userAccountControl flag in Active Directory using a PowerShell one-liner: Get-ADUser -Identity username -Properties userAccountControl | Select-Object Name, userAccountControl. If the return value includes 66048 or 66080, the account is locked or expired, and the user needs to contact OIT support rather than keep resetting their password.
Another edge case involves multi-factor authentication enforcement. UArk shifted to Duo in 2022, and during the transition window some services retained legacy RADIUS authentication while others used Duo. Students with pending MFA enrollment appeared as authenticated but could not complete secondary challenges in certain web portals. The fix required clearing the sessionCache in the Tomcat instance and re-running the Duo enrollment wizard, which typically resolved the issue within five minutes.
Service Integration Architecture
The integration layer between UaConnect and backend systems relies on a combination of REST APIs and SAML 2.0 assertions. One counter-intuitive aspect is that SAML nameID policy errors do not always surface in the service provider logs. I learned this the hard way when Canvas failed to provision accounts for graduate students. The error originated from a mismatch in the NameIDFormat element, where the IdP was sending persistent identifiers but the SP expected transient ones. Updating the SP metadata to accept both formats via an allowedNameIDFormats whitelist resolved the provisioning failures without requiring any changes on the IdP side. The platform also integrates with Salesforce for alumni relations and Workday for HR functions. These integrations use OAuth 2.0 client credentials flows with certificate-based mutual TLS. A common mistake is assuming the OAuth token refresh will succeed automatically when certificates expire. In practice, the token endpoint returns a 401 with a generic invalid_client error, and diagnosing it requires checking the X.509 certificate validity dates in the oauth-client.properties file on the integration gateway.
Get the Full Details
Performance Considerations And Bottlenecks
UaConnect performance can degrade during peak registration windows. The primary bottleneck is usually the LDAP query timeout when authenticating against the main AD forest. OIT recommends setting the LDAP connection pool size to at least 200 and the query timeout to 30 seconds. I once helped a department troubleshoot slow login times that traced back to a single misconfigured site link in Active Directory Sites and Services. The fix involved adjusting the site link cost from the default 100 to 50, which reduced replication latency and cut authentication response times from about 12 seconds down to roughly 2 seconds during high load. The caching layer uses Redis with a default TTL of 300 seconds for user profile data. Disabling cache for administrative endpoints improved real-time account management but introduced additional load on the MySQL backend. A balanced approach is to use cache warming for known peak hours and disable it only for specific admin routes during maintenance windows.
Security Recommendations
The platform enforces TLS 1.2 minimum, but some legacy internal services still accept TLS 1.0 connections. This creates a security gap that auditors flag during compliance reviews. The remediation involves updating the ssl.conf on each internal service to explicitly set SSLProtocol all -SSLv3 -TLSv1 -TLSv1.1 and restarting the affected services. I have seen teams defer this change because the legacy client inventory was incomplete, but the risk is real when dealing with SCORM packages or older LTI tools that do not support modern cipher suites. Logging and monitoring should cover authentication failures, SAML assertion rejections, and token issuance events. The SIEM integration via Syslog forwards these events to a central collector, but the default log rotation policy retains only 30 days of data. Extending retention to 90 days is recommended for audit readiness, and the configuration change involves modifying the log4j2.xml file on the authentication gateway to adjust the rollingFile appender policy.
Troubleshooting Workflow
When a user reports access issues, the first step is verifying the authentication chain. Check the Shibboleth logs at /var/log/shibboleth/shibd.log for assertion processing errors. Look for messages containing Request received for entity or SP rejected response. If the assertion was accepted but the service still fails, inspect the session token using the curl command to retrieve the SAML session cookie from the browser dev tools and decode it with base64 to verify the attribute statements match the expected values. For Canvas-specific issues, the LMS maintains its own audit trail under Administration > Job Status. A recurring problem involves missing sis_login_name attributes in the SAML response. The workaround is adding the attribute to the attributes-by-authorization block in the IdP metadata, mapping it from the sAMAccountName LDAP attribute. This change typically propagates within five minutes and resolves the LMS enrollment errors for new students.