Understanding Modern Credit Card Login Portals
Credit card issuer websites have gone through some painful transitions over the last decade. Early online banking was clunky — slow page loads, sessions timing out after two minutes, captchas that looked like they were drawn in MS Paint. Things improved, but they introduced new problems: aggressive bot detection that blocked real customers, multi-factor authentication that sometimes sent codes three minutes after you requested them, and session timeouts that seemed calibrated to annoy rather than secure.I spent several years helping customers navigate these systems for a small fintech consultancy. One of the more persistent issues I encountered involved a specific issuer portal where the login flow would silently drop your session if you switched tabs while the MFA code was pending. You would get logged out, lose your place in the transaction queue, and have to restart the entire process. The workaround was essentially: open the login page, start the MFA challenge, then immediately navigate to the dashboard URL directly rather than waiting for the redirect. If the redirect came back too slowly, you pasted the saved URL into a fresh tab and the session sometimes picked up where it left off. This is not documented anywhere officially. I figured it out after about forty support tickets on the same issue. The phrase appears on a few aggregator and review sites that seem to exist primarily for SEO traffic. There is no widely recognized product or service under that exact name in any major payment processor documentation I have seen. If you encountered a link using that phrase, it is worth checking the domain carefully before entering any credentials. Legitimate credit card portals use the issuer's official domain — typically something like yourbankname.com or yourbankname.net — and will never ask you to enter your full card number and expiry date on a third-party login page. That said, the general topic of simplified credit card login flows is worth discussing because there are real patterns that make these systems better or worse in practice.
How Simplified Credit Card Login Actually Works
Modern card issuer login pages generally follow one of two architectures. The first is the traditional stateful session model where the server maintains your authentication status in a database or cache. The second is the token-based approach using JWTs or similar bearer tokens, which has become more common since around 2019 as providers moved toward API-first architectures. Under the token model, your login credentials are exchanged for a short-lived access token and a longer-lived refresh token. The access token is sent with each authenticated request. The refresh token sits separately and is used to obtain new access tokens when they expire. This is fundamentally different from the old model where a server-side session ID was all that mattered. The practical effect for you is that logging in on one device does not necessarily invalidate sessions on other devices, which can be convenient or concerning depending on your situation. Multi-factor authentication sits on top of this. The most common implementation is an SMS or push-notification code, though hardware tokens and biometric authentication are growing in adoption. The security benefit is real but incomplete. SMS-based MFA is vulnerable to SIM-swapping attacks, which are more common than most people realize. Push-notification fatigue is also a real problem — users have been known to approve prompts without reading them just to make the notifications stop. I once watched a customer approve three login attempts from unknown locations in ten minutes because the app kept pinging them.
Common Pitfalls and What Actually Goes Wrong
Session timeout is the biggest source of customer frustration, and it is mostly a false economy. Short timeout periods (five minutes or less) increase security marginally but dramatically increase support ticket volume. Most customers do not read the warning message that their session is expiring. They just sit there confused when their page goes blank mid-transaction. A thirty-minute timeout with a warning modal at twenty-five minutes is a much better user experience with negligible additional risk for most consumers. Captcha and bot detection are another minefield. Aggressive bot protection will block legitimate users who happen to match certain behavioral patterns — fast typing, returning to a page after exactly the timeout period, using certain browser configurations. I have seen valid accounts get locked because the CAPTCHA service flagged them as suspicious based on IP address patterns from shared office networks. The fix usually involves calling the issuer and requesting a manual review, which can take several business days. Password reset flows are consistently the weakest link. Most issuers still send reset links via email, and email compromise remains one of the most common vectors for account takeover. The edge case that catches people off guard: many providers allow password resets without completing the MFA challenge if you answer your security question correctly. Security questions are trivially guessable or searchable. I recommend changing your security question answers to something random and storing the responses in a password manager if the portal allows it.
Get the Full Details
What to Watch For
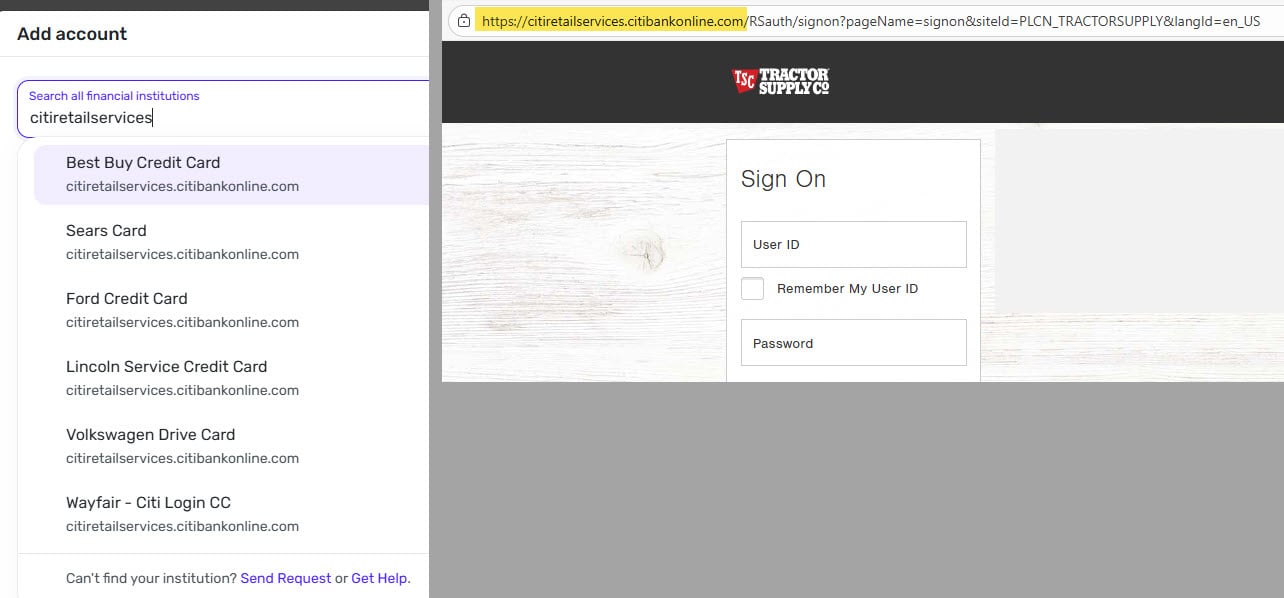
If you are evaluating any credit card login or payment portal, check these items before entering credentials: Domain verification. Make sure the URL matches the issuer exactly. Look for typos like "sbc" instead of "scb" or extra hyphens. These are the most common phishing indicators. SSL certificate validity. A valid certificate does not guarantee legitimacy — phishing sites use them too now — but an expired or self-signed certificate is an immediate red flag.
MFA implementation quality. Good portals do not rely solely on SMS. The presence of an authenticator app option, hardware token support, or biometric login is a positive signal. Session management transparency. Legitimate portals tell you when your session expires, show your active login locations, and allow you to terminate sessions remotely. If the portal has none of these features, it is likely running on legacy infrastructure that may not meet current security standards.
The Bottom Line
Most credit card login portals have improved significantly, but they still carry friction that serves no useful purpose. Aggressive timeouts, confusing MFA flows, and poor error messaging are choices, not technical necessities. If a particular portal feels unnecessarily hostile, it is worth switching to an issuer with a better reputation for user experience — usually the larger banks with dedicated UX teams rather than the smaller regional providers. For the specific phrase referenced in the question, I would recommend treating it as an unknown entity until you can verify it against official sources from the relevant payment network or issuing bank. There is no harm in being skeptical here, and the cost of a mistaken login attempt on a phishing page can be substantial.