What TrustedInstaller Actually Is
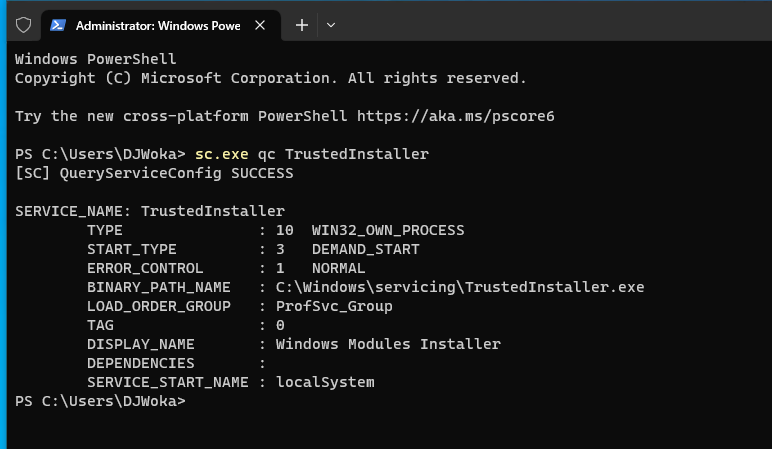
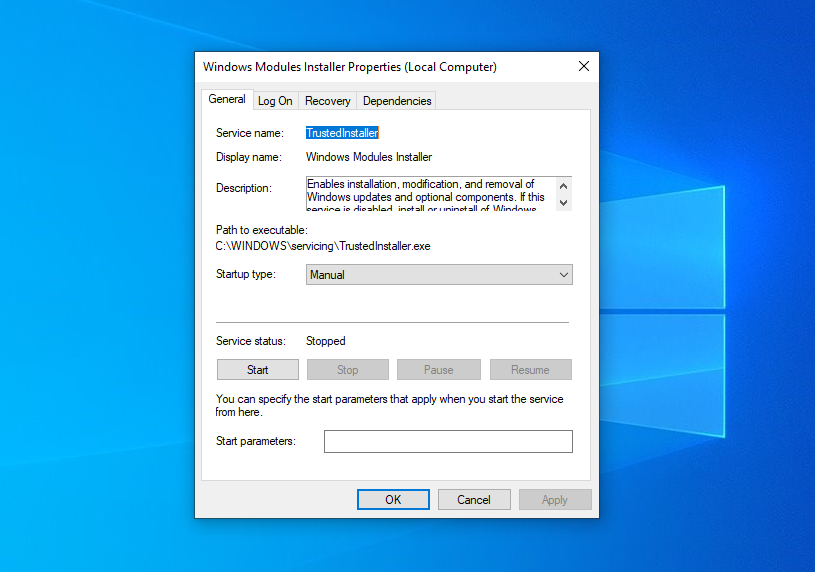
TrustedInstaller isn't a user account you log into. It's a built-in service identity tied to the Windows Modules Installer service. The service controls how Windows installs, modifies, and removes optional features and feature updates. When you see that permission prompt blocking your changes to files in C:\Windows\System32 or the WinSxS folder, TrustedInstaller is the one sitting between you and the file. The service runs under a local security principal called NT SERVICE\TrustedInstaller. It exists specifically to enforce the idea that not even the SYSTEM account should be casually modifying core Windows installation files. This is why standard administrator rights won't let you rename or delete a lot of files in System32. The access control lists on those objects explicitly grant ownership and full control to TrustedInstaller, not to Administrators and not to SYSTEM either. I ran into this directly when I was trying to remove a leftover telemetry DLL after disabling certain diagnostic features on a machine. The file sat in System32 with a long chain of service-specific SIDs in its ACL. Even running as SYSTEM through PsExec gave me an Access Denied. The fix was straightforward in hindsight: take ownership of the file from TrustedInstaller, add an explicit full-control ACE for yourself, then do the work. The commands are well documented, but the important part most people miss is that changing ownership doesn't automatically grant permission. You have to set both. After that, restore the original owner if you want to keep things clean. Windows won't punish you for it.
How It Relates to Windows Updates
When Windows Update downloads a feature update or a cumulative patch, the actual staging and installation happens under this service. The Component Based Servicing engine, often called CBS, orchestrates the transaction. Files get staged in the WinSxS directory, components get enabled or disabled, and the system integrity gets validated before anything is committed to the live installation. TrustedInstaller is the gatekeeper here because the wrong modification at this layer can brick the entire servicing stack. This is also why DISM errors during repair are so frustrating. The engine expects certain files to remain untouched unless the operation itself is driving the change. If someone manually replaces a system binary outside of the servicing pipeline, CBS will detect the mismatch during the next update cycle and flag it. You'll see error 800F081F or similar codes in the CBS logs. The component store gets into a conflicted state and Windows Update stalls until it resolves.
Common Misunderstandings
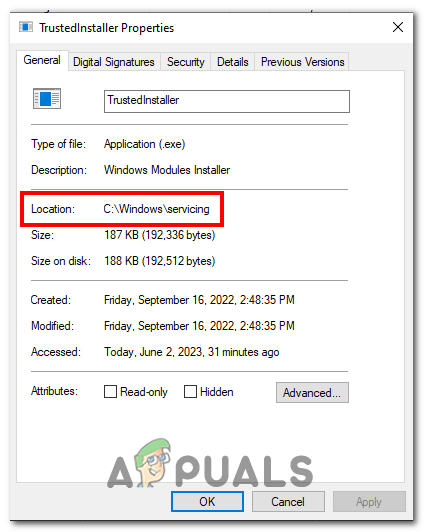
People often confuse TrustedInstaller with something malicious because the name sounds like a background process tied to spyware or unauthorized software. It isn't. The service is legitimate and shipped with Windows. You won't find it in Task Manager as a traditional process because it runs as a Windows service under a service SID. The binary is srservice.dll, loaded by services.exe. Another misconception is that TrustedInstaller grants total system control. It doesn't. Its permissions are scoped to specific directories and registry keys related to the component store and optional features. It can't protect your documents or your user profile. It only guards the Windows installation infrastructure. If you're looking at malware reports claiming TrustedInstaller is doing something suspicious, the more likely explanation is that the malware is impersonating or hijacking a different process, not that the service itself is compromised.
Get the Full Details

Working with the Service
If you need to intervene, you're usually doing one of three things: taking ownership of a locked file, disabling the service temporarily, or repairing the component store. Each has tradeoffs. Taking ownership is the most common operation. Run a command prompt as administrator and use takeown or cacls/icacls to modify the ACL. A typical sequence for a stubborn file looks like this: takeown /f "C:\Windows\System32\filename.dll" /a
icacls "C:\Windows\System32\filename.dll" /grant administrators:F Then proceed with your modification. Restore the owner afterward with takeown using the /r flag if you modified a directory tree, or manually reset it with icacls if you want precision. Disabling the Windows Modules Installer service outright is not recommended. It breaks Windows Update and any feature install or removal. You can stop the service temporarily if you're doing maintenance, but leaving it disabled will cause cumulative damage to your update pipeline over time.
For component store corruption, DISM is the tool. The two commands that matter most are: DISM /Online /Cleanup-Image /ScanHealth DISM /Online /Cleanup-Image /RestoreHealth
The ScanHealth command checks for corruption without making changes. The RestoreHealth command attempts to fix it, and it will pull replacement files from Windows Update or a local source if you specify one. Running both in sequence after a bad update is usually enough to resolve most servicing errors.
What Happens When You Override It
Removing TrustedInstaller protections to install third-party patches or custom configurations is possible but risky. The servicing stack has internal consistency checks. If you bypass TrustedInstaller and drop a file into System32 manually, the next CBS transaction may detect the foreign file and roll back or fail. In some cases, the failure is silent. Windows appears normal until you try to install an update and hit a component store error. I dealt with this once on a server where a vendor provided a custom driver replacement for a legacy hardware component. They told us to copy the DLL directly into System32. It worked immediately but caused DISM restore operations to fail for months afterward because the hash didn't match the component store manifest. The resolution required manually rebuilding the affected component entry in WinSxS using DISM component cleanup commands and then re-registering the DLL through the proper servicing API instead of a direct file drop.
When TrustedInstaller Fails
The service itself rarely fails. What fails is the environment around it. Corrupted Windows Update components, a damaged CBS log, or a misconfigured ACL can make the service appear broken. Check the CBS.log and the Windows Update log if you suspect an issue. The CBS.log lives at C:\Windows\Logs\CBS\CBS.log. Look for lines containing either Error or Failed during the timeframe of your update problem. If the component store is corrupted beyond repair, the nuclear option is an in-place upgrade using installation media. It rebuilds the Windows folders while preserving your applications and user data. This is significantly less painful than a clean install and usually fixes issues that DISM cannot resolve on its own. It also takes about 45 minutes on a modern SSD, compared to the hours some manual repair sequences can consume.
Bottom Line
TrustedInstaller is a protection mechanism, not a user account. It exists to prevent accidental or unauthorized modification of Windows core files. You will encounter it whenever you try to touch System32, WinSxS, or component store registry keys. The correct approach is to work through the proper tools and acknowledge that the restrictions are there for a reason. If you need to override them, do it deliberately, understand the consequences, and restore the original permissions afterward. Ignoring that last step is what creates problems down the road.